

Hunting Bugs Everywhere | https://teapaw.org/t.co/5Sj1CzQ4zn for private audits
Web3
Joined June 2020
- Tweets1.1K
- Following558
- Followers1.5K
- Likes6.5K




Hunter retweeted

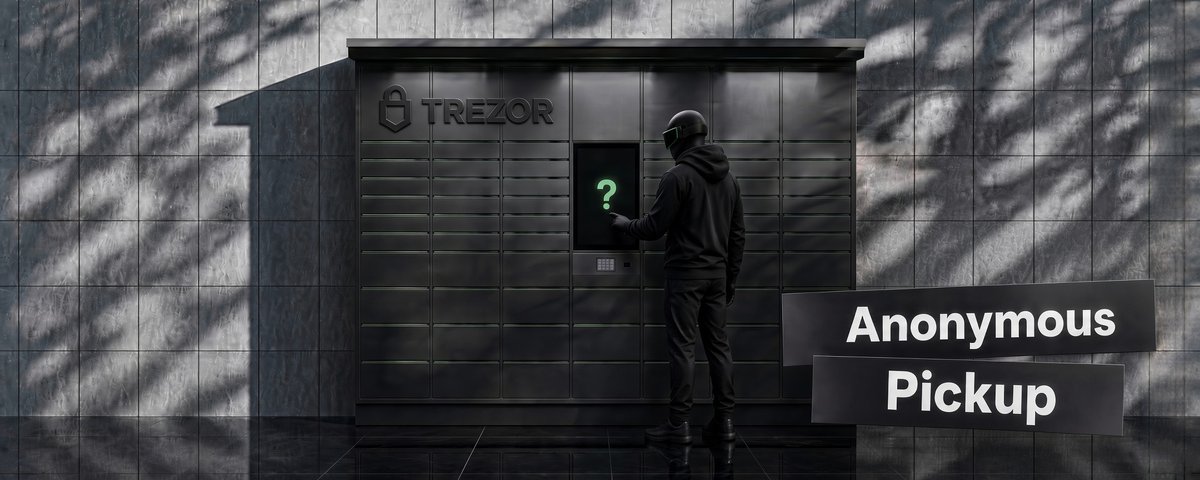
one thing i've started thinking about more while working around privacy in crypto:
we spend so much time trying to make the transaction private, while completely ignoring all the data created around the transaction.
your wallet can be non-custodial.
your funds can stay onchain.
your transaction can be private.
but if three different companies know your name, phone number, home address and that you bought a hardware wallet...
you've still left a pretty valuable trail.
the Trezor situation is a good reminder that privacy isn't only an onchain problem.

Hunter retweeted

I’m looking for a new team to join!
Past 7 years: distributed systems, developer tooling, and cryptography. Led teams at ChainSafe and NEAR, most recently at RISC Zero/Boundless.
DMs are open to any team working on difficult problems, especially in new domains for me!

in the old days (2 years/1 year ago), you could distinguish your self by ai finding non hallucinated severe bugs cheaply and fastly.
currently in the ai-era, where ai security tooling is everywhere with different triage boundaries preferences and same underlying models . what do you think is the logical distinguish here?
3
13
968
you really didn't know i do Solana anchor/pinocchio audits?
github.com/0xhuntoor

if only we were faster?🥲


Our teams are aware of reports of a potential security issue and are actively investigating. User funds are completely safe.
Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information.
Users should remain cautious of scams and should not trust unofficial links, messages, or requests for account information.

3
492
Hunter retweeted

my spidey senses are telling me the labs are, as we speak, using unguardrailed versions of their unreleased models to systematically reverse-engineer ALL of the internet’s software, apps, and games, then feeding the reconstructed source code straight into their training pipelines while simultaneously building guardrails to ladder-pull the rest of us
Hunter retweeted

After my time at Zellic, I’m now looking for Security Engineer or Security Researcher roles, especially in Web3 and protocol security.
I’ve worked on L1 clients, Solana, Cosmos, cross-chain protocols, system software, and browser security. If your team is hiring, my DMs are open.
Portfolio: github.com/gxh191/Security-P…

i know like 4 auditing firms almost operates explicitly on the same 20 trusted auditors circle.
the pricing between those firms is also insanely different.
What etches my head and derives me crazy is how they sell themself as providing more value (than other firms using same auditors) and how they justify the pricing difference
i expect more of this easily, those type of facilities (at least where i live) have the lowest cybersecurity practices
This quoted post is unavailable.
158
Honestly, this was more naive than i thought and i'm very disappointed.
The initial report is giving large Looking words, but technically this was a complete missed up security layering and employee devops.

1
3
265
Once you run deep in the code and comments start to go on top of each others, use this extension in addition to have a clean repo for latter more deep passes if you prefer
marketplace.visualstudio.com…

5
291
Most of my fixed bugs during engagement comes during last 20% of the audit duration.
This makes me feared to my stomach of underquoting a code and not delivering those valuable fixed bugs.
Private auditing is giving me nightmares.
8
390
Did we reach the level of live address poisoning yet?
like:
1. compromised signing infrastructure but we don't know the `to` address yet.
2. address `to` put into the signing infra
3. immediately generate a different owned to hacker an address that ends with same last 4 letters and show it to the signers
are we there yet?, or its still hard to generate, compute?
1
224
MEV bots have been doing this for years. But no thanks, AI is more fancy to create.
Some chains have subseconds finality, what ai is going to flag an abnormal value increase, process it, counter it?, or wouldn't it be better to have a simple faster script on top of the node infra?

5
378