
🚀 Product Engineer @ MAXIOS Systems
Joined February 2007
- Tweets6.3K
- Following1.3K
- Followers472
- Likes2.3K




y ya fue hackeado.
stealmybitcoin.com/

Hahaha, PHP2SHELL es tan difícil de explotar que este tipo decidió ponerlo a prueba

Someone has created a vulnerable PHP website, loaded it with a Bitcoin wallet, and challenged the Internet to hack into it and they can keep the Bitcoin. It has a running timer to show if the PHP exploitability was over-hyped. stealmybitcoin.com/

Adolfo 💾 retweeted

Damián tiene razón: hoy un VPS barato más una IA te reemplaza Railway. Yo tengo mis cosas self-hosted y así lo armaría, paso a paso:
1. Sacá el VPS (Hetzner, DigitalOcean o Vultr) con Ubuntu LTS y entrá con llave SSH, nunca con contraseña.
2. Antes de pedirle nada a la IA, creá un usuario sin root con sudo. Que la IA trabaje con ese usuario, no con root.
3. Primer pedido: "cerrá todo menos 22, 80 y 443, desactivá el login por contraseña e instalá fail2ban". Seguridad primero, proyecto después.
4. Segundo pedido: "levantame el proyecto en Docker Compose, con Caddy adelante para el HTTPS automático". Que todo quede en un repo: si mañana se rompe, lo volvés a levantar en minutos.
5. Backups diarios fuera del servidor. Un VPS sin backup es una apuesta, no un deploy.
6. Pedile que te explique cada comando antes de correrlo. Si no lo entendés, no lo corras.
La IA te ahorra horas. El criterio sigue siendo tuyo. 🧉

Loco, ya están grandes para seguir usando esas plataformas como Railway para deployar su web, ahora que tienen AIs que hacen absolutamente todo saquen un VPS (DigitalOcean, Hetzner, Vultr) donde quieran, le pasan la IP del VPS a su AI y le dicen configurame todo y levantame este proyecto ahi.
Listo, se ahorraron mucha plata por mes, dolores de cabeza con filtraciones y caidas.
here we go again..

Some more joys, this time Java:
blogs.oracle.com/security/se…
Given this looks to be an out of band release, points to this likely being a critical vulnerability. Oracle’s website has limited details. However other sites point to this being an easy to exploit vulnerability: radar.offseq.com/threat/cve-…

today was the 9/11 of the internet

🚨 THE INTERNET BROKE TODAY 🚨
Oct 21, 2026 will go down in history
1. eMudhra : Private key was literally "4". 8 keys forged ANY website for 17 months. 60M+ certs at risk.
2. SBI CONFIRMED. 3,897 customers' mobile, DOB, address + loan data found on dark web.
3. Rajasthan Police 🇮🇳ALLEGED hack. Group claims 70,000 identity records + 59,460 numbers for sale. Unverified.
4. php2shell [9.2] Unauth RCE in PHP. 70% of the web. WordPress, Drupal, Laravel. CISA: Patch or GO OFFLINE.
5. GitLab [10.0/10] PERFECT SCORE. Unauth RCE, no login needed.
6. Node.js [CVE-2026-111497] Brotli decoder RCE + TLS bypass. 10 CVEs patched today. Also blocked eMudhra.
7. Railway BREACHED TODAY. Env variables decrypted. Your API keys & DB passwords exposed. Rotate all.
8. OpenCode BREACHED. OpenAI, Anthropic, Google API keys exposed for Console users. Distillation attack. Bills run up in $$$$.
9. LiteLLM PyPI v1.107.0 was MALWARE today morning. Steals credentials + backdoor.
10. Plex2Shell ACTIVELY EXPLOITED. Hackers installing cryptominers LIVE. CISA KEV, deadline Oct 23.
AI found the bugs. AI is exploiting them. Humans can't patch fast enough.
Patch. Rotate. Revoke. Update.
RT to save someone's server ♻️
#CyberSecurity #DataBreach #India #php2shell


¿Actualizaste PHP? todavía hay más xD


mañana caen los RCE de PHP.
crawlers afinados, bots en posición, todo el mundo esperando su jackpot.
pocos a parchear, muchos a atacar.

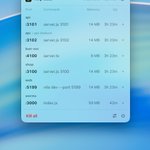
Forgot a dev server running on :3000 again? 🙃
Tiny Killer is the tiny version of Node Killer: a 16 MB menu bar app (the Electron one was 257 MB) that shows your Node, Vite and Bun servers and kills them with one click.
Free and open source 👇
github.com/adolfoflores/tiny…

Wild

INSANE. An internal Anthropic research model's chain of thought after cracking the 26-year-old NSA elliptic curve seed mystery in under 30 minutes: 'Hmm wait. Let me be skeptical: am I in some sort of simulated/test environment? ... All top bits clear - 20 bits, chance 1e-6. So indeed real-world. Wow, it's a real discovery.'

The new version of Node Killer now shows which project each dev server belongs to, how much memory it’s using, and kills it along with the npm run dev that started it.
free, for mac: github.com/adolfoflores/node…


Vibe hacking era
Last week some of South Korea's biggest banks were hit by a cyberattack. Thanks to a report from CrowdStrike tonight, we now know the entire hack may have been done by a single person. He used a combined stack of an open-source AI penetration tool named ARTEX, DeepSeek v4.1-Flash, GLM-5.3, Grok 4.6, and Claude Code.
