

The Intelligence for AI-Powered Security. Real-time defense requires real-time intelligence and visibility.
- Tweets2.8K
- Following1.5K
- Followers13.2K
- Likes1.4K






ALT The image is a detailed comparison of a security vulnerability in nginx version 1.31.8, labeled as CVE-2026-123007. The left section, titled "VULNERABLE / nginx 1.31.8," lists three actions occurring with queue response data, RST_STREAM, and WINDOW_UPDATE handling. The right section, titled "PATCHED / nginx 1.31.9," describes how the new version rejects the update, specifically noting connection closure and logged flow-control violations. A highlighted section confirms the accounting primitive, and the source is Censys Research, dated November 18, 2026.


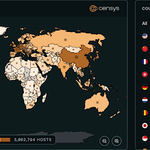
ALT Censys world map displays the number of hosts by country, with varying shades indicating host counts. The United States, China, and Germany are among the highest. A sidebar lists countries with their host counts: United States (54,132), Germany (23,894), China (21,345), Japan (11,995), France (8,649), Singapore (5,486), United Kingdom (5,038), India (4,385), and Ireland (4,034).


ALT Censys world map displaying a global distribution of hosts. The United States is highlighted with the highest number, followed by Germany, China, Japan, Canada, Australia, France, the United Kingdom, and Brazil. A color gradient indicates varying host densities, with darker shades representing higher counts.

ALT The image is an informative graphic titled "Java4Shell: OpenJDK Remote Code Execution [CVE-2026-114938]," with the "Censys ARC" logo and a "Rapid Response" label. The background has a gradient from dark to light.

ALT Censys orld map showing host distribution by country. The United States, China, and France have the highest counts, followed by Hong Kong, Germany, Netherlands, Belgium, Japan, and Singapore. A color gradient indicates varying host densities. Country totals listed on the right. Censys logo present.

ALT The image shows a digital advertisement for an eBook by Censys titled "Building an AI SOC: The Context Architecture Behind Defensible Security Decisions." The ad features the eBook cover with abstract network graphics in the background. A button reads "Get the eBook.


ALT Censys flowchart titled "Caishen / Optimizely Campaign" outlining the process of generating, serving, and deploying with various steps and entities involved. Each step includes detailed notes, arrows indicating the flow, and references to specific tools or services like Atob.js, Atob.beautiful.js, and ruleset loaders for Android and iOS. The layout is structured with color-coded sections for clarity.

ALT The image is an informative graphic titled "Java4Shell: OpenJDK Remote Code Execution [CVE-2026-114938]," with the "Censys ARC" logo and a "Rapid Response" label. The background has a gradient from dark to light.

ALT Webinar promotional image for 'From Internet Exposure to Investigation: Building the AI-Enabled SOC' featuring speakers from Dropzone AI and Censys: Himaja Motheram, Robert Crisp, and Joe McMann. Scheduled for 11:30am ET, virtual event.


ALT A Censys world map with varying shades indicating host counts by country. Darker areas represent higher counts. A sidebar lists countries and their total hosts: United States with 10,395, China with 3,642, Germany with 1,443, France with 301, Iran with 289, Australia with 223, Russia with 214, Singapore with 80, and Ireland with 70. The Censys logo is displayed at the top.