

The Premier Cybersecurity and Compliance Services leader. This profile is not monitored. Please find us on LinkedIn, Threads, Bluesky.
Greenwood Village, CO
Joined December 2011
- Tweets6.3K
- Following1.7K
- Followers3.2K
- Likes3.6K





Pinned Tweet
The federal government is the largest buyer of IT products and services. As new security regulations emerge, many cloud service providers are considering a FedRAMP® ATO. Discover key factors shaping their decisions: ow.ly/H3ma50TlubR @omdia #publicsector #fedramp

Existing audits may cover familiar cybersecurity controls, but CCPA requirements can extend into controls that reduce the risk of misuse, including data tagging, masking, and third-party contract oversight.
Check out our latest blog: coalfire.com/the-coalfire-bl…

Good process + AI = acceleration. 🚀
Bad process + AI = accelerated failure. 😵💫
In Part 2, John Dwyer looks at why governance has to be designed into the process.
👉 Read Part 2: coalfire.com/the-coalfire-bl…

In healthcare, PCI is rarely just PCI.
Scoping the cardholder data environment surfaces systems, data flows, vendors, and control owners that other assessments will revisit. The reports may stay separate. Our understanding of the environment should not: coalfire.com/insights/resour…

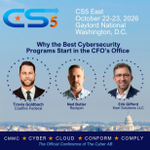
What happens when cybersecurity moves into the CFO’s office? Travis Goldbach joins Redspin and Kieri Solutions LLC to dig into why the best cybersecurity programs start there.
Catch the conversation October 22–23 in Washington, D.C.
Learn more: cs5east.org/agenda/

AI adoption is moving fast. Can you see what your agents can access? 🔎
Our VP of Defensive Services, Neil Wyler "Grifter" on @hackernoon: hackernoon.com/shadow-ai-age…

Join us and @FableSecurity on Oct. 20 for a practical field guide to generative AI social engineering, with live Q&A at the end.
Bring your questions. Save your seat: streamyard.com/watch/qimaWet…

CCPA cybersecurity audits can extend beyond traditional system boundaries to include the systems that process or provide access to covered personal information, including relevant enterprise and vendor-managed systems.
👉 Read the blog: coalfire.com/the-coalfire-bl…

Before we automate with AI, we should ask a simpler question: do we need AI at all? ❓
John Dwyer opens his four-part series with the questions leaders should ask before they build. 👏
👉 Read Part 1: coalfire.com/the-coalfire-bl…

🎤 We’re speaking at CS5 Conference East.
Travis Goldbach, VP of CMMC, will unpack why the best cybersecurity programs start in the CFO’s office.
Catch the conversation October 22–23 in Washington, D.C. Then stop by Booth #43. 🔐
Learn more: cs5east.org/agenda/

We’re expanding our global delivery capabilities with a new office in Buenos Aires! 🌎
As our CEO, Brad Little, shared: “Buenos Aires gives us access to exceptional talent while strengthening the connectivity of our global teams.”
Read the press release: coalfire.com/insights/news-a…


🤖 In @PCISSC’s latest AI Exchange: Innovators in Payment Security our VP Andy Barratt explores what responsible AI adoption looks like in practice.
🔥 Read the full conversation: blog.pcisecuritystandards.or…

.@FedRAMP Ready under Rev. 5 is no longer a holding pattern.
Providers now need to move toward full certification by the later of their next annual assessment expiration or 11/17.
We explain how to turn Ready status into a practical certification plan: coalfire.com/the-coalfire-bl…

At the @WWHackinFest, Jack Hooker, Principal US, will explore the vulnerabilities hiding in enterprise drones and what security teams need to know.
“Bad Birds: Discovering Vulnerabilities in Enterprise Drones”
📍 Deadwood, SD
⏱️ 10/8 @ 3:55PM
Join us 👉 web.cvent.com/event/085f4a29…

At @WWHackinFest, Matt Bangert @bngrsec, will show how voice attacks can scale far beyond traditional testing and why security teams need to rethink their approach.
🎤 “Your Security Program Has a Blind Spot and It Answers the Phone”
⏱️ 10/8 @ 2:45 PM
web.cvent.com/event/085f4a29…

.@FedRAMP is raising the bar for how cloud providers manage vulnerabilities.
The lesson for security leaders: better tools are only part of the answer. Strong programs connect evidence to sound judgment and clear ownership.
🔎 Read our analysis: coalfire.com/the-coalfire-bl…

PCI Services That Support the Full Assessment Path 🤝
From scoping and readiness to assessment and testing, we help you move through PCI as your experienced partner: coalfire.com/go/pci-complian…

We’re kicking off the @WWHackinFest with Neil Wyler's “Grifter” keynote, “It Feels Like One Long Con: Building a Community with Curiosity and Questionable Decisions.”
📍 Deadwood Mountain Grand, Main Stage, Track 0
🗓️ October 8, 2026
Join us: web.cvent.com/event/085f4a29… #WWHF

We believe PCI guidance has to account for the technology behind the payment flow, especially when cloud and connected services are part of the environment.
Get PCI guidance built for the technology behind your environment: coalfire.com/go/pci-complian…

What does FedRAMP 20x mean for your organization?
Join @coalfire, Paramify, and A-LIGN for the FedRAMP 20x Road Show in New York on 9/22 for practical answers on existing programs, continuous monitoring, and preparation.
There is still time to register: coalfire.com/insights/news-a…

Breaking into the @FedRAMP Marketplace? Start here. 🚀
Our FedRAMP Go-to-Market Playbook delivers practical guidance for navigating market entry and planning for long-term success.
Download it today: coalfire.com/insights/resour…
