
Senior Contributor @Forbes Contributing Editor @pcpro - [email protected] - "All My Opinions Are Belong To Me"
Joined February 2007
- Tweets21.5K
- Following3.3K
- Followers14.8K
- Likes17.2K


Pinned Tweet
You can find a searchable archive of my online work, going back a good few years, at Authory. Check it out.
#journalism #writing #infosec
authory.com/DaveyWinder


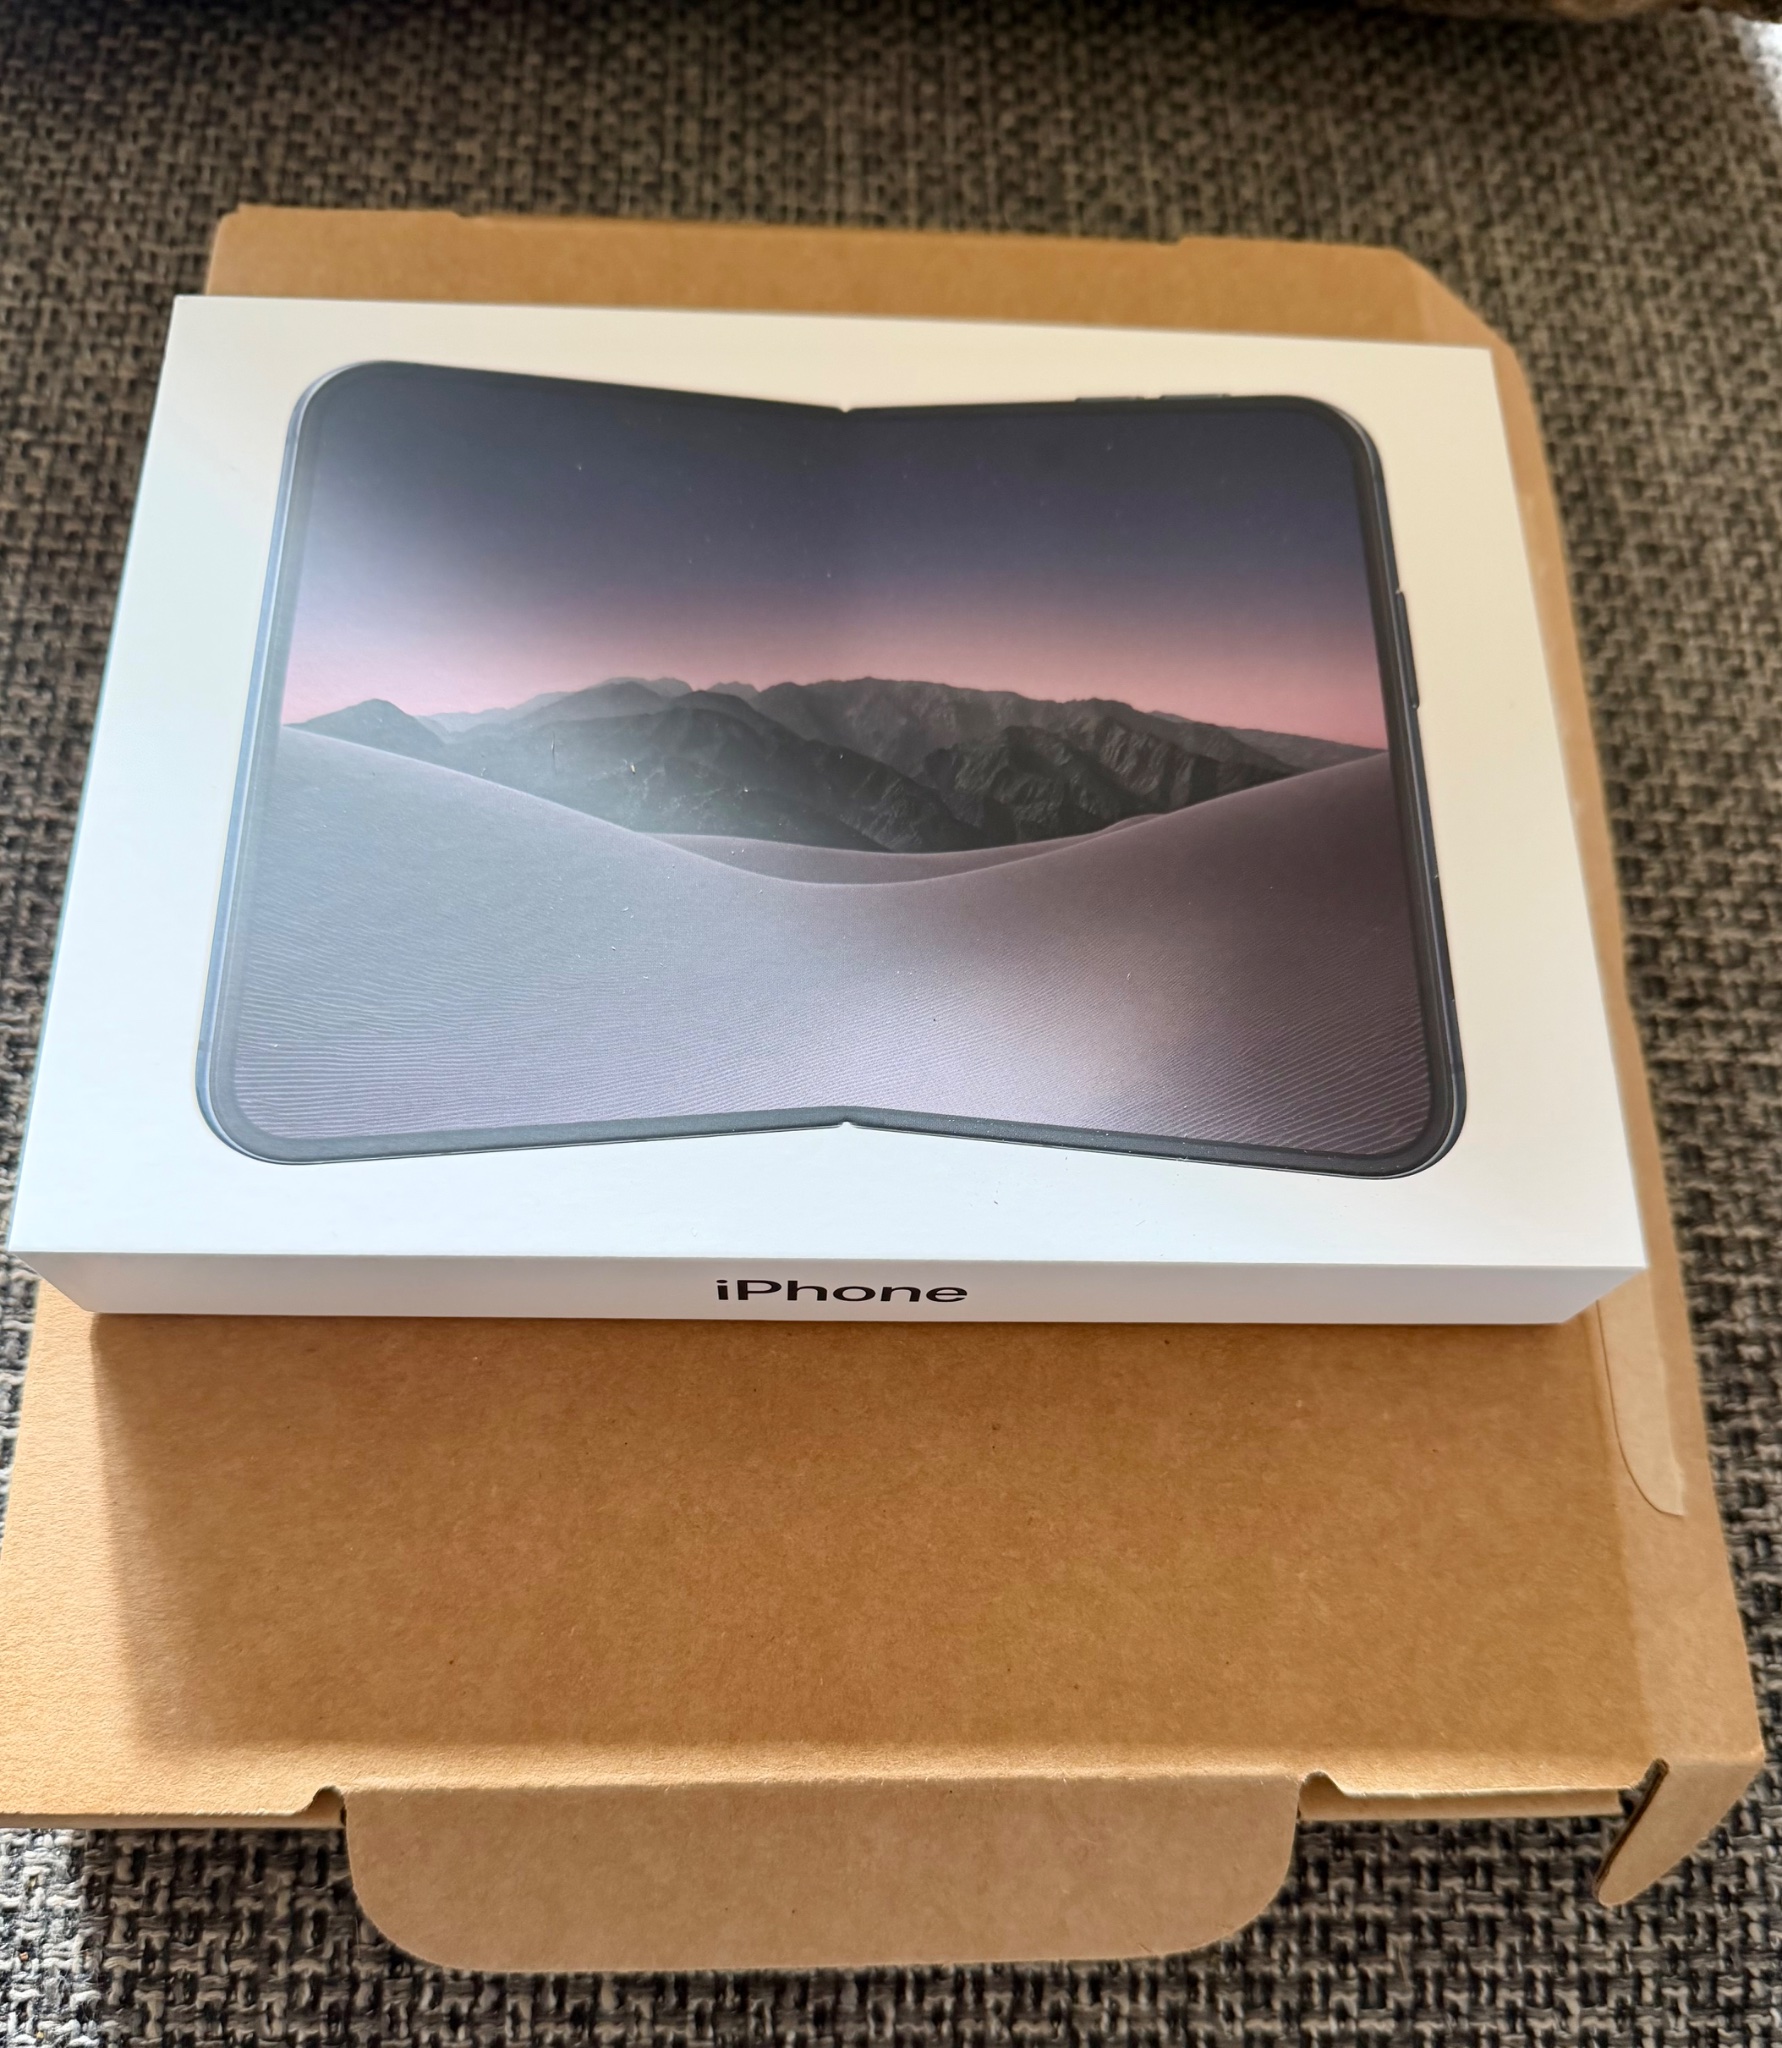
The perfect little travel charger for the #iPhoneDuo
Almost like it was made for the Duo. Really good in the hand when folded, OKish when unfolded.
Anker Nano Power Bank,5,000mAh - £20 from Amazon.


Reasons NOT to buy the iPhone Duo (according to x) ✍️
❌ You can’t drop it off a building without it breaking
❌ You can’t pour a handful of corse sand directly into its hinge without it breaking
❌ If you stab the inside screen with a knife more than twice it just breaks
❌ If you bend it backwards with so much force it makes you physically shake, it breaks
❌ Some app developers haven’t redesigned their apps in the last 5 days
❌ If I get one of the tiny fraction which are already broken, it doesn’t matter if Apple replace it immediately, under warranty, you should still absolutely not buy it just in case.
What else am I missing?
Great “service” from @RoyalMail today. Four items collected, including two for special delivery (total value £850) and two Amazon returns. Guy turns up as expected, with the labels, we ensure they are all on the right packages. This was at, checks doorbell video footage, 2.45pm. Yes, I have the collection on video, and screenshots taken.
Have not had usual collected emails, Amazon reports collection might be delayed.
Emails at 7.03pm from Royal Mail say it was “unable to fulfil your collection request” on all four items.
Of course, customer service phone shuts at 6pm.
Yes, I’m venting. Not least as it will no doubt be a right PITA hassle with both Royal Mail (although SD items have proper insurance) and Amazon to get sorted. And I’m not on best place, healthwise, to deal with such things.
Now all sorted. Looks like a standard system message that goes out when items not scanned before some arbitrary cutoff point. Both special delivery parcels arrived OK, both Amazon returns now showing as picked up. @RoyalMail really should do better with sending out such emails tbh.
Arse. Leak from bath, water came through kitchen light downstairs. Stopped when bath had emptied, so it’s not going to be a big deal. But insurance company is so snowed under with the storm stuff, can’t get the ‘emergency’ cover plumber to us until Thursday evening. No biggie, won’t use bath/shower in meantime (who doesn’t love sharing a strip wash with their partner) but a pain nonetheless. Talk about bad timing…
I’m returning the Duo Folio case. Looks lovely, but I’ve found it to be too much hassle for me in use since Friday. Front flap awkward when using Duo folded. Kickstand really not great, for me at least, I prefer a MagSafe ring thing tbh.
Most of all, though, it’s flimsy and falls off when opening/closing up phone too much for my liking.
Your mileage will vary, naturally, but it’s not for me. Using a vegan leather JEtech case (mag backplate and hinge cover, no adhesives) with a screen protector, at least for now.
Excellent advice.

⚠️ WARNING: Things to avoid with your iPhone Duo.
• Don’t rub keys or coins against the inner screen
• Don’t dig your fingernails into the inner screen
• Don’t scrape the titanium frame with a knife
• Don’t rub chainmail armour against the display
• Don’t peel off the screen protector
• Don’t pour dirt into the hinge or ports
• Don’t bury it in the sand
• Don’t force it closed if something is stuck
• Don’t fold it 10,000 times just to see what happens
• Don’t put it in a freezer at -20°C and repeatedly fold it
• Don’t hold a lighter up to the screen
• Don’t sit on it when it’s unfolded
• Don’t bend it backwards
• Don’t twist the phone to test its strength
• Don’t drop it down a flight of stairs
• Don’t run over it with your car
Or if you do, make sure you have AppleCare+ 😆

The perfect ring piece for the iPhone Duo with Folio - looks even better IRL, the blue is a great match. Shame the Apple logo isn’t centred, but maybe that’s just my OCD kicking in…


I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.
