

Official account of MalwareMustDie, NPO & public account @unixfreaxjp Info: https://teapaw.org/t.co/131r5UW4bF Blog: https://teapaw.org/t.co/lUnpKnXOqV
Joined September 2018
- Tweets746
- Following150
- Followers6.1K
- Likes351




#Updates on #malwaremustdie #MMD-073 #blog:
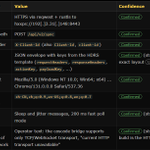
1/ #EasyShell tool's developer released #Go #C2 code in github 1.5days ago (not Client code/#Rust) which I reckon/assess instantly & wrote addendum on #Linux/EasyShell blog in many sections (see attached chapters).
2/ The builder by default compiled #MacOS & #LoongArch despite adversaries' needs. (PoC: In stage_http_listener.go the one-click stager writes all 7 download variables in a fixed order: #darwin_amd64, #darwin_arm64, l64, l32, a32, a64, l128. There is no setting or flag to drop one.).
URL to 1st of many addendum: blog.malwaremustdie.org/2026…


Unsure if there is already infected #macOS by #EasyShell #RAT, but I guess signatures alone aren't helping, so I've added a SelfCheck guideline in the #blog so #Mac users can run initial checks themselves.
It's #advisory only, so please read & understand the commands before pasting those into your terminal.
Rgds, @unixfreaxjp #MalwareMustDie
Advisory link: blog.malwaremustdie.org/2026…

I guess we just found the 1st #LoongArch (258) #cpu #RAT #malware (#Linux/EasyShell made in PRC) virustotal.com/gui/file/7fbe… rgds! @unixfreaxjp #malwaremustdie
New #BLOG: #MMD-073-2026 - #Linux/EasyShell, a new #Rust #RAT implant and #beacon aims Linux and #MacOS blog.malwaremustdie.org/2026…
Analysis by @unixfreaxjp of #malwaremustdie
Detection signature: github.com/unixfreaxjp/malwa…
thanks @0xrb for great support!


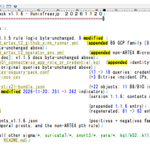
#Artex SigPack v1.1.6 is out! 7th updates, #BehaviorFirst, #TLP:CLEAR, confirmed+tested. Added: 5 recent events #cti sources: 91APP (#Taiwan), #EU Commission (#Europe), #Bitrise (global CI/CD), #Spectrum , #Microsoft agent-framework (global/supply-chain) drive v1.1.6. (details see attached 2 images)
Ref: blog.malwaremustdie.org/2026… Sigs at #malwaremustdie's Github: github.com/unixfreaxjp/malwa…
Regards! @unixfreaxjp #aof #signature #detection #playbook


#Artex #signature detection pack v1.1.5 is out! 6th updates, did it after day work. #BehaviorFirst, #TLP:CLEAR, confirmed+tested. Added:
- #Barracuda’s 44h machine-speed cloud intrusion: CI/CD build steps that encode secrets to slip past job-log masking (B7) &
- A read-only #Kubernetes hostPath container harvesting node creds (B8) plus the widened intentID & wallet hunt
- Deferred: artex.lol re-tier, 0.0.0.0:8788 self-audit, D1 UA/TLS hunt, non-Barracuda chronology rows
Ref: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
Regards! @unixfreaxjp

I made online presentation about #ARTEX Signature Detection & its #Playbook, to make it clearer explanation about how we can deal with this type of #AI/#LLM #cyberthreat in the future too. #malwaremustdie
Video: youtube.com/watch?v=hrcIvTZg…
Ref, blog: blog.malwaremustdie.org/2026… & github: github.com/unixfreaxjp/malwa…
#Artex #signature detection pack v1.1.5 is out! 6th updates, did it after day work. #BehaviorFirst, #TLP:CLEAR, confirmed+tested. Added:
- #Barracuda’s 44h machine-speed cloud intrusion: CI/CD build steps that encode secrets to slip past job-log masking (B7) &
- A read-only #Kubernetes hostPath container harvesting node creds (B8) plus the widened intentID & wallet hunt
- Deferred: artex.lol re-tier, 0.0.0.0:8788 self-audit, D1 UA/TLS hunt, non-Barracuda chronology rows
Ref: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
Regards! @unixfreaxjp
#Artex #signature detection pack v1.1.4 is out.
Added: #BehaviorFirst: foothold-gated #WinRM/#PsExec lateral-movement correlation from the #ExtraHop thx ScopeWeaver lab, plus two fork user-agents, and now tracking the new Ayven fork (thx!).
Confirmed/append-only/tested/is on #malwaremustdie's GitHub. PS: Detect the behavior, not the name. Rgds/@unixfreaxjp
Notes: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
Thank you to #infosec & #journalism communities for recognizing our work!
海外と日本国内のジャーナリズム皆さま、いつも有難う! ai-industry.jp, @BleepinComputer @securityaffairs
ai-industry.jp/trends/fbi-fl…
bleepingcomputer.com/news/se…
securityaffairs.com/203230/h… #malwaremustdie

#SecurityAffairs has published a nice summary of our #artex sigpack work here: securityaffairs.com/203230/h… written by a respected #infosec senior Mr. Pierluigi Paganini @securityaffairs , thank you, sir!
20 new attack nodes within 2hours.. dangerously impressive.. #artex (+artex-like nodes).
src: #shodan. Advise: Start dork shodan/censys & build #blacklist folks, eliminate ip you really don't need to communicate with, #pewpew is on.

#Artex #signature detection pack v1.1.4 is out.
Added: #BehaviorFirst: foothold-gated #WinRM/#PsExec lateral-movement correlation from the #ExtraHop thx ScopeWeaver lab, plus two fork user-agents, and now tracking the new Ayven fork (thx!).
Confirmed/append-only/tested/is on #malwaremustdie's GitHub. PS: Detect the behavior, not the name. Rgds/@unixfreaxjp
Notes: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
4th ruleset update of #Artex signatures pack v1.1.3 (minor) is out. #Playbook for dev works well (no update/v0.4). Added Sophos' X-Ops "HOLD" indicators (finally confirmed), & added Testing.md a #howto test /tools script.
Read: 1)#blog addendum: blog.malwaremustdie.org/2026… and 2)#malwaremustdie github: github.com/unixfreaxjp/malwa… - best regards - @unixfreaxjp
☩MalwareMustDie retweeted
4th ruleset update of #Artex signatures pack v1.1.3 (minor) is out. #Playbook for dev works well (no update/v0.4). Added Sophos' X-Ops "HOLD" indicators (finally confirmed), & added Testing.md a #howto test /tools script.
Read: 1)#blog addendum: blog.malwaremustdie.org/2026… and 2)#malwaremustdie github: github.com/unixfreaxjp/malwa… - best regards - @unixfreaxjp
4th ruleset update of #Artex signatures pack v1.1.3 (minor) is out. #Playbook for dev works well (no update/v0.4). Added Sophos' X-Ops "HOLD" indicators (finally confirmed), & added Testing.md a #howto test /tools script.
Read: 1)#blog addendum: blog.malwaremustdie.org/2026… and 2)#malwaremustdie github: github.com/unixfreaxjp/malwa… - best regards - @unixfreaxjp
Just to put things right:
1/ Many read my #ARTEX signature release as "an IOC list". It isn't. The #IOCs expire within a year by design. The real release is the workflow: how to turn the next ARTEX-style attack into detections as fast as the attacker moves.
2/ ARTEX is an #LLM harness. Swap the model, prompts or infra and every IOC changes. What changes much less is how an agent behaves: machine-speed recon chains, ~1/s #PasswordSprays with rotating UAs, self-correcting API retries, systematic record enumeration.
3/ So the pack is behavior-first. Those patterns live in Sigma correlations, Sentinel KQL and Zeek SumStats on the upper network layers, not in packet filters. IPs are clearly labelled T3/T4 context for retro-hunting what already happened.
4/ The #playbook is the core: verify the source, classify how specific an indicator really is, assign a tier, route it to the right format, expire it. We applied it to four campaigns with an LLM assisting and humans gating every verification step. Next trail, same loop.
5/ That's the big picture: attackers use LLMs to compress weeks into hours. Defenders can use LLMs to compress "new report → tested detection" into hours too, as long as humans keep the verification gates. We must defend atacker's powered LLM/#AI with AI.
6/ The Zeek section shows how to carry the same behavioral logic into network sensors you already run. Playbook, rules and tests: [link]. Break them, send FP/TP reports. That's how this grows.
#BLOG: #MMD-072-2026 - #ARTEX detection signature pack - from #IOC w/#playbook : blog.malwaremustdie.org/2026…
Artex detection signature pack's repo: github.com/unixfreaxjp/malwa…
Read the playbook carefully, asses & test before apply, you can use my python scripts in /tools dir and see /tests result in github repo beforehand. Posted to inspire #block-ing this threat for defenders in FIRST(dot)oeg or xCERTs and xSIRTs. Hope helps. - @unixfreaxjp Nov,2026


#BLOG: #MMD-072-2026 - #ARTEX detection signature pack - from #IOC w/#playbook : blog.malwaremustdie.org/2026…
Artex detection signature pack's repo: github.com/unixfreaxjp/malwa…
Read the playbook carefully, asses & test before apply, you can use my python scripts in /tools dir and see /tests result in github repo beforehand. Posted to inspire #block-ing this threat for defenders in FIRST(dot)oeg or xCERTs and xSIRTs. Hope helps. - @unixfreaxjp Nov,2026
#Blog: #MMD-071-2026 #KinsingBot a "bad-bad"-designed Linux botnet a while ago.. until recent.
blog.malwaremustdie.org/2026…
(I posted this to answer requests on new analysis #education materials. I rendered by chapters accordingly. Thanks for sticking with #malwaremustdie! Enjoy! - @unixfreaxjp, Nov 2026)


BLOG: MMD-0070-2026 - Once upon a time, Linux/Hajime hexstring-pushed a tiny ARM ELF fileless downloader: blog.malwaremustdie.org/2026…
#malwaremustdie (#research & #education purpose)
For followers & IR folks. Updated fakedns python tool with bugfix (for py 2.7) and upgraded to v2 for py 3.11+ compatibilities. Please use it with tests beforehand.
This updates inspired by code originally made by Francisco Santos & I still use it for +/- 20years (since Sat, 15 Apr 2006/thanks) - @unixfreaxjp
PS: feel free to improve.
py 3.11+:github.com/unixfreaxjp/malwa…
py 2.7:github.com/unixfreaxjp/malwa…
#malwaremustdie friends
