
The latest research and news from Unit 42, the Palo Alto Networks (@paloaltontwks) Threat Intelligence and Security Consulting Team covering incident response.
- Tweets3.1K
- Following81
- Followers72.3K
- Likes256






ALT The image is a flowchart illustrating the "ClickFix Campaign" by RomulusLoader. It outlines various stages of the campaign, including "Platform Lure," "ClickFix – Win+R," "Decimal IP Stager," "MSI Dropper," "AMSI Bypass," "Fileless PE Load," "VBScript PS → Delete," "Binary Table Staging," "C2 Beacon," "Persistence," "Process Injection," and "Credential Access." Each stage includes brief descriptions of the actions taken during that phase.

ALT Login page for "Romulus" with username and password fields, and a "Log in" button.

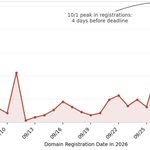
ALT Graph of normalized domain registration volume from 08/01 to 11/01 in 2026. Sharp peak on 10/01, labeled as "peak in registrations: 4 days before deadline." Data points are connected by a line chart, with shaded area below the curve.

ALT A screenshot of a scam online casino site. The page features a prominent illustration of a bull in a tuxedo holding a sign that says "Diversão em Primeiro Lugar." Surrounding text describes various features and promotions, such as a welcome bonus and payment methods.

ALT A screenshot of scam domain Bulls Bet casino website in Portuguese.

ALT Network diagram illustrating relationships between URLs, file/sample hashes, hostnames, and IP addresses. A legend at the bottom explains icons: URL, file/sample hash, hostname, and IP address.

ALT A flowchart titled "Multi-Stage Attack Flow: From Reconnaissance to Business Logic Abuse" illustrates six stages. Stage 1: "Recon" involves broad reconnaissance with scanned public IPs, S3 buckets, and internal hostname. Stage 2: "Mapping" includes application mapping with software bundles, source maps, and OpenAPI specs. Stage 3: "Identity" focuses on IdP probing with login, recovery, and OAuth flows. Stage 4: "Pivot" entails pivoting to exposed API and falling back to API surface. Stage 5: "Abuse" involves business logic abuse with actions to escalate and obtain functions. Stage 6: "Write" covers unauthorized API actions and executing commands.

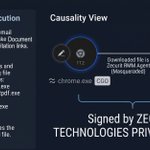
ALT The image illustrates a phishing lure and execution scenario. It begins with a phishing email containing links like "Docusign.exe" and "ViewDoc.exe". The "Causality View" section shows a flow where a file named "Zecurit RMM Agent" is downloaded and disguised. The process involves "chrome.exe" and "ViewDoc.exe" applications.

ALT The image is a screenshot of a phishing email that appears to be from DocuSign. It informs the recipient about a new document available for review regarding an account update. A prominent yellow button labeled "VIEW COMPLETED DOCUMENT" is displayed. There is a warning not to share the email, as it contains a secure link. The URL shown is suspicious and differs from a standard DocuSign address.

ALT The image shows a web browser with a warning about a downloaded file named "ViewDoc.exe" potentially harming the device. Options are given to "Keep" or "Delete" the file. An inset window displays the file's properties. Another inset highlights the digital signature details. Microsoft Teams is open in the background.

ALT A flowchart illustrating a cyber attack process in four steps: 1) Initial Access via phishing email; 2) Redirect through a deceptive link; 3) Payload Delivery with signed RMM installers; 4) Execution and Impact leading to endpoint compromise with the silent installation.

ALT Process chain diagram illustrating the web server (httpd.exe) spawning multiple cmd.exe processes for scanner validation commands in a cybersecurity program.

ALT The image shows a PHP code snippet for a first-stage webshell.


ALT The image shows two phishing pages designed to mimic legitimate websites. Both pages contain misleading login prompts and branding elements to appear authentic.

ALT The image shows two phishing pages mimicking site builders. Each page highlights the suspicious URL at the bottom.

ALT Screenshot displaying a pop-up message titled 'Payment update required' over a blurred background. The right pane shows a web page's source code.

ALT Screenshot of a chat-app code snippet designed to send form data to a Telegram bot.


ALT Flowchart illustrating a cyber attack involving Casbaneiro banking Trojan and a malicious Chromium extension. It shows stages from phishing emails to remote sessions, including ScreenConnect, VMlauncher.exe, and Casbaneiro payload.

ALT A PowerShell script is displayed. The screenshot highlights a browser extension file drop using a PowerShell script.

ALT The image shows a screenshot from the VirusTotal website. It features analysis details of a scanned file, including a community score, URL, file type (text/plain), and the last analysis date of "27 days ago."

ALT The image shows a sequence of command lines and a flowchart related to a phishing attack leading to RMM installation. Text and arrows point to the Delphi payload and legitimate installer retrieval (top) and the sequence of events from phishing to RMM installation (bottom).

ALT Flowchart illustrating a seven-step malware attack using a fake PuTTY MSI with Nodja and EtherHiding Loader.

ALT A smartphone displaying an app interface is centrally placed over a background featuring an open book with an image of an ancient structure. The text on the smartphone reads "PUTTY," which appears to be an app for sharing print articles online. A button below the smartphone encourages downloading the app, and there is an "Available on the App Store" label.

ALT The image shows a list of HTTP requests with details such as source IP addresses and date/time. A specific entry highlighted, marked as a "Webshell Request from Threat Actor" with a red border.

ALT A diagram titled "Exploitation process chain" shows a sequence of processes. A highlighted step indicates an issue with the description "XMRig Config disguised as JPG." Below the diagram, a detailed table lists timestamps, host, user names, and actions related to the process execution.

ALT Screenshot of the C3Pool Monero mining dashboard.

ALT Flowchart titled "C2Agent: an LLM-operated Windows implant" outlining the components and processes of a system with 'MCP, Skills and Living-off-the-AI.' It includes sections: Delivery Chain with stages 'Stager,' 'copilot.txt,' 'Injected,' and 'Beacons to C2,' and 'On the Host: an LLM Runs the Operation' with roles 'Operator,' 'LLM tool loop,' 'Living off the AI,' 'MCP client,' and 'Remote skills.' Additional details and steps for each component are provided in labeled sections.