
Site Reliability Engineer, GitHub Star
In front of a computer
Joined August 2007
- Tweets79.5K
- Following2.2K
- Followers8.3K
- Likes742





Outsider retweeted

Ghostty 1.4 is now out! Full Kitty graphics with animation (the first terminal besides Kitty to do it), scrollback compression for much lower memory usage, macOS 27 support, a new OpenGL renderer on Linux, ghostty +ssh, big performance gains, and hundreds more changes.
The highlights:
- Scrollback compression: scrollback compresses ~90+% on average, meaning your terminals use that much less live memory
- Huge memory savings across the board: no single large thing, just lots of good improvements lowers memory usage everywhere, netting anywhere from 50 to 90% less memory usage depending on workload
- Kitty graphics is now 100% complete, including animation and relative placements, after a full conformance pass against the spec and Kitty itself
- The Kitty clipboard protocol, with an image preview when a program asks to read your clipboard
- Split drag and drop on Linux, including between windows
- ghostty +ssh installs terminfo on remote hosts automatically, so things just work over SSH
- Lots of terminal emulation accuracy fixes
This release is 7 months of work from 172 contributors over 2,889 commits. It also fixes 10 security advisories, so please update.
Full release notes: ghostty.org/docs/install/rel…

내일 Pro and Tell 애플 이벤트인데 그때 사전예약을 시작하는 M6 맥북 프로가 나왔네요. 내일은 새 라인업 발표에 집중할 생각인가보군요.
apple.com/kr/macbook-pro/

Outsider retweeted
JetBrains IDEs are now powered by libghostty! This brings huge feature and performance improvements to JB terminals! Based on their own annual reports, that's over 12.5 million active users across all platforms about to get a libghostty-powered terminal. blog.jetbrains.com/platform/…
I'll repeat myself: libghostty is and was always the primary goal of the Ghostty project (I said this in the first public talk I ever gave about Ghostty). The importance and impact of a free, liberally licensed, high quality terminal emulator library that runs anywhere and everywhere dwarfs any single terminal emulator application on its own.
I've estimated Ghostty's (GUI, not libghostty) own users at around a couple million. Overnight, 6x that are using a libghostty-powered terminal. From one integration.
Happy to see this, happy to hear JetBrains had a positive experience, and looking forward to continuing to improve and ship a stable libghostty tag soon!


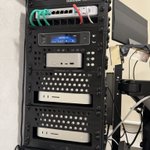
[New Post] 3D 프린터로 만든 10인치 서버 랙
blog.outsider.ne.kr/1816

Outsider retweeted

Meet Dessa, our speech model trained from scratch on human conversation.
Hear it for yourself: block.xyz/dessa
Outsider retweeted

PHP2Shell 취약점이 어떻게 동작하는지를
단계별로 간단한 애니메이션과 함께
배워보는 웹페이지
hackerschool.org/HackingGame…

Outsider retweeted

Prometheus & Observability - 2026년 10월 소식 promkr.substack.com/p/promet…
Outsider retweeted
속도전이 시작되었음.
누가 AI를 이용해서 먼저 취약점을 찾아내고
그 취약점에 대한 보완책을 찾아내는가의 전쟁.
당분간 신사업을 위한 개발을 할 수 있을 것인가에
커다란 물음표가 생기는 티핑포인트가 된 듯한 느낌.

netflixtechblog.com/beyond-a…
Netflix에서 API의 브레이킹 체인지가 발생할 때 어디에서 사용하는지 파악하기 어려운 문제를 해결하기 위해 SCIP로 각 저장소에서 라이브러리 버전과 심볼의 관계를 저장하고 Quasar라는 시스템으로 보내서 PR을 올릴때 Quasar을 통해 파악할 수 있게 함.

auth0.com/blog/what-is-id-ja…
에이전트 인증쪽은 ID-JAG쪽으로 모일거 같다. 계속 보다보니 조금씩 이해되고 있긴 한데 실제로 만들고 사용해봐야 확실히 이해될 듯 하다. 이문제도 해결하려고 한참 고민하다가 다른 팀에 맡기고 다른 쪽을 더 집중하고 있긴 하지만....

linkedin.com/blog/engineerin…
LinkedIn이 사용자 이벤트를 수집하는 시스템이 낙후되어 새로운 시스템을 구축하고 이벤트를 점진적으로 전환하면서 최적화한 과정.

Outsider retweeted

I’ve left Anthropic after more than a year of working on Claude Code and seeing it scale larger than I ever imagined.
I have really loved working at Ant and believe deeply in the mission, and most of all, the idea of a race to the top.
The idea that if we work hard and responsibly, we can raise the bar and inspire others to great outcomes. And if we all push each other to be better, things can be radically good. I will carry the spirit of this with me forever.
My colleagues at Anthropic are the most talented, thoughtful, competent, and earnest people I have ever met. I am glad they are at the wheel and trust them deeply.
To the community on X, thank you for everything. You’ve made this the most fun (and sometimes stressful) job I’ve ever had.
For me, it is time for a bit of a break before diving into something new.
If you want more excellent Claude Code content, you should follow @addyosmani , @lydiahallie, @_catwu, @ClaudeDevs and of course @bcherny who started it all.
emudhra.we-have-a-problem.co…
eMudhra가 25년 4월 만든 중간 인증서의 프라이빗키가 너무 약하게 만들어져서 누구나 복구할 수 있었고 이번에 제보되어 모든 브라우저와 플랫폼에서 차단 조치가 이루어졌다.
많은 신뢰 검증 장치가 있겠지만 그럼에도 항상 빈틈은 생기기 마련이다.
Outsider retweeted

[펀글][PHP 보안 문제 시계열 순 요약]
2024년: PHP의 잠재적 취약점 발견
외부 감사로 인해 메모리 관리 문제를 인식.
그러나 수정 방침이 정리되지 않아 약 2년간 대응이 지연됨.
↓
2026년 8월: 중대한 임의 코드 실행 위험 확인
Calif(보안 기업)와 OpenAI 등이 인증 없이 임의 코드 실행(RCE)이 가능한 공격 경로를 보고.
PHP 개발팀이 수정을 최우선으로 진행.
↓
10월 21일 0시경: 취약점 정보 사전 유출
수정 패치 공개 전에 2건의 CVE 번호가 Hacker News에 게시되어, 그것이 SNS나 게시판으로도 확산됨.
※이 시점에서는 기술적 세부 사항은 포함되지 않았음.
↓
10월 21일 4시 30분: PHP 공식이 긴급 공지
정보 유출에 따라 패치 공개 예정일을 22일에서 21일 23시(일본 시간)로 앞당김.
↓
10월 21일 5시경: 공격 실증 영상 오공개
Calif가 공격 동작 영상을 실수로 공개.
즉시 삭제되었으나 복제본이 확산되어 공격 코드 개발이 가속화됨.
↓
10월 21일: 연구자들에 의한 미검증 정보 확산
패치 공개 전에 @J4ck3LSyN 등에 의해 취약점 원인이나 재현 방법이 SNS 등에서 발신되는 움직임 발생.
↓
10월 21일 16시 41분: 수정된 바이너리 선행 공개
Chainguard(보안을 전문으로 하는 미국 기업)가 공개 예정인 약 6시간 전에 수정된 컨테이너 이미지를 배포.
이로 인해 공격자에 의한 패치 차분 분석이 가능한 상태에 놓임.
※PHP Foundation도 이를 일방적인 엠바고 위반(사전에 정한 정보 공개 금지 기간을 지키지 않는 것)이라고 명확히 밝힘.
↓
10월 21일: 국내외에서 서비스 긴급 중단 연이어 발생
수정 패치가 아직 제공되지 않았기 때문에 국내외 웹 서비스나 정부 기관이 예방 조치로 일시 중지·유지보수 실시.
↓
10월 21일 23시경: PHP 공식이 수정 버전 공개
CVE-2026-109618, CVE-2026-109619에 대한 수정이 포함된 PHP 8.2~8.5 업데이트 버전 공개.
↓
10월 22일: 정보 유출과 관리 체제의 문제가 초점
PHP Foundation이 2024년부터의 수정 지연을 조직적 실패로 인정. 조정적인 취약점 공개가 무너진 경위도 문제시됨.
1password.com/personal-ai-ag…
SDK나 MCP로 어떻게 해보려고 했는데 마침 나왔네. 빨리 받아보면 좋겠다.

php2shell.com/
난 PHP를 쓰지 않아서 특별히 PHP2Shell을 대처하거나 할필요는 없이만 이를 통해 유출된 많은 정보와 크리덴셜로 또다른 공격이 이어지겠지. ㅠ
