





Congratulations @micronics3d on joining @formlabs! Still looking forward to a potential low-cost SLS solution (pretty please!)

Joel H retweeted

Like the opsec of NightHawk but missing Aggressor-like scripting functionality? Check out DayBird, an extension I built for NightHawk to allow for automation of operator workflows and initial check-in actions via C# plugins.
b:securityintelligence.com/x-f…
gh:github.com/xforcered/DayBird

Joel H retweeted

Just published a new blog post covering how to hide Beacon during BOF execution. If your BOF triggers a memory scan then EDR is likely to find Beacon and kill your process, but we can mask it using a simple technique. securityintelligence.com/pos…
Joel H retweeted

My new blog post! Dissecting and Exploiting TCP/IP RCE Vulnerability “EvilESP”. Reverse engineering CVE-2022-34718 + write a remote Denial of Service exploit. Covers IPsec and IPv6 fragmentation in the Windows kernel, bin-diffing, and making weird packets securityintelligence.com/pos…

I was cleaning and came across one my favorite finds at the HPB warehouse sale in Dallas (many years ago). There are some cool examples in here, including a catalog of block diagrams for binary operations, like finding a square root.


I’m convinced that, if nothing else in this industry, reviewing reports will turn me into a bitter old man.
Joel H retweeted
Demonstrating CVE-2022-37958 RCE Vuln. Reachable via any Windows application protocol that authenticates. Yes, that means RDP, SMB and many more. Please patch this one, it's serious!
securityintelligence.com/pos…
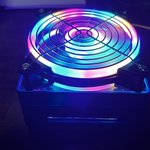
4 x Nvidia Xavier NX 32GB modules: $2500. 4 x Active Heatsinks: $135. Reference Carrier Board: $169. Hardwired, bright-as-the-fucking-sun, non-adjustable, rainbow-colored LEDs in the cooling fan: priceless.

Joel H retweeted

I feel like I’ve been reading the same “TTPs” in every report for a decade now. Not really sure what to say.

Microsoft has been tracking Iranian actor PHOSPHORUS’ ransomware sub-group known as DEV-0270, aka Nemesis Kitten. The group is responsible for multiple attacks typically using high-severity vulnerabilities to gain access. TTPs and more in our latest blog:
microsoft.com/security/blog/…
If you’ve ever met me, you’d likely already know a few reasons why my buddy @anthemtotheego lovingly calls me a ‘turbo-nerd’. I fully accept this label, and would like to interrupt your infosec feed to share a non-computer hobby of mine: ants.
If you are into 3D printing, you can also design and print a ton of different useful tools and enclosures. This hobby is surprisingly cheap! thingiverse.com/search?q=For…
That’s my ant thread. I hope I’ve inspired others to learn about these fascinating creatures. Special shout out to Mikey and the team behind @AntsCanada whose YouTube channel got me interested in the hobby nearly 10 years ago.