

Full-stack engineer · React · Next.js · AI Shipped apps to 10K+ users · GSoC · Expensify OSS Building @ RideNear · https://teapaw.org/t.co/nvaukzMQvw
Joined September 2022
- Tweets146
- Following35
- Followers9
- Likes33
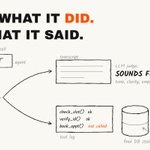





Your voice agent said "you're booked." Did the booking row change?
G2 and Bluejay's new voice agent eval passes a call only if the tool log and final DB state are right. No LLM judge.
Grade what it did from state. Use a judge for how it sounded.

Karpathy got tired of his YouTube feed, so he had Claude build HackerTube: 6,454 videos recommended on Hacker News, in about 2 hours.
Code is cheap now. Taste isn't.
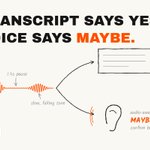
Your voice agent's transcript can be perfect and still miss the call.
"Yeah... sure" reads as a yes. Said slowly after a long pause, it's a maybe.
Builders: do pauses and tone feed any of your agent's decisions yet, or is it all text?

Voice agents can now start tool calls before the caller finishes talking. Great for lookups.
But callers change their mind mid-sentence. In my agents: speculate on reads, wait for the final turn before anything that writes (bookings, payments). #VoiceAI

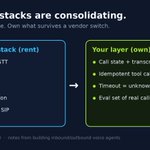
Voice AI is consolidating: Cartesia Managed Agents, Deepgram buying Daily (Pipecat).
Use the managed stack. But having shipped voice agents, I'd own:
- call state + transcripts
- idempotent tool calls
- an eval set of real calls
That's what survives a vendor switch. #VoiceAI

Aqib Nawab retweeted

🚨BREAKING: RAILWAY has just disclosed MAJOR security incident.
Customer API keys, database passwords, and other sensitive credentials may have been EXPOSED TO HACKERS.
Railway is urging ALL customers to rotate their credentials IMMEDIATELY.
And in an extraordinary move, the cloud hosting giant has PAUSED ALL DEPLOYMENTS while it investigates.
Here's what we know:
→ POTENTIAL SECURITY BREACH: Railway detected unauthorized activity involving systems storing customer environment variables.
→ DECRYPTED SECRETS EXPOSED: Attackers may have accessed encrypted environment variables AND obtained the decrypted contents of some of them.
→ CRITICAL CREDENTIALS AT RISK: Database passwords, cloud credentials, API keys, and private registry credentials could all be compromised.
→ ALL DEPLOYMENTS HALTED: Railway has suspended builds and deployments across its platform. Its dashboard and API are also experiencing major disruptions.
→ EMERGENCY WARNING TO EVERY CUSTOMER: Railway is urging ALL users to immediately rotate stored credentials and investigate suspicious activity.
→ POSSIBLE COORDINATED ATTACK: Railway believes this could be part of a larger campaign targeting cloud platforms to compromise AI inference providers.
→ FULL SCOPE UNKNOWN: Railway says the impact may be limited to a subset of users, but it is still investigating.
Think about how serious this is.
The platform developers trust to PROTECT their application secrets may have exposed those very secrets to attackers.
And now they're being told to rotate credentials while new deployments are BLOCKED.
First PHP. Then Node.js. Then LiteLLM.
Now RAILWAY.
October 21, 2026 is turning into one of the most alarming days in cybersecurity this year.
If you use Railway, take action NOW.

🚨 BREAKING: Node.js just dropped its OWN security bombshell.
4 HIGH-SEVERITY vulnerabilities patched TODAY, including one that could let hackers remotely execute malicious code on vulnerable servers.
→ 10 SECURITY FLAWS were addressed in today's Node.js release, FOUR rated HIGH severity.
→ REMOTE CODE EXECUTION: CVE-2026-111497 is a serious flaw in Node.js's Brotli decoder that could allow attackers to execute malicious code remotely.
→ TLS SECURITY BYPASS: Two separate vulnerabilities could trick affected applications into accepting certificates for the WRONG server under certain conditions.
→ Think about that. Your application could establish an encrypted connection while failing to properly verify WHO it's talking to.
→ THREE MAJOR NODE.JS VERSIONS AFFECTED: Node.js 22, 24 and 26 all required emergency security updates.
→ RUNNING NODE.JS 18 OR 20? Those versions are END-OF-LIFE and aren't receiving these official security patches.
→ PATCH IMMEDIATELY: Update to Node.js 22.23.4, 24.22.1 or 26.12.1, depending on your release line. If you're using Docker, rebuild and redeploy your containers.
PHP AND Node.js both facing major security disclosures on the SAME DAY.
If you run a website or application, TODAY is the day to check your servers.
And remember: the public release of security patches can give attackers a roadmap to systems that haven't updated.
Don't be the last one to patch.
Aqib Nawab retweeted

Dario watching DeepSeek open-source the infrastructure behind its cheap Al
🤖 Made with AI

🚀 Introducing DeepInfer, our in-house inference framework, now fully open source!
Powering DeepSeek-V4.1-Flash at scale with high throughput and low latency. We’re sharing our production stack to help the community lower compute costs, reduce energy use, and make AI more affordable.
🔗 github.com/deepseek-ai/DeepI…
1/4


Aqib Nawab retweeted

Cursor Pro is FREE 😳
- no student ID needed
- open to everyone worldwide
- normally $20/month
- claim your code through MLH
ends October 15
claim here: events.mlh.com/events/14553-…
Aqib Nawab retweeted

Judging by my tl there is a growing gap in understanding of AI capability.
The first issue I think is around recency and tier of use. I think a lot of people tried the free tier of ChatGPT somewhere last year and allowed it to inform their views on AI a little too much. This is a group of reactions laughing at various quirks of the models, hallucinations, etc. Yes I also saw the viral videos of OpenAI's Advanced Voice mode fumbling simple queries like "should I drive or walk to the carwash". The thing is that these free and old/deprecated models don't reflect the capability in the latest round of state of the art agentic models of this year, especially OpenAI Codex and Claude Code.
But that brings me to the second issue. Even if people paid $200/month to use the state of the art models, a lot of the capabilities are relatively "peaky" in highly technical areas. Typical queries around search, writing, advice, etc. are *not* the domain that has made the most noticeable and dramatic strides in capability. Partly, this is due to the technical details of reinforcement learning and its use of verifiable rewards. But partly, it's also because these use cases are not sufficiently prioritized by the companies in their hillclimbing because they don't lead to as much $$$ value. The goldmines are elsewhere, and the focus comes along.
So that brings me to the second group of people, who *both* 1) pay for and use the state of the art frontier agentic models (OpenAI Codex / Claude Code) and 2) do so professionally in technical domains like programming, math and research. This group of people is subject to the highest amount of "AI Psychosis" because the recent improvements in these domains as of this year have been nothing short of staggering. When you hand a computer terminal to one of these models, you can now watch them melt programming problems that you'd normally expect to take days/weeks of work. It's this second group of people that assigns a much greater gravity to the capabilities, their slope, and various cyber-related repercussions.
TLDR the people in these two groups are speaking past each other. It really is simultaneously the case that OpenAI's free and I think slightly orphaned (?) "Advanced Voice Mode" will fumble the dumbest questions in your Instagram's reels and *at the same time*, OpenAI's highest-tier and paid Codex model will go off for 1 hour to coherently restructure an entire code base, or find and exploit vulnerabilities in computer systems. This part really works and has made dramatic strides because 2 properties: 1) these domains offer explicit reward functions that are verifiable meaning they are easily amenable to reinforcement learning training (e.g. unit tests passed yes or no, in contrast to writing, which is much harder to explicitly judge), but also 2) they are a lot more valuable in b2b settings, meaning that the biggest fraction of the team is focused on improving them. So here we are.

When a caller cuts in, the agent should stop mid-word.
Not at the end of the sentence.
Then it has to remember what it already said so it doesn’t restart the same paragraph.
Talking over the customer is bad. Repeating yourself afterward is worse.
#VoiceAI #VoiceAgents

People keep asking when voice AI gets its ChatGPT moment.
Full duplex is mostly solved.
What still kills the call is the silence while the agent thinks or hits a tool.
Callers just hear nothing and assume the line dropped.
#VoiceAI #VoiceAgents

In 𝗱𝗶𝘀𝘁𝗿𝗶𝗯𝘂𝘁𝗲𝗱 𝘃𝗼𝗶𝗰𝗲 𝗰𝗮𝗹𝗹𝗶𝗻𝗴, keeping session state consistent across servers without adding 𝗹𝗮𝘁𝗲𝗻𝗰𝘆 is a real challenge.
𝗧𝘄𝗼-𝗽𝗵𝗮𝘀𝗲 𝗰𝗼𝗺𝗺𝗶𝘁 (𝟮𝗣𝗖) can coordinate distributed 𝘁𝗿𝗮𝗻𝘀𝗮𝗰𝘁𝗶𝗼𝗻𝘀, but the coordination and 𝗹𝗼𝗰𝗸

Hi @elonmusk, what do you think of replacing traditional phone calls dependent on the SIM network with a totally Starlink-based system providing accessibility everywhere in the world? This can help humanity a lot.
Most Voice AI SLAs still quote the average.
I’d reject any of them.
Ask for p95 and p99 under peak load.
Callers only feel the tail.
Averages look fine. The slow turns kill trust.
#VoiceAI #VoiceAgents
