Aptori (@AptoriDev) header
Aptori (@AptoriDev) profile picture

Developer-First Application Security for the Shift-Left Revolution!

Joined October 2020
Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)Photo by Aptori (@AptoriDev)
The security industry is entering the era of agentic security. Attackers already use AI to accelerate discovery & exploitation. Defenders need systems that continuously validate apps, reason about runtime behavior, and prioritize exploitable paths. 🧵👇 #Aptori
1
22
The future of AppSec is not AI-generated summaries of your backlog. It is autonomous security operations that validate risk, assist with remediation at machine speed, and verify closure. #AgenticSecurity #AppSec #RuntimeSecurity #AIAgents #Aptori
22
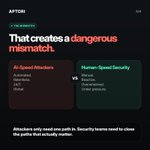
Attackers are now operating at AI speed, while most security programs still function at human speed. This gap is emerging as a defining challenge in AppSec this decade. 🧵👇
1
13
To keep pace with the rapid evolution of apps and APIs, modern security teams require: ▪️ Continuous runtime validation ▪️ Exploitability proof ▪️ Autonomous remediation workflows #AppSec #DevSecOps #Aptori
43
Most security tools stop at the worst possible place: the finding. But findings alone do not reduce risk. Modern AppSec needs a closed loop that validates runtime, proves exploitability, and verifies the issue is resolved.
1
16
The future of application security is not more alerts. It is autonomous validation and verified risk reduction. #AppSec #RuntimeSecurity #AutonomousSecurity #AgenticSecurity #Aptori
22
Myth: Clean scan = secure application. Reality: Clean scan = scanner found nothing it was built to find, in paths it was told to check, at the moment it ran. Runtime was not included in that sentence. It never is. The breach happens at runtime. #AppSec #DevSecOps #Aptori
106
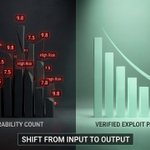
Vulnerability count tells you how much code you scanned. MTTR tells you how fast your team works. These are input metrics. They measure activity. They do not measure security. 🧵👇
1
43
The only metric that maps directly to risk reduction: verified exploitable paths closed. Most programmes track the first two and just guess at the third. That gap is where risk lives. #AppSec #CISO #DevSecOps #Aptori
28
SAST finds what it was taught. DAST tests what it is told. Neither knows what your system does at runtime under real conditions. That is not a gap in implementation. It is a gap in design. 🧵👇
1
20
Modern applications are distributed systems. Security is determined by how components interact, not just the correctness of individual code blocks. The tools were built for an old problem. The problem has moved. It's time our tooling moved with it. #AppSec #DevSecOps #Aptori
19
Security leaders: How many open findings in your backlog have a proof-of-exploit attached? ​Not a CVSS score. A reproducible attack path. ​If the answer is close to zero, your backlog is a list, not a programme. What's that number for your team? ​#AppSec #CISO #Aptori
24
If 90% of your code never runs, 90% of your static analysis findings are chasing ghosts. The backlog grows because the input is wrong, not because your engineering team is slow. Most of what scanners flag are paths the app never uses. 🧵👇
1
12
The rational response to a list where 90% is noise is to deprioritize the whole list. That is engineering judgment operating correctly. Runtime reachability changes this. If a vulnerability is in dead code, it's just a theory. Treat it differently. #AppSec #DevSecOps #Aptori
31
A finding without proof is a hypothesis. Developers do not fix hypotheses. This is the real reason your AppSec backlog exists. Not a lack of headcount. Not sprint planning. Security tools produce probabilistic signals. Engineers need certainty. 🧵👇 #Aptori
1
5
The boundary between findings and proof is the most important line in security. On one side: patterns and noise. On the other: a reproducible sequence demonstrating real exploitability. Attackers operate on the right side of that line. It's time we join them #AppSec #DevSecOps
12
If your security dashboard is optimized for findings count, you are measuring activity. Not security. Findings without proof of exploitability are just hypotheses. And engineers don't patch hypotheses. #AppSec #DevSecOps
22
Security programmes are built before runtime. Attacks happen during it. That gap has a name: your actual attack surface. 🧵👇
1
11
Most tools measure what happens before a breach. Almost none measure what happens during it. Start from runtime. Not as a phase. As the source of truth. #AppSec #CyberSecurity #Aptori
33
Authorization is fundamentally a graph problem. Who can do what to which object? Via which service? The vulnerabilities that matter most in 2026 like BOLA & privilege escalation emerge from inconsistencies in this graph. 🧵👇
1
15
Do you have an accurate map of the authorization relationships between your services? Or does that map exist only in people's heads? To secure modern architectures, you have to stop looking at individual requests and start modeling entire interaction paths. #Aptori
1
8
This is where Semantic Models come in. They map nodes (identities, APIs) and edges (data flows, access controls) to track exactly where context is lost. Read our full technical breakdown on how system-level security analysis actually works: 🔗 aptori.com/blog/semantic-mod… #AppSec
7