

Continuous API security for developers. Passive monitoring · Active scanning · Real findings. Built for African devs
Lagos, Nigeria
Joined July 2026
- Tweets152
- Following1
- Followers171
- Likes24




AuditGate retweeted

Jump on @AuditGateHQ if you love your product 😂🤝

Meet AuditGate, another Nigerian-built product recently listed on Africa Is Building! 🇳🇬 Built by Akintola Stephen (@Akintola_steve).
@AuditGateHQ is an API security platform that helps developers identify vulnerabilities, investigate security issues, and fix them before they become serious problems.
It offers automated API and frontend security scans, traffic monitoring, GitHub integration, remediation guidance, and security reports.
What I find interesting is that developers can start using it for free, making API security more accessible to solo builders and small teams.
If you're building APIs or managing applications in production, this is one worth exploring.
Discover AuditGate on AIB:
africaisbuilding.com/product…
Africa is Building! 💚

AuditGate retweeted

Meet AuditGate, another Nigerian-built product recently listed on Africa Is Building! 🇳🇬 Built by Akintola Stephen (@Akintola_steve).
@AuditGateHQ is an API security platform that helps developers identify vulnerabilities, investigate security issues, and fix them before they become serious problems.
It offers automated API and frontend security scans, traffic monitoring, GitHub integration, remediation guidance, and security reports.
What I find interesting is that developers can start using it for free, making API security more accessible to solo builders and small teams.
If you're building APIs or managing applications in production, this is one worth exploring.
Discover AuditGate on AIB:
africaisbuilding.com/product…
Africa is Building! 💚
AuditGate retweeted
For the past 3 days, I’ve had 17 people get hands-on with @AuditGateHQ, explore what we’ve built, put it to use and share their feedback.
The feedback has been genuinely encouraging, and some of the conversations have been very insightful.
A lot has been happening behind the scenes, and we’ve been working hard to make AuditGate better.
Now, for the first time, I’m officially putting our public URL out here.
app.auditgate.io
So, what exactly is AuditGate?
AuditGate helps engineering teams identify security vulnerabilities in their APIs before attackers find them.
You can connect your API through GitHub or an OpenAPI specification, run security scans against it, identify vulnerabilities, get AI-assisted remediation guidance, monitor security alerts, and generate reports that provide visibility into your API security posture.
Our goal is simple: help developers and engineering teams build, ship and maintain APIs with confidence.
You can now create an account, explore the platform and see what we’re building.
If you have questions, need clarification, or would like a walkthrough, my DMs are open. I’d genuinely love to have a conversation.
We’re just getting started.
Let’s secure what we ship. 🤝

It’s Finally time.
Let’s come onboard and explore !

For the past 3 days, I’ve had 17 people get hands-on with @AuditGateHQ, explore what we’ve built, put it to use and share their feedback.
The feedback has been genuinely encouraging, and some of the conversations have been very insightful.
A lot has been happening behind the scenes, and we’ve been working hard to make AuditGate better.
Now, for the first time, I’m officially putting our public URL out here.
app.auditgate.io
So, what exactly is AuditGate?
AuditGate helps engineering teams identify security vulnerabilities in their APIs before attackers find them.
You can connect your API through GitHub or an OpenAPI specification, run security scans against it, identify vulnerabilities, get AI-assisted remediation guidance, monitor security alerts, and generate reports that provide visibility into your API security posture.
Our goal is simple: help developers and engineering teams build, ship and maintain APIs with confidence.
You can now create an account, explore the platform and see what we’re building.
If you have questions, need clarification, or would like a walkthrough, my DMs are open. I’d genuinely love to have a conversation.
We’re just getting started.
Let’s secure what we ship. 🤝
AuditGate retweeted
Say less !
Check out @AuditGateHQ

Thank you, @Limtech001! 🤝
Also, have you explored our alerting rules section yet?
Kindly create an alert rule and test the Slack integration. You’ll get real-time security alerts directly in your Slack channel, just like this.
There’s a lot more to explore with @AuditGateHQ. Go preach it! 😁


I got to test @AuditGateHQ , and I like what I’m seeing.
I ran an initial security scan on a project I’m working on, and it identified issues around security headers, dependency vulnerabilities and infrastructure information exposure.
After addressing the findings, I ran another scan, and the summary showed zero findings across all severity levels.
I particularly like the visibility into individual security checks and the actionable recommendations.
It’s good to see Nigerian developers building products that solve real engineering problems.
Well done @Akintola_steve
Let’s keep building! 👏


1
87
AuditGate retweeted
What’s stopping you all from jumping on @AuditGateHQ?! 😁
Thank you, Temitope! Really glad you find value in what we’re building. I also appreciate the feedback you shared. I listened, took notes, and there’s quite a lot we’re taking back to the team.
Building with users who genuinely care about the product makes the journey even more exciting. 🤝
I got to test @AuditGateHQ , and I like what I’m seeing.
I ran an initial security scan on a project I’m working on, and it identified issues around security headers, dependency vulnerabilities and infrastructure information exposure.
After addressing the findings, I ran another scan, and the summary showed zero findings across all severity levels.
I particularly like the visibility into individual security checks and the actionable recommendations.
It’s good to see Nigerian developers building products that solve real engineering problems.
Well done @Akintola_steve
Let’s keep building! 👏

AuditGate retweeted
Your API passed the scan.
Now your bank, your enterprise client or your auditor wants proof.
AuditGate now generates:
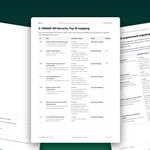
• OWASP API Security Top 10 reports, with every finding mapped to API1 to API10.
• PCI DSS v4.0 reports mapped to requirements like 6.2.4, 8.3.1 and 4.2.1.
Each one shows what was tested, what’s affected and what’s out of scope.
No vague “you’re compliant” badge.
auditgate.io


Taking a look at the generated report?
That’s all your auditor needs.
Security engineers, compliance teams, developers and businesses can now have clear, structured security reports that show exactly what was tested, what was found and what needs attention.
With AuditGate, security doesn’t just stop at detecting vulnerabilities. You can also generate the evidence to back up your security posture.
Explore AuditGate: auditgate.io


Your API passed the scan.
Now your bank, your enterprise client or your auditor wants proof.
AuditGate now generates:
• OWASP API Security Top 10 reports, with every finding mapped to API1 to API10.
• PCI DSS v4.0 reports mapped to requirements like 6.2.4, 8.3.1 and 4.2.1.
Each one shows what was tested, what’s affected and what’s out of scope.
No vague “you’re compliant” badge.
auditgate.io

AuditGate retweeted
This is exactly how I see the opportunity with @AuditGateHQ.
API security isn’t a new market. There are already established players offering security testing, vulnerability scanning and monitoring.
But what if we approached it differently?
What if developers could integrate API security directly into their development workflow, run security checks, identify vulnerabilities, understand the risks, get AI-assisted remediation guidance and even enforce security checks in their CI/CD pipelines?
That’s the direction we’re taking with AuditGate.
We’re not trying to reinvent API security. We’re building a product that makes securing APIs a more natural part of building and shipping software.
The added edge isn’t just detecting vulnerabilities. It’s helping developers understand, prioritize and act on them.
A crowded market doesn’t scare me. It tells me there’s a problem worth solving.
And we’re just getting started.
Do well to check us out auditgate.io


Linear is one of the most popular project management tools today. It’s barely 7 years old.
It entered a market already dominated by Jira, Trello, Asana, and Monday.com.
Resend is already a major player in the email API space. It’s barely 3 years old.
It entered a market with established players like SendGrid, Mailgun, Amazon SES, and Postmark.
Neither invented a new category. They simply approached existing problems differently and built products developers love.
The lesson? You don’t need to invent something new to build something big. You just need to solve an existing problem better.
A crowded market doesn’t mean there’s no opportunity. It means there’s already demand.

AuditGate retweeted
Damn! What a day! 🔥
Just wrapped up my scheduled sessions for today, introducing and walking engineers through @AuditGateHQ.
@Limtech001, you took over 3 hours of my time 😂, but it was absolutely worth it. Really enjoyed having the session with you and walking you through the platform. 🤝
@Thedanieloreofe, glad you gave me your listening ears and took the time to understand what we’re building. Even better that you saw the brilliance behind it.
@lagalo__, coming from a security engineer’s perspective, I’m glad you could appreciate what we’ve built. Your insights and feature recommendations were also incredibly valuable. They gave us a lot to think about and improve on.
One thing I’m taking away from today’s sessions is that getting people to see what you’re building, understand the problem it solves, and share their perspectives is incredibly important.
We’re building, listening, learning and getting better.
And we’re just getting started with @AuditGateHQ.
We will be glad to work with @GammsApp

AuditGate retweeted
Did you know you can integrate AuditGate directly into your CI/CD pipeline?
Whether you’re using GitHub Actions, Jenkins, or another CI/CD workflow, you can bring security scanning closer to where you build and deploy your applications.
This means security doesn’t have to be an afterthought. You can make vulnerability checks part of your development and deployment process.
The video below gives you a quick walkthrough of how this works.
And this is just a small part of what AuditGate can do.
There’s a lot more to explore.
Get yourself onboarded, connect your APIs, and see what you’ve been missing.
auditgate.io/docs/connect/ci…
AuditGate retweeted
Kindly go through @AuditGateHQ docs


AuditGate retweeted
Where are the hackers and code reviewers?
I have a small code security challenge for you.
Take a close look at the screenshots below.
How many vulnerabilities can you identify?
A few hints have been intentionally included, but don’t limit your investigation to them.
I’m particularly interested in knowing:
What vulnerabilities can you spot?
Are there other attack surfaces beyond the hints?
Can any of these vulnerabilities be chained together?
What’s the worst-case impact if an attacker discovers them?
Don’t just point out the vulnerable lines. Explain the attack path and how you’d exploit the weakness in a controlled environment.
Let’s see who can find what others might overlook.
Security isn’t just about finding vulnerabilities. It’s about understanding how they connect.


AuditGate retweeted
Your users are your best testers. ❤️
Just had another session with someone about @AuditGateHQ, and she described it as a brilliant product. She also shared some valuable ideas that could make the product even better.
Our current onboarded user count has climbed to 10 since yesterday.
I’m being intentional about this process. Carefully selecting users, having one-on-one sessions with them, answering their questions in real time, listening to their feedback, and making sure their onboarding experience is as seamless as possible.
Building a great product isn’t just about writing code. It’s also about listening to the people who use it.
We’re learning, improving and building with our users.
One conversation at a time.