



Pinned Tweet
I just open-sourced my Shape Security reverse-engineering toolkit.
What started years ago as research into Shape's JavaScript virtual machine has evolved into a much larger engineering project.
The toolkit is built primarily in Rust and includes:
• VM bytecode disassembly and analysis
• Automated JavaScript deobfuscation
• Execution tracing and program reconstruction
• Signal extraction, encoding, and decoding
• SDK integrations and reproducible examples
• Extensive regression testing across thousands of seeds
A significant part of the recent development was accelerated using AI coding agents.
But generating code was only part of the challenge. The real work was understanding the underlying system, reconstructing its behavior, validating correctness, and building tooling that could reliably reproduce the results.
I'm making the research, implementation, and documentation publicly available for other engineers to explore, learn from, and build upon.
This is the first of several reverse-engineering projects I plan to release.
More technical write-ups and research coming soon.
Source code: github.com/BottingRocks/Shap…

Damn is fucking crazy GTA 6 is getting released on the 19th of November, Andrew Tate is getting his final extradition hearing on the 19th of November and Anthropic going to IPO on the 19th of November. Everything is moving so fast!
3
533
Minecraft clones are the new to-do apps.
Back then, every fucking JavaScript framework had developers building the same CRUD to-do app to show off their shiny new stack.
Now, every new AI model has people generating Minecraft clones and acting like it's some insane engineering breakthrough.
1
541
With AI everything that can be written in Rust will be written in Rust. I do agree with DHH, Rust is an ugly language to look at but is one of the best languages for your agents to write their back-end code. Long Live Rust.
2
6
744
A lot of companies are repeating the same mistake from the cloud era, just with AI now.
Before:
throw more AWS at the problem.
Now:
throw more Opus tokens at the problem.
Using frontier models for everything doesn’t teach workflow design or token discipline. It just hides inefficiency behind intelligence.
The real leverage is probably:
better routing
better workflows
better validation
better state/history
better escalation logic
Not “use the strongest model for every step”.
Token discipline is the new infra discipline
1
395
In some orgs, performance low key gets judged without factoring in dependencies.
If your work relies on another team that can’t deliver, you’re basically working with your hands tied, but you still get rated like you had full control.
You call it out, you’re “difficult” or “underperforming”
You stay quiet and just do what you can, you’re “disengaged”
And if you were ever labeled “difficult” or a “crash out,” even locking in, staying quiet, and just working doesn’t reset it. The label sticks.
Same situation, just different labels depending on how you act.
And performance reviews don’t really fix it, they just dress the narrative up in more polished, corporate sounding language.
At some point, it’s better to move on and build somewhere you’re actually evaluated on real output.
378
Mexico the only place where the ice cream machine always works and you get your order in under 60 secs.

4
425
BottingRocks retweeted

Developers automated the web.
Now everyone can.
Announcing Director and our $40M Series 🅱️
I recently joined a rapidly growing startup that raised a Series A of $21,000,000.
I joined 5 weeks ago and so far my experience has been a short of amazing. The founder, @pk_iv , likes to shoot for the fences, nah scratch that he likes to shoot for the stratosphere.
My position was essentially to be part of a newly created stealth team that would match the likes of the top web scraping companies.
As many of you guys know, I like reversing anti-bots, so much that I've barely used browsers to bypass anti-bots as my strength lies in reversing Javascript protections.
When I joined Browserbase I had to roll up my sleeves and dig down into the Chromium source(something I've never done before) to patch all the leaks that Playwright, Selenium and Puppeteer leave.
@pk_iv specifically wanted to meet the customer where they are and not force them to use any custom frameworks. That meant that the only way forward was to build our own custom chrome binaries.
The ugly truth is that there is not a single entity where you can just license or buy all the stealth tools needed to effectively bypass a website's captcha and antibot protection. You have to build a lot of in-house and keep playing the cat-and-mouse game.
When I originally joined my contract was to be remote for the initial 4-6 weeks, but after 4 days I decided to say screw it and drive down to San Francisco and just stay at a hostel near by so I can synchronize better with the team.
I live in Davis,CA which is technically very close to San Francisco, but it is a nightmare to commute every day to be there at 9 AM in the office.
That was the best decision ever as it wouldn't have worked out since a lot of my work needed to be integrated into the Browserbase product.
We use Slack for communication, but waiting for a response back when you can just get help from your co-worker by going to their desk or scheduling a conference room is so much better.
Now regarding @pk_iv , he doesn't have a personal office, desk or stationary place at the office where he works, yet he is there 6-7 days a week.
He eats, lives, and breathes @browserbase and he is everywhere. I'm still amazed at the level of context he is able to hold as he moves from product to engineering to customer support all within a short time frame.
He is answering customer queries, drafting documents on notion, pushing code to github, reviewing PRs, bringing in new customers.
You can't barely see me in the picture, but I'm the guy on the very back with the white board in-front. The guys on the front are all working on stagehand.
Yes, I do have a kid, but he is 7(not 9 @pk_iv lol) going to be 8 next year. I do get to spent time with him on the weekends grinding @fortnite on the Switch.
Yeah, I know I work a lot but honestly I've grown so much in the past 5 weeks that I'm excited to see what the future holds.
The hardest thing for me was working in a team where there are processes you have to follow, discussions that must be had with all the stake holders(people in the team), stand-up meetings where you report what you have done. I've always been sort-of a lone wolf doing my own thing.
@pk_iv is currently looking for more amazing people to add to the team. He hires extremely fast though, you won't wait weeks or months to know if you are a good fit. I was hired under 1 week(but I was referred internally though).
Don't be afraid though, @pk_iv, won't force you or make you work weekends. I actually did it on my own accord and I didn't mind at all as I was able to get way more help(I was stuck on the dev environment) from @pk_iv on the weekends as there were barely any people there.
You will be provided with a:
- MacBook Pro M3
- Unlimited Celsius, cold brew drinks, coconut water and sparking water
- Unlimited snacks(beef jerky, bananas, nuts, goldfish crackers, popcorn)
- Free lunch via DoorDash on Friday
- And last but not least, tons of natural sunlight and beautiful plants that are nurtured and watered by our dedicated PlantLord that comes every week to keep them live and green.
teapaw.org/pk_iv/status/186076206…

how to build a healthy "grind" culture:
1. the founder needs to set the cadence. if you aren't grinding, why would anyone else? i would never ask someone to do something that i wouldn't personally do.
2. we set realistic expectations. the default state is 10am-5pm, monday-friday, in person at our office. need to go to the dentist or WFH to sign for a package? do your thing.
3. weekends are for the fun work. stuff that's hard to prioritize or has unclear ROI. if you really want to build that feature, the weekend is your time.
4. sometimes, we have to work outside the norm. we're an infrastructure company, which means we're open 24/7. and we're a startup, which means sometimes we push. if we need to step up to meet the demands of the business, even outside of normal hours, we do that.
5. we're a high trust team. i deeply trust everyone on our team. i care about results, not hours in. we're in person daily because it's what we enjoy. in the end, it's all about doing what we need to do, and having a ton of fun doing it.
I decided that Babel sometimes isn't the right tool for the job when it comes to speed.
Here is a deobfuscator I was working on for Akamai's Javascript.
github.com/BottingRocks/Akam…
I'm in the process of switching everything over to tree-sitter for a much faster parsing both in the Web(via WASM) and on NodeJS(via nodejs bindings).

1
19
2,785
Today, as I was working on a new VM tracer for a super hard antibot, I came across this new anti-bot that I have never seen before.
My interests were piqued and I quickly went to their website to see what all the buzz was about. I quickly went to their docs to understand what new technology they were bringing to the table. Then, within 4 minutes, I came across their StrongCaptcha technology.
My heart was racing, I couldn't believe my eyes, a new type of Captcha. Did these new incumbents really come up with a novel, sophisticated, out-of-the box approach to a zero-friction user-experience using a Captcha?
Within minutes I became a skeptic, how in the world did the big 4 antibots(or should we say top 5) couldn't come up with something this innovative?
I then proceeded to load up my coffee mug with another extra coffee serving as I prepared to dig into their telemetry.js file. To my dismay, I discovered that their telemetry.js file wasn't obfuscated, nothing was dynamic. Didn't think much of it as my quest was to find out how their StrongCaptcha worked.
Well ladies and gentleman, with the help of SourceGraph.com and their public search code, I searched for all of their TypeErrors strings to find any resemblence of open-source code that they might have used.
Then within 30 seconds, I hit a match!.
They are using webP encryption to encrypt the images through WASM using a public open-source repo from Google: github.com/GoogleChromeLabs/…
My excitement wore off within the next 20 minutes as I quickly realized how their StrongCaptcha actually worked, and the "loophole" they seek to patch by creating this reCaptcha wrapper that in theory should work.
Now, usually how 2captcha and other captcha solving services work is that they use your proxy(ip address) and the reCaptcha siteKey to solve the challenges(images) for you. The way this work is that on their backend they use their own AI and browser farms to click on the correct images, then they send you back the solved token that reCaptcha gives you upon success.
Coincidentally, the solving IP will all look fine and dandy when the site administrator checks on reCaptcha backend for the device IP address that solve the challenge. This is because the captcha solving service used your IP to solve the captcha.
What StrongCaptcha is attempting to do is to patch that loophole by becoming the "middleman". Yes, you heard that right, the FUCKING middleman.
If you have read up to this point, you might be asking, how in the world does this work?
Well is quite simple:
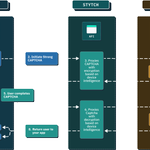
They, Stytch, will pull the reCaptcha challenge from their end and send you the encrypted images using webP from their telemetry.js file to the Visitor.
The Visitor cannot use the reCaptcha site key and their proxy to send it to a captcha solving service to solve because Stytch will be the one "proxying" the requests from each visitor to reCaptcha. This will mean that the solving device IP will always be Stytch's IP address.
So then what happens when you can just decypt the images they send using webP on the client(your browser) and then just send the images to a captcha soving service to give you back a grid of the correct images, then submit those answers back "encrypted" to Stytch's StrongCaptcha backend?

ALT Stytch's Strong Captcha
4
40
5,045
Scraping airlines is the new sneaker twitter 2017. It's just getting started, the only difference is that the threat actors all have previous knowledge about antibots.
I was just putting two and two together from what I've seen some of the close contacts of mine working on antibots were doing(working for companies scraping airlines), the handful of recent dms I have been getting if I have an Akamai and Kasada bypass for some airlines. Didn't think this tweet was gonna blow up.
1
1,264
ChatGPT,Claude, Cursor etc. are all great at helping new comers build their first web scraping or bot script using Selenium/Puppeteer/Playwright.
However, what happens when they hit a Datadome, Incapsula, or Cloudflare block?
What's next do you roll-up your sleeves and learn about antibots or do you accept that probably web scraping and botting is not as easy as launching a headless chrome browser and using LLMs to automatically extract content?
6
17
2,942
Every time I deobfuscate some new script and look at the contents being more than 50% dead-code, I ask myself what kind of gas were the developers smoking was it some Za or some NOS?
Dead-code does nothing to impede someone from understanding your code, it just adds more bandwidth costs to your visitors and makes your site slower.
1
8
1,416
Are there any public open-source deobfuscators for Akamai's JS script or do I have to create one? I have been searching for the past few days on github and I can't find anything that can deobfuscate this kind of script
gist.github.com/pinyugi/be93…
4
6
1,305
There are 3 types of antibots companies.
The first type is the one that serves you pictures of animals asking you which one lays eggs and/or asks you to find all the squares that are part of a fire hydrant. Eventually, these type of antibot companies will start serving SAT tests as bot challenges.
The second type is the one that proudly serves you a heavily branded block page when they block you letting you know exactly who they are. They are cheap and easy to use, and allow anyone that isn't retarded to bypass them by patching puppeteer/playwright or a chromium browser for obvious leaks of automation traces.
The third type operate on the belief that they are harder to reverse because having a highly sophisticated VM, with changing seeds every 30 mins that shuffle the signals order, which are packed using their own proprietary bit packing library, with a custom base64 alphabet, and a xoring byte to further encode their UFT-8 strings will only be attempted by the most determined actor whose goals might not be money after all.
The first type of antibots will make some humans solve 20 puzzles while letting 20 other bots go through while giving antibots a bad name in general.
The second type of antibots will try to expand by taking as much market share from all the other antibots by over promising and under delivering.
The third type of antibot will sit on their laurels while allowing their main product to rotten away as their massive edge erodes away due to their inability to see beyond the present and into the future, thus they will let type 1 and type 2 antibots eat their whole fucking lunch.