

The National CERT/CC @NITAUganda1 is the national point of contact for cybersecurity incident coordination Uganda & coordinates sub sector CERT teams in Uganda.
Kampala, Uganda
Joined January 2014
- Tweets6K
- Following300
- Followers1.5K
- Likes945



🚨 Cyber Pulse Issue 18 is out.
The Optimizely story is worth sitting with: 178 major sites, zero of them hacked directly. The trusted script running on your site is now as much an attack surface as your own code, and most teams have no idea what access it actually holds.

CyberPulse Issue 18 | Cybersecurity Awareness Bulletin
🚨 This week’s biggest threat: Attackers exploited a flaw in Optimizely’s A/B testing platform to inject malware into 178 organisations, including Zoom, BBC, CNN, HSBC and IKEA. The code was rebuilt 26 times in a day to steal card data, cookies and crypto payments. None of these sites were hacked directly. A trusted script was.
Also flagged:
❗ JPMorgan, Visa, Mastercard Data Leak: Extortion group n0n claims it accessed cardmember records through third-party vendors, exposing over 16,000 customer emails and some phone numbers.
❗ Critical Apache HTTP Server Flaw: A flaw in Apache’s HTTP/2 module lets an unauthenticated attacker run code remotely. It is fixed in version 2.4.71, so update now if HTTP/2 is enabled.
❗ Microsoft Patches 1,000+ Flaws: November’s update fixes 48 critical code-execution flaws and an actively exploited Outlook vulnerability that can expose authentication data and let attackers impersonate users.
💡 Tip: Three of this week’s biggest stories share one thing in common. The company itself wasn’t breached directly; a vendor or embedded third-party tool was. If your website runs scripts from analytics, A/B testing or chat tools you didn’t build yourself, ask what access those scripts actually have, and whether anyone would notice if that code suddenly started behaving differently.
Protect yourself:
✔️ Review every third-party script running on your website
✔️ Ask vendors how they protect the data and systems they access
✔️ Apply the latest Apache and Microsoft security updates without delay
Read, share, help build a safer digital Uganda.
#CyberPulse #CyberSecurity #CERTUg #PoweredByNITAU

68
National CERT/CC retweeted

Today, @NITAUganda1 completed the Key Generation and Signing Ceremony for Uganda’s National Public Key Infrastructure (PKI), under the Uganda Digital Acceleration Project - Government Network (UDAP-GovNet).
The ceremony formally established the Uganda National Root Certification Authority, Uganda National Root CA RSA G1, along with its Issuing Certification Authority.
The Root CA is the foundation of the National PKI and through it, Ugandans will be able to:
✔️ Prove who they are online with trusted digital identities
✔️ Sign documents electronically with signatures that can be verified
✔️ Carry out online transactions more securely
This means citizens, businesses and government can offer and use digital services with greater confidence.
#NITAU #DigitizeUG


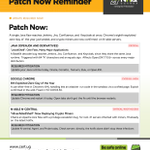
Patch Now | Nov 19
Apache Roller (CVSS 9.8): Sept fix was incomplete, now under attack. Update to 6.1.6.
Puppet (CVSS 9.4): config mgmt servers hit. Patch and audit your CA for rogue certs.
CISA now urging immediate action on Java4Shell from yesterday. Patch it today

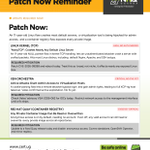
Patch Now | Nov 18
"Java4Shell" (CVE-2026-114938): one Java flaw hits Jenkins, Jira, Confluence, Keycloak at once. Update your runtime today.
Chrome zero-day #8 of 2026 (CVE-2026-125350): update and restart browser.
N-able N-central: crypto miners now confirmed on 21 servers.

Patch Now | Nov 17
"NoisyTCP" (CVE-2026-99288): 11yr Linux kernel flaw crashes almost any default Nginx/Apache/SSH server, no auth needed. Patch and reboot.
Xen Orchestra: active attacks bypass login for admin access, no fix yet, restrict access.
Red Hat Quay (CVSS 9.8/9.9)

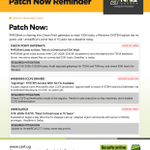
Patch Now | Nov 16
Check Point gateways (CVE-2026-123039): PHP2Shell now chaining to root, TSGA backdoor, some ESXi wipes. Patch today.
Windows "SignDrop": SYSTEM exploit public, no patch exists yet. Restrict code execution as a stopgap.
UnrealIRCd: worst flaw in 15 years.

🚨 Cyber Pulse Issue 17 is out.
Worth noting: State-linked groups increasingly pick soft, civilian targets because the retaliation calculus is murkier than hitting a power grid or a military system directly.
cert.ug | #CyberSafeUG #CERTUGCC
🚨CyberPulse Issue 17 | Cybersecurity Awareness Bulletin
This week’s biggest threat: France has formally attributed a wave of supermarket refrigeration attacks across France, Belgium, Luxembourg, Sweden, and Estonia to Iran. What started as unexplained spoiled stock is now confirmed as a nation-state campaign of industrial sabotage targeting civilian food infrastructure.
Also flagged:
❗GitHub Supply Chain Attack: A malicious workflow compromised tens of thousands of repositories (including Uber’s) by abusing trusted automated pipelines rather than a single product flaw.
❗Maersk Data Breach: The shipping giant confirmed data was extracted from a legacy system. Attackers are now demanding $5 million to prevent its release.
❗N-able Platform Offline: N-able took its N-central platform offline after a researcher published 30+ claimed zero-days, with no patch available yet.
💡Tip: This week’s AI agent attack on a telecom and the GitHub supply-chain hit share the same root cause broad, standing access granted to an automated tool that nobody was watching. Before connecting any AI assistant, bot, or CI/CD workflow to systems with real data or deployment power, ask what it can actually reach and whether that access is ever reviewed.
Protect yourself:
✔️Limit standing access for automated tools and AI agents
✔️Review and revoke unused pipeline/workflow permissions regularly
✔️Treat industrial control and operational systems as high-value targets, even when they seem “offline”
Read, share, help build a safer digital Uganda.
#CyberPulse #CyberSecurity #CERTUg #PoweredByNITAU

National CERT/CC retweeted
SCAM ALERT 🚨
Be careful of a Telegram channel called AXIS_UGA that is pretending to be the National Information Technology Authority - Uganda (NITA-U).
The channel claims it can help with frozen accounts and fund recovery, and directs people to continue the conversation on WhatsApp. This is a scam.
NITA-U does not operate through such channels or handle personal fund recovery this way.
Please protect yourself and others. Do not engage, and share this warning.
#NITAU

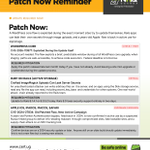
Patch Now
OpenSSH "SSHole" (CVE-2026-123158): root on Alpine Linux within hours of disclosure. Update to 10.6p2.
CryptoPayment Gateway WP plugin: CVSS 10, no fix exists, wallet credentials exposed. Remove it today.
WordPress Core: even patching CVE-2026-119977 has a catch.

Patch Now | Nov 5
WordPress Core (CVE-2026-119977): exploited during the upgrade process itself. Federal deadline tomorrow.
Rails Active Storage: crafted uploads can leak server secrets. Update to 8.1.4.1/8.0.5.2.
Apple (CVE-2024-27834): old flaw, new espionage campaign.

Patch Now
Synology NAS: C3RB3R ransomware hitting outdated DSM builds. Update to the latest build for your line today.
GitLab: 1,000+ exposed servers still vulnerable to active exploitation weeks after patch.
BTCPay Server: $1.63M stolen from unpatched hot wallets.

Patch Now | Nov 3
Cisco SD-WAN "KeyDrift" (CVE-2026-20127): encryption keys stolen since 2023. Patch, then rotate keys separately.
Langflow (CVSS 9.8): unauth RCE, Metasploit module exists. Update to 1.13.0.
s2Member WordPress plugin: public exploit out. Update now.

Patch Now | Nov 2
Drupal Commerce Core (CVE-2026-118539): active attacks, 42,000+ stores exposed. Patch and audit orders.
Ivanti Connect Secure: 3 flaws chained to unauthenticated root. Update today.
Cisco ASA/FTD (CVE-2026-76418): unauth firewall crash, exploited.

2
205
🚨 Cyber Pulse Issue 16 is out.
Worth noting on Binance: this is the second major exchange in two years brought down by one compromised employee device, not a platform flaw. Bybit in 2025, now Binance. Exchanges harden infrastructure, not always the humans with access to it.
🚨CyberPulse Issue 16 | Cybersecurity Awareness Bulletin
This week’s biggest threat: Binance has confirmed a security incident affecting about $6.3 billion in assets, the largest crypto heist on record, overtaking the $1.5 billion Bybit theft. Nearly $3 billion has been frozen so far. The breach reportedly started with a compromised laptop belonging to one Binance engineer, which gave the attacker access to submit unauthorised withdrawals. TRM Labs and Chainalysis have linked the attack to North Korea with high confidence. One compromised laptop, billions gone.
Also flagged:
❗eMudhra CA Weak Keys: A script error caused this Indian certificate authority to generate weak intermediate CA keys. No publicly trusted certificates were affected, but it’s a reminder that even trust infrastructure has bugs.
❗GitHub Token Leak: A leaked GitHub token with publish access to widely used npm packages was found this week. One leaked token can threaten software that millions depend on.
❗ConnectWise Cloud Backup Breach: Attackers used stolen credentials and AI-assisted tools to reach downstream Microsoft 365 accounts, and the access keys they obtained reportedly still work even after the vendor’s fix.
💡Tip: After a major breach like Binance’s, scammers move fast with fake “compensation” or “verify your account” messages aimed at worried users. If you get a message claiming to be from an exchange after a breach, go directly to their official website instead of clicking any link.
Protect yourself:
✔️Secure work laptops and the accounts on them
✔️Keep access tokens and keys private, and replace them if exposed
✔️Ignore “compensation” messages and use official websites only
Read, share, help build a safer digital Uganda.
#CyberPulse #CyberSecurity #CERTUg #PoweredByNITAU

3
186
Patch Now | Oct 29
Veeam Backup & Replication (CVE-2026-108142, CVSS 9.1): unauthenticated auth bypass. Also patch Veeam ONE and Linux Agent.
Oracle EBS (CVE-2026-101767): scanning started days after the patch. Apply Oct CPU now.
EDK II UEFI: 16yr PXE flaw, no tagged fix yet.

Patch Now | Oct 28
Tailscale officially confirms nearly a dozen SSH flaws from last week's Tailworm report. Patches coming, keep mitigations in place.
Microsoft: emergency update distrusts compromised eMudhra cert keys. Apply today.
Apple: CoreGraphics spyware patch
#CERTUGCC

Patch Now | Oct 27
F5 NGINX (CVSS 9.2 x3): heap overflow and use-after-free flaws across Plus, Open Source, Ingress. Patch or apply mitigations today.
Plex2Shell (CVSS 9.8): chained flaws, CISA deadline passed. Update now.
Cisco Nexus: 5 critical NX-OS flaws, root access.

Patch Now | Oct 26 (weekend recap)
PHP2Shell escalated hard: millions of attempts, Mirai deployment, a government agency hit. Patch today.
Node.js "Node2Shell" (CVE-2026-111497): Brotli RCE, update now.
Tailscale: 11 unpatched flaws, no fix yet, tighten SSH rules.
#CERTUGCC

National CERT/CC retweeted
After the keynote, @JonnnieT presented a cash prize to St. Lawrence, winners of the cybersecurity hackathon.
Congratulations to the team, and well done to all the young innovators helping to keep Uganda’s digital space safe. 🇺🇬
#NITAU #DigitizeUG #EastCon2026


@JonnnieT Manager Governance and Risk at @NITAUganda1 delivered a keynote address at the 2026 EastCon Cybersecurity Symposium, hosted by @milimatechug at the National ICT Innovation Hub, Nakawa.
The symposium brought together government, industry, academia and students to talk about:
🛡️Emerging cyber risks and fraud
🛡️Digital trust and data protection
🛡️Building Uganda’s national cyber resilience
At NITA-U, we remain committed to keeping Uganda’s digital space safe and secure for everyone.
#NITAU #DigitizeUG #EastCon2026


National CERT/CC retweeted
@JonnnieT Manager Governance and Risk at @NITAUganda1 delivered a keynote address at the 2026 EastCon Cybersecurity Symposium, hosted by @milimatechug at the National ICT Innovation Hub, Nakawa.
The symposium brought together government, industry, academia and students to talk about:
🛡️Emerging cyber risks and fraud
🛡️Digital trust and data protection
🛡️Building Uganda’s national cyber resilience
At NITA-U, we remain committed to keeping Uganda’s digital space safe and secure for everyone.
#NITAU #DigitizeUG #EastCon2026