




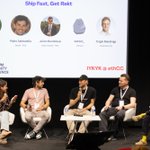
⚠️ It has just been decided to delay the Glamsterdam hard fork on the Hoodi testnet because of security impacts we identified in this blog post: chainsecurity.com/blog/glams…
We already found 13 real-world examples and are in responsible disclosure with the affected projects.
Please check your contracts as soon as possible, as the EF is determining how many contracts are impacted in which way.
Feel free to reach out to us with questions via [email protected].


Security for institutions has been in our DNA since our days at PwC Switzerland in 2020.
If you're bringing assets, payments or treasury on-chain, Pietro is the person to talk to at Bluechip26.
📍 Vienna, Nov 10-11. DM us to talk.

🎙️ Pietro Carta (@PtrCarta) is speaking at Bluechip26, the Crypto Safety Conference!
Pietro is Partner & Senior Blockchain Engineer @Chain_Security, one of the longest-standing blockchain security firms, securing critical code & architecture across crypto since 2017.
Bluechip26 is the world’s first and leading conference dedicated to crypto safety. Get tickets at conference.bluechip.org.
📍 Nov 10-11 in Vienna

ChainSecurity retweeted

@chain_security team is going 🥰

How likely is an address collision attack at 2⁸¹ hashes?
- Some audit competition reports said 86%.
- In fact it is 63%.
Why? They apply the classic birthday-paradox formula, counting collisions that aren't useful to the attacker. We break down the correct model in this blog: chainsecurity.com/blog/addre…

We're always happy to bring a security perspective to the Vault Summit. This time in Singapore! 🔜

ChainSecurity is one of the longest-established blockchain security auditing firms, providing smart contract and blockchain security audits since 2017.
It serves the largest DeFi protocols, including Aave, Lido, Sky, and Polymarket, alongside institutions like Circle, banks, and regulated exchanges.
@Spittfires_, Blockchain Security Engineer at @chain_security, will take the stage at Vault Summit Singapore.
9 October · sg2026.vaultsummit.xyz

ChainSecurity retweeted
How to make security interesting to a wider audience?
Apparently, add AI.
Had a great time talking with @pashov, @allypry and @jgattermayer at @ETHSofiaBG.

We're very happy to contribute our engineer time to @stblcnsummit. Meet us in Singapore!

ChainSecurity is one of the longest-established blockchain security auditing firms, providing smart contract and blockchain security audits since 2017.
It serves the largest DeFi protocols, including Aave, Lido, Sky, and Polymarket, alongside institutions like Circle, banks, and regulated exchanges.
Yanis De Busschere, Security Engineer @chain_security, moderates the fireside "Purpose-Built Before It Was Cool" at Stablecoin Summit Singapore.
Oct 8 · sg26.stablecoinsummit.com

Launching a token means putting critical code under scrutiny. We're happy to provide Charter builders with independent security audits, identify risks before launch and offer a security signal investors and ecosystem partners can rely on.

"Building a Security Playbook for Solana" at @solana summit by @SuperteamBLKN
Creating best practices for secure Solana DeFi development, based on our audit findings and learnings

This framework allows a flexible way to manage assets across multiple chains while ensuring that losses can be limited, even in the event of an operator secret key compromise.

Makina Protocol v1.3 is now live.
This release upgrades Makina’s cross-chain infrastructure, improves operational controls, and strengthens protocol safeguards.
The main novelty in v1.3 is the introduction of @chainlink CRE to power Makina’s cross-chain accounting.
Chainlink CRE brings a leaner snapshot-based accounting model and additional sanity checks.
Makina v1.3 also gives operators more granular cross-chain controls. Individual Spoke Calibers can now be enabled or disabled, providing finer control over cross-chain operations and transfers.
Audited by @chain_security.
Full information can be found in the post below.
We're in Belgrade and happy to let you know @k_besic will present a playbook that will make your Solana development more secure-by-design. Or as he put it:


Kenan Bešić, partner and senior blockchain engineer at @chain_security, is joining us at Solana Summit Serbia.
Kenan is a top-tier security researcher and DeFi auditor across Solana and Ethereum, ranked top 70 all-time on Immunefi and known for discovering the "read-only reentrancy" vulnerability class.
Aug 26-27, Belgrade, Sava Centar.
ChainSecurity retweeted

We've been getting more audit requests lately.
Are you guys bullish, or just back from summer holidays?

See you at @belgradebw 🙌

Speaker announcement 📢
Marc from @chain_security joins Web3 Security Summit to talk about what happens to lending markets when an L2 sequencer goes down: stale prices, bad debt and broken assumptions.
See you in Belgrade 🫡

We reviewed the new YBLendingOracle, allowing YB shares to be priced correctly and used as collateral.
Thanks @yieldbasis for the continued trust and collaboration!

Oracle for using yb-positions as lending collateral is audited by @chain_security.
Builders can find live audited oracles here by ENS addreses:
wbtc.oracles.yieldbasis.eth (and similar for cbbtc, tbtc, weth)
chainsecurity.com/security-a…

ChainSecurity retweeted

It is rare to meet a top tier team irl in this space (outside of a conference), but this month I was lucky to meet the @chain_security team
Great office, amazing people, fantastic nature. Thanks for the invite, gigabrains 🤝

The most critical subjects we reviewed include arithmetic precision & asset solvency. Full report available👇

A new Aave V4 security audit by @chain_security is now available, covering the Liquidity Hub, Spoke, and position manager contracts.
Review it below.

ChainSecurity retweeted

The ChainSecurity audit of Mezzanine is public. Zero Critical findings. Zero High. This sits alongside the Certora formal verification audit, a Sherlock audit, and an ongoing operational security audit. Full report: chainsecurity.com/security-a…
