

Threat intelligence | Content Manager en X Sec
argentina
Joined November 2014
- Tweets272
- Following97
- Followers283
- Likes458






Soy DrPlaga
Threat Intelligence, ciberseguridad defensiva, OSINT, CVEs, ransomware, malware, leaks y laboratorio real.
Acá no vendo humo: separo evidencia, claims y ruido.
📌 Menos humo, más evidencia.
🧪 Nos vemos en los logs.
#DrPlaga #ThreatIntel #CyberSecurity
🤖 Made with AI

Dr.Plaga retweeted

El lado del mal - Cómo recuperar claves de Wallets de Criptomonedas Exodus : "Not Your Keys, Not Your Coins"... ¿o tal vez sí? elladodelmal.com/2026/10/com… #Criptomonedas #Wallets #Cracking #Hacking #Web3 #BitCoin #Ethereum #IA #AI #BIP39 #Criptoanálisis #Criptografía

Dr.Plaga retweeted

¡Seguimos presentando las charlas de nuestra 7.ª edición! 🚀
Nuestro próximo speaker confirmado es @hbenja_m aka bronxi , quien estará presentando:
🔥 “Entender, Usar, Hackear, Repetir: hunting con LLMs”
Pentester, Bug Bounty Hunter y speaker, Benjamín es un apasionado por la tecnología y especialmente por el hacking. Actualmente trabaja como Staff Engineer en el equipo de AI de Strike, y llega a la Bug Bounty Village para compartir su experiencia explorando el uso de LLMs aplicado al hunting. 🤖🔎
¡Gracias Benja por sumarte a la Bug Bounty Village en Ekoparty Buenos Aires 2026 y compartir tu conocimiento con la comunidad! 🙌
[EN] We’re continuing with the talk announcements for our 7th edition! 🚀
Our next confirmed speaker is @hbenja_m aka bronxi, who will be presenting:
🔥 “Entender, Usar, Hackear, Repetir: hunting con LLMs”
A Pentester, Bug Bounty Hunter, and speaker, Benjamín is passionate about technology and especially hacking. He currently works as a Staff Engineer on Strike’s AI team and is joining the Bug Bounty Village to share his experience exploring the use of LLMs in hunting. 🤖🔎
Thank you Benja for joining us at the Bug Bounty Village at @ekoparty Buenos Aires 2026 and sharing your knowledge with the community! 🙌
#ekoparty2026 #bugbountyvillage #bugbountyargentina #bugbounty #cybersecurity

Dr.Plaga retweeted

Desde el domingo, @DonWebOficial tiene fuera de servicio el nodo NOVA. El 100% de sus Cloud Servers sigue inaccesible, sin tiempo estimado de recuperación. Tampoco se puede acceder a los backups ni migrar los servicios.
Pero esta caída abre una discusión bastante más grande.🧵

Dr.Plaga retweeted

🇦🇷 Alleged Database Containing 8.1 Million Argentine Citizen Records Advertised on Cybercrime Forum
A threat actor is advertising a dataset allegedly containing more than 8.1 million records associated with Argentine citizens.
According to the listing, the database reportedly includes:
* National ID numbers (DNI)
* CUIT tax identification numbers
* Full names
* Year of birth
* Province information
* City/town information
The seller claims the dataset covers multiple Argentine provinces, including Buenos Aires, Córdoba, Corrientes, Entre Ríos, Jujuy, La Rioja, Catamarca, and Mendoza, with records primarily covering individuals between the ages of 18 and 70.
The actor further claims the database was updated in May 2026 and contains approximately 8,175,364 unique records. The dataset is reportedly being offered for sale through a private transaction.
If authentic, the exposed information could be leveraged for:
* Identity theft
* Financial fraud
* Account verification bypass attempts
* Social engineering campaigns
* Targeted phishing operations
* Large-scale profiling of citizens
At the time of writing, Daily Dark Web has not independently verified the authenticity of the dataset or the source of the alleged records.
Analyst Note: National identity datasets remain among the most valuable commodities on cybercrime forums because they can be combined with breached credentials, financial records, and telecom data to facilitate large-scale fraud and impersonation attacks.
#DDW #Intelligence #DarkWeb #Argentina

Dr.Plaga retweeted

CYBER INTELLIGENCE ALERT: ARGENTINA DATA API — ARGENTINA 🇦🇷
[STATUS: UNCONFIRMED / VISIBLE EVIDENCE]
A new commercial activity has been detected offering public access to a cybercrime API targeting Argentine citizens. The service, which has allegedly operated privately, claims to integrate databases from RENAPER (National Registry of Persons).
Affected Entity: Argentine citizens, including government and political figures.
Threat Actor: LaPampaLeaks 👤
Date of Registration: 2026-06-03 📅
Reported Scope: The actor claims to offer access to millions of records, including information on families, address history, and mobile phone data.
State of Evidence and Assessment 📊
Evidence: The actor has published identified screenshots showing the API endpoints and the alleged data extracted from Argentine public figures.
Methodology: The actor claims the API is "100% local," operating independently of external government systems to avoid disruptions.
Data Exposed: The service promotes access to specific endpoints, such as /renaper-id, /familiares-arg, and /direccion-personas, among others.
Individuals Impacted: The actor's documentation mentions the compromise of data from various individuals, including President Javier Gerardo Milei, Congresswoman Lilia Lemoine, SIDE (Argentine Intelligence Secretariat) officials, and former President Cristina Kirchner.
Mitigation Recommendations 🛡️
Data Security: Government entities should audit their database access systems to rule out security vulnerabilities that allow for the mass scraping of data. Personally identifiable information (PII).
Technical Caution: Due to the unverified nature of the platform, any interaction with the domains or services promoted by the actor is discouraged, given the potential for associated cybersecurity risks.
Strategic Monitoring Tools 🌐
Intelligence Platform: analyzer.vecert.io 💻
Security Verification: monitor.vecert.io 🛡️
#CyberSecurity #DataLeak #Argentina #RENAPER #Doxing #LaPampaLeaks #ThreatIntelligence #CyberAlert #VECERT #UnderInvestigation


Medidas mínimas:
Revisar commits recientes y workflows nuevos.
Rotar secretos expuestos o sospechosos.
Limitar permisos de GitHub Actions.
Validar OIDC y runners.
Bloquear ejecución automática de PRs no confiables.
Menos humo, más evidencia.
#DrPlaga #SupplyChain #DevSecOps
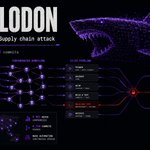
Lo relevante: los workflows maliciosos buscaban ejecutar payloads dentro del entorno CI/CD.
Eso puede exponer:
secretos de GitHub Actions
tokens cloud
SSH keys
configs Docker/Kubernetes
credenciales de Terraform/Vault
variables de entorno sensibles
Megalodon: más de 5.500 repos GitHub apuntados en una campaña supply chain contra CI/CD.
El ataque no fue “romper la app”. Fue ir directo al sistema nervioso del desarrollo: GitHub Actions, secretos, tokens, SSH keys y credenciales cloud.
El pipeline también sangra.
🤖 Made with AI


Prioridad defensiva:
• revisar exposición Drupal/PostgreSQL
• endurecer firma y confianza de binarios
• medir patch lag real
• monitorear leaks y phishing post-brecha
• mirar OT como continuidad operativa, no como “red rara del galpón”
Nos vemos en los logs.
La lectura del día:
El malware ya no solo busca ejecutarse: busca parecer legítimo.
Los CMS siguen siendo superficie crítica.
Las vulnerabilidades ya pesan más que las credenciales en brechas.
Y la extorsión por datos sigue reemplazando al ransomware clásico.
#CyberSecurity
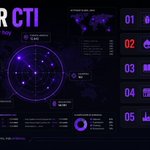
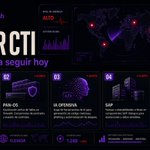
RADAR CTI | 21 mayo 2026
5 temas para seguir hoy:
Fox Tempest / malware signing
Drupal highly critical
Verizon DBIR 2026
7-Eleven / ShinyHunters
OT bajo ransomware
Menos ruido, más evidencia.
DrPlaga.sh
#DrPlaga #CTI
🤖 Made with AI

Dr.Plaga retweeted

"que no crean que nadie los va a mirar"
No lo digo yo, esa fue la recomendación de un grupo de ransomware a las Pymes para que no terminen en una filtración de datos en la entrevista que hizo @CodeBugBOX al grupo Chronus Team.

Hablé con “Chronus Team”.
Filtraciones, exposición de datos, motivaciones y señales para defensores.
Contexto, evidencia y preguntas incómodas.
Artículo completo:
linkedin.com/pulse/entrevist…
#DrPlaga.sh #CTI #CyberSecurity
