

Staring at the world from my own little Idaho. Conservative 2A tech geek. Ska music is under rated. I want a HumV. Small guy, helping the small guy. Dog lover.
East Idaho, USA
Joined October 2022
- Tweets11K
- Following708
- Followers2.7K
- Likes51.4K





Idaho Over Under 🇺🇸 retweeted

East New York
A man was taped to a pole after being caught speaking to minors with his pants down.
You might say that this is unlawful imprisonment, and you might ask how many times he had been caught in the past, and nothing was done about it.
Idaho Over Under 🇺🇸 retweeted

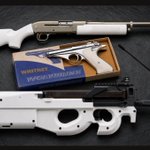
Beretta and La Vallée Build a Shotgun You Can See Into – tinyurl.com/5cfwh6sv

Idaho Over Under 🇺🇸 retweeted

#BREAKING: A Mexican lynch mob broke two child rape suspects out of jail and beheaded one of them.
Idaho Over Under 🇺🇸 retweeted

Just saw an ad where Governor Brad Little said he “cut the tax on groceries.”
He in fact, did not.

Idaho Over Under 🇺🇸 retweeted

Through the first two days of Early Voting in New York City, the electorate is:
🔵 76.3% Democratic
🔴 11.2% Republican
⚪️ 10.4% Unaffiliated
🟣 12.5% Age 18-34
🟢 17.4% Age 35-49
🟠 29.3% Age 50-64
🟡 40.9% Age 65+
Significantly bluer than 2024!
Idaho Over Under 🇺🇸 retweeted

🇺🇸 A USPS letter carrier in Utah just got indicted for allegedly dumping more than 300 mail-in ballots in a church parking lot dumpster.
Acting Deputy Attorney General Trent McCotter laid it out: "The carrier knew they were ballots. They were clearly marked. He threw them in the trash anyway. They never reached the June 23 primary voters."

Idaho Over Under 🇺🇸 retweeted

Unfortunately , the many of the Basque population in Boise are flaming socialist /liberals . I am Basque and it amazes me the inculcation of socialist ideology in many of them .
Idaho Over Under 🇺🇸 retweeted

🚨As numerous federal investigations into Ilhan Omar’s immigration and financial history continue, the congresswoman has just made her first public appearance in nearly four weeks (since September 22) to solicit financial contributions from supporters.
Based on buildings visible through a window in recently released footage of Ilhan Omar, online investigators have traced her location to the “Somali American Community Outreach and Consultancy Center” in Minneapolis.
The organization, which advertises 24-hour operations seven days a week, maintains a notably vague and seemingly incomplete website, as if it was hastily assembled and left unfinished.
The website identifies no owner, director, or other organizational leadership. The only specific service advertised is “consultancy,” with no substantive explanation of what services are provided.
Furthermore, the organization’s listed address corresponds to the Brian Coyle Neighborhood Center, an entirely different and seemingly unrelated organization.
The group also advertises a nationwide membership network, an extensive calendar of social events, professional speakers, and charitable initiatives. However, its website provides no corresponding event calendar, membership directory, or any supporting documentation whatsoever.
Follow: @MorseReport

Idaho Over Under 🇺🇸 retweeted
//The Wire//1300Z October 21, 2026//
//SPECIAL REPORT//
//BLUF: MAJOR CYBERSECURITY VULNERABILITIES EXPOSED GLOBALLY, AS TWO SEPARATE MAJOR CODING FLAWS AFFECT MAJORITY OF INTERNET-CONNECTED DEVICES.//
-----BEGIN TEARLINE-----
Global: Around the world, two major cybersecurity incidents are underway. The first incident involves an Indian cybersecurity firm using poor cybersecurity practices in generating Certificate Authorities, which might allow malign actors to exploit web-connected devices. The second issue revolves around an exploit discovered in the PHP programing language, which could allow malign actors to intercept traffic to and from affected web servers, and theoretically take control of them.
Analyst Comment: Today will be a very interesting day for the internet. Neither issue is worth undue panic, but these incidents are causing questions for the bedrock of internet security. In terms of what the average user should do, today will be "update day" for the majority of the planet. Anyone who runs internet-connected home servers, hobby PC's, or muddles in the tech world at all, will probably want to update their systems sometime today.
For more causal internet users, the immediate actions that would be helpful are simply to adhere to good internet security practices: Enabling two-factor authentication for web-connected devices, not re-using passwords, and being aware that phishing attempts will be extremely likely over the next few days, which will seek to capitalize on these major vulnerabilities.
-----END TEARLINE-----
Analyst Comments: The timing of two major cybersecurity incidents taking place at the same time is exceptionally rare and very remarkable. To be clear, these issues are totally separate from each other, with neither one causing the other. However, due to the sheer scale of both incidents, it's possible that some sort of compounding effect could be achieved. One major global tech vulnerability is bad enough, but two on the same day is very serious. Knowing the rough details of how both incidents came to be, is helpful for understanding the seriousness of these events.
The first incident revolves around a vulnerability being discovered within the ecosystem for issuing certificates for various websites. Under normal conditions, when a person visits a website (such as (https:)//www.google.com), a certificate is used to ensure that the website is genuine. Essentially, the web browser itself cross-checks that website with a trusted authority (called a Certificate Authority), which vouches for that website being genuine. This happens after the website gives the webs browser it's certificate, which the browser or app can automatically check against a big list of genuine certificates, to make sure the certificate provided by the website matches what it should be. 18 months ago, the Indian cybersecurity firm eMudhra issued a series bad certificates that had extremely low security; instead of being a long string of numbers which would be hard to crack, some certificates ended up being only the number 4. Since these certificates were genuine, and came from a genuine trusted authority, websites and platforms which trusted these bad keys are now at major risk of exploitation, and malign actors could forge fake keys for any website on Earth, and the fakes would be accepted by most devices (because the keys are genuine, they're just bad).
To frame the magnitude of this incident with an analogy, imagine that a large safe company builds a safe that uses a master code to get into their safes. And after selling and installing a bunch of those safes in homes around the world for 18 months, it becomes clear that the master code to get into most of those safes, was the number 4. Under the right conditions, someone who finds the safe could theoretically guess the code without the owner ever doing anything wrong on their part. More importantly, a thief could access the safe for as long as they want (using the master "code"), and the owner would be none the wiser. Now imagine that a thief actually had access to the safe company, and could generate a master key of their own, that would work with any safe sold by that company. That's essentially what has been happening for 18 months. As far as how many websites have actually been compromised, the true number is not known. Theoretically, this incident has the potential to affect every single website and internet-connected device on the planet. eMudhra themselves state that zero fake certificates have been issued using this vulnerability. So in terms of magnitude, the potential scale of this is somewhere between zero, and every device on Earth. Considering that eMudhra themselves allowed this shockingly bad incident to take place (and not being noticed by two separate security audits), trust in this company is quite low. Moreover, this vulnerability will probably be made worse by an exponentially more serious separate incident that was disclosed overnight.
The second major cybersecurity incident which was revealed overnight, revolves around a problem being discovered within the PHP programming language. As noted with the eMudhra vulnerability, when a user visits a website, a lot of stuff happens in the background. Certificates get exchanged, databases are consulted, and if all goes well, data is sent to a user's device to load the webpage. PHP is one of the programming languages used to make all of this happen. As of early this morning, a vulnerability was discovered within this programming language itself, which can allow malign actors to breach web servers, by leveraging a vulnerability in the way that PHP handles data from the server. In this way, the PHP vulnerability is much like the eMudhra vulnerability, in that both can allow malign actors to gain unauthorized access to systems. The differences are that both vulnerabilities are completely separate and unrelated...but in theory one could compound on the other, especially since IT departments are scrambling to fix both issues right now. The PHP incident is more serious, because the details were leaked before patches were written, and malign actors were indeed observed trying to take advantage of the vulnerability ahead of it's discovery.
Normally, major cybersecurity incidents are not disclosed on a more widespread basis, until patches have been rolled out to fix the problem. This is to prevent malign actors which might not have noticed the vulnerability from knowing about it and capitalizing on it. In this case however, the vulnerability was so severe, that the PHP Foundation released the notice before patches went live. The British National Cyber Security Centre even went as far as to suggest organizations bring their systems offline until a patch is released...in some cases this vulnerability is significant enough to warrant pulling server racks, and websites/servers going offline completely, until the fix is pushed out. As of this morning, many government websites were taken offline globally, and throughout the day millions of websites will also probably be taken offline by IT departments as a precautionary measure, until fixes can be rolled out.
In terms of mitigating both events, the most substantial risk will be for internet connected devices which do not receive regular updates. Using a smartphone or a regular web browser will be fine as mass updates were already pushed out days ago, before the disclosure of the certificate vulnerability was made public. The real risk will be for 'Internet of Things' or IoT devices: Smart thermostats, portable power stations, lawn irrigation systems, doorbells, smart TV's and appliances, utility meters, streetlights, dash cams, remote data servers, and many other older devices that have internet connectivity, and still use the bad set of keys. These are the kind of IT disasters that get technicians woken up during the night, and in both cases IT departments around the world are rapidly patching their own devices to fix the vulnerability now that two major cybersecurity incidents are public, and have the potential to become much more serious problems within the cyber realm.
Analyst: S2A1
Research: publish.obsidian.md/s2underg…
NomadNet: 5fa68c88be727a0e1a250a75e5e79269
Disclaimer: No LLMs were used in the writing of this report.
//END REPORT//
There was an uprising on Mars back in the 90s. I went there and straightened things out. Brought my kit.


Idaho Over Under 🇺🇸 retweeted

>ATF kills 90% of the NFA
>*one week later*
>Multiple mass shootings as if MK Ultra sleeper agents were activated
I've never watched a TV show where, at the end every episode, I yell "holy sh*t!". Well. Maybe LOST but.

Idaho Over Under 🇺🇸 retweeted

🚨#BREAKING: According to Channel2 NOW, Kaylub Giamanco has reportedly been identified as the Good Samaritan who stopped the gunman during Thursday’s shooting at Silver Rail Elementary School in Bend, Oregon.
A personal friend has claimed Giamanco was indeed the man who intervened during the attack.
He is being described as a brave man who stepped up when it mattered most.
If this is the man who stopped the shooter, he is a hero.
channel2now.com/2026/10/16/a…
