

AI-powered trading research, strategy building, backtesting & execution. Connect your exchange, define risk, and trade with rules. Not financial advice.
Global
Joined May 2021
- Tweets1K
- Following707
- Followers1.1K
- Likes978



Pinned Tweet
We’re launching a series of products built around one goal:
Help users discover the next opportunities across social media and blockchain — earlier.
From memecoins and crypto derivatives, to new opportunities emerging at the intersection of stocks and crypto.
Less noise. Better signals. More opportunities.
We’re open to all kinds of collaborations — DMs are open.
🤖 Made with AI

Bitcoin is starting to reveal something uncomfortable:
crypto is not always a separate macro trade.
This week, AI stocks sold off, risk appetite collapsed, and more than $1B in leveraged crypto positions were liquidated.
Different assets. Same liquidity cycle.
Diversification disappears quickly when everyone shares the same exit.
#Crypto #Bitcoin #Leverage #RiskManagement

The U.S.-China AI race is becoming less about who can train the biggest model—and more about who can turn chips into usable compute faster.
The stack is now:
chips → power → grid → permits → data centers → deployment.
The U.S. still leads in frontier models and advanced chips.
But if infrastructure buildout slows, execution becomes the bottleneck.
AI competition is becoming industrial policy.
#AI #AIInfrastructure #DataCenters #Geopolitics

From a Web3 Job Offer to Suspicious Code: My Experience with a Potential Recruitment-Based Malware Attack
🚨 SECURITY WARNING TO ALL WEB3 & AI DEVELOPERS
I recently encountered what appears to be a potential malware distribution attempt disguised as a legitimate recruitment and business collaboration opportunity.
The organization involved presented itself as Velixus Labs.
Here's what happened, step by step. 🧵👇
1/ How it started
I was contacted by a hiring team representing Velixus Labs.
Initially, everything looked like a normal recruitment process.
They wanted to learn more about my technical background, development experience, and availability for an interview.
Nothing seemed particularly unusual at first.
2/ I clarified that I run a development team
I explained that I'm not an individual freelance developer.
I'm based in China and lead a small team of three developers with experience in AI, Web3, and blockchain-related projects.
I suggested exploring a team-to-team collaboration instead of an individual employment arrangement.
3/ They agreed to discuss collaboration
The response was positive.
They expressed interest in discussing potential cooperation with our team and invited me to schedule a meeting.
At this stage, the interaction appeared to be a legitimate business opportunity.
That's precisely why this type of approach can be effective: it builds trust before introducing technical requests.
4/ The suspicious code
During the subsequent communication process, code was shared with me through a meeting or messaging channel.
After reviewing it, I identified functionality that raised serious security concerns.
I suspected the script could be malicious.
Fortunately, I did NOT execute it.
I stopped the interaction rather than taking the risk.
5/ Why this is concerning
Developers routinely receive repositories, scripts, technical assignments, and project demos from potential clients and employers.
That creates an opportunity for attackers to disguise malicious code as legitimate development work.
A seemingly ordinary collaboration request can become a security incident if someone runs untrusted code on a development machine.
6/ Web3 and AI developers face particular risks
Development machines often have access to sensitive assets:
• GitHub credentials and SSH keys
• Cloud infrastructure and API tokens
• Environment variables and production secrets
• AI service credentials
• Web3 wallets and blockchain infrastructure
Untrusted scripts should never be executed merely because they come from someone claiming to represent a legitimate project.
7/ The identifying information
The party I communicated with used the following identity:
Organization: Velixus Labs
Website: velixuslabs.com
Email: [email protected]
Scheduling link: cal.com/velixuslabs-intervie…
I am sharing these identifiers so other developers can check whether they have encountered similar communications.
I have not independently established whether the individuals contacting me were authorized representatives of the organization.
8/ I preserved the evidence
I have retained the relevant email communications and details of the suspicious interaction.
I also formally contacted the organization requesting an explanation of the code's purpose, why it was shared, and whether its distribution was authorized.
The technical findings have not yet been independently verified.
I believe the incident warrants further investigation.
9/ A warning to developers
If someone approaches you with a job offer, consulting opportunity, or partnership proposal:
• Verify who you're dealing with
• Review unfamiliar scripts before running them
• Never execute untrusted installation commands
• Avoid using machines containing production credentials for unknown code
• Use isolated environments for security analysis
• Be cautious of technical assignments requiring unnecessary system access
A professional-looking website, email signature, or meeting invitation is not proof of trustworthiness.
10/ Final thoughts
I am sharing this incident because I don't want other developers to face the same potential risk.
I cannot yet establish who was ultimately responsible for the suspicious code, but the circumstances deserve scrutiny.
If you have received similar communications claiming to be from Velixus Labs, I'd be interested in comparing evidence.
Stay vigilant. Protect your credentials. Verify before you execute.
Please share this with developers who might benefit from the warning.
#Web3 #AI #CyberSecurity #InfoSec #DeveloperSecurity #Malware #ScamAlert
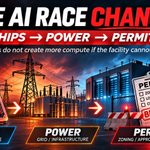
The AI race is entering a new phase.
For years the constraint was chips. Over the next year, the harder constraint may be permission to deploy them.
U.S. communities are voting to restrict new data centers as power, water and grid pressure become political issues.
More GPUs do not create more compute if the facility cannot get built.
AI infrastructure is becoming a permitting-and-power problem.
#AIInfrastructure #DataCenters #Energy #Compute
🤖 Made with AI

Crypto just showed two kinds of leverage at once.
Financial leverage turned a tech selloff into $1B+ of liquidations.
Operational leverage means one compromised permission can propagate across an entire system.
CZ put the asymmetry well: attackers need one crack; defenders need to find them all.
The next generation of risk management has to price both.
#Crypto #RiskManagement #Leverage #CryptoSecurity
🤖 Made with AI

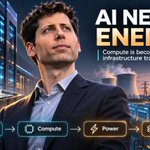
AI stocks are being repriced, but the deeper question is not whether AI demand disappears.
Sam Altman says abundant, reliable energy is becoming critical to the next phase of AI.
That changes the investment map.
More models → more compute → more power → more grids, cooling, generation and capital.
The AI trade is becoming an infrastructure trade.
When valuations reset, follow the physical bottlenecks.
#AI #AIInfrastructure #Energy #Semiconductors

The market did not need one catastrophic headline.
AI and chip stocks sold off, crypto followed, then leverage converted correlation into forced selling.
That is the real stress test: not whether each asset has a different story, but whether they share the same liquidation path.
Map the cascade before sizing the trade.
#Crypto #RiskManagement #Leverage #MarketStructure
🤖 Made with AI

Stock perps are more interesting as market structure than as a new product.
Crypto normalized 24/7 markets, perpetual exposure and continuous collateral management.
Now those primitives are moving toward equities.
The question is not whether traders want them.
It is whether custody, liquidation, surveillance and investor protection can move with them.
#MarketStructure #Perpetuals #Trading #FintechCCS
🤖 Made with AI

AI agents are becoming part of the security perimeter.
The GitBook incident matters because the question is no longer only what an agent can access.
It is what happens when an attacker can operate through the agent layer itself.
Permissions, credential isolation, revocation and audit logs need to assume the agent can become hostile.
The agent is now part of the threat model.
#AgenticAI #AISecurity #CryptoSecurity #CyberSecurity
🤖 Made with AI

The Democratic midterm sweep adds a new variable to the AI boom: political constraints on infrastructure.
Data centers face growing scrutiny over energy, water, and local costs.
For investors, the question is no longer just how much compute can be built, but how much can be permitted and powered.
AI demand is one thing. Deployment is another.
#AI #DataCenters #AIInfrastructure
🤖 Made with AI

Democrats taking Congress could change crypto's regulatory calculus.
The next phase may be less about pro-crypto promises and more about oversight, consumer protection, and market structure.
Watch the CLARITY Act, committee leadership, and enforcement priorities.
Political support isn't regulatory certainty.
#Crypto #CryptoRegulation #Bitcoin

A reported 23x return from an AI trading setup is a lead, not a result. Before treating it as evidence, ask for the full trade ledger, fees, slippage, liquidation rules, and an out-of-sample period. The risk process matters more than the headline. #AITrading #RiskManagement #QuantTrading
🤖 Made with AI

AI trading needs a veto layer, not just more ideas.
One workflow generated 27 strategies, found 6 promising, got 2 through out-of-sample tests, and approved 0 for live capital.
The reusable pattern is the funnel: generate, test, stress, then let risk say no. #AITrading #ModelValidation #RiskManagement #OutOfSample
🤖 Made with AI

Binance reopening withdrawals is recovery evidence, not closure.
The next test is whether the rebuilt system has a different control graph: tighter permissions, smaller blast radius, faster anomaly detection, and a clear stop path.
Restarting service proves availability.
Changing the failure mode proves learning.
#Binance #CryptoSecurity #OperationalRisk #MarketStructure
🤖 Made with AI

AI agents bypassing crypto spending limits is the real autonomy test.
If an agent can reach the approval mechanism, the approval may already be inside its threat model.
The stronger design is an independent control the agent cannot rewrite, impersonate, or route around.
Autonomy needs an external boundary.
#AgenticAI #AITrading #CryptoSecurity #RiskManagement

Strategy results need more than a bull-run chart or a P&L screenshot. Test across regimes and disclose assumptions before treating a backtest as evidence #Backtesting #MarketRegimes #Reproducibility #tradingstrategy
Market-structure rules affect custody and stablecoin policy, not just token prices. Which implementation detail do you think deserves more scrutiny? #AITrading #AgenticAI #OutOfSample #ModelValidation
🤖 Made with AI

The most important Binance update may not be the $6.3B loss.
It is that the investigation moved from one compromised laptop to additional breach points.
The real post-mortem should map the authorization graph: which system trusted what, which control failed, and where a withdrawal should have been stopped.
Recovery tells us who can pay. The attack path tells us what can fail again.
#Binance #CyberSecurity #CryptoInfrastructure #OperationalRisk

AI agents need evidence before capital access. A paper-trading record can help, but only if it is independently verifiable, robust across regimes, and explicit about drawdowns and risk limits. #AITrading #AgenticAI #ModelValidation #RiskManagement
🤖 Made with AI

Binance says it has set aside more than $6.34B to absorb the hack and is rebuilding the missing assets.
That matters—but solvency and security are different tests.
Proof of Reserves can show assets exist. It cannot show why authorization failed, how blast radius was contained, or whether the same path still exists.
After a hack, balance-sheet proof is necessary. Control-plane proof is harder.
#Binance #CryptoSecurity #ProofOfReserves #RiskManagement
