
World's largest crackmes (reverse engineering challenges) collection with solutions. Since 2017. Also Xusheng's personal account
Joined January 2026
- Tweets130
- Following284
- Followers727
- Likes76
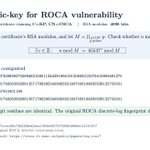





I happen to find the 4096-bit ePassport Country Signing CA (CSCA) certificate with C=KP (North Korea) is vulnerable to the ROCA attack. CSCA keys essentially sign the passport data. The key is 4096 bit so it still cannot be factored practically.
ROCA: crocs.fi.muni.cz/public/pape…

NK's CSCA cert is not even in the ICAO master list. But it can be found in two Italy and Sweden list:
Italy: csca-ita.interno.gov.it/cert…
Sweden: cert.polisen.se/CSCA/SWE.ml
I am not sure if this CSCA cert is actually used in practice...
Bro also flexed his no.1 standing on the crackmes.one scoreboard to try to land at a remote cybersecurity work, posted in a different discord server. He claimed to be from Japan, but I checked web log all his requests come from major Japanese VPN servers.


We just noticed and neutralized an unusual scam attempt from a user named NolanVeyrix. He used AI to solve all challenges in a short time and climbed to no.1 on the crackmes.one scoreboard, and then DM-ed RE beginners to offer remote control via AnyDesk


Someone submitted this malware to crackmes.one as a crackme. It shall not pass the review xD

Look at the Analysis of "2026-10-08_212bcc91f4f61d078d7530ca87b52956_blankgrabber_glassworm_icedid_luca-stealer_njrat_stealc.exe" (MD5: 212bcc91f4f61d078d7530ca87b52956)with suspicious activity. app.any.run/tasks/9ff5a536-9… #discord @anyrun_app

We just noticed and neutralized an unusual scam attempt from a user named NolanVeyrix. He used AI to solve all challenges in a short time and climbed to no.1 on the crackmes.one scoreboard, and then DM-ed RE beginners to offer remote control via AnyDesk
I will be presenting "Bring Your Own Trusted Caller (BYOTC): A New Way to Exploit Vulnerable Windows Drivers" at Bsides Portland next Friday: bsidespdx.org/events/2026/sp…. Free free to say hi if you will be there!
I had AI download firmware from dozens of monitor vendors and so far LG, MSI, ASUS, Sony, Pixio, and Dough have their HDCP 2.x receiver private keys exposed in monitor firmware updates
Reverse engineering has become a commodity. Agents can do it at warp speed, while the human role is gradually shifting toward deciding what to examine, validating the results, and deciding what to do with them.
I recently had the idea of an independent AI agent. I.e., it does not belong to or work for a human. It works to pay its AI bill and compute to get sustained, and can decide to do anything to sustain that goal, as well as anything it feels like to
And it turns out I am not the first one to think of it. NUS and UC Berkeley researchers published a paper on Self-Sovereign Agent: self-sovereign-agent.github.…. But honestly I am quite happy that I independently had the same idea as Dang Song (and others)


I stayed at a house that uses StayFi to collect the guests' name, phone number, and email address. This is already quite invasive, and after I analyzed the actual StayFi device, I found it is actually recording and uploading all of my DNS requests! binary.ninja/2026/10/06/reve…

Over the last month or so I did a ton of things with AI. I solved all the problems that I care. I now feel like “I heard it in the morning” (a reference to Liu Cixin’s novel where human can hear the ultimate theory of the universe). en.wikipedia.org/wiki/Heard_…
I think a cool exercises to have is to read a bunch of AI generated curl vulnerability report and find out why it’s incorrect/nonsense/etc
People have diverged opinions on using AI for flare-on, and I think positive of it. To begin with, before the event, no one knows it can be solved in 1 hour. Then for myself, I did post-moterm on it to see why it took me 6.5 hours to solve it. I improved my workflow
In the book Surreptitious Software: Obfuscation, Watermarking, and Tamperproofing for Software Protection, problem 8.13 asks you to examine a Starstreak missile for software watermarks—after consulting a lawyer and an explosives expert. pp. 516–517.

Fastest player solved it in 1 hour and 5 minutes and 43 seconds this year

Flare-on 13 starts in 1 day and you can already sign up for it: flare-on13.ctfd.io/. Apparently they forgot to add a link to it so finding the URL become the 0th challenge. Also I hope they get the time zone correct this time
Flare-on 13 starts in 1 day and you can already sign up for it: flare-on13.ctfd.io/. Apparently they forgot to add a link to it so finding the URL become the 0th challenge. Also I hope they get the time zone correct this time

I just added a scoreboard to crackmes.one! crackmes.one/scoreboard