
Posts warning about cryptocurrency related scams
Joined February 2020
- Tweets1.1K
- Following133
- Followers86
- Likes270
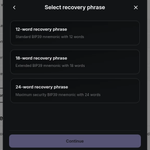




1/3 🚨 Newly registered phishing domain impersonating @binance Vault:
🌐 Domain: liveness-binance[.]com
📅 Registered: 12 October
The site serves a single-page application built to harvest credentials and siphon crypto assets. Technical breakdown 👇
@BinanceHelpDesk


2/3 🔍 Attack Flow:
• Access Gate: Demands 6-digit code or auto-bypasses targets via ?sessionTransfer=
• Seed Harvesting: Steals 12-word recovery phrases via /api/vault/restore-seed
• Spoofed Dashboard: Fakes incoming balances and sets withdrawal hold timers to trap funds.
🚨 Phishing & Web3 Alert: EIP-2612 USDT Drainer on Arbitrum One
usdtverify[.]online
Phishing lure masquerading as an official "USDT Verification" page. The campaign leverages off-chain EIP-712 Permit signatures to steal funds gas-free without an upfront on-chain approve() alert

1/7 🧵 Fake @Ledger Proposal Drops ScreenConnect via DocuSign Decoy
A Web3 phish on ledgerproporsal[.]com lures targets with a fake proposal.
Runs a real DocuSign installer as a decoy while silently installing weaponized ScreenConnect RMM backdoor. 👇
@Ledger_Support

6/7 🛡️ File Hashes (SHA-256)
• ZIP: 39438314580cd65e73c02d664df8183e218ec409021b327aff317df4c584fbec
• BAT Dropper: 1abf3f6ac62e8f1f390ecf062a9a154c10eaf3a2c8f2b962ad02e37e5a6ddab9
• ScreenConnect MSI: c0fb7911a2ca099632e39172a5dce9356d4aa960afa5b90bc8479bc31a6793e5
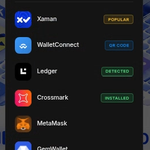
🚨 SCAM ALERT: XRPL wallet drainer targeting @XamanWallet
• Domain: ledger-allocation[.]app
• Lure: Spoofed "Xaman Airdrop / XRPL Allocation"
• Vector: Malicious Web3 modal targeting Xaman, WalletConnect, Ledger, Crossmark
Triggers malicious signing payloads to drain assets


🚨 SCAM ALERT: Campaign impersonating @Ledger_Support with a fake "2026 Exploit" advisory claiming $150M in losses.
• exploits2026-ledger[.]app
Lure: Claims older @Ledger devices have weak-entropy seeds via a fake MicroPython/Yasmarang bug to push a "risk scan."


