

Cybersecurity researcher/blogger/pentester. Try to tweet only technical/educational but occasionally post about https://teapaw.org/t.co/MTZoEINlWg 🙂
Indianapolis, IN
Joined October 2011
- Tweets3.9K
- Following871
- Followers2K
- Likes4K




Pinned Tweet
Pretty excited to share Intel for new and emerging trends in Phishing with the community!
I've already been tracking and implementing threat actors and techniques weekly, so I figured why not turn it onto a FREE Cybersecurity Awareness Newsletter! Always trying to blog new research and techniques I'm discovering, as well as incorporate novel techniques the black hats are using for training.
Sign up with just an email at phishu.net/newsletter.html
#SisforSpearPhishing #TheMoreYouKnow #CyberAware #CyberAwareness #Phishing

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

🚨 BREAKING: AI coding agent OpenCode was breached in what it calls a "large scale distillation attack".
OpenAI and Anthropic keys saved by 1.4% of its Console users have been exposed after intruders hit a legacy system.
One developer says their keys ran up $400+ overnight.


Hey All!
Lots of great new features and training opportunities built into the PhishU Framework in the last week after following emerging kits and research.
If you're not already, I HIGHLY recommend signing up for the free weekly newsletter. It's a great breakdown of threats to be aware of going into the work week. I honestly can't think of a better consolidated list of social engineering-related news you can glance at to stay abreast of these topics without having to sort the noise yourself.
Sign up with just an email and opt-out anytime at phishu.net/newsletter and please repost or like to help me get the word out! 🙌
#CyberAware #CybersecurityAwareness #Phishing #SocialEngineering #SisforSpearPhishing


PhishU Framework now supports text-based QR codes! Based on some research by researchers from Kaspersky, I decided to bake this in by default, replacing photos with ASCII QRs instead.
Now red teams and internal teams performing phishing or training don't have to rely on images being enabled by default or victims manually allowing images in email clients. Tested and confirmed working on Gmail and Outlook! Just another advanced feature PhishU Framework has that no other phishing tool has in its arsenal. And naturally, it's included in training so users know this is a thing now. 😉
Check out the new blog at phishu.net/blogs/blog-text-r…!
#SisforSpearPhishing #Phishing #QisforQRCodes

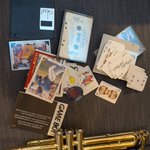
My son started band today for the first time. He chose the trumpet as his instrument, something I played. I still had mine after 30 years, but hadn't opened it since.
Most 90's accidental time capsule ever? 😂

It's so crazy to me that around 24 hours ago I posted about a new attack technique I discovered and within hours there were literally dozens of AI-generated slop articles and infographics. 🤣
Kind of hilarious, but a little scary.. since many of the LLM bots regurgitating my original blog got the main point SO wrong. They're claiming ALL you need is a 6-digit PIN in some places..
Here are just a few of my favorites (that I've seen so far) for your entertainment!
#VaultJacking #SisforSpearPhishing


𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted
New Phishing Technique - Vaultjacking: One Captured PIN, the Entire Google Password Manager Vault phishu.net/blogs/blog-vaultj…

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

New phishing meta just dropped: Vaultjacking.
One captured 6-digit Google Password Manager PIN = attacker gets your entire synced vault. All passwords. All passkeys. Banking, crypto, email, work SSO - the whole jackpot.
Google's "convenient" sync layer turns out to be one weak PIN away from total compromise. No device needed, pure Adversary-in-the-Middle magic.
Remember when we were told password managers + passkeys would save us?
Turns out they just created a juicier single point of failure.
"Trust us with your passwords" - famous last words.
Stay safe out there.
phishu.net/blogs/blog-vaultj…
Hey all! If I've been quiet (for me) it's because I've been hard at work on a NEW phishing technique I'm excited to share. I'm calling it "#Vaultjacking" and the impact is honestly a bit sobering.
In my blog I demonstrate how a single AiTM landing page can spoof your Google passkey/password manager PIN and use that to access ALL of a victim's third-party credentials (yes, including passkeys). A simple phish on one site can lead to a total compromise of all Chrome-saved credentials. 😬
As always, I'm sharing for awareness and will include in my forever-free training in the PhishU Framework.
phishu.net/blogs/blog-vaultj…
#SisforSpearPhishing #VisforVaultJacking
Hey Friends! I need your help.
It's been so long since I've posted, but if you remember me you know I've been contributing open source tools and phishing research for well over a decade now.
I've been building upon my open source phishing tool all along (PhishAPI). I can't count the thousands of hours I put into it. It's now a full-blown, centrally-hosted framework for red teams, internal orgs, and does training right. I think I've built something REALLY cool, a one-of-a kind phishing platform that's honestly better than the kits the black hats are using.
Each time a new research technique comes out, I work to apply it so pentesters and orgs can use it to perform accurate, real-world phishing tests with conditional training. Think AiTM proxies, ClickFix, OAuth attacks, Device Code phishing, etc. Users need to know what real evasion techniques look like, not allow-listed domains and canned, unrealistic scenarios.
I'm not in marketing or sales and I feel like I've been screaming into the void on LinkedIn and getting banned by mods on Reddit. 😅 The community gets really excited about new kits using some of the same techniques I've already baked in. The less technical folks think it's just another ineffective, allow-listed training tool. I'm just a geek and I think it's genuinely a great and helpful tool that I'm proud of. It's all I use for phishing engagements, as I originally built it for myself.
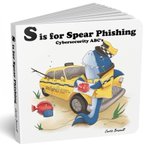
Hit me up for a demo or trial. I'll be giving away signed copies of "S is for Spear Phishing" to the first 50 people! Please retweet to help me get the word out.
Thanks for your time! ♥️
Reach out at phishu.net/contact-us.html

With Cloudflare now supporting PQC encryption, I thought it'd be a fun experiment to see if I could encapsulate Plex traffic in a tunnel since it's not supportive natively. 🤓
"Using Cloudflare’s Post-Quantum Tunnel to Protect Plex Remote Access": infosecwriteups.com/using-cl…

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

New board book from @CurtBraz is in!
“S is for Spear Phishing" cybersecurityabcs.com
#SisforSpearPhishing #CybersecurityABCs

Exciting news! 😁
The new "S is for Spear Phishing" books are in, along with a restock of a
"M is for Malware" @ cybersecurityabcs.com!
Also, after a DECADE + in the making, I'm launching my enterprise PhishU Framework spear-phishing & training tool @ PhishU.net!


Friends! I'm making something new. 😉 This time I'm promoting my company, #PhishU, by being my own sponsor! If you'd like to reserve your copy and pre-order today, please do so at cybersecurityabcs.com/USpayp…. I'm also reprinting M!
#OceanLife #SisforSpearPhishing #CybersecurityABCs


It's been a while since I've posted here...
.. but I have a little surprise that's coming very soon that some of you may be interested in... 🤞😅
#ComingSoon #SisforSpearPhishing #OceanLife #PhishU #CybersecurityABCs
