





From open-source code to Android apps—Hyunseo Shin is back with another post! 📱
“LEAD: LLM-Based Static Analysis of Session Hijacking Vulnerabilities in Android Deep Links”
🔍 Hyunseo Shin (KU, 4th year) builds on his previous AI-assisted vulnerability research with LEAD, an LLM-based APK analysis workflow that helped him uncover and manually verify 20 session hijacking vulnerabilities in Android apps.
See how it works 👇
🔗 blog.cykor.kr/2026/10/LEAD-L…
#CyKor #AI #LLM #Android #Security


We’re excited to share our new article on the CyKor blog! 📝
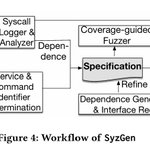
“[Paper Review] SyzGen: Automated Generation of Syscall Specification of Closed-Source macOS Drivers”
🛠️ Youngin Won (KU, 4th year) reviews how SyzGen works and shares hands-on experience setting up a Catalina VM and testing selected components.
Check it out below 👇
🔗 blog.cykor.kr/2026/10/Paper-…
#CyKor #macOS #Fuzzing


We’re excited to share our latest article on the CyKor blog! 🚀
“Adversarial Attacks 101: A fatal attack on deep learning models”
🤖 Jungwoo Park (KU, 4th year) explains how adversarial examples fool deep learning models, from FGSM and PGD to defenses and modern LLM security.
Worth a read👇
🔗 blog.cykor.kr/2026/08/Advers…
#CyKor #AISecurity #AdversarialML


We just posted a new article on our blog! 📝
"[Paper Review] FPGA Bitstream Reverse Engineering"
🧩 Jinkyung Bae (KU, 4th year) breaks down FPGA bitstream reverse engineering—from netlist recovery to hardware Trojan detection.
Read the full article below 👇
🔗blog.cykor.kr/2026/07/FPGA-B…
#CyKor #FPGA #HardwareSecurity


Korea’s #1-ranked hacker on HackerOne is back with a follow-up post! 👀
Hyunseo Shin (KU, 4th year) previously shared how he uncovered open-source 0-days using LLM agents.
Now, he breaks down the AI-based vulnerability detection workflow behind those findings.
Full post below 🔥
🔗 blog.cykor.kr/2026/06/Buildi…
#CyKor #AI #hackerone


We just posted a new article on our blog! 🚀
"How I Found Open-Source 0-days with an LLM Multi-Agent Workflow"
🔍 Hyunseo Shin (KU, 4th year) shares how an LLM-based multi-agent workflow uncovered real 0-days in open-source projects.
Worth a read👇
🔗 blog.cykor.kr/2026/02/How-I-…
#Cykor #LLM #ZeroDay


We're excited to share our first post for 2026!: "[Paper Review] Factoring an integer with three oscillators and a qubit", written by Minjae Lee, who is a member of our club and 4th year at KU!
blog.cykor.kr/2026/01/Paper-…


Attention, hackers 💥💥
CyKor CTF (@cykorctf) is just 2 days away — sign up now, we’re ready for you! 💪
Join and Play 👉 ctf.cykor.kr
This time, we’re proud to introduce HSPACE as our Infra Sponsor!
*HSPACE* is a *community of hackers* doing all kinds of exciting things.
*Our cozy space is open 24/7 and completely free to use*, so feel free to stop by anytime. you'll love it.
Address: 4F, 29 Teheran-ro 4-gil, Gangnam-gu, Seoul, 06240, Republic of Korea

Thrilled to have Zellic (@zellic_io) on board as a sponsor for CyKor CTF (@cykorctf)!
Thanks for helping us make this year’s event bigger, better, and bolder. 💪✨
Zellic is a security research firm. We hire talented hackers to break critical software, ranging from virtual machines to compilers and major web apps to proof systems. Before Zellic, we founded perfect blue, the #1 CTF team in 2020 and 2021. We offer a comprehensive benefits package and direct equity participation, as well as flexible hours, remote work, and both full-time and part-time roles.

We’re proud to have ExpOnlyNoPoc (@exp_only_no_poc ) join us as a sponsor of CyKor CTF (@cykorctf)!
We truly appreciate your partnership and support in empowering this year’s competition to reach new heights. 💪✨
We are not a company, just trying to trying to build a network of researchers especially in South Korea( or any other countries nearby! ) to perform collaborative, funny security vulnerability research without breaking your( and my ) NDAs! DMs via X(@exp_only_no_poc) if you have any vulnerability research projects to dig into together!

CyKor retweeted
CyKor CTF is now registered on CTFTime!
We invite everyone to join!
ctftime.org/event/3028

We’re excited to welcome Enki Whitehat (@ENKI_official_X ) as a sponsor of CyKor CTF (@cykorctf)!
we’re grateful for your partnership in taking this year’s competition to the next level. 🚀
ENKI Whitehat is a leading South Korean offensive security company specializing in pentesting, threat intelligence, and vulnerability research.
Renowned for their technical excellence, they hold a staggering record of 24 CTF championships and over 100 disclosed vulnerabilities.
Beyond services, they empower the industry through ‘OFFen’ (ASM/PTaaS) and their ‘CAMP’ training platform. Experience top-tier offensive security capabilities with ENKI Whitehat. 🚀
