

InfoSec \ PC Gaming \ Views are my own.
Joined September 2019
- Tweets413
- Following2.2K
- Followers1.9K
- Likes2.5K



CygnusX1 retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
CygnusX1 retweeted

Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
Thanks for the shoutout @vxunderground
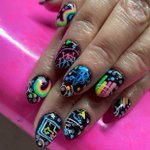
Definitely happy with my @defcon nails for this year!
Anyone who sees me at the conference is welcome to come say hello!


CygnusX1 retweeted

Cybersecurity incidents are measured in the Kitty Cat scale. It ranges 1 to 10.
A 1 is a small incident, impacting a small business or organization. This is most likely a DDoS attack or website defacement.
A 3 is slightly more severe. This is akin to detonating information stealer malware on your computer or a WordPress domain hosting or distributing malware.
Anything above a Kitty Cat 5 gets more recognition. A Kitty Cat 5 can result in widespread damage such as, economic damage, political damage, and in rare instances the loss of human life.
The VERCEL compromise is a classic Kitty Cat 6. It is a large organization with a fairly significant impact. However, impacted organizations is minimal and this was a standard smash-and-grab operation.
Is today "the time of our lives"? No, today is a Kitty Cat 6. This will mildly annoy some Digital Forensics and Incident Response people, but this could have been far worse.


CygnusX1 retweeted
Something nerds don't want to admit: they low-key enjoy the chaos
Yeah, yeah, ransomware is bad, state sponsored threat actors are bad, but deep down when shit hits the fan it is exciting.
Even though it's just a beep boop computer your adrenaline gets pumping


CygnusX1 retweeted
Yeah, so basically the reason why nerds who work on computers are so weird about universities and stuff is because of the weird cultural shift that occurred when the internet really started booming
Historically, universities were the only places people could get high quality information, labs, advanced literature, etc etc. They were higher education institutions.
When the internet exploded, more and more information was dumped online in extreme volumes. Suddenly, in just a few decades, there is more information online than in universities. Universities no longer possess the elitism or secret knowledge or information they once had.
Of course, for argument sake, some exceptions are still place, such as for healthcare. You can read all you want about surgery online, but you need to attend a university to get formal training.
Anyway, when cybersecurity first popped up, universities didn't really have any material on it. They did, but it wasn't like it was online with forums and stuff (IRC, whatever) where information was pouring out every day. The problem universities faced was how fast information traveled.
The information taught in universities is relatively old. In the age of the internet information is fast. Lightning fast. Everyday I see new malware papers being released. It would be virtually impossible for a university to keep up with this pace.
So, the other thing is universities have structure and stuff. Being an internet nerd does not require structure and stuff. Many cybersecurity nerds thrived on being an autodidact and self exploring.
When the autodidact nerds find a university nerd, there is a cultural divide whereas autodidact nerd thinks university nerd wasted their time and money and could have learned it themselves.
University nerd sees autodidact nerd as someone who (probably) doesn't have an education or feels a bit elitist because they graduated from a university. The elitism they feel circles back to the historical stuff with universities, the secret knowledge, the alumni, etc.
Ultimately, nerds can do whatever. Old heads and new head autodidact nerds will thrive and be driven by curiosity forever. Doing this requires immense self discipline and being infinitely hungry for information.
University nerds may feel the same, but may feel lost without guidance and are more reliant on structure. University nerds can do well in our field as long as get their feet wet in university stuff, then continue self education outside of the university.
Neither is wrong per say, just a different learning style and preferred method.

CygnusX1 retweeted
Oh yeah? You're a "hacker"? Prove it.
Show me your carpel tunnel syndrome and nerve damage from sitting in a chair for too long


CygnusX1 retweeted

// SYSTEM ALERT: INTRUSION DETECTED
// THREAT ACTOR: UwU Underground
// SECTOR: @DistrictCon Network
Anomalous signals detected inbound to Washington D.C.
Intelligence suggests a coordinated infiltration of the physical layer.
PAYLOAD: Unidentified Class-IV Acrylic Artifacts.
QUANTITY: Extremely Limited.
PROTOCOL: Enable notifications. Monitor this frequency.


CygnusX1 retweeted

Ride to Austin = 3 hours
Bar tab = $30
Hanging out with @hak5darren, @CygCygnus, Bambou & @GlytchTech (Glytch left before we took the pic but the 2nd pic holds a clue to why he’s so busy) 😉 #WifiPineapplePager


CygnusX1 retweeted
In the mid-2000's I played a lot of video games. Most notably Halo 2 and Halo 3. I had achieved the highest ranks possible in many playlists.
For my Halo nerds, I was a 50 in Lone Wolf, Doubles, Team Slayer, Team Sniper, and SWAT. I was a 47 in MLG.
As I became more and more competitive it was semi-common to encounter cheaters. It was primarily people abusing the P2P networking system they implemented (as the kids called it, lag switching). It eventually transformed into people doing DdoS attacks (Distributed Denial of Service Attacks) using popular tools at the time like Cain & Abel (for getting computer addresses in the game lobby) and silly botnet stuff like "XR Booter" and "Biozombie".
I became enamored with the concept of DdoS attacks. I eventually had a small little botnet (I was very dangerous, I had over 20 infected machines) and was cheating in Halo as well. However, while many of the degenerate filth I associated with at the time continued to do DdoS attacks and lame shit, I became much more interested in the internals of botnets and computer networking.
As a teenager I then took the initiative to self-teach myself introductory computer networking stuff. I mostly focused on the TCP/IP stack. I thought it was fascinating. Eventually however, I became more curious on the "booters" themselves and how they fundamentally operated.
After reading through forums and conversing with hundreds of noobs, such as myself, I eventually came to the realization I would need to learn to code to truly understand how these "booters" worked. On FreeNode someone convinced me to grab a physical copy of C Primer Plus ... so, I did.
I got the book and suffered. It was insanely boring. I fucking hated it. I hated the "exercises". I hated debugging. The if-else and while-loop conditional statements annoyed me. Data structures seemed intense. The entire concept of the stack and dynamic memory allocation seemed like alien technology.
However, I persisted because I was determined to understand what the fuck this "booter" stuff was doing.
Was I good at coding? No.
Did I learn fast? No.
Am I high-IQ 1337? No.
Eventually after struggling, kicking my feet, and being self-dragged through the mud I actually finished the book. During this time StackOverflow didn't exist. ChatGPT didn't exist. My only help was forums and schizos on IRC.
When I finished my book I decided to lock in and dive into malware. My goal (initially) was to make my own "booter". Yeah, I struggled unironically for like, 2 years, self-teaching myself networking and C to make a shit fucking DdoS botnet.
I did some web searching and found a place called "VxHeaven". On there I found tons of papers and source code for malware. I was blown away. Everyday after school I went to VxHeaven and read papers on malware. I took notes, I read papers, I tried copy-pasting source code to understand how it worked.
After more struggling I completed some small malware projects. They were never released into the wild because as I learned more I stopped caring about the applicability of malware. I instead exclusively wanted to focus on the "potential" of malware. I wanted to explore malware and ... just do weird stuff on the computer. I didn't want to hurt people. I didn't want to play video games anymore. All I wanted to do was code weird stuff and learn more. Many of my "peers" at the time thought I was lame for this.
Anyway, I was a super hardcore loser and stopped writing malware and instead switched up to just regular programming. I didn't think it was possible to do malware stuff as a career.
Around 2018, or 2019, I decided to make a website that archived malware source code, samples, and papers. I did it for myself because I wanted to emulate what VxHeaven did. I didn't expect anyone to give a fuck about me or my project. However, much to my surprise, it has exploded in popularity.
Am I a faster learner? No.
Do I have a good memory? No.
I have to re-read stuff like 300 times. I suck at stuff. My only saving grace is, despite being ridiculously dumb, I am absurdly persistent in things I am interested in. This persistence and willingness to fail over and over, yet continue trying, has some how lead me to having a relatively successful career and relatively success website and social media presence
tldr video games, tried hard, failed, I'm dumb, kept doing stuff, some how success. Mostly luck and failing a bunch


CygnusX1 retweeted
Reverse engineering tip
If you're not sure something is ransomware, run it as Admin on your computer
If your documents are no longer accessible and your wallpaper has changed, then it is probably ransomware
CygnusX1 retweeted
What an amazing day hanging out with @CygCygnus I love it when my #HackerFam visit Houston! 🥰


