

Security researcher and CTO at @scorpiones_io
Israel
Joined June 2018
- Tweets275
- Following297
- Followers384
- Likes321




El3ct71k retweeted

These fuel tanks are inside Gaza.
They contain more than 500,000 liters of fuel.
Ask Hamas if you can have some.


🛑@UNRWA warning: If we do not get fuel urgently, we will be forced to halt our operations in the📍#GazaStrip as of tomorrow night.
🆘 @UN agency says its #Gaza operation will end tomorrow 'if we don't get fuel'
@JulietteTouma @BBCNews
bbc.co.uk/news/live/world-mi…
El3ct71k retweeted

.@VP and I sat down with our teams to receive a situation update on the terrorist attack in Israel and to direct next steps.
We connected with Prime Minister Netanyahu to discuss coordination to support Israel, deter hostile actors, and protect innocent people.

ALT President Biden and Vice President Harris meet with their national security teams in the White House Situation Room to receive a situation update and give direction on next steps.
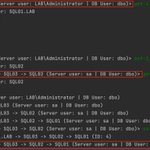
MSSQLPwner v1.3.2 is released!! the tool now can perform bruteforce against servers using tickets, hashes and passwords he can do as much impersonation as needed to lateral your movement, all the stuff i learned in #OSEP is inside. github.com/ScorpionesLabs/MS…

3
127
github.com/ScorpionesLabs/MS…
MSSQLPwner Version 1.3 is released!
What has changed?
To escalate privileges to execute commands, the tool can now do depth impersonations.
more changes will mentioned in comments
2
1
91
If our user cannot execute commands, but, he can impersonate as the "test" user, which can also not execute commands, but the "test" user can impersonate as the "manager" user, which can! This chain will be made by the tool in order to execute commands.
1
27
The interactive mode has been added!
You should check that tool if you are attacking MSSQL servers!
github.com/ScorpionesLabs/MS…
#pentest #hackingtools

4
163
github.com/ScorpionesLabs/MS…
Here's my new tool that I developed from @offsec's practices!
This tool will build you an attack chain that will allow you to gain access to authenticated MSSQL service and move laterally to other linked MSSQL servers.
El3ct71k retweeted

We are ready for writeups!!!
We will keep the CTF challenges running as much as possible!
@BSidesTLV_CTF
ctftime.org/event/2008/tasks…
#ctf #writeups
El3ct71k retweeted
Once upon a time, I had this crazy dream of creating epic mobile challenges with iPhone and Android devices. I reached out to @CorelliumHQ with my wild ideas, and guess what? Now With Amazing writers, they actually came true! Now, there's no way I can ever look back.
#CTF


El3ct71k retweeted

Yeehaw! CTF extravaganza has kicked off! We've released 10 challenges for you, and fear not, partner, because there's a whole herd of 'em on the way!
ctf23.bsidestlv.com/
El3ct71k retweeted
Countdowns on! 5 days until the annual @BSidesTLV_CTF kicks off 🚀 Big shoutout to @CorelliumHQ for backing us up this year! And yep, you guessed it... we're introducing REAL mobile challenges for the first time in CTF history! Can't wait to see you there! #CTF #BSides #Mobile
El3ct71k retweeted
Giddy up, hackers! 🤠 Saddle up for the most epic #ctf ride of the year! From June 26-28, we're galloping into action with our challenges. Get ready to wrangle some wicked code, lasso vulnerabilities, and ride off into the sunset of cybersecurity glory! Yeehaw! 🏇 #BsidesTLV2023

El3ct71k retweeted
New security research: #PassBleed: How to get @okta *master passwords* in *clear text* for *all employees* and several other important findings
Why care? Because compromise in your IdP is *game over* for your security
A meta thread - Plz RT for reach
#identitysecurity


El3ct71k retweeted

.@k3r3n3 @Reutooo_ @x_Freed0m @barnhartguy @inbarraz @realgam3 @_elad_ @DamskyIrena @omercnet @El3ct71k and Inbal Pearlson, thank you 🙏💚

