




Pinned Tweet
Twitter is full of surprises. Today I got called a 'sexist asshole' by Roseanne Barr of 80s sitcom fame. :-)
Garve Scott-Lodge retweeted

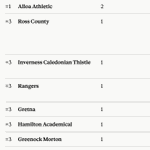
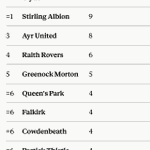
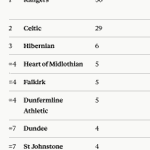
While researching for the recent piece I did on Ross County’s goal scoring feats I asked SPFL for these stats;
Most goals in a season (all competitions, all-time)
184 - Celtic (1966/67)
Most goals in a season (all competions, SPFL era)
159 - Celtic (2024/25)


Garve Scott-Lodge retweeted

ליל ההצתות ביהודה ושומרון הוא טרור יהודי לכל דבר ועניין, ויש לקרוא לו בשמו. פעילות חבלנית של קבוצות קיצוניות המציתות רכבים ובתים מערערת את היציבות האזורית, מסכנת חיי אדם ופוגעת פגיעה קשה בביטחון הלאומי של מדינת ישראל וביחסי החוץ שלה.
המציאות הזו אינה גזירת גורל. המהלכים שהובילו בן גביר וסמוטריץ' באיו״ש הביאו את השטח לסף אנרכיה שאינה מטופלת.
על ממשלת ישראל ומערכת הביטחון להפעיל את כל הכלים העומדים לרשותן, לרבות מעצרים מנהליים ופעילות ממוקדת של השב"כ, כדי לעצור את הפורעים ולנקוט נגדם סנקציות קשות.
Garve Scott-Lodge retweeted

A true Ross County legend.
Bobby Wilson played a huge part in shaping the club we are today. From back-to-back Highland League titles to helping secure our place in the Scottish Football League, his contribution will never be forgotten.
Read our tribute to Bobby and remember a man who will forever hold a special place in the history of Ross County Football Club.
🔗 buff.ly/qXNFT6Q

Garve Scott-Lodge retweeted

Here we go again. They can't win power at Holyrood so they will do everything possible to undermine it and redirect its responsibilities and powers. A bit like the Tories before them.....
holyrood.com/news/view,dougl…

Eyal Berkovic

Israeli TV host returns from suspension after racist remarks on Abdul el-Sayed haaretz.com/israel-news/isra…

I worry about these guys. What are they going to do when they're too old for this?

The hit comedy Still Game will return to the stage in 2028, the creators behind the much-loved sitcom have announced thenational.scot/news/267352…

51
Garve Scott-Lodge retweeted

I wanted to understand how someone could get 30 years for moving a box. So months ago I tried to interview Daniel Sanchez in prison. The warden denied my request, saying it would "cause serious unrest or disturb the good order of the institution.” So we began a series of calls...
Garve Scott-Lodge retweeted

Don't eat it, whatever you do, folks.

Yellow snow warning for large part of the UK
trib.al/C97y8pe


Garve Scott-Lodge retweeted

Lewis Hamilton: "I'm here with the Egyptian Red Crescent as they load these boxes containing aid they have prepared to send to Gaza. They went to the Rafah border today, accompanied by their wonderful volunteers. They have more than 70,000 volunteers across Egypt, and over 2,000 people here volunteer every day to make sure these boxes are ready and packed as well as possible. They're fully ready to be
deployed. So we really need to put pressure on Israel to
reopen the crossing from the Palestinian side, because not enough trucks are getting through each day."
"The people in Gaza and Palestine are in such urgent need that they could hardly need this aid more than they do right now, so we really must apply pressure.
And work together to ensure this aid gets there. There is a great deal of it, and this center is just one of several different sites that also contain such wonderful supplies, full of food, medicine, and things that individuals and families in Palestine really need."
Garve Scott-Lodge retweeted

Delighted to see Dylan getting a start here.


Garve Scott-Lodge retweeted

People who say Scots law allows publication of stuff covered by an English injunction need to be aware that as in most areas of law it depends.
(a) how do you know there is not an interdict sought under equivalent reciprocal arrangements up here?
(b) publication online is based
Garve Scott-Lodge retweeted
The russian ambassador unexpectedly died without falling from a window, a death the Russian government described as "suspicious"

BREAKING: Alexander Darchiev, Russia’s ambassador to the United States, has died at the age of 66, according to the Russian Foreign Ministry. abcnews.link/IXrQyiD

Garve Scott-Lodge retweeted

Darren McGarvey deserves a lot of credit for this. It would have been easy to just keep his head down and say that this isn't his problem - instead, he has stuck his neck out and done the right thing.
darrenmcgarvey.substack.com/…
Garve Scott-Lodge retweeted

An OpenSSH bug that took 46 years to ripen!
1980
UNIX puts * in the password field of system accounts. The idea is simple: it’s not a real hash, so it can’t be brute-forced and you can’t log in with a password.
2012
The musl libc developers decide that returning NULL from crypt() on failure is dangerous - programs often forget to check it and crash with a segfault. So they return an error string instead.
Guess which one?
The same asterisk: *.
Three weeks later they add a length limit: passwords longer than 256 bytes burn CPU. Anything longer is rejected. And since it’s an error, crypt() returns *.
2016
OpenSSH fixes a timing attack (CVE-2016-6210). If a user doesn’t exist, the server still hashes the password with a fake/borrowed salt so an attacker can’t tell valid usernames by response time.
2022
Alpine Linux changes the locked root password in /etc/shadow from ! to * so SSH keys work properly on cloud images.
… and the loop closes!
You connect over SSH as root (whose shadow entry is *).
You type any password longer than 256 characters (e.g. 300 As).
crypt() hits the length limit → returns * → OpenSSH compares it with the value in the database → that value is also * → you’re in as root.
That chain took 46 years (!!!) to complete.
Every individual change was reasonable. Together they produced a perfect * == * authentication bypass (CVE-2026-123158, nicknamed *sshole). Fixed in OpenSSH 10.6p2 and Alpine packages.

🚨 Critical OpenSSH flaw allows passwordless account access using any password over 256 characters
sshhole.com
A newly disclosed vulnerability dubbed *sshole has been discovered in OpenSSH installations using musl libc, potentially allowing attackers to bypass authentication and gain access to accounts that should reject password logins entirely.
The flaw affects certain configurations of Alpine Linux, OpenWrt, Buildroot, and Yocto where PAM is disabled and password authentication remains enabled. Under specific conditions, attackers can authenticate to locked accounts using arbitrary passwords between 257 and 1,024 characters.
The researcher demonstrated that affected Alpine Linux cloud images could allow attackers to gain root privileges through a passwordless administrative account.
OpenSSH 10.6p2 addresses the issue. Administrators are urged to update immediately or disable SSH password authentication until patches can be applied.

Garve Scott-Lodge retweeted

As Diwali begins, First Minister @JohnSwinney sends his warmest wishes to Hindu, Sikh and Jain communities celebrating across Scotland and around the world.
Garve Scott-Lodge retweeted

I remember when I lived in #Gaza just how devastating the rains were each November - and that was without almost an entire population sheltering in tents and under flimsy plastic sheeting!
Israel’s obstruction of all forms of shelter and aid is an atrocity!

Garve Scott-Lodge retweeted

Sometimes, like the one he did about Airdire, he writes a classic.
Thurso and classic rarely make the same sentence but this is very well worth the read.
I often wish that all match reports were written thus.
stuckonthebench.substack.com…