

Sólo un geek creando contenido. Negocios: [email protected]
Venezuela
Joined March 2010
- Tweets20.3K
- Following210
- Followers804
- Likes5.8K




Pinned Tweet
Affinity en tu Idioma es la mayor comunidad en español de #AffinityByCanva. Puedes compartir trabajos, resolver dudas y ayudar a otros. ¡Únete a nuestra comunidad de #Affinity!
►One Page: go.geeklania.com/OnePage
Estamos más activos en Facebook y Telegram #AffinityStudio

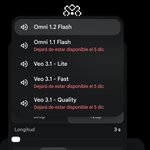
Al parecer Google está haciendo limpieza de los modelos de video en Flow. Me pregunto si es que se vienen reemplazos o es por ser suscriptor Plus

Señores de @MovistarVe deberían dar alguna opción para poder desactivar la publicidad que recibimos los clientes de parte de ustedes por SMS. De verdad que últimamente están demasiado intensos #Venezuela
Todos preocupados porque la inteligencia artificial nos va a dejar sin trabajo pero la realidad es que nos está quitando la paz mental a nivel online.
Nada es seguro y cualquier equipo que tenga una conexión a internet es un riesgo.

Microsoft Paint has a security vulnerability that could let hackers run malicious code on your PC over a network.
The flaw, tracked as CVE-2026-83844, is rated 8.1 (High) and could allow attackers to execute code over a network without permission.
Microsoft has published a security advisory and a patch for the issue.


Jose Manuel retweeted

COMISIONES BANCARIAS: ¿Qué está pasando con los BANCOS en Venezuela?
Ese es el titulo del nuevo video donde trato de arrojar un poco de luz sobre el tema
Video:
👉 youtu.be/2dwaSFb_IYI

La actualización de Affinity v3.3.3 con las novedades de noviembre para escritorio y, por fin... ¡la versión para iPadOS ya está aquí! En este video analizamos los requisitos y compatibilidad de hardware para sacarle el máximo provecho en iPad #AffinityByCanva
Enlace 👇
🤖 Made with AI

Yo creo que esto lo escribió una IA. Esas opciones no me salen por ningún lado en mi cuenta de Banesco, ni en la web ni en la app. A ver si responde y por fin nos dice dónde se desactivan los estados de cuenta para la cuenta en divisas de Banesco.

Bueno como era de esperarse ya los emuladores están empezando a convertirse en objetivo para infectar con malware.
Lo mismo aplica para todo ese poco de aplicaciones que supuestamente están luchando contra Adobe. Tengan cuidado con lo que descargan sobre todo ahora con la IA


Las empresas en Venezuela no invierten nada en seguridad y bueno aquí tenemos el resultado, toda las semanas un nuevo robo de datos

⚠️ 🇻🇪 🛜 🗄️ PREVENTIVE ALERT - ALLEGED EXPOSURE OF VNET CONTRACT AND SUBSCRIBER DATA (ACTOR: X01X00)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: X01X00 / VICTIM: VNET / DATE: OCTOBER 29, 2026]
Centralized cyber-intelligence systems have intercepted a "proof of concept" (PoC) post, released on October 29, 2026, by the threat actor x01x00, targeting the Venezuelan telecommunications company VNET. The report contains JSON-formatted snippets that appear to expose internal records, including customer contracts, email addresses, phone numbers, and details regarding connectivity plans (VNET 200, VNET 600).
It is strictly noted that the veracity of this compromise, the actual intrusion into the company’s servers, and the overall authenticity of the exposed records have not been officially confirmed. As this information appeared on clandestine platforms, the actual status of the infrastructure remains alleged and unconfirmed.
Threat Actor: x01x00
Victim / Target: VNET (vnet.com.ve) — 🇻🇪 Venezuela.
Sector: 🛜 Telecommunications, Internet Service Provider (ISP).
Date of Publication: October 29, 2026.
🔍 TECHNICAL BREAKDOWN OF THE COMPROMISED INFORMATION
Identifiers: Subscriber `contractId`.
Personally Identifiable Information (PII): Email addresses (`email`, `accountEmail`) and mobile phone numbers (`telefono`, `accountMobile`). Service Details: Subscribed plans (plan, current plan, plan ID), account status, and notifications regarding system restrictions.
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (FOR SOC / CSIRT / ADMINISTRATORS)
Perimeter Audit and Review: VNET’s technical teams must urgently review their access logs and databases to rule out any breaches or unauthorized data exfiltration.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: analyzer.vecert.io
Quickly check your security status at: monitor.vecert.io
Quotes and services: vecert.io/contact
#VNET #Venezuela #Telecommunications #ISP #DataLeak #DataBreach #BreachAlert #DatabaseLeak #PII #X01X00 #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
Por fin tenemos enlace para la nueva aplicación de Affinity para el iPad y por lo que indica la tienda estará disponible el 3 de noviembre.
Recuerda que puedes enterarte de las noticias de Affinity a través de mi canal de Telegram #AffinityByCanva t.me/AffinityConGeeklania

We were going to count how many times you asked about iPad, but we ran out of numbers somewhere around “iPAAAAAAAAAAAAAAD”. The truth? We were listening and we wanted to get it right 💚 Pre-orders for the brand new Affinity for iPad are open: affin.co/get-affinity-for-ip… 🔥
Por fin después de tanto tiempo la aplicación del banco Provincial me actualizo pero me parece un chantaje que te obligue a la activación del token para poder activar la biometría.
No quiero activar el token solo quiero la biometría para entrar fácilmente a mi cuenta #Venezuela

Le tocó el turno a Thundernet. Quedará algo sin hackear en este país? 🤔
⚠️ 🇻🇪 📡 PREVENTIVE ALERT - ALLEGED EXPOSURE OF CUSTOMER/SUBSCRIBER DATABASE AT THUNDERNET VENEZUELA (ACTOR: X01X00)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: X01X00 / DATE: OCTOBER 25, 2026]
The centralized cyber-intelligence system has intercepted a post on social media (X / Twitter), published on October 25, 2026, at 7:54 PM by the account "x01x00." In the message—directed in a defiant tone toward the official account of Thundernet, a telecommunications and fiber-optic service provider in Venezuela—the actor shares a 42-second demonstration video displaying records of subscribers and residential customers in a structured JSON format.
It is strictly noted that the veracity of this compromise, the actual intrusion into the company’s databases, and the overall authenticity of the total volume of records have not been officially confirmed by Thundernet’s management or by Venezuela’s telecommunications regulatory authorities (CONATEL / CSIRT-VEN). As this involves social media posts by threat actors, the definitive status of the infrastructure remains unconfirmed.
Victim / Target: Thundernet Venezuela
Sector: 📡 Telecommunications, Internet Service Providers (ISP), Fiber-to-the-Home (FTTH), and Digital Telephony.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / TELECOMMUNICATIONS SECTOR)
Audit of CRM and Billing Systems: Thundernet’s security and IT support team must immediately audit their customer relationship management (CRM/ERP) systems, self-service portals, and SQL databases to determine whether the data dump originated from a malicious query or an exposed API key.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: analyzer.vecert.io
Quickly verify your security at: monitor.vecert.io
Inquiries and services: vecert.io/contact
#Venezuela #Thundernet #ThundernetVzla #Telecommunications #ISP #FiberOptic #FTTH #Caracas #Barquisimeto #Valencia #Maracaibo #DataLeak #DataBreach #BreachAlert #DatabaseLeak #JSONDump #PII #Cedula #x01x00 #Cybersecurity #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk #CybersecurityVenezuela

Jose Manuel retweeted
Tenemos un clip de como se realiza la compra y venta de USDT en Bolívares directamente en Binance desde la aplicación, el video de youtube explicaba desde la pagina y este clip es desde la app
El clip estará en el Grupo de Telegram
t.me/aguilafintechchat

Que increíble que seguimos necesitando VPN para instalar o actualizar Java #Venezuela

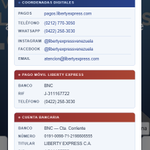
Lo de liberty Express está muy raro. Cuando entras a la web que lleva toda la vida usándose y seleccionas venezuela lo primero que hace la pagina esa darte un aviso con los pagos, dejando claro que no tienen cuenta en esta red social.


Pues nada, el drama PHP continua. El nuevo parche sigue siendo vulnerable 💀

🚨 UPDATE: PHP 8.5.12 may still be vulnerable to php2shell!
Researchers are reporting a successful double-free trigger on the newly patched release.
⚠️ The official fixes may be incomplete. A crash alone doesn't confirm RCE, but this deserves urgent investigation.
Don't assume you're safe just because you've patched.
#php4shell #php #cybersecurity
teapaw.org/_annieversary/status/2…
Jose Manuel retweeted

The PHP project has released fixes for 2 critical vulnerabilities affecting servers that host PHP applications. Site owners and technical teams should confirm their hosting provider’s update plan and update PHP immediately. Versions before PHP 8.2 no longer receive security updates. These issues are not specific to WordPress, and no WordPress update is required. wp.me/pZhYe-5Gb


El problema del PHP está poniendo a todos a correr
