
innovative crypto enjoyer
Latvia
Joined July 2023
- Tweets312
- Following17
- Followers13
- Likes687




Golden retweeted

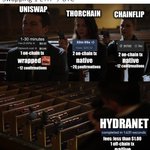
Hydranet – Monthly Recap #50
Hydranet has been live on mainnet since September 7, and for the first time, users can trade BTC for ETH peer-to-peer across Bitcoin Lightning and Lithium!
We've already shipped several fixes and improvements, including token permits to make swaps more accessible to wallets holding only tokens but no ETH for gas, stronger safeguards around channel payments, and more accurate fee estimates.
Stay tuned to our official channels for a chance to get an invite code. Invite codes are never sold, and we will never DM you first.

Golden retweeted
Irony of the week. This is really so funny.
Until last Sunday Starknet was the "dead chain" meme. Down 97 to 98% from the 2024 highs, revenue in free fall, thin TVL, a 127 million STRK unlock every single month, the airdrop drama, the outages. One exchange delisted spot and perps on October 5.
Then October 8. The quantum topic explodes, Eli Ben-Sasson floats the idea of leaving Ethereum to become an L1, "the first fully quantum-resistant network, 2027 target". $STRK goes from under $0.06 to above $0.11 in days and leads the whole market for a while.
Now read it again. "Actively considering". Not a decision, not a date, not a line of code shipped. TVL, revenue and supply are exactly what they were last Sunday.
On October 15 another 127 million STRK unlock to investors and early contributors. Five more of those follow, one every month until March 2027.


Golden retweeted

The bunker was built in 2018. Hash-based from genesis, just like the doctor ordered.
Meet the quantum-safe vault.

Golden retweeted

If you own crypto, this is genuinely scary.
A top bitcoin researcher, who actively works at the Ethereum foundation, is telling us to move our crypto to a bunker.
He thinks there is now a reasonable possibility that superhuman AI discovers a way to break the cryptography securing Bitcoin and Ethereum before quantum computers do.
That sounds insane, but there’s some important context.
Bitcoin and Ethereum rely heavily on ECDSA. At a very basic level, your wallet has a private key, and mathematics allows you to derive a public key from it.
Going forward is easy.
Going backward and figuring out the private key from the public information is considered effectively impossible.
A huge amount of crypto security rests on that assumption.
Drake is worried that AI could discover some completely new mathematical shortcut that changes it.
Why is he worried about this now?
AI has made some pretty ridiculous advances in mathematics this year.
Earlier this year, an OpenAI model autonomously disproved a famous Erdős conjecture dating back around 80 years, using mathematical techniques researchers hadn’t expected.
Then, literally the day before Drake made this post, OpenAI released hundreds of AI-generated mathematical results across hundreds of problem families.
One of those results broke through a longstanding assumption involving the complexity of integer multiplication.
That does NOT mean AI broke ECDSA.
It didn’t.
The signal is that AI is increasingly demonstrating an ability to find novel approaches to mathematical problems humans have studied for decades.
At the same time, researchers have been making progress on the other threat: quantum computers.
Estimates for the resources required to attack elliptic-curve cryptography have fallen significantly, and researchers, including Drake himself, have been working on making those attacks more efficient.
So his concern is basically:
What if everyone is preparing for quantum computers to eventually break ECDSA, but superhuman AI discovers a mathematical shortcut first?
That’s the part he thinks the crypto industry isn't sufficiently prepared for.
If ECDSA were efficiently broken, the consequences could obviously be catastrophic. Depending on the attack and what information an address has exposed, an attacker could potentially recover private keys and steal funds.
Drake isn't saying this has happened.
He isn't even saying it's definitely going to happen.
He's saying that recent AI progress has moved the probability from something he could comfortably ignore to something worth preparing for.
His recommendation is surprisingly simple.
If you're a major holder, exchange, custodian, ETF, treasury, etc., consider moving assets from heavily used addresses into fresh addresses that have never signed a transaction.
Then don't use those addresses.
That limits the cryptographic information you've exposed and potentially buys you additional protection if a vulnerability is suddenly discovered.
For the really large players, he thinks the industry should begin preparing to move beyond ECDSA entirely and toward post-quantum / hash-based cryptography.
The downside is enormous, the precautions are relatively cheap, and AI progress is moving fast enough that waiting until an attack exists may be too late.
He thinks it's now reasonable to consider the possibility that ECDSA could break before AGI/Q-Day, potentially on a timeline of months rather than years.
Nothing publicly known can currently do this.
But his argument is essentially:
For decades we've protected trillions of dollars with mathematical problems because humans couldn't figure out how to solve them efficiently.
We're now building machines that may become much better at mathematics than humans.
Maybe it's time to stop assuming those two facts can coexist forever.


Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
Golden retweeted

I’ve accumulated close to 0.5% of the entire $QRL supply, currently trading at around a $120M fdv
They’ve spent the last 8 years building around the exact class of risk Justin is warning about
I think this is one of the more interesting asymmetric bets and is worth a gamble for the long term from this level
If there’s even a small chance that AI driven mathematical breakthroughs could compromise cryptographic assumptions we’ve relied on for decades, imagine what happens the moment a credible breakthrough puts ECDSA security into question
$QRL is my pick. Funny enough similar alternatives like $CKB, $ALGO, $QANX and $MCM have barely reacted from this latest wave of breakthroughs
QRL seems to be the one actually benefiting
Do not bid this if you’re not looking to hodl
This is a conviction gamble


Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
Almost 2 weeks live and the volume is exponentially increasing. best dex/network in crypto right now.
Instant, private, trustless, native cross-chain offchain/onchain swaps, with zero gas fees. Go get an invite code from @HydranetX to start using this crazy DEX

Golden retweeted

MAINNET IS UPON US.
The First Wave is now live.
Non-custodial. Cross-chain. Yours.
app.hydranet.ai/
Golden retweeted
It has been a long time in the works but we're finally happy to share more with you guys soon.
Stay tuned!

Golden retweeted
Eight years ago, QRL mainnet launched with a conviction that felt early at the time: quantum resistance belongs at the foundation, not on the roadmap someday.
Since then, QRL has kept doing what secure infrastructure should do: operate, endure, and prove itself over time. Now, as post-quantum standards mature and quantum timelines compress, the industry is catching up to a risk QRL was built around from genesis.
QRL's anniversary is both a milestone and a signal of where quantum-safe infrastructure is headed next.
Read more: theqrl.org/blog/celebrating-…

Golden retweeted
Independent review of post-quantum cryptographic library from security partner, @halbornsecurity, finds no vulnerabilities; all 13 findings rated Informational
theqrl.org/press/halborn-aud…

Golden retweeted

#Ethereum PQ Migration strategy, let’s break it down and get real.
“Quantum computing will eventually break the public-key cryptography that secures ownership, authentication, and consensus across all digital systems.”
Officially, it is no longer if, but when. Important narrative change. Definitive. Absolute.
“Enabling users to transition to quantum-safe authentication through account abstraction, without a disruptive ‘flag day.’”
This references migration only, not disabling legacy ECDSA signed transactions.
The important part has still not been solved. The official page pq.ethereum.org/ explicitly states that the fate of unmigrated funds “is ultimately a community governance question. Two natural scenarios exist: do nothing, or freeze vulnerable coins.” To me, this language points toward forks. If you hold ETH today, a “do nothing” outcome leaves vulnerable coins stealable, while a freeze (or lockup in a smart contract for years) means you could effectively lose access to those funds. Either path creates winners and losers.
Assuming everything runs as designed, the implication, though never stated outright, is that some legitimate accounts will lose funds. Governance decisions, and in my view inevitable forks, will ultimately dictate who keeps what. Is this acceptable? Maybe, maybe not. It is a philosophical question, and not everyone will agree. Hence forks. I see no other realistic outcome.
Ethereum’s own consensus puts the at-risk portion at roughly 0.1 percent to 5 percent of supply. But here is what is not said.
This narrow risk estimate assumes that all upgrades will be completed before cryptographically relevant quantum computers (CRQCs) become available, development of which is occurring under extremely high levels of nation-state classification, with public timelines highly uncertain.
“What is at risk” also does not factor in the very real conditions under which accounts might not migrate: dormant or long-inactive accounts, lost or irrecoverable private keys, unaware or uninformed users, technical or UX friction in migration, economic disincentives or negligible value from dust holdings, institutional or custodial or contractual barriers, immutable or non-upgradeable smart contracts, multi-party coordination failures, timing and governance delays, distrust of new PQ schemes, and legal or estate complications.
Justin Drake (Ethereum Foundation researcher) has explicitly framed this view in the recent Bankless podcast, estimating that “at max two, three, four, five percent maybe” of Ethereum supply consists of funds that are “both lost and in quantum crackable addresses,” with his concrete prediction being around 2 percent, roughly an order of magnitude less than Bitcoin’s comparable exposure. He argues this small percentage carries “qualitative consequences,” leading him to “strongly advocate for not doing anything and really honoring property rights because at the end of the day, whatever, 2 percent is not a big deal.”
Independent verification has not been performed and even so, well, it's probably not a big deal.... at least to 95% of the Ethereum community, minus the unrepresented account holders listed above. They might not be to happy about it.
So the real question is still unanswered, how much is REALLY at risk?
No one knows.
Sources -
(Bankless podcast, March 2026)
Citations / Sources:
• Official Post-Quantum Ethereum page: pq.ethereum.org/
• Justin Drake on Bankless podcast (March 2026): bankless.com/podcast/ethereu… and full transcript at podscripts.co/podcasts/bankl…
pq.ethereum.org/

Golden retweeted
We have selected @trailofbits as an audit partner for QRL 2.0.
Trail of Bits, renowned cybersecurity firm that played a pivotal role in auditing Ethereum’s major upgrades, will bring that expertise to the world’s first post-quantum, EVM-friendly Layer-1.
More details to come.


Golden retweeted
Most people think Bitcoin can just upgrade to post quantum cryptography when the time comes.
It can’t.
And it has nothing to do with the reasons you think it does.
Thread 👇


Golden retweeted
@nic_carter, take a look at $QRL. I'll summarize to get you started - the first L1 blockchain in the world to use NIST DSAs to be resistant against a CRQC, since the first block in 2018. We saw this coming a while ago, so built our own chain, NOT ERC20. Full Disclosure - I work on the @qrledger team.