

grassy.eth Discord Security Consultant/Auditor. Cool Cats Discord Security Cold Admins, No Kings.
Various Metaverses
Joined September 2021
- Tweets850
- Following732
- Followers1.2K
- Likes1K






Pinned Tweet
🚨 🚨 important opsec alert! 🚨 🚨
Unless you have a long term support arrangement from ANY discord creator or auditor, you NEED to remove their permissions after an audit/server setup.
And even if you intend to work together longer, you need to make sure that ONLY cold accounts have dangerous permissions!

While I am sure there are many talented people out there, there are very real risks in the space, and you need someone on your side who understands both what they are, and how to defend against them!
And on that note, who are your favorite discord builders, even if they don’t have a background in security? I always love to meet other talented individuals in the space, because we all have so much we can help teach one another, and when we share our knowledge, it benefits the space as a whole!
This is not the first time something like this was happened. Mee6 as well as several other major bots have had severe attacks in the past.
No bot is perfect, so you have to secure your servers accordingly.

This one is a new enough approach that it’s a good idea to read up on it! While job offer based attacks are nothing new, an explicit focus on devs via GitHub is new!
⚠️ DISCORD SECURITY PSA ⚠️
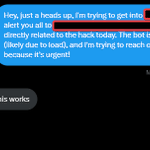
A new token grabbing technique is going around, revolving around GitHub & soliciting dev help. The attacker will direct you to a GH repo with malicious code, which WILL STEAL ALL CREDS from your browser cache.
Verify/block DMs:
blog.pnly.io/our-tools-for-m…


A critical look at token gating on Discord:
Why Vulcan's secure approach is gaining traction over CollabLand, especially concerning ad vulnerabilities.
🧵 Ephemeral Message Vulnerability 👇

Enhanced Security Measures:
Vulcan steps up with enhanced security measures, providing robust protection against unauthorized access and ensuring that community safety is never compromised by ad-related vulnerabilities.
🧵 Potential Path Forward 👇

Glad to help!

Update: We have locked down the Discord server and are currently collaborating with @GrassyEth to ensure that all immediate threats are closed before proceeding with a full security audit.


grassy.eth retweeted

🛠️ Doing a Discord audit is hard. 🛠️
Discord servers can quickly turn into giant unmanageable jumbles and even the best Discord auditors have horror stories of certain servers just being too much.
The only way to know if your Discord audit was not good, is when it fails and a server gets compromised.
That is obviously not a great outcome. In terms of a feedback loop as well, someone can avoid having their servers compromised purely out of luck, and feel like they give the best audits in the world, until they start falling like dominos.
That is why we made a better feedback loop at @Server_Forge.
For free, every member of ServerForge can submit an audit and have like 7 expert auditors all review it.
Want to know what happens when most SF members submit? They trigger an instant fail option. But this is good, we identify a major issue with their setup and tell them WHY.
This improves their auditing game immensely and they can resubmit. Once they pass they get to join the ranks of the ServerForge Approved Auditors.
This is a free service, that anyone can participate in, and we actively try and prod people in the space providing Discord audits towards doing this.
Seriously, would you prefer a Discord auditor with a feedback loop of instant feedback and corrections, or one where they learn over months or years by having their client's servers fail.

grassy.eth retweeted
Why can't a bot just make my Discord server secure?
I think this is a route a lot of folks go down when thinking about Discord security.
They look for an easy out. But sadly I don't think this route can ever exist. Bots can make an auditor's life easier, but should never fully replace them.
Here's why...
1. Most compromises start from phishing.
When looking at a human-centric problem, it is going to
require education of the humans involved to help solve it.
If all these compromises were solely because of permissions issues then a bot might have been able to solve it. But it goes deeper than that.
2. Each server is wildly different.
While every server has some commonalities, each server is very different.
There are too many uncontrolled variables among the variance in channels, roles, and even other bots. Trying to fix every server with a fixed solution bot is going to break almost every server it touches.
Fixing and securing servers takes a lot of critical thinking that bots aren't going to be able to provide.
3. Changes in a live environment.
While you go through and make changes in a server, other bots or rarely other users might modify things as you go. At best this creates inconvenience, but if you were following a fixed order of operations like a bot would, it could miss channels or permissions or potentially leave a backdoor in the server.
4. Server Owner issues.
A verified bot cannot take over server ownership of a server. This means there will always remain a human element weak link. Unless a team is taught and reminded constantly to switch to a cold server owner, the server will remain under threat.
5. False confidence.
Discord does push some changes occasionally that could create potential unseen issues with the fixed solution the bot implements. With a human behind the wheel, any weird behaviors, hiccups, or anything of that sort could be caught. But with a bot it might slide through unnoticed.
---
Essentially it all boils down to the fact that there are way too many variables that vary between each server, that appear with developing attacks, or even on the platform as a whole itself. I don't think an all in one solution makes sense, but I do think that bot-assisted audits are a must.
I have a tool that I use to export all permissions from roles and channels in the server, using this and some very handy spreadsheets I can get a review of the entire server's permissions and any major issues.
I don't use this tool as the primary way of fixing server permissions. It is just a check (my third check) to make sure I didn't miss anything.
Using bots as tools is extremely important, but having a bot-first, or bot-only method is going to skip important steps and cause issues.
I think this is a slightly controversial take, but what do you guys think?
grassy.eth retweeted
In my Twitter bio, I mention something called a "Discord Server Audit." Here's a brief explanation of what that entails.
The goal is to make a server safe.
A big part of that is looking for weaknesses that an attacker will use in combination with phishing to
attack the server. Knowing exactly what attackers do once they compromise a staff member comes from two years of experience of analyzing live compromises that occurred.
Some attacks are pretty straightforward, but there are plenty that used misconfigurations to escalate their permissions. An audit first and foremost is looking to identify those issues and rectify them.
This process requires checking every role, every individual channel, and every existing bot. It is meticulous, it can't be fully automated, and it takes time.
Next, looking at the issue of phishing and staff compromises, you have to start from an assumption that every single team member will get compromised. With that assumption, setting up the server to be safe even if a team member gets phished is vital. Using cold admins, 2FA announcement bots, and other protections to police staff is required here.
One way the audit protects against phishing is also education. My audits have two major educational components, a quiz bot and a seminar to educate the entire team on how their Discord account will be targeted. Even if the server will be safe if someone gets phished, stopping phishing at the source (the user) is ideal.
Another big part of the audit is protecting users. Even without a compromised staff account, scammers can do a lot of damage in a community. Making sure all user roles have no additional permissions is an easy place to start, but adding in anti-nuke, automod, anti-link, anti-impersonation bots to police the community and make sure spammers don't try to scam the community is vital.
There are so many different aspects of a Discord server to review and check, additional things like community settings, invite links, automod settings, and even boost status need to be looked over and fixed if necessary.
Hopefully that help explains a bit about what a Discord audit is, why it requires actual experience, and why it takes so much time and effort to complete.
Feel free to ask any questions in the comments!

grassy.eth retweeted
What you should do if you think someone you're talking to online is acting off:
Step 1: Try to communicate on a different platform, if they send you a Discord message, ask them to respond on Twitter DM. Or maybe to text you or send an email.
Step 2: Take it slow. Someone asking you for a loan, and saying they absolutely need it now, should raise red flags. Ifs something feels off, it usually is. If you feel uncomfortable, tell them you can continue discussing tomorrow.
Step 3: They'll have access to all of your previous messages if it is a compromised account, so ask for confirmation by asking about something you both did IRL. i.e. "What was the name of the bar we went to after losing at poker?"
Step 4: You can ask to do a voice call, but voice modulating is not a hard thing to do these days, so take it with a grain of salt. Video call can be better. Be especially suspicious if they claim they're using a new mic.
Step 5: Overall, be suspicious of everything, always double check, and trust your gut. You have no obligation to be nice, if your gut feels like something is off, don't send them money.
One of the largest problems I faced earlier on in my discord security career was being unable to get a team member to remove dangerous permissions from my accounts unless I was a permanent member of the project, and could thus remove it from hot accounts myself, and this is an issue of exactly how dangerous it is to leave dangerous permissions on staff accounts.
While I am sure there are many talented people out there, there are very real risks in the space, and you need someone on your side who understands both what they are, and how to defend against them!
And on that note, who are your favorite discord builders, even if they don’t have a background in security? I always love to meet other talented individuals in the space, because we all have so much we can help teach one another, and when we share our knowledge, it benefits the space as a whole!


grassy.eth retweeted
🚨🚨 Discord Security Alert 🚨🚨
There is a new phishing scheme going around MASS TARGETING DeFi and NFT projects.
This one, unfortunately, is impersonating security researchers, smart contract/Discord auditors.
It uses fear, intimidation, and bookmarks to snag discord tokens.

Keeping a ‘hot’ account that publicly handles communications and only has basic permissions and access while maintaining a ‘cold’ account that works behind the scenes to update settings, channels, and permissions and has higher-level clearance segregates the duties of your staff.