
I document #ThreatHunting playbooks in the form of #jupyter notebooks and share them with the world! https://xitter.cf/t.co/djKSwSGXgA @Cyb3rWard0g
Joined December 2018
- Tweets86
- Following7
- Followers6.2K
- Likes112


ThreatHunter-Playbook retweeted

Thank you for sharing @DrAzureAD 😎!
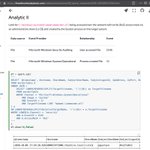
A process that is NOT Lsass attempting to access ("CloudDomainJoin" OR "WorkplaceJoin") AND "Ngc\KeyTransportKey" before exporting the Device certificate and transport key is interesting 😉
✅ SACL
✅ Detection Idea: github.com/Azure/Azure-Senti…


New #AADInternals version and related blog post (with multicolor arrows) out now!
"Stealing and faking Azure AD device identities":
o365blog.com/post/deviceiden…
Credits to @gentilkiwi/#Mimikatz!
#infosec #redteam #blueteam


ThreatHunter-Playbook retweeted

⏳ Good morning! #InfosecJupyterthon Day 2 is here!
⏰Starting at 8:30 AM (PST)
😎 Discord Q&A: discord.com/invite/tFsRKR72
🚀 Agenda: infosecjupyterthon.com/2021/…
📺YouTube Live Stream 🔴: aka.ms/Jupyterthon2021Live2
See you soon!

ThreatHunter-Playbook retweeted

Looking forward to speak on #ThreatHunting at scale with Spark notebooks at 4:15 PM PST. #infosecjupyterthon
👀Tune it to Youtube Livestream : youtube.com/watch?v=nMnHBnYf…

ThreatHunter-Playbook retweeted
🚨 #InfosecJupyterthon going live 🔴 in 24hrs 😎
Dec 2nd and 3rd at 8:30 AM (PST) 🗓️
The agenda for this year is 🔥🔥 aka.ms/Jupyterthon2021Agenda
Live Streams 📺(FREE virtual event)
Day 1: aka.ms/Jupyterthon2021Live1
Day 2: aka.ms/Jupyterthon2021Live2
@OTR_Community #MSTIC #Jupyter 🙏
ThreatHunter-Playbook retweeted
🚨 Learning how to install #Sysmon for Linux 🐧 & send security events to #AzureSentinel in a research lab environment!! 🧪 #MSTIC #Microsoft
📡 Sysmon (SysinternalsEBPF) -> Syslog -> SIEM 🚀
✅ Scripts
✅ ARM templates
✅ Sysmon configs and more..
techcommunity.microsoft.com/…
ThreatHunter-Playbook retweeted
🚨 A few detection opportunities while interacting with local AD hybrid health agent registry keys & Azure AD connect health AD FS services ☁️
📡SACLs & 🛰️Activity Logs (Directory Activity) FTW
🛡️ #AzureSentinel : github.com/search?q=repo%3AA…
🌎 @sigma_hq : github.com/SigmaHQ/sigma/pul…
Did you know that local admin can export AD FS Hybrid Health Agent secret and create fake Azure AD sign-in events? 😈
Read my blog "Spoofing Azure AD sign-ins logs by imitating AD FS Hybrid Health Agent" to learn more & how to do it with #AADInternals 🔥
o365blog.com/post/hybridheal…

ThreatHunter-Playbook retweeted

Today, Microsoft is open sourcing Cloud Katana, a cloud-native serverless application built on the top of Azure Functions to assess security controls in the cloud and hybrid cloud environments. Read about the design principles and learn how to deploy: msft.it/6011n46MT

ThreatHunter-Playbook retweeted
🚨 New version of the Windows Security Events connector from #AzureSentinel reached public preview
Looking for a way to test & filter the collection of event logs via XPath queries? I got you! 💜🍻 @MSThreatProtect #MSTIC @OTR_Community @OSSEM_Project
techcommunity.microsoft.com/…
ThreatHunter-Playbook retweeted
It's time to go to SimuLand! 🎠🎡🎢
But it isn't a new vacation theme park hot spot, it's a new open-source initiative that will help you deploy a lab environment to reproduce real attack scenarios to test your security defenses.
Get the details: msft.it/6017VxcHv

ThreatHunter-Playbook retweeted

Sharing @Mordor_Project datasets for "Getting AD FS Database Config Remotely" (Security, Sysmon & PCAP) @Cyb3rWard0g 🍻🙏
mordordatasets.com/notebooks…
1⃣ A few tool-based comments at the host level
2⃣ Group hosts & processes connecting to AD FS server over port 80 (Usually 443)


New version of #AADInternals out now, including remote dumping of #ADFS configuration database🔥
Read the blog at: o365blog.com/post/adfs/
Credits to @vesat, @doughsec, @BakedSec, @_dirkjan, @gentilkiwi, @MGrafnetter, and @Cyb3rWard0g for your help and previous work!

ThreatHunter-Playbook retweeted

This morning Starship SN15’s nosecone is heading into the high bay. It appears that SpaceX is not wasting any time in preparing SN15 to roll to the launch site ASAP.🔥🚀🔥
@NASASpaceflight

ThreatHunter-Playbook retweeted

CVE-2021-27065 - @sigma_hq rule to detect adversaries modifying the offline address book (OAB) virtual directory in Exchange and setting the ExternalUrl property to script. #ProxyLogon chain event
PR: github.com/SigmaHQ/sigma/pul…


ThreatHunter-Playbook retweeted
Now that #ProxyLogon POCs are public, help defenders learn the underlying behavior? The weekend isn't over yet! @Cyb3rWard0g
1⃣ Azure Sentinel Env: github.com/OTRF/Azure-Sentin…
2⃣ Install 🐍, ⬇️ &💥 POC
4⃣ Share @Mordor_Project datasets, @sigma_hq rules, @ProjectJupyter notebooks


ThreatHunter-Playbook retweeted
Looking for anything to do this weekend? 😉
🔥 A way to create and start services remotely using the amazing NtObjectManager from @tiraniddo leveraging the latest support for named pipes RPC clients 🔥
Help us to create more PS scripts @OTR_Community
blog.openthreatresearch.com/…

ThreatHunter-Playbook retweeted
💥😱 @tiraniddo added "named pipe RPC client transport" to NtObjectManager 🔥 Thank you very much James for all your work 👏!
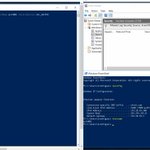
I'll create PS scripts to cover a few scenarios 🍻 (Img 4)
If anyone would like to help me, let me know 😉 @OTR_Community
github.com/Cyb3rWard0g/WinRp…


Very happy to see the @OSSEM_Project leading the way to help standardize how we add metadata about the security events and relationships used in the detection rules / analytics we share with the community!! Thank you @Cyb3rPandaH ! I like the "How can you contribute?" section! 🍻


Formalizing the mapping of security events to the @MITREattack data source objects concepts 🍻 We would love to hear your feedback and see your contributions to this community-led effort!! 💜 Thank you @Cyb3rPandaH 💜
Blog: medium.com/threat-hunters-fo…

ThreatHunter-Playbook retweeted

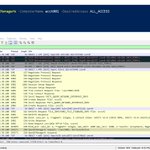
If you are wondering what this might look like in Sysmon, we got you covered with a new small dataset. You can simply download it from the link below and explore it with PSH as shown in the second image below 😊 Thank you @jxy__s !
😈 mordordatasets.com/notebooks…


I’m pleased to present this Windows exploit. Process Herpaderping is a method for evading detection - similar to process migration, hollowing, or doppelganging.
herpaderping.com/
ThreatHunter-Playbook retweeted
HOW to contribute a @Mordor_Project dataset in 2 mins ⏳w/ the help of @redcanary ART & then contribute to @sigma_hq after exploring the data! @OTR_Community
♻️ Clear, Exec & Collect: youtu.be/6iteEfbuwU8
😈 Data: mordordatasets.com/notebooks…
🏹 Rule: github.com/OTRF/sigma/blob/m…
ThreatHunter-Playbook retweeted

Check out mordordatasets.com/notebooks… and threathunterplaybook.com/not… - Mordor Dataset and Playbook entry for wuauclt.exe abuse with many thanks to @Cyb3rWard0g 🤜 for his epic work as ever! Will be updating blog with these links too for reference 💪

I found an interesting #LOLBIN using Windows Update Client (wuauclt.exe) as a loader - blog, pull request to LOLBAS and in the wild sample here dtm.uk/wuauclt/ - I am hoping to finalise some of my work on the methodology I used soon @MDSecLabs so keep your eyes posted.

ThreatHunter-Playbook retweeted
Starting your week 🏡 & looking for ways to automate the deployment of #AzureSentinel w/ a basic Windows environment in your lab?
1) Go to GitHub (OTRF/Azure-Sentinel2Go)
2) Click on Win10 scenario 🏗️ -> ☁️
3) Wait a few mins ⏲️
4) Play 🚀
5) Repeat ♻️
techcommunity.microsoft.com/…
