
Intercept, edit & replay the non-HTTP traffic Burp & Fiddler can't see - TCP, TLS, DTLS, QUIC. Native GUI for Win/macOS/Linux. 7-day free trial ↓
India
Joined August 2025
- Tweets79
- Following22
- Followers11
- Likes363


Pinned Tweet
Your app talks to a database, a message broker and a few APIs.
How many of those conversations can you actually see?
InterceptSuite shows the real traffic: the SQL your ORM sends, the MQTT your device publishes, the DNS lookups, the QUIC. Edit it, replay it.
This macOS app logs in over DTLS. No HTTP, no proxy settings to change.
Add one redirect rule for the app's bundle ID and its packets land in InterceptSuite decrypted, where you can edit, forward or drop them.
3 minutes, from first launch to intercepted login.
Thick client pentest gotcha: if the app uses DNS over HTTPS/TLS, domain-based redirect rules won't match. Use IP rules instead. Encrypted Client Hello (ECH) also can't be intercepted, so turn it off in the browser.
1
84
Plaintext first, TLS later: SMTP, POP3, PostgreSQL, MySQL. Most proxies miss the upgrade. InterceptSuite detects the STARTTLS/TLS upgrade and keeps intercepting after it.
1
33
Replay in InterceptSuite is a repeater for raw TCP, UDP, TLS, DTLS and QUIC. Capture a message, edit the bytes, resend, compare responses. Like Burp Repeater, but for non-HTTP.
interceptsuite.com/replay/

1
70
InterceptSuite retweeted

Debugging an MQTT device over TLS. Decrypted topic and payload, all in one history.
Why thick clients skip your proxy:
• no proxy setting
• ignore the system proxy
• use their own DNS
• Windows system proxy is HTTP only, no SOCKS5
Fix: redirect at the network level instead of asking the app.
Testing an IoT device? Once you're inside its MQTT-over-TLS traffic (port 8883), check:
• CONNECT packet: are credentials shared across devices?
• Topic names: device IDs, sometimes customer IDs
• Retained messages: last state, sent to anyone who subscribes
• Does the broker allow a # wildcard subscribe?
1
35
InterceptSuite retweeted
18 months ago InterceptSuite was Windows only and could just about a TCP packet.
Now its on Mac & Linux intercepting QUIC/DTLS with replay + Python extensions.
First version vs Latest version


Most proxies stop at TCP. InterceptSuite redirect handles UDP too, so DTLS and QUIC traffic from an app can be sent through the proxy, decrypted and edited like any other connection.
1
54
InterceptSuite redirect rules can match on:
• application name or *
• IP, CIDR, domain
• port, range, list
• TCP, UDP or both
Action per rule: Proxy, Direct or Block. First match wins. Apps that match nothing are untouched.
InterceptSuite retweeted
Your app talks to a database, a message broker and a few APIs.
How many of those conversations can you actually see?
InterceptSuite shows the real traffic: the SQL your ORM sends, the MQTT your device publishes, the DNS lookups, the QUIC. Edit it, replay it.
What is your app really sending?
InterceptSuite allows you to intercept, Inspect and edit network traffic in real time, not just real time traffic, you can also send network request directly from the application in the same as postman but for network pacekt not just HTTP.
1
61
InterceptSuite 2.1.0 is out. Traffic redirect is now built in on Windows (Proxy > Redirect), so thick clients with no proxy setting go through the proxy without a separate app. Also adds one-click CA install on Windows, macOS, Linux.
interceptsuite.com/blog/inte…
1
30
InterceptSuite retweeted
🚀 InterceptSuite Pro 2.0.0 is out.
The biggest InterceptSuite release since 1.3.0.
Now with:
• TCP/TLS/STARTTLS/UDP/DTLS/QUIC Replay
• Interception Rules + Scope
• TLS pass-through
• HTTP/3 QUIC interception
• Wireshark-style Proxy History filters
• Editable hex data
• MCP/AI access for Claude Code & Claude Desktop
• Major Linux/macOS fixes
Download:
interceptsuite.com/download/
#Cybersecurity #NetworkSecurity
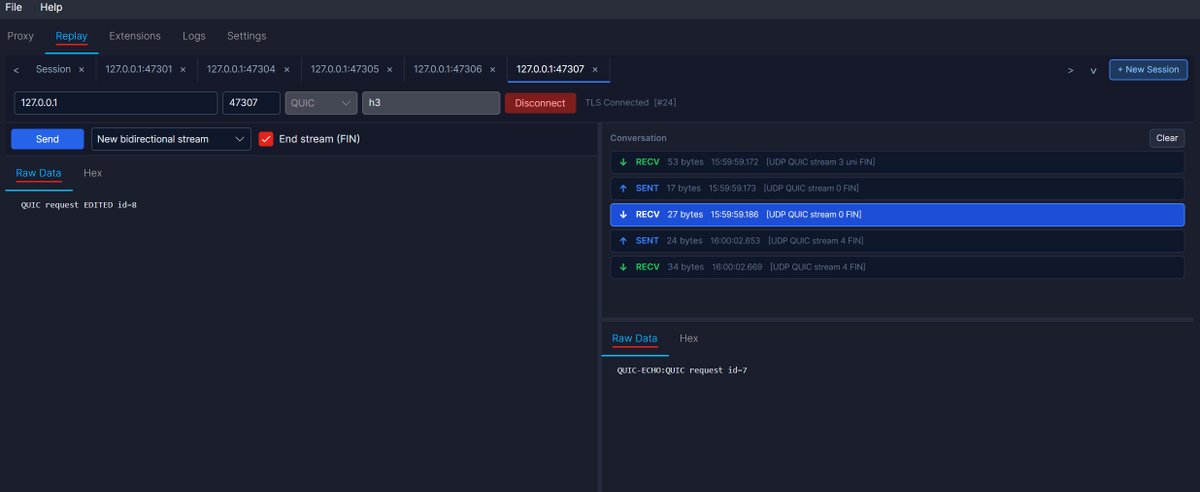
ALT InterceptSuite Replay Packets

ALT InterceptSuite MCP Server

ALT InterceptSuite Intercept Rules

ALT InteceptSuite Proxy History
InterceptSuite retweeted
Burp Suite works great for HTTP—but what about desktop apps that don’t use HTTP? 🚫 Learn how @InterceptSuite saves the day by intercepting raw TCP/TLS traffic in our latest blog:
interceptsuite.com/blog/burp…
#BurpSuite #PenTest #Cybersecurity

Did you know Burp Suite only covers HTTP? 🤔 With InterceptSuite’s new SOCKS5 MITM proxy, you can inspect any TCP/TLS traffic (even QUIC, IoT protocols).
🚀 Read how in our blog: interceptsuite.com/blog/burp…
#InterceptSuite #BurpSuite
1
76