

God's plan💫
Dubai, United Arab Emirates
Joined November 2021
- Tweets279
- Following0
- Followers1.1K
- Likes35K





I reported a supply chain dependency confusion issue to Amazon that resulted in confirmed internal RCE via a malicious npm package.
The package executed automatically during normal dependency resolution and returned a callback proving it ran inside Amazon’s internal environment.
The report was closed as “operational security.”
This isn’t OSINT.
This isn’t theoretical.
This was real code execution inside corporate infrastructure.
I’ve followed up multiple times and contacted @Hacker0x01 support. No clarification so far.
@amazon @Hacker0x01
#BugBounty #AppSec #SupplyChainSecurity #hackerone #amazonsecurity

Security work pays off — literally and professionally.
Disclosed a CRITICAL issue to @krakenfx , helped improve their security, and earned a six-figure bounty $$$,$$$.
This only pushes me to go harder in bug bounty & security research 💪
#HackerMindset #BugBounty #kraken #Web3

Yay, I was awarded a $$,$$$ bounty on @Hacker0x01
Happy to secure!
#hackerone #rce #supplychain #bugbounty

I have found a RCE in @AsrcSecurity and i was try to report directly but i couldn't because their security domain login didn't work for me and i see they stop bug bounty program in @Hacker0x01 also they running VDP. I don't want to report VDP is there any other way?
#BugBounty
2
6
1,274
7/
I’m disappointed, but not surprised.
Big tech companies love open-source
...until it’s used to show real flaws in their processes.
This was a valid, impactful bug. Google shut it down.
1
3
1,199
6/
Google even uses this same package internally (public GitHub search confirms it in their org).
So the impact was not theoretical.
They just didn’t want to deal with the supply chain reality we all face.
1,031
5/
This is how real-world Dependency Confusion works:
* You publish a package
* It’s pulled by mistake (or by automation)
* Code is executed during install
* You gain RCE
It doesn’t need to be "prod" to be dangerous. It just needs to run in an internal context.
2
1
1,041
4/
Supply chain RCEs don’t need direct infra access they exploit the human + automation factor in CI/CD and dev environments.
That’s exactly what happened here. A Googler machine ran my malicious package. Google ignored it.
Why?
1
950
3/
Google claimed the machine was "likely personal" despite logs showing usage of Google-specific tooling, Google Cloud SDK and package installs consistent with internal usage.
Even if this was a dev’s machine, it shows Google’s real-world exposure.
1
963
2/
I responsibly reported it to Google VRP, highlighting it as a Dependency Confusion attack a well-known supply chain vector.
Instead of investigating, Google closed it saying:
"We will not be investigating this further...”
3
1,191
Just got a reward for a critical RCE vulnerability submitted on @Bugcrowd
#ItTakesACrowd #bugbounty #RCE #bugcrowd #hackerone


3
57
2,576


Yay, I was awarded a $$,$$$ bounty on @Hacker0x01!
Happy to secure @Airbnb
#hackerone #bugbounty #airbnb #rce


Hello @yeswehack why don't you have paypal payment option? The bank payment is very late and sucks. It almost 3weeks still i dont get my payment. Kindly add the other payment options like crypto, PayPal it's very helpful for the researchers in future.
1
2
905
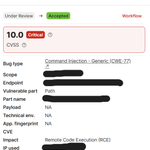
Just got a reward for a critical vulnerability submitted on @yeswehack -- Command Injection - Generic (CWE-77).


Another Remote Code Execution (RCE) exploit successfully reported and accepted with Perfect 10.0 CVSS score 🎯💰
A big thanks to the security team for their swift review✌ @yeswehack
#BugBounty #YesWeHack #CyberSecurity #RCE #SecurityResearch #hackerone #bugcrowd #Immunefi

