





Pinned Tweet
1/ Faites très attention au marketing de Tangem dans ces moments de panique.
Tangem n'est pas du tout une solution miracle. Elle est pleine de compromis en matière de sécurité qui sont trop peu mis en évidence.
Reprenons certains points très importants 👇

Ledger Cryptobilis Incident: How Complexity Creates Security Risks
The simpler the wallet, the more difficult it is to fit anything extra inside.
💡How Tangem’s design addresses risks like this:
1. Seedless by design. No seed phrase to capture.
2. Just a card. No screen, battery, USB, or Bluetooth, so fewer attack vectors.
3. Buy anywhere, verify in the app. Tangem checks your wallet’s authenticity and warns you if it was activated before you received it.
Full breakdown on our blog:
tangem.com/en/blog/post/ledg…
Rarement vu un truc aussi idiot.

#PJL2027 Adopté par l'Assemblée nationale : la "taxe assise sur les flux de données numériques émises par les fournisseurs de contenu et acquittée par ces derniers"
Selon les députés PS, "au taux de 0,055 € par giga, un rendement de 10Md€ est attendu".
assemblee-nationale.fr/dyn/1…

Julien Guilloux retweeted
Keystone fam,
Here's an update on some of the actions we promised and how to protect yourself from phishing.
Where things stand:
- We cut shipping data retention from 180 to 90 days, effective now.
- Want your data gone sooner? Once your order arrives, contact our support team, and we'll delete it right away.
- We emailed every affected user from [email protected].
- We paused all shipments and began quarantining affected devices at every warehouse we use, including Amazon's.
- We're answering your questions here on X and through support tickets.
Thank you to everyone who shared feedback on the lookup page for affected users. We're working through every concern to make it as secure as possible.
Stay safe from phishing:
- Incident emails only come from [email protected]. Check the sender every time.
- We will never ask for your seed phrase. Not by email, DM, or phone.
- If a message pushes you to act fast, stop and check with us first.
We'll share more on next steps in the coming days.
Again, we're sorry we let this happen. We're doing everything we can to make it right and to help every affected user through it.
Questions, or think we missed something? Drop them in the replies.


Les embrouilles sur X ont changé 😆
Ça se menace carrément à coup de milliards maintenant.
Je suis trop pauvre, je retourne sur Facebook.

"les exchanges sont plus safe que les hardware wallets"

Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…

Les implants matériels qui avaient touché Ledger avec le revendeur CryptoBilis concernent également Trezor.
Comme je l'avais expliqué, cette histoire pouvait concerner tous les constructeurs de hardware wallet passant par ce revendeur.
Soyez prudents et suivez les conseils de Trezor si vous avez acheté un hardware wallet par ce revendeur.

CryptoBilis update
We've been made aware, through responsible disclosure, of a single hardware implant in a Trezor Safe 5 device bought from the reseller CryptoBilis in August 2026.
No CryptoBilis buyer has reported a loss of funds to us.
IMPORTANT: If you bought a Trezor from CryptoBilis from March 2026 onwards, we know this is unsettling. Here’s what to do:
Already using it?
Move your funds to a newly created wallet with a new seed as soon as possible. Do not reuse the old seed in any wallet, hardware or software. If you don’t have another secure hardware wallet available, we recommend temporarily migrating your funds to a software wallet or an exchange you are familiar with.
Not set up yet? Don’t set it up, and never enter your existing wallet backup on it.
We haven’t received the device to confirm this report, but based on the customer’s description, we’re treating it as credible and sharing it now so customers who purchased a Trezor via CryptoBilis can secure their funds as a precaution. Our security team will examine the device as soon as it arrives.
On October 9, 2026, we removed CryptoBilis as a reseller following reports of tampered Ledger devices sold through it. Since then, we have been inspecting Trezor devices that customers bought from CryptoBilis and have found no signs of tampering on any of the four devices we’ve received so far.
NEVER share your wallet backup (recovery phrase) with anyone. Trezor Support will never ask for it.
If you are affected by this incident, please keep your CryptoBilis device and contact Support to receive a new Trezor hardware wallet: trezor.io/support#open-chat
We're investigating and will post updates here as soon as we know more. Thank you to the customer who reported this through our responsible disclosure program, and to @SEAL_911 for working alongside our teams on the response. Reports and engagement like this help us protect everyone else.
For more information, visit our blog: trezor.io/blog/news/implant-…

Encore une plateforme qui s'est fait avoir...

🚨 FLASH: Binance face à un hack de près de 3 milliards de dollars ?!
2,77 milliards de dollars sortent des portefeuilles Binance sur cinq blockchains, sur fond de soupçons de vidage de portefeuilles.
Un possible vol de fonds des hot wallets a été signalé, avec plus de 60 jetons transférés vers une adresse financée par Tornado Cash.
Le hack reste non confirmé et les détails sont encore flous.

Julien Guilloux retweeted

We've identified & fixed an issue impacting our international platform, Polymarket.com. One of our 3rd party providers was compromised, and we have referred this to relevant law enforcement.
Anyone who has been impacted will be made whole.
Out of an abundance of caution, we have temporarily halted trading & are working to bring the platform back online.
S'ils avaient fait ça en France, ils se seraient fait enlever dès la première semaine.

Finally Home! 🏡
Just wrapped up an epic 3 week cross-country road trip with @Tangem from Boston to San Francisco on their Campus Tour🎉
Talked to a ton of students about self-custody, protecting their assets, and why owning your keys actually matters. 🔒
The conversations were real, the energy was high, and a lot of them walked away understanding that “not your keys, not your crypto” isn’t just a slogan. 🔑
If you’ve been thinking about taking control of your own assets, now’s a solid time. ⏰
Use my referral link + promo code SEEDLESS for up to 30% off Tangem products! 🎁
#Seedless #TANGEMBUS #tangemPAY

Julien Guilloux retweeted
Dear Keystone fam,
We know this has been a stressful week, and many of you have questions. Here are answers to the ones we’re hearing most.
→ I bought my device in 2024/2025/2026. Am I affected?
If you placed an order from 2024 to 2026, your shipping data may have been exposed. We’re building a page where you can check whether you’re affected, and we’ll share it here as soon as it’s live.
→ The authentication key was exposed. How can I verify a device delivered before Oct 20?
Our device verification page still runs on the old authentication key, so you can still use it to verify an unopened Keystone. The attacker has that key now, but it doesn’t affect devices that were already delivered before Oct 20.
→ I already use my Keystone. Can I keep using it?
Yes. If you received it before Oct 20, verify it on our website and keep using it as normal.
→ I received my device on/after Oct 20. What should I do?
With the key exposed, attackers could build a fake device with the real key inside, making it look genuine. Contact our support team right away at [email protected], and they’ll walk you through the next steps.
→ My order is in transit. What should I do?
Refuse the package when it arrives and email us at [email protected]. Our support team will help you from there.
→ Is it safe to place a new order on your website?
Yes. Because of the key leak, we’ve set aside all existing Keystone 3 Pro inventory to be destroyed. Any order you place now is a pre-order from a fresh batch with new authentication keys, expected to arrive in 4 to 6 weeks. If you’re OK with the wait, go ahead and order.
→ Is it still safe to update my Keystone’s firmware?
Yes. Your Keystone only installs firmware signed by our team. The key that leaked is our web authentication key, which is completely separate from our firmware signing key. Firmware updates are safe, so you can update and keep using your device as normal.
⚠️ Remember, scammers may pose as Keystone by phone, text, email, or mail, offering refunds, replacement devices, or “fixes” for your order or address. None of it is from us.
We will never ask for your recovery phrase or private keys. NEVER share them with anyone, and NEVER enter your recovery phrase into a device you didn’t order. Don’t click links in messages you weren’t expecting. Type keyst.one into your browser yourself.
Need help? Reach us directly here on X or at [email protected]
Once again, we’re sorry we let this happen. We’re doing everything we can to make it right and to help every affected user through it.
Still have questions, or think we missed something? Drop them in the replies, and we’ll help.


Julien Guilloux retweeted
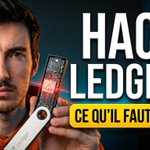
Hack Ledger : on fait le point dans cette vidéo !
On voit ce qu'il s'est passé, les risques et comment mieux se protéger.
Lien en commentaire 👇
🤖 Made with AI


Coup dur pour Keystone.
Ils se sont fait dérober la clé WebAuth qui sert à vérifier l’authenticité d’un appareil sur leur page d’authentification.
Pour rappel, cette dernière est intégrée dans les hardware wallets au moment de leur fabrication et ne peut être ni effacée ni remplacée.
Keystone doit donc tout basculer sur une nouvelle clé WebAuth car si un attaquant possède cette clé, il pourrait théoriquement fabriquer des contrefaçons capables de passer les contrôles d'authenticité.
Les appareils en stock sont donc invendables et Keystone annonce détruire plus de 18000 produits.
Fuite de données chez Keystone.
Faites attention aux e-mails que vous recevez.
Une fuite de données n'est jamais anodine, encore moins quand cela vient d'un acteur du secteur des cryptomonnaies.
Faites attention à vous.
We owe you an apology.
On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we didn't keep them safe.
Exposed: names, contact details, shipping addresses, and order details (items and prices).
Not exposed: payment card or bank details, recovery phrases, private keys, or wallet passwords.
We've blocked access, fixed the vulnerability, opened an investigation, and are emailing affected customers.
Scammers may pose as Keystone by phone, text, email, or mail, offering refunds, replacement devices, or "fixes" for your order or address. None of it is from us.
NEVER share your recovery phrase or private keys, and NEVER enter your recovery phrase into a device you didn't order. We will never ask for them. Don't click links in unexpected messages. Type keyst.one yourself.
A detailed report is coming soon.
Until then, trust only our official channels. If anything feels off, email [email protected]. We'd rather hear from you than have you take a chance.
Again, we're truly sorry to everyone affected.
Julien Guilloux retweeted

Lille suit !
Une majeure partie de collectivités territoriales en France vont suivre.
Débranchez vos sites internet s'ils tournent sous php et patchez !
C'est hyper critique.
php2shell. teapaw.org/lillefrance/status/211…
C'est exactement ce vers quoi doivent tendre tous les constructeurs de hardware wallet.
Améliorer sans cesse leurs produits et tout ce qui gravite autour qui pourrait menacer leurs utilisateurs.
Aucune solution n'existe pour se protéger contre les attaques sur les chaînes d'approvisionnement, il est cependant possible de réduire les risques.
Cela est valable pour Ledger et tous les autres constructeurs qui auraient pu être concernés par cette affaire.
En prendre conscience et traiter ça sérieusement est une très bonne chose 👏
📣 The Ledger supply chain attack is a wake-up call for every hardware wallet maker. Us included.
And we’re treating it like one.
Here’s what that means:
Our team is auditing our entire supply chain, starting with how we vet and manage resellers, and tightening controls wherever this kind of attack could slip through.
On the device side, the Keystone 3 Pro already ships with anti-tamper protection, and we’ll make it even tougher in every device that follows.
Keeping your keys safe is the reason Keystone exists. We’ll work every day to stop attacks like this before they ever reach you.
Huge thanks to the whole Keystone community for your continued support 💙

