

For over 20 years, leading companies in Cybersecurity, Healthcare, Finance, New Media and more have come to rely on Loginsoft as a trusted technology partner.
Chantilly, VA USA
Joined June 2018
- Tweets471
- Following64
- Followers228
- Likes3



Disclosures turned into attacks within hours this week, and flaws patched months ago were still being exploited.
𝗞𝗲𝘆 𝘁𝗵𝗿𝗲𝗮𝘁𝘀 𝘁𝗵𝗶𝘀 𝘄𝗲𝗲𝗸:
🔹CISA added nine vulnerabilities to its KEV catalog, including all four flaws in the Plex2Shell chain, plus Atlassian Data Center, BeyondTrust Remote Support, SiteGuard Server, Siemens Software Center and multiple Fortinet products, some patched as far back as April and August
🔹Active exploitation hit the PHP core flaws four days before disclosure, and the Redis RESTORE flaw was attacked on October 16-17
🔹ARMORY CASTLE exploited BeyondTrust Remote Support as a zero-day, deploying the SAWFLY webshell and the BARECLAW SOCKS5 tunneler
🔹Plex2Shell attackers dropped the myawesomeproxy proxyware alongside an XMRig miner
🔹CL-STA-0954 deployed PEERSTITCH, a stealthy memory-resident ARM64 implant on Fortinet firewalls
🔹Multiple ransomware groups exploited the PAN-OS GlobalProtect authentication bypass to break into corporate networks
The lesson: a patch that isn’t applied is an open door. Patch fast, cut exposure, and hunt for compromise.
Get the full breakdown in this week’s LOVI report: loginsoft.com/reports/weekly…
#ThreatIntelligence #CyberSecurity #VulnerabilityManagement #ZeroDay #CISAKEV #LOVI #Loginsoft #VulnerabilityIntelligence #Plex #BeyondTrust #Fortinet #PEERSTITCH #PaloAltoNetworks #Ransomware

Zero-days and decade-old flaws hit at the same time this week, and attackers exploited both. CISA added 11 vulnerabilities to its KEV catalog, including zero-days in Palo Alto Networks PAN-OS, Cisco Secure Email Gateway, Microsoft Windows and Ivanti Connect Secure, plus two chained AhsayCBS flaws. Five older flaws also landed in KEV after a joint advisory confirmed exploitation by Chinese government-linked actors, some dating back more than 10 years: Apache Struts, ProFTPD, ISC BIND, ONLYOFFICE and Strapi.
𝗞𝗲𝘆 𝘁𝗵𝗿𝗲𝗮𝘁𝘀 𝘁𝗵𝗶𝘀 𝘄𝗲𝗲𝗸:
🔹UTA0576 chained three Ivanti zero-days to gain root access without leaving a web shell
🔹AhsayCBS backup servers were hijacked to run a disguised XMRig cryptominer
🔹CL-STA-0954 deployed PEERSTITCH, a stealthy memory-resident FortiGate implant
🔹Attackers exploited the Bricksforge WordPress plugin and redirected EC-CUBE shoppers to phishing pages
The lesson: an unpatched vulnerability doesn’t expire. Patch fast, cut exposure, and hunt for compromise.
Get the full breakdown in this week’s LOVI report : loginsoft.com/reports/weekly…
#ThreatIntelligence #CyberSecurity #VulnerabilityManagement #ZeroDay #CISAKEV #LOVI #Loginsoft #VulnerabilityIntelligence #PaloAltoNetworks #ApacheStruts #ONLYOFFICE #EC_CUBE #Cisco #PEERSTITCH #Bricksforge

𝗬𝗼𝘂𝗿 𝗰𝗼𝗻𝘁𝗮𝗶𝗻𝗲𝗿 𝗶𝗺𝗮𝗴𝗲 𝗽𝗮𝘀𝘀𝗲𝗱 𝘁𝗵𝗲 𝗯𝘂𝗶𝗹𝗱. 𝗕𝘂𝘁 𝗶𝘀 𝗶𝘁 𝘀𝗲𝗰𝘂𝗿𝗲 𝗲𝗻𝗼𝘂𝗴𝗵 𝗳𝗼𝗿 𝗽𝗿𝗼𝗱𝘂𝗰𝘁𝗶𝗼𝗻?
Imagine deploying hundreds of microservices across Kubernetes, only to discover hundreds of CVEs across your container images. Many may come from unnecessary packages and dependencies, leaving security teams overwhelmed with alerts and developers waiting to ship.
𝗧𝗵𝗲 𝘀𝗼𝗹𝘂𝘁𝗶𝗼𝗻 𝗶𝘀𝗻'𝘁 𝗷𝘂𝘀𝘁 𝘀𝗰𝗮𝗻𝗻𝗶𝗻𝗴 𝗺𝗼𝗿𝗲. 𝗜𝘁'𝘀 𝗿𝗲𝗱𝘂𝗰𝗶𝗻𝗴 𝘁𝗵𝗲 𝗮𝘁𝘁𝗮𝗰𝗸 𝘀𝘂𝗿𝗳𝗮𝗰𝗲 𝗮𝘁 𝘁𝗵𝗲 𝘀𝗼𝘂𝗿𝗰𝗲.
Loginsoft's 𝗛𝗮𝗿𝗱𝗲𝗻𝗲𝗱 𝗖𝗼𝗻𝘁𝗮𝗶𝗻𝗲𝗿 𝗜𝗺𝗮𝗴𝗲𝘀 service helps organizations strengthen container security through:
🔹Minimal images: Remove unnecessary packages, shells, and utilities.
🔹Secure configurations: Apply non-root execution and restricted permissions.
🔹SBOM + VEX: Improve dependency visibility and understand vulnerability exploitability.
🔹Signed attestations: Verify build provenance and strengthen software supply chain security.
🔹Continuous CVE monitoring: Track emerging vulnerabilities and patches.
𝗧𝗵𝗲 𝗶𝗺𝗽𝗮𝗰𝘁: Loginsoft's service page cites a typical 𝟲𝟬–𝟵𝟬% 𝗿𝗲𝗱𝘂𝗰𝘁𝗶𝗼𝗻 𝗶𝗻 𝗖𝗩𝗘 𝗰𝗼𝘂𝗻𝘁𝘀, helping reduce vulnerability noise and improve security visibility. Actual results vary by image and workload.
For security and engineering leaders, the goal is simple: 𝗿𝗲𝗱𝘂𝗰𝗲 𝘂𝗻𝗻𝗲𝗰𝗲𝘀𝘀𝗮𝗿𝘆 𝗿𝗶𝘀𝗸 𝘄𝗶𝘁𝗵𝗼𝘂𝘁 𝘀𝗹𝗼𝘄𝗶𝗻𝗴 𝗱𝗼𝘄𝗻 𝗱𝗲𝗹𝗶𝘃𝗲𝗿𝘆 across AWS, Azure, and GCP.
Explore our service: loginsoft.com/cloud-native-s…
#HardenedContainerImages #ContainerSecurity #CloudNativeSecurity #DevSecOps #Kubernetes #SoftwareSupplyChainSecurity

October opened with a relentless wave of exploitation, as attackers hit helpdesk platforms, email gateways, edge appliances and even office printers. Zero-days, AI-driven intrusions and hours-old disclosures left defenders almost no time to react.
𝗞𝗲𝘆 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗼𝗳 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹CISA added four flaws to its KEV catalog, including two Zammad zero-days that an autonomous AI agent chained to root in seconds, plus zero-days in Citrix NetScaler and Fortinet FortiMail. Attackers also moved fast on Atlassian Data Center, WordPress plugins, MediaWiki and Sharp printers, often within hours of disclosure.
🔹ClingSTUN built a stealthy IoT proxy network that hid inside public STUN traffic
🔹WHIPSHOT and SLAPSHOT surfaced in Citrix NetScaler zero-day attacks
🔹UAC-0277 turned 100+ compromised sites into ClickFix traps delivering LUNEXSTEALER
The gap between disclosure and exploitation keeps shrinking. Patch fast, cut exposure, and hunt for compromise.
Read the full breakdown in this week's LOVI report: loginsoft.com/reports/weekly…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #CISAKEV #Zammad #MediaWiki #WordPress #ClingSTUN #WHIPSHOT #SLAPSHOT #UAC0277 #ClickFix #LUNEXSTEALER

𝗦𝗲𝗽𝘁𝗲𝗺𝗯𝗲𝗿 𝟮𝟬𝟮𝟲 𝗰𝗼𝗺𝗽𝗿𝗲𝘀𝘀𝗲𝗱 𝘁𝗵𝗲 𝗲𝘅𝗽𝗹𝗼𝗶𝘁𝗮𝘁𝗶𝗼𝗻 𝘄𝗶𝗻𝗱𝗼𝘄 𝗳𝘂𝗿𝘁𝗵𝗲𝗿
🔹CISA's KEV catalog grew by 43 entries, the highest monthly count of 2026. Cisco, Citrix, MikroTik, Microsoft, Google, and JFrog accounted for the bulk of additions, confirming in-the-wild exploitation across perimeter appliances, OS components, browsers, and software supply chain infrastructure.
🔹Active exploitation persisted throughout the month, as threat actors hit perimeter devices, AI platforms, WordPress plugins, and webmail servers through authentication bypass, code injection, and file upload flaws.
🔹Ransomware telemetry showed a leaderboard shift. TheGentlemen led ransomware activity with 102 victims, followed by Qilin (74) and KRYBIT (34).
The organizations that came through September safely weren't the ones that patched everything. They were the ones that patched the right things first.
Get the full breakdown in this month's LOVI report: loginsoft.com/reports/monthl…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #September2026 #ActivelyExploited #CISAKEV #Cisco #Citrix #MikroTik #Microsoft #Google #JFrog #Langflow #LiteLLM #Roundcube #WordPress #Ransomware #TheGentlemen #Qilin #KRYBIT #Safepay #IncRansom

The final week of September 2026 left no room for delayed patching. It closed with fresh evidence that both opportunistic exploitation and state-sponsored campaigns continued to accelerate, as critical zero-day vulnerabilities in network perimeter infrastructure drew emergency responses from vendors, national CERTs, and law enforcement.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹CISA added six vulnerabilities to its KEV catalog, headlined by two Citrix NetScaler zero-days that drew emergency pre-disclosure warnings from the Dutch NCSC-NL, alongside flaws in Microsoft SharePoint, MikroTik RouterOS, Apple CoreGraphics, and WordPress Core
🔹SharePoint exploitation escalated to webshell deployment within hours of technical disclosure, while WordPress Core drew 548,000+ blocked attacks within 24 hours of going public
🔹Volexity identified UTA0565 as the third Chinese APT group to weaponize the same shared Chrome and Windows zero-day chain reported last week, delivering the previously undocumented CLEANGULP backdoor through typosquatted media and NGO websites
The through-line is not just speed but coordination. Vendors, CERTs, and law enforcement moved to pre-notification protocols before patches existed, while state-sponsored actors demonstrated that shared exploit development turns one zero-day chain into three simultaneous campaigns.
Full breakdown in this week's LOVI report:loginsoft.com/reports/weekly…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #Microsoft #WordPressCore #MikroTikRouter #Apple #UTA0565 #ThreatActor #CitrixNetScaler

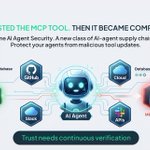
𝗬𝗼𝘂 𝗮𝗽𝗽𝗿𝗼𝘃𝗲𝗱 𝘁𝗵𝗲 𝗠𝗖𝗣 𝘁𝗼𝗼𝗹. 𝗕𝘂𝘁 𝗰𝗮𝗻 𝘆𝗼𝘂 𝘁𝗿𝘂𝘀𝘁 𝗶𝘁 𝘁𝗼𝗱𝗮𝘆?
As AI agents connect to GitHub, cloud environments, databases, Slack, CI/CD, and other enterprise systems through 𝗠𝗼𝗱𝗲𝗹 𝗖𝗼𝗻𝘁𝗲𝘅𝘁 𝗣𝗿𝗼𝘁𝗼𝗰𝗼𝗹 (𝗠𝗖𝗣), a new supply-chain risk is emerging: 𝗠𝗖𝗣 𝗥𝘂𝗴 𝗣𝘂𝗹𝗹 𝗔𝘁𝘁𝗮𝗰𝗸𝘀.
A tool can be legitimate when approved, then change its behavior later, while the AI agent continues to trust it.
𝗧𝗵𝗶𝘀 𝗰𝗮𝗻 𝗹𝗲𝗮𝗱 𝘁𝗼:
🔹Data exfiltration
🔹Credential exposure
🔹Unauthorized actions
🔹Workflow manipulation
For CIOs, CISOs, and security leaders, the question is no longer just:
“𝗗𝗶𝗱 𝘄𝗲 𝗮𝗽𝗽𝗿𝗼𝘃𝗲 𝘁𝗵𝗶𝘀 𝘁𝗼𝗼𝗹?”
“𝗜𝘀 𝘁𝗵𝗲 𝘁𝗼𝗼𝗹 𝘄𝗲 𝘂𝘀𝗲 𝘁𝗼𝗱𝗮𝘆 𝘀𝘁𝗶𝗹𝗹 𝘁𝗵𝗲 𝘁𝗼𝗼𝗹 𝘄𝗲 𝗮𝗽𝗽𝗿𝗼𝘃𝗲𝗱?”
Organizations should consider provenance and integrity verification, version controls, continuous change detection, least-privilege access, runtime monitoring, and re-approval workflows.
𝗔𝗜 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗶𝘀𝗻'𝘁 𝗼𝗻𝗹𝘆 𝗮𝗯𝗼𝘂𝘁 𝘀𝗲𝗰𝘂𝗿𝗶𝗻𝗴 𝘁𝗵𝗲 𝗺𝗼𝗱𝗲𝗹. 𝗜𝘁’𝘀 𝗮𝗯𝗼𝘂𝘁 𝗰𝗼𝗻𝘁𝗶𝗻𝘂𝗼𝘂𝘀𝗹𝘆 𝘃𝗲𝗿𝗶𝗳𝘆𝗶𝗻𝗴 𝗲𝘃𝗲𝗿𝘆𝘁𝗵𝗶𝗻𝗴 𝘁𝗵𝗲 𝗺𝗼𝗱𝗲𝗹 𝘁𝗿𝘂𝘀𝘁𝘀.
Read the full analysis: loginsoft.com/post/mcp-rug-p…
#AISecurity #MCP #AgenticAI #AIAgents #Cybersecurity #CISO #CIO #CTO #AISupplyChain #SupplyChainSecurity #LLMSecurity #AIThreats #EnterpriseSecurity #CyberRisk

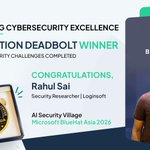
𝗖𝗬𝗕𝗘𝗥𝗦𝗘𝗖𝗨𝗥𝗜𝗧𝗬 𝗘𝗫𝗖𝗘𝗟𝗟𝗘𝗡𝗖𝗘 𝗜𝗡 𝗔𝗖𝗧𝗜𝗢𝗡
We’re proud to celebrate 𝗥𝗮𝗵𝘂𝗹 from 𝗟𝗼𝗴𝗶𝗻𝘀𝗼𝗳𝘁 for completing all 5 challenges at the 𝗔𝗜 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗩𝗶𝗹𝗹𝗮𝗴𝗲 and winning 𝗢𝗽𝗲𝗿𝗮𝘁𝗶𝗼𝗻 𝗗𝗲𝗮𝗱𝗯𝗼𝗹𝘁 at 𝗠𝗶𝗰𝗿𝗼𝘀𝗼𝗳𝘁 𝗕𝗹𝘂𝗲𝗛𝗮𝘁 𝗔𝘀𝗶𝗮 𝟮𝟬𝟮𝟲.
A major highlight of the event was 𝗢𝗽𝗲𝗿𝗮𝘁𝗶𝗼𝗻 𝗗𝗲𝗮𝗱𝗯𝗼𝗹𝘁, an AI security challenge focused on attacking and securing AI models. Rahul achieved 𝗙𝗶𝗿𝘀𝘁 𝗕𝗹𝗼𝗼𝗱 🩸, successfully completed the challenge, and was recognized as a winner, receiving the trophy.
This remarkable accomplishment reflects Rahul’s technical expertise, problem-solving mindset, and passion for advancing cybersecurity and AI security.
Congratulations, Rahul!
#Loginsoft #Cybersecurity #AISecurity #BlueHatAsia2026 #OperationDeadbolt #SecurityResearch

This week, attackers probed the seams of enterprise infrastructure and found plenty to work with, turning freshly disclosed flaws in kernels, VPN gateways, and web platforms into active campaigns before many teams could react.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹CISA added eight vulnerabilities to its KEV catalog, including three Linux kernel flaws, two Check Point product flaws, and one each in F5 BIG-IP APM, Arista VeloCloud Orchestrator, and Zyxel GS1900 switches
🔹Active exploitation surfaced across Roundcube Webmail, WordPress Core, and the Orkes Conductor workflow platform, with some flaws weaponized within hours of public disclosure
🔹Volexity uncovered a third Chinese APT, UTA0565, chaining the same Chrome and Windows zero-days as UTA0560 and JungleBamboo, this time through typosquatted fake websites to deploy the previously undocumented CLEANGULP backdoor
The through-line is speed. The gap between disclosure and exploitation keeps shrinking, and shared exploit kits are letting separate actors strike the same surfaces in parallel.
Full breakdown in this week's report: loginsoft.com/reports/weekly…
#Cybersecurity #ThreatIntelligence #Loginsoft #Vulnerability #LOVI #CISAKEV #WordPress #CheckPoint #Zyxel #F5 #ZeroDay #CLEANGULP #UTA0565

𝟳𝟬% 𝗼𝗳 𝗖𝗹𝗼𝘂𝗱 𝗕𝗿𝗲𝗮𝗰𝗵𝗲𝘀 𝗦𝘁𝗮𝗿𝘁 𝗪𝗶𝘁𝗵 𝗮 𝗠𝗶𝘀𝗰𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗮𝘁𝗶𝗼𝗻
Cloud security isn’t just a patching problem anymore.
Misconfigured IAM, exposed storage, overly permissive access, and insecure cloud controls can create an attack path long before a CVE becomes the issue.
That’s why 𝗰𝗹𝗼𝘂𝗱 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗶𝘀 𝗮𝗻 𝗲𝗻𝗴𝗶𝗻𝗲𝗲𝗿𝗶𝗻𝗴 𝗽𝗿𝗼𝗯𝗹𝗲𝗺.
Security teams need to continuously:
🔹Identify misconfigurations
🔹Prioritize the risks that matter
🔹Strengthen cloud posture
🔹Automate security controls
🔹Validate that fixes actually work
The shift is simple:
𝗗𝗼𝗻’𝘁 𝗷𝘂𝘀𝘁 𝗽𝗮𝘁𝗰𝗵 𝘃𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀. 𝗘𝗻𝗴𝗶𝗻𝗲𝗲𝗿 𝗮 𝘀𝗲𝗰𝘂𝗿𝗲 𝗰𝗹𝗼𝘂𝗱 𝗲𝗻𝘃𝗶𝗿𝗼𝗻𝗺𝗲𝗻𝘁.
Explore Loginsoft’s 𝗖𝗹𝗼𝘂𝗱 𝗜𝗻𝗳𝗿𝗮𝘀𝘁𝗿𝘂𝗰𝘁𝘂𝗿𝗲 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝘀𝗲𝗿𝘃𝗶𝗰𝗲𝘀: loginsoft.com/cloud-infrastr…
#CloudSecurity #CloudMisconfiguration #CSPM #CloudBreach #CloudPosture #Cybersecurity #CloudInfrastructure

This week the threat landscape delivered zero-days under active attack, chained exploits, and relentless pressure on enterprise infrastructure simultaneously.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹CISA added 10 vulnerabilities to its KEV catalog, including dual flaws in MikroTik RouterOS and JFrog Artifactory exploited in coordinated campaigns
🔹Active exploitation confirmed across WSO2 API Manager, The Events Calendar WordPress plugin, and Issabel Framework within 24-hour windows
🔹Nation-state and hacktivist clusters converged on identical vulnerability surfaces through shared exploit infrastructure, transforming individual flaws into synchronized multi-vector attacks
🔹NightEagle and Hacking Cat targeted Russian enterprises with GhostContainer backdoors and polymorphic Monkey Ransomware variants
🔹UTA0560 and JungleBamboo synchronized Chrome V8 exploitation chains targeting international NGOs with credential-stealing extensions
🔹Red Heron rapidly weaponized Gitea vulnerabilities across seven countries, while Mirai_ptea and Mirai_aurora infiltrated legacy IoT infrastructure establishing encrypted botnet networks
Full breakdown in this week's LOVI intelligence report: loginsoft.com/reports/weekly…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #WSO2 #WordPress #Issabel #MikroTik #JFrog #AISecurity #ZeroDayExploits #ThreatIntelligence

70% of cloud breaches start with a misconfiguration.
Not a CVE. Not a zero-day. A misconfiguration.
In cloud, configuration is code. And configuration drift is your attack surface.
🔹 Over permissioned IAM roles sitting idle
🔹 Storage buckets exposed to public read
🔹 Security groups with 0.0.0.0/0 left open
🔹 CloudTrail logging disabled in production
CSPM tools surface these. The real fix is treating cloud posture as a control engineering discipline: drift detection in CI/CD, misconfiguration as code debt.
At Loginsoft, we help teams build proactive cloud posture programs so misconfigurations never reach production.
Is your cloud security strategy still reactive? Drop a comment below.
#CloudSecurity #CSPM #CloudMisconfiguration #CloudPosture #CyberSecurity #DevSecOps

When your firewall becomes the front door and your browser becomes the attack surface, it's not a slow week in cybersecurity. This one wasn't.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹Nine actively exploited vulnerabilities hit the CISA KEV catalog, spanning Microsoft, Google, Cisco, Fortinet, Citrix, N-Able, and Adobe, with four confirmed as zero-days
🔹Four state-aligned espionage clusters adopted the same exploit kit, BlueMoon, within days of each other, weaponizing Chrome patch-gap zero-days before stable fixes reached users
🔹PivotC2, an AI-assisted RAT built exclusively for FortiGate appliances, turned compromised firewalls into autonomous credential-harvesting machines, with 178 infections confirmed out of 30,000+ targeted
🔹Three separate threat clusters converged on Cisco FMC vulnerabilities, deploying Cyclops Blink malware and Qilin ransomware through the same attack surface
🔹MikroTik routers fell to "MikroTrick," a chained SSH exploit discovered by Poland's CERT with the help of GPT-5.5-cyber and GPT-5.6-sol
🔹AI fingerprints showed up in both offensive tooling and defensive research, the line between who uses AI and how is getting thinner every week
Full breakdown in this week's LOVI report: loginsoft.com/reports/weekly…
#Cybersecurity #Loginsoft #LOVI #Vulnerabilty #Intelligence #Microsoft #GoogleChrome #CISAKEV #MikroTrick #Fortinet #Cisco #Citrix

Your AI model passed the benchmark.
𝗕𝘂𝘁 𝗰𝗮𝗻 𝘆𝗼𝘂 𝘁𝗿𝘂𝘀𝘁 𝗶𝘁 𝗶𝗻 𝗽𝗿𝗼𝗱𝘂𝗰𝘁𝗶𝗼𝗻?
AI can still hallucinate, fail on edge cases, generate false positives, or behave unpredictably under adversarial inputs.
That’s why 𝗔𝗜 𝗠𝗼𝗱𝗲𝗹 𝗩𝗮𝗹𝗶𝗱𝗮𝘁𝗶𝗼𝗻 matters.
At Loginsoft, we test AI models against real-world scenarios using:
🔹Domain-specific test cases
🔹Human expert validation
🔹Adversarial testing
🔹Failure & hallucination analysis
🔹Continuous validation
𝗨𝗽 𝘁𝗼 𝟵𝟴% 𝗮𝗰𝗰𝘂𝗿𝗮𝗰𝘆.
𝗨𝗽 𝘁𝗼 𝟳𝟬% 𝗵𝗮𝗹𝗹𝘂𝗰𝗶𝗻𝗮𝘁𝗶𝗼𝗻 𝗿𝗲𝗱𝘂𝗰𝘁𝗶𝗼𝗻.
𝟯× 𝗳𝗮𝘀𝘁𝗲𝗿 𝗶𝗺𝗽𝗿𝗼𝘃𝗲𝗺𝗲𝗻𝘁 𝗰𝘆𝗰𝗹𝗲𝘀.
Don’t just deploy AI.
𝗩𝗮𝗹𝗶𝗱𝗮𝘁𝗲 𝗶𝘁. 𝗧𝗿𝘂𝘀𝘁 𝗶𝘁. 𝗧𝗵𝗲𝗻 𝘀𝗰𝗮𝗹𝗲 𝗶𝘁.
Learn more: loginsoft.com/artificial-int…
#AI #ArtificialIntelligence #AIModelValidation #LLM #GenerativeAI #AIGovernance #AISecurity #ResponsibleAI #Cybersecurity #EnterpriseAI

As August rolled into September, the threat landscape offered no quiet handover: the new month opened with zero-days under active attack, chained exploits, and a fresh wave of pressure on both enterprise and AI infrastructure.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹CISA added 12 vulnerabilities to its KEV catalog, including two SonicWall SMA1000 flaws and two PaperCut NG/MF flaws exploited as chained zero-days
🔹Active exploitation beyond KEV struck Langflow, the Elementor Pro WordPress plugin, and Ruby on Rails Active Storage, some within days of going public
🔹The AI stack took direct hits, with LiteLLM, Langflow, and Kestra targeted for the API keys, model access, and cloud credentials they quietly hold
🔹ToxNetV2 surfaced as an AI-assisted Linux botnet that plugged a language model into its controller, spreading through neglected IoT and networking gear while still leaning on a human to approve its moves
Full breakdown in this week's LOVI report: loginsoft.com/reports/weekly…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #SonicWall #PaperCut #JFrog #LiteLLM #Langflow #RubyonRails #ToxNetV2 #AISecurity #ZeroDay

𝗔𝘂𝗴𝘂𝘀𝘁 𝟮𝟬𝟮𝟲 𝗱𝗶𝗱𝗻'𝘁 𝗲𝗮𝘀𝗲 𝘂𝗽 𝗳𝗼𝗿 𝗮 𝘀𝗶𝗻𝗴𝗹𝗲 𝗱𝗮𝘆.
By the time the month closed, CISA had added 32 vulnerabilities to its KEV catalog, one of the heaviest runs of the year, and every entry told the same story: attackers were already inside real systems before most defenders knew there was an unpatched vulnerability.
Meanwhile, the human threat sharpened. The China-linked QTFY group breached US critical infrastructure. The Chinese-speaking UAT-10147 crew folded AI directly into its attacks and deployed a cross-platform backdoor. And the Mirai-bred Evooo1Bot botnet quietly turned everyday routers and cameras into weapons.
Then came the extortion. Qilin dominated the month with 162 organizations hit, followed by TheGentlemen at 111 and Cl0p at 85, a relentless pace that showed just how industrialized ransomware had become.
The takeaway was hard to miss: the gap between disclosure and exploitation had all but disappeared. In August, speed wasn't an advantage. It was survival.
Full breakdown in this month's LOVI report: loginsoft.com/reports/monthl…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #August2026 #ActivelyExploited #CISAKEV #Microsoft #TrueConf #PaperCut #Apple #Oracle #RedHat #Citrix #UAT10147 #QTFYgroup #Ransomware #Qilin #TheGentlemen #Cl0p

𝟳𝟬% 𝗼𝗳 𝗰𝗹𝗼𝘂𝗱 𝗯𝗿𝗲𝗮𝗰𝗵𝗲𝘀 𝘀𝘁𝗮𝗿𝘁 𝘄𝗶𝘁𝗵 𝗮 𝗺𝗶𝘀𝗰𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗮𝘁𝗶𝗼𝗻.
Not a CVE. Not a zero-day. A misconfiguration.
In cloud, configuration is code. And configuration drift is your attack surface.
🔹 Over permissioned IAM roles sitting idle
🔹 Storage buckets exposed to public read
🔹 Security groups with 0.0.0.0/0 left open
🔹 CloudTrail logging disabled in production
CSPM tools surface these. The real fix is treating cloud posture as a control engineering discipline: drift detection in CI/CD, misconfiguration as code debt.
At Loginsoft, we help teams build proactive cloud posture programs so misconfigurations never reach production.
Is your cloud security strategy still reactive? Drop a comment below.
#CloudSecurity #CSPM #CloudMisconfiguration #CloudPosture #CyberSecurity #DevSecOps

This week the pattern was pressure from both ends: a heavy run of catalog additions met a wave of same-week exploitation, while two China-linked campaigns showed how state-aligned operators and AI-assisted tooling keep bending toward internet-facing infrastructure.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹CISA added 11 vulnerabilities to its KEV catalog
🔹Active exploitation beyond KEV across GitLab, the Pods and TranslatePress WordPress plugins, miniOrange SAML SSO, TYPO3, and SPIP
🔹QTFY, a China-linked group tied to a Nanjing front company, breaching US critical infrastructure with its QScan, QTRouter, and QTBotnet platforms
🔹UAT-10147, a Chinese-speaking group, deploying the cross-platform SPECTRE implant with a Linux rootkit and AI-assisted development
Full breakdown in this week's LOVI report: loginsoft.com/reports/weekly…
#Cybersecurity #Loginsoft #Vulnerability #Intelligence #LOVI #Microsoft #RedHat #TrueConf #Linux #UAT10147 #QTFY #Gitea #GitLab

This week the pattern was speed: disclosure and exploitation collapsed into the same window, and attackers outpaced patch cycles across enterprise, open-source, and AI infrastructure alike, from federal catalog additions to a Mirai-bred botnet and an AI-orchestrated intrusion campaign.
𝗔 𝗳𝗲𝘄 𝗵𝗶𝗴𝗵𝗹𝗶𝗴𝗵𝘁𝘀 𝗳𝗿𝗼𝗺 𝘁𝗵𝗲 𝘄𝗲𝗲𝗸:
🔹6 new CISA KEV entries: MLflow, Apple macOS, two from Microsoft, Broadcom VMware, and Ray Project spanning AI tooling, operating systems, virtualization, and distributed compute
🔹Active exploitation beyond KEV across Citrix NetScaler, the User Profile Builder WordPress plugin, SAP Commerce Cloud, New API, and Zimbra, several within days, some within hours, of disclosure
🔹Evooo1Bot, a Mirai-derived Linux botnet, turning internet-facing edge devices into stealthy proxy relays and DDoS nodes
🔹knaithe (KnYuan), a Chinese-speaking actor, pairing autonomous AI-driven attacks with hands-on manual exploitation
The disclosure-to-exploitation window has effectively closed.
Full breakdown in this week's LOVI report:loginsoft.com/reports/weekly…
#Cybersecurity #LOVI #ZeroDay #CISAKEV #Ransomware #MLflow #Apple #Microsoft #VMware #Citrix #SAP #Zimbra #Mirai #AIsecurity #ThreatIntel
