

Tech Journalism with zero ads, & zero Big Tech influence. We cover the Big Tech stories that other publications are afraid to touch.
Joined July 2021
- Tweets10K
- Following682
- Followers39.3K
- Likes48.5K




With the PHP security news, it's worth taking a moment to look at the current leadership of PHP.
The Executive Director of the PHP Foundation, Elizabeth Barron (Naramore), has built a career on pushing DEI and Leftist politics in software.
- Worked on "Code of Conduct" and "Developer Inclusion" at GitHub.
- Cofounded a "women and non-binary individuals" PHP organization.
- Worked at The Linux Foundation (CHAOSS) where she wrote a "2021 DEI Audit".
- Her X bio used to read: "DEI in Open Source".
- Regularly posted anti-Trump, anti-MAGA, anti-White, and pro-Baby Murder statements on her @ElizabethN account.
Since becoming the PHP Executive Director she has:
- Started an "Accessibility & Inclusion group".
- Started an initiative to onboard "marginalized and underrepresented groups".


LCOS 0.9.5 Has Landed!
Fixes! More hardware support! 1.0 arrives Nov 1st!
lunduke.com/lcos.html

Indian Root Certificate Authority Sets Private Key to 4
Anyone has been able to make fake HTTPS certificates for over a year.
Many years back, I made a statement that “HTTPS is dangerous” due to significant, and obvious, problems in the design of the Certificate Authority system.
The core point I made: A small, simple mistake with a Root Certificate Authority has massive impacts throughout the system, making it highly likely that there were untold numbers of “fake” certificates which were “trusted”.
It is a “security based on trust” system, where we are asked to blindly trust dozens upon dozens of Root Certificate Authority organizations (from countries around the world) to never make a single mistake (or implement any backdoors for any government they are beholden to).
It is, quite simply, a design that appears specifically made to be abused and manipulated.
I was told that I did not understand how CA’s work.
I was mocked and ridiculed.
Well… as a wise man once said…
Who’s laughing now, Wayne?!
In April of 2025, eMudhra (an Indian Certificate Authority), published 8 intermediate CA keys which were so weak that a small child could guess the numbers in a few seconds.
One of the private keys was, literally, 4.
Just… 4.
This massive problem was not made public until October 17th of this year, when it was discovered by an anonymous guy on the Internet who goes only by “Wayne” (like “Cher”…. but… “Wayne”).
What this means in practical terms: It has been trivially simple, for the last year and a half, to create fake “secure” HTTPS certificates. (One person even created a fake HTTPS certificate for a Google.com subdomain.)
It took Mozilla 3 days, after learning about this (from “Wayne”), before they updated their certificate list (which many open source projects — including curl and Python — rely upon).
As of this moment, many systems are still vulnerable (including macOS).


The progress the @omarchy crew is making in adding hardware support is astoundingly impressive. Latest Apple Silicon Mac Mini is now booting Linux.


In April of 2025, eMudhra (an Indian Certificate Authority), published 8 intermediate CA keys which were so weak that a small child could guess the numbers in a few seconds.
One of the private keys was, literally, 4.
Just… 4.
This massive problem was not made public until October 17th of this year, when it was discovered by an anonymous guy on the Internet who goes only by “Wayne” (like “Cher”…. but… “Wayne”).
What this means in practical terms: It has been trivially simple, for the last year and a half, to create fake “secure” HTTPS certificates. (One person even created a fake HTTPS certificate for a Google.com subdomain.)
It took Mozilla 3 days, after learning about this (from “Wayne”), before they updated their certificate list (which many open source projects — including curl and Python — rely upon).
As of this moment, many systems are still vulnerable (including macOS).
FOSDEM (the largest Open Source conference in Europe) has rejected a proposed “DEI Devroom”… and the Leftists of Open Source are furious.
Within moments of the announced rejection, the attacks began to fly. Angry Leftists hurled nearly every attack in their arsenal at FOSDEM (which saw over 10,000 attendees in 2026).
“Fascists!”
“Appease Trump!”
“Part of the problem!”
“Genocide-complicit!”
“Slop!”
These attacks are still ramping up, supported by leadership of several Open Source organizations (including, as expected, GNOME).


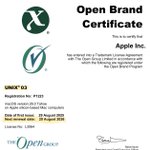
Apple’s macOS is no longer UNIX… officially.
It would appear that Apple did not renew their UNIX certification (from the Open Group) when it expired back on August 29th.
As a result, macOS has been removed from the list of “UNIX Certified Products”.
At this point it remains unclear if Apple not renewing UNIX certification was intentional, or an oversight.


As of 3 hours ago, the Linux Kernel no longer requires the usage of AI to be declared for new code submissions.

LCOS 0.9.5 has landed! (Only 12 days until 1.0!)
The following fixes have been added since the 0.9.4 update:
- Hardware support improved for built-in touchpads on some MacBook models, ExpressCards & some eSATA devices.
- Fixed issue where closing the lid on some laptops would not properly suspend.
- Improved support for wireless printers.
- Fixes for dual booting.
- Minor fixes to Lunduke Paint, Lunduke Edit, Updates, and Lunduke City.
- Visual fixes for boot menu under some configurations.
ISO download:
github.com/BryanLunduke/LCOS…
Users of the previous 0.9 releases can update to 0.9.5.

GNOME Founder Attacks Omarchy Founder as "Lazy, Racist, Ignorant"
Plus: Red Hat spokesman calls for impeachment of President Trump and to "fight the far-right extremist" Elon Musk.
Lifetime Sub Sale, Plus Your Name on the LCOS About Window: lunduke.substack.com/p/lifet…
A Python Software Foundation Fellow, and developer of the popular “Twisted” Python networking framework, says that Linus Torvalds’ “delusional and antisocial behavior” (aka “advocating for AI usage”) has “provoked a wave of revulsion” causing people to stop updating their Linux systems.

“The only justified police shooting is when they accidentally shoot one of their own.”
This was just posted by Rich Felker, Linux Kernel maintainer and “musl” creator.

Congratulations to the @openbsd team on their 8.0 release!
Looks like 8.0 received tons of improvements to multiple hardware architectures, expanded and improved hibernate support, and a boatload of fixes.
Keep up the excellent work, OpenBSD!
openbsd.org/80.html

Hey, hey, hey! I don’t want to jinx anything, but it looks like both the memory leak and KVM are fixed in Grok Bot!
Thanks to the @Bot team for getting on top of this!
Time to put that shared computer through it’s paces and make sure everything is working again.
Heads up @Grok @Bot team:
There is an incredibly gnarly memory leak in the Grok Bot shared computer. The process “host-main.cjs” grows rapidly, eating up 14+ GB or RAM within minutes… rendering the shared computer unusable for most purposes (even after updates and restarts).
Also… nested KVM is broken. Which is also a big blocker.
Any idea what’s happening, @poteto? I assume your team is already aware, but figured I’d reach out just in case! (I also emailed the support bot.)
Keep up the great work, btw!
“If foreign courts decide to… try and get in our way, there will be a point at which we have to accept that we won’t be able to recover that money.”
– Dame Melanie Dawes, Chief Executive, Ofcom
In other words: The UK is begrudgingly admitting that they lost the Revolutionary War, and that the USA is not under their control.

Ofcom Concedes Defeat in the 4chan Case
prestonbyrne.com/2026/10/20/…

As a general rule, the long-time (decades+) Linux kernel contributors and maintainers (Linus, Greg-KH, etc.) have embraced AI development of the kernel.
The people who have objected to AI contributions to the kernel, on the other hand, tend to be newcomers (comparatively).
There’s exceptions on both sides of the argument, but that generally seems to hold true.
