

Fighting the good Cyber fight and helping to protect our customers. Opinions expressed are my own.
Joined October 2019
- Tweets717
- Following95
- Followers499
- Likes1.2K




Your double-take attention please: *5* October revision to Exchange guidance msrc-blog.microsoft.com/2022…

Your attention please: 4 October revision to Exchange guidance msrc-blog.microsoft.com/2022…

Elizabeth Tyler retweeted

33 DaysToGo - If Basic Auth remains enabled in your tenant, your data is at risk, and so your role is to get your clients and apps off Basic Auth, move them to stronger and better options, and then secure your tenant, before we do.
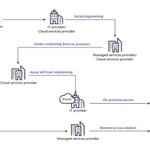
NOBELIUM are at it again. Or maybe they never stopped.
microsoft.com/security/blog/…
The bigger the org is, the slower it can be to respond but some excellent work was done on a US holiday to get this out to our customers #follina
msrc-blog.microsoft.com/2022…
msrc.microsoft.com/update-gu…
Spring4Shell has generated lots of questions.
There are detections and hunting to be done in this article. But overall the exploit attempts really are low


Microsoft is currently assessing the impact associated with the Spring Framework for Java vulnerabilities. Sharing our analysis and guidance here: microsoft.com/security/blog/…

Enabled MFA? Yay! But threat actors who get past the first gate can wear down users with MFA requests. Expose it for where it’s from docs.microsoft.com/en-us/azu…

Please read this one, I know folks have wanted to know what’s happening with Microsoft and lapsus$ microsoft.com/security/blog/…
Just how do you get into a container? How do you troubleshoot apps running in containers? No RDP here. It's more like Server Core only it's not. You'll get the idea.
techcommunity.microsoft.com/…

Fun things to do in your spare time! This is legit from someone that doesn't know the meaning of the words "I know enough"
This quoted post is unavailable.
Actionable info released quarterly news.microsoft.com/cyber-sig…


User has access. But how long should user keep that access? What if their account is revoked/deleted, pwd changes, their location changes or their risk level increases? Continuous Access Evaluation in AAD is now enabled for all tenants techcommunity.microsoft.com/…
Elizabeth Tyler retweeted

We have observed a China-based ransomware operator that we’re tracking as DEV-0401 exploiting the CVE-2021-44228 vulnerability in Log4j 2 (aka #log4shell) targeting internet-facing systems running VMWare Horizon. microsoft.com/security/blog/…
On prem AD needs basic checks done every so often. CE Paul Harrison came up with some great PS scripts to to monitor known problems like any forgotten computers in the Computers container: techcommunity.microsoft.com/…

Betty White, Y2K22, it better get better from here. 2010 and 2013 unaffected, 2016 and 2019 you have some work this morning (remember this is On Prem only)
techcommunity.microsoft.com/…

Elizabeth Tyler retweeted

Azure AD Password Protection provides coverage for this as well as character substitution (P@ssw0rd is normalized to password)
It also prevents admins from setting or resetting passwords to known bad/weak passwords
If you have Azure AD P1+, check it out:
docs.microsoft.com/en-us/azu…

Keyboard walking or pattern passwords are easily guessed. Attackers include these types of password since admins use them (they certainly look random and complex) and are often used as service account passwords.
Image reference article: wpengine.com/resources/passw…

Lots of contentious topics for the holiday dinner table but here's a good thing to share
haveibeenpwned.com/Passwords
The UK National Crime Agency has share 585 million compromised passwords with haveibeenpwned
therecord.media/the-nca-shar…
Did you apply the November patches? Cause a PoC is out . These 2 are for your DC's, CVE-2021-42287 and CVE-2021-42278. Explanation of these and how to identify potentially compromised systems in this excellent article
techcommunity.microsoft.com/…