

I break down how software, AI, and systems actually work. Real-world failures, architecture, and security insights.
Space & Sounds
Joined September 2022
- Tweets719
- Following182
- Followers156
- Likes2.4K






Professeur | AI, Systems & Security retweeted
Anthropic added invisible watermarks to Claude text.
Someone built a remover the same day.
The watermark was supposed to survive copy-paste and light edits.
The remover kills it entirely.
Anthropic complied with EU regulations.
Someone complied with market forces.
The watermark lasted eight hours before someone shipped a tool that defeats it.
The detection mechanism Anthropic promised hasn't shipped yet.
The removal tool already has.
This is how regulation works in 2026.
Government mandates invisible mark. Company adds invisible mark. Someone builds tool to remove invisible mark.
All before lunch.

Claude can now watermark every sentence it writes.
Invisible. Travels with copy/paste. Survives light edits.
Introducing Claude Watermark Remover.
Paste Claude text. Kill the statistical mark. Keep the meaning.
Free. No signup. Built today after reading this @paulg post, shipping now.
claudewatermarkremover.app

Professeur | AI, Systems & Security retweeted
The surprising part isn't that software gets installed.
It's how it gets there...
A report circulating on X claims some LG UltraGear monitors trigger Windows to automatically download and install LG software as soon as the monitor is connected.
No installer.
No website.


Professeur | AI, Systems & Security retweeted

77 million women use Flo to track their periods, cycles, ovulation, and pregnancies.
here's what Flo actually collects:
your menstrual cycle details. pregnancy information. symptoms. details about your sex life. physical and mental health. weight, height, BMI, body temperature. sleep. water intake. location. IP address. device ID. every time you open the app.
if you connected Flo to Apple Health or Google Health Connect: heart rate. calories burned. fitness activities. body temperature. steps taken.
all of it. automatically imported.
now here's the funniest part:
by using the product you consent to Flo sharing your data. you don't tick a separate consent box. you just use the app. that's the consent.
and in the Terms of Service:
by adding any information to Flo your period dates, your symptoms, your notes you grant Flo a non-exclusive, transferable, sublicensable, worldwide, royalty-free licence to use, copy, modify, distribute, and create derivative works from that content in any way they deem appropriate.
your most intimate health data. royalty-free. worldwide. sublicensable.
Flo shares data with TikTok Ad Manager, AppsFlyer, Firebase, and 20+ subprocessors including Tecton machine learning company that powers cycle predictions.
in 2022 Flo settled with the FTC for $59.5 million after allegations they shared user health data with Facebook and Google between 2016 and 2019. they denied wrongdoing.
if you deleted the app without deleting your account first: your data is retained for 3 years.
Have a read below:

Article #21 in my 'I Read The Policies So You Don't Have To' Series;
Flo App (Period, Ovulation & Pregnancy Tracking)
medium.com/@ItsNotNicole/i-r…


Professeur | AI, Systems & Security retweeted

YOU CAN BREATH OXYGEN, DRINK WATER
YOU CAN BREATHE OXYGEN, DEINK WATER
YOU CAN DRINK OXYGEN, BREATHE WATER

Professeur | AI, Systems & Security retweeted
The advice is NOT WRONG. The framing leaves out the most important context.
Without a VPN your ISP sees every DNS query you make. Every domain you visit, timestamped and logged. They see the IP addresses your device connects to. They see the volume of traffic, the timing, and the duration of every session. On unencrypted HTTP they see the full content of everything.
What they cannot see on HTTPS is the content. The actual data exchanged between you and a website using HTTPS is encrypted at the TLS layer. Your ISP cannot read your messages, your search queries, your banking details, or the body of any page you visit over HTTPS. That encryption exists regardless of whether you use a VPN.
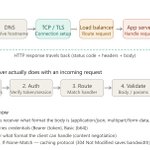
What HTTPS does not hide is the domain name itself. SNI, Server Name Indication, sends the hostname you are connecting to in plaintext during the TLS handshake so the server knows which certificate to present. Your ISP sees that you visited a domain even when they cannot read what you did there. ECH, Encrypted Client Hello, is a newer standard that fixes this but adoption is still limited.
A VPN shifts that visibility from your ISP to the VPN provider. Your ISP now sees encrypted traffic going to one IP address. The VPN provider sees everything your ISP previously saw. You traded one observer for another.
The accurate picture is this. HTTPS already protects your content from ISP surveillance. A VPN additionally hides the domains you visit and your traffic patterns. Both together provide meaningful privacy. Neither provides anonymity.
The missing variable in most VPN marketing is who you are now trusting instead.
Professeur | AI, Systems & Security retweeted
Partially true, but mostly misunderstood.
what your ISP can actually see
Since HTTPS became standard, your ISP can see DNS queries and domain names. not page content, not passwords, not what you searched. they know you visited reddit[.]com at 11pm. they don't know what you read.
what they can sell: your browsing metadata. which sites you visit, how often, for how long. Since 2017, US ISPs can sell this without consent. it's valuable to advertisers.
what a VPN actually does
encrypts traffic between your device and the VPN server. hides your DNS queries and domain visits from your ISP. replaces your IP address with the VPN's.
BUT, the VPN now sees everything your ISP did.
Most VPN "no-log" claims are unverified. NordVPN was breached in 2018 and stayed silent for 18 months. IPVanish handed user logs to the FBI despite claiming to keep none. Hola VPN sold user bandwidth to a botnet. PureVPN provided connection logs to the FBI and so on...
The top-ranked VPN review sites are almost entirely driven by affiliate marketing or owned by these VPN companies themselves!. Vpnmentor and the likes...
When a VPN is actually useful:
— public Wi-Fi: yes. Encrypts your traffic from the network.
— hiding activity from your ISP specifically: yes, with a trustworthy provider.
— bypassing geo-restrictions: yes.
— stopping Google, Meta, or advertisers from tracking you: NO.
— protecting you from spyware or government access: NO.
VPN doesn't solve the problem most people think they're buying it for.
Professeur | AI, Systems & Security retweeted

If you're thinking about getting a VPN. Here's how to pick one that doesn't make things worse.
Avoid:
— free VPNs. if you're not paying, your traffic is the product.
— VPNs with no published audit. Claims mean nothing. Third-party audits mean something.
— VPNs recommended in sponsored YouTube videos or affiliate review sites.
Look for:
— independently audited no-log policy. Mullvad have both been audited multiple times.
— open-source clients. you can verify what the app actually does.
— WireGuard protocol. faster, leaner, more auditable than OpenVPN.
— jurisdiction outside Five Eyes countries. Mullvad is Swedish. Proton is Swiss.
best options:
Mullvad(@mullvadnet): $5/month. accepts cash. no email required to sign up. strongest privacy posture of any commercial VPN.
ProtonVPN(@ProtonVPN): Swiss-based. free tier available. open source. audited.
Windscribe(@windscribe): Feature-rich (R.O.B.E.R.T. blocker, split tunneling, proxies), audited no-logs, generous free tier (10GB+), customizable plans, good speeds.
Remember:
A VPN protects you from your ISP and from network-level snooping.
It does not protect you from Google, Meta, browser fingerprinting, device-level spyware, or physical surveillance.
use it for what it does.
not for what the ad says it does.
Professeur | AI, Systems & Security retweeted

your AI designed website looks.. sloppy??
it's easy to fix it
Professeur | AI, Systems & Security retweeted

Every time you visit a website, you're probably asked to "Accept Cookies." But what are you actually agreeing to?
Most people assume cookies exist to collect and sell their data.
The reality is a bit more nuanced.
A cookie is a small text file that a website stores in your browser. Think of it as the website leaving itself a note so it can remember information about your visit.
For example, cookies can remember:
That you're already logged in, so you don't have to sign in on every page.
Your language or region preference.
The items in your shopping cart.
Whether you prefer light or dark mode.
Without these cookies, many websites would feel frustrating to use. Imagine logging into your email, opening another page, and being asked to sign in again every single time.
That's where cookies help.
Why do websites ask for permission?
Not all cookies serve the same purpose.
Essential cookies are necessary for a website to function. They keep you logged in, maintain your session, and support core features. In many regions, these don't require consent because the site can't operate properly without them.
Analytics cookies help website owners understand how people use their site. They can show information like:
How many visitors the site receives.
Which pages are the most popular.
How long people stay.
Whether visitors are using a phone or a computer.
This data is usually aggregated and helps improve the website.
Then there are advertising or tracking cookies.
These can follow your activity across multiple websites to build a profile of your interests, allowing advertisers to show you more relevant ads.
For example, if you search for running shoes on one website and then start seeing shoe ads on other websites, tracking cookies may be part of the reason.
Do websites actually sell your data?
Sometimes—but not always.
Many websites don't literally sell your personal information.
Instead, they may share certain data with advertising networks or analytics providers, who use it to personalize ads, measure campaign performance, or better understand user behavior.
Whether your data is collected, shared, or sold depends on the website, its business model, and its privacy policy.
What happens if you reject cookies?
In most cases, the website will still work because it relies on essential cookies.
However, you may lose conveniences such as staying logged in, receiving personalized recommendations, or having your preferences remembered between visits.
The bottom line
Cookies aren't inherently good or bad.
They're simply a technology that helps websites remember information.
Some are essential for the web to function smoothly.
Others are designed to measure usage or personalize advertising.
Understanding the difference helps you make informed decisions instead of automatically clicking "Accept All" or "Reject All" without knowing what either option means.

Professeur | AI, Systems & Security retweeted
Italy fined Character.AI for failing to protect children
Character.AI got fined €158,000 by Italy for not verifying user ages and leaving children exposed to an AI chatbot platform with zero safeguards
The company didn't check who was using the service. Didn't implement protections for minors. Just let kids interact with AI designed for unrestricted conversation
Italy's regulators looked at it and said: you let children into a system built for adults, with no guardrails, no verification, no accountability.
Character.AI's response: a fine they'll absorb in a week
The real problem isn't the penalty. It's that companies know the EU will fine them eventually, but the fine is just a cost of business. Cheaper than implementing actual safety measures.
So they don't
They'll keep shipping products aimed at kids with parent verification that's theater. With age gates that don't work With moderation that doesn't happen
Because €158,000 is nothing compared to the value of unfiltered user data
Italy proved it's willing to act. But fines alone won't change behavior. Only when the cost of negligence exceeds the profit from negligence will companies care
Sadly we're not there yet

Professeur | AI, Systems & Security retweeted
Italy just fined Character[.]AI €158,000 for age-check failures.
Character AI allows users to create and interact with AI personas. some of those personas are explicitly romantic. some are designed to simulate relationships. the platform has no meaningful age gate. a child can sign up with a fake birthdate and immediately access content designed for adults.
Italy's data protection authority found three specific violations:
— inadequate age verification
— insufficient protections for minor users
— failure to comply with GDPR obligations around children's data
this isn't the first action against Character AI. the FTC is investigating. there are active lawsuits in the US including cases involving the deaths of Sewell Setzer III, 14, and Juliana Peralta, 13. a Texas judge refused to dismiss a wrongful death case in April 2026.
Character[.]AI has introduced age restrictions, content filters for under-18 accounts, and pop-up mental health resources since the lawsuits began.
Italy is the first country to formally fine them.
Professeur | AI, Systems & Security retweeted
META JUST FILED PAPERWORK FOR AN AI THAT LOGS HOW YOU FEEL, ALL DAY, TIED TO WHERE YOU WERE AND WHAT YOU WERE DOING.
READ THAT AGAIN.
A device that logs your sighs and cross-references them with your location and medication schedule, justified as a workout app.
These companies won't rest until we're all living in a dystopian cyberpunk society where they control and track everything.
Meta's at it again. The patent, filed December 2025 and published July 2, 2026, describes a wearable that continuously records your voice and surroundings.
An AI model analyzes sighs, laughter, tone, pacing, all of it, to infer your emotional state.
Then it correlates that mood data with your location, the time of day, what objects are around you, and even when you take your medication.
The stated reason: better fitness coaching. Personalized workouts, pose correction, that kind of thing.
It doesn't stop at raw data either. The system generates periodic reports summarizing your emotional trends, citing specific recorded moments as "evidence" of how you felt.
Meta's response: patents get filed all the time and don't guarantee a product ships.
Sure. But the same company already ran a study in 2012 manipulating 700,000 users' emotions through their news feed, without telling them. This isn't a company earning the benefit of the doubt on emotional data.
Fitness coaching doesn't need to know when you take your pills. It doesn't need your location history. It doesn't need a permanent audio record of every sigh you let out today.
That's not a feature. That's a surveillance architecture wearing a fitness tracker as a disguise. And at this point, it's less a plot twist and more Meta's entire brand.

Professeur | AI, Systems & Security retweeted

Grok 4.5 is the truth seeking leader that other AIs can aspire to become

Professeur | AI, Systems & Security retweeted
It’s all about how strict you want to be with updates!
— ^4.21.2 (Caret) = Give me new features & bug fixes (i.e., stops before v5.0.0)
— ~4.21.2 (Tilde) = Safety first! Only give me tiny bug fixes (i.e. stops before v4.22.0)
— No symbol = Lock it down to this exact version!
Professeur | AI, Systems & Security retweeted

Professeur | AI, Systems & Security retweeted

X App (Formerly Twitter), Acquired by xAI, a Product by SpaceXAI, a division of SpaceX
Professeur | AI, Systems & Security retweeted
Apple just sued OpenAI for systematically stealing its trade secrets.
Tang Tan — 24-year Apple veteran. VP of product design for iPhone and Apple Watch. left in 2024. co-founded io Products with Jony Ive. OpenAI bought it for $6.5 billion. now OpenAI's Chief Hardware Officer.
Chang Liu — 8 years at Apple. left for OpenAI in January 2026. kept his Apple laptop.
What happened:
Tan turned job interviews into intelligence operations. Apple employees still on payroll were asked to bring actual hardware batteries and logic boards to OpenAI for "show and tell." One candidate said he "didn't even know we could take those from the office."
Tan circulated Apple's own internal exit security protocol to coach new OpenAI hires on how to evade it. he told them not to tell Apple they'd accepted jobs at OpenAI so they could stay as long as possible.
Liu kept his Apple laptop after quitting. found a bug that still gave him cloud access. downloaded dozens of confidential files. labeled confidential. while already at OpenAI.
one candidate took a screenshot of confidential Apple project files hours before their OpenAI interview. Tan then asked about that exact project.
For context... two years ago Apple and OpenAI were partners. ChatGPT in Siri. Altman at Apple HQ. Cook and Altman at a White House dinner together.
Now Apple just replaced Siri with Google Gemini.
And Apple is suing OpenAI.
Apple flagged everything in February. sent a letter. asked OpenAI to investigate. never got a response. five months later: lawsuit.
what Apple wants:
full discovery into OpenAI's hardware operation. right before the device launch. right before the IPO. if granted, OpenAI may have to prove its device was built clean, component by component, before it ships.
Apple called OpenAI's hardware business "rotten to its core."
OpenAI: "we have no interest in other companies' trade secrets."
400 former Apple employees work at OpenAI.
only two are named.
Apple says this is "the tip of the iceberg."
