



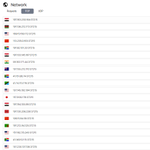


#Mirai #C2 domains are using Round-Robin DNS to resolve to multiple hosts
Using "Resolve-DnsName" in PowerShell we can resolve the domains to their corresponding IPs.
Ports used for Mirai connection: 1337, 2222, 2474, 5555, 6969, 8745, 8932, 12381
IOCs: threatfox.abuse.ch/browse/ta…


Distribution domain queries for #RobotDropper on @ValidinLLC and @censysio
Validin: RapidShare - Fast & Secure File Transfer for Free
Censys: services.http.response.html_title="RapidShare - Fast & Secure File Transfer for Free"
IOCs shared on ThreatFox: threatfox.abuse.ch/browse/ta…


💢 Low-Detection MSI Dropper Delivers #Malware – #ExploreWithANYRUN
⚠️ A recently developed #dropper is an #MSI file containing a #password-protected RAR archive
📌 Both the sample and #C2 domains have a very low detection rate on #VirusTotal
🔗 virustotal.com/gui/domain/ge…
📤 The dropper sends requests to the get-license4[.]com and get-license2[.]com resources, with the example of the following content:
IsICS=0&LangCode=5875&AwaitTmp=17&Kiid=81257
⚙️ After execution, it asks the user to confirm that they are not a robot by clicking the "OK" button. It then displays the 'Sending collected data' message
📝 Now the server’s returning only the '0a' string. It may be intended to return the password for its content
🤖 We named it #RobotDropper because it requires the user to confirm that they are human
👉 app.any.run/tasks/9e428266-9…
We've observed it dropping #Lumma and #Stealc:
👉 app.any.run/tasks/185bc3b0-1…
Find more samples by these #TILookup requests:
👉 intelligence.any.run/analysi…
👉 intelligence.any.run/analysi…
🐼 Special thanks to @RussianPanda9xx for providing the initial sample in her tweet!
Analyze and investigate the latest #malware and #phishing threats with #ANYRUN 🛡️

#Censys query to find #GossRAT #C2 servers:
services.http.response.body_hash="sha1:b7c4a3bf814a5aaf96e208f47a17066c32ac0ad0"
The URL path used for C2 communication is the same across all domains > /rat/apps/mellat/notify.php
IOCs: threatfox.abuse.ch/browse/ta…
#IOC #IRATA #GossRAT


Iranian threat actors are using phishing sites that impersonate @mellatbankiran to distribute #GossRAT through a download page claiming to be the bank's mobile app.
Using @censysio DNS records i found over 100 domains to have been involved, most of them using .buzz as their TLD.

ALT Fake site targeting Mellat Bank.


Iranian threat actors are using phishing sites that impersonate @mellatbankiran to distribute #GossRAT through a download page claiming to be the bank's mobile app.
Using @censysio DNS records i found over 100 domains to have been involved, most of them using .buzz as their TLD.
ALT Fake site targeting Mellat Bank.
As for now, the 10 active domains are delivering the same #GossRAT payload.
URLhaus: urlhaus.abuse.ch/browse/tag/…
Mellat.apk: bazaar.abuse.ch/sample/b97df…
1
3
374
#GuLoader #opendir
hXXps://www.pineappletech.ae/at/
at.vbs: joesandbox.com/analysis/1468…
#Rhadamanthys ?
#Stealer

teapaw.org/NDA0E/status/180897721…
Search using @urlscanio
filename: "interpol.mp4" AND filename:"country.json" 🔥
+ cancel-service[.]info
teapaw.org/spamhaus/status/180887…
I have identified eight more domains targeting Russian individuals.
cyber-eu[.]info
cyber-payback[.]info
get-return[.]com
global-refund[.]digital
inter-return[.]com
internet-cyberpolice[.]network
payback-int[.]com
refund-service[.]digital
1
2
375
teapaw.org/spamhaus/status/180887…
I have identified eight more domains targeting Russian individuals.
cyber-eu[.]info
cyber-payback[.]info
get-return[.]com
global-refund[.]digital
inter-return[.]com
internet-cyberpolice[.]network
payback-int[.]com
refund-service[.]digital

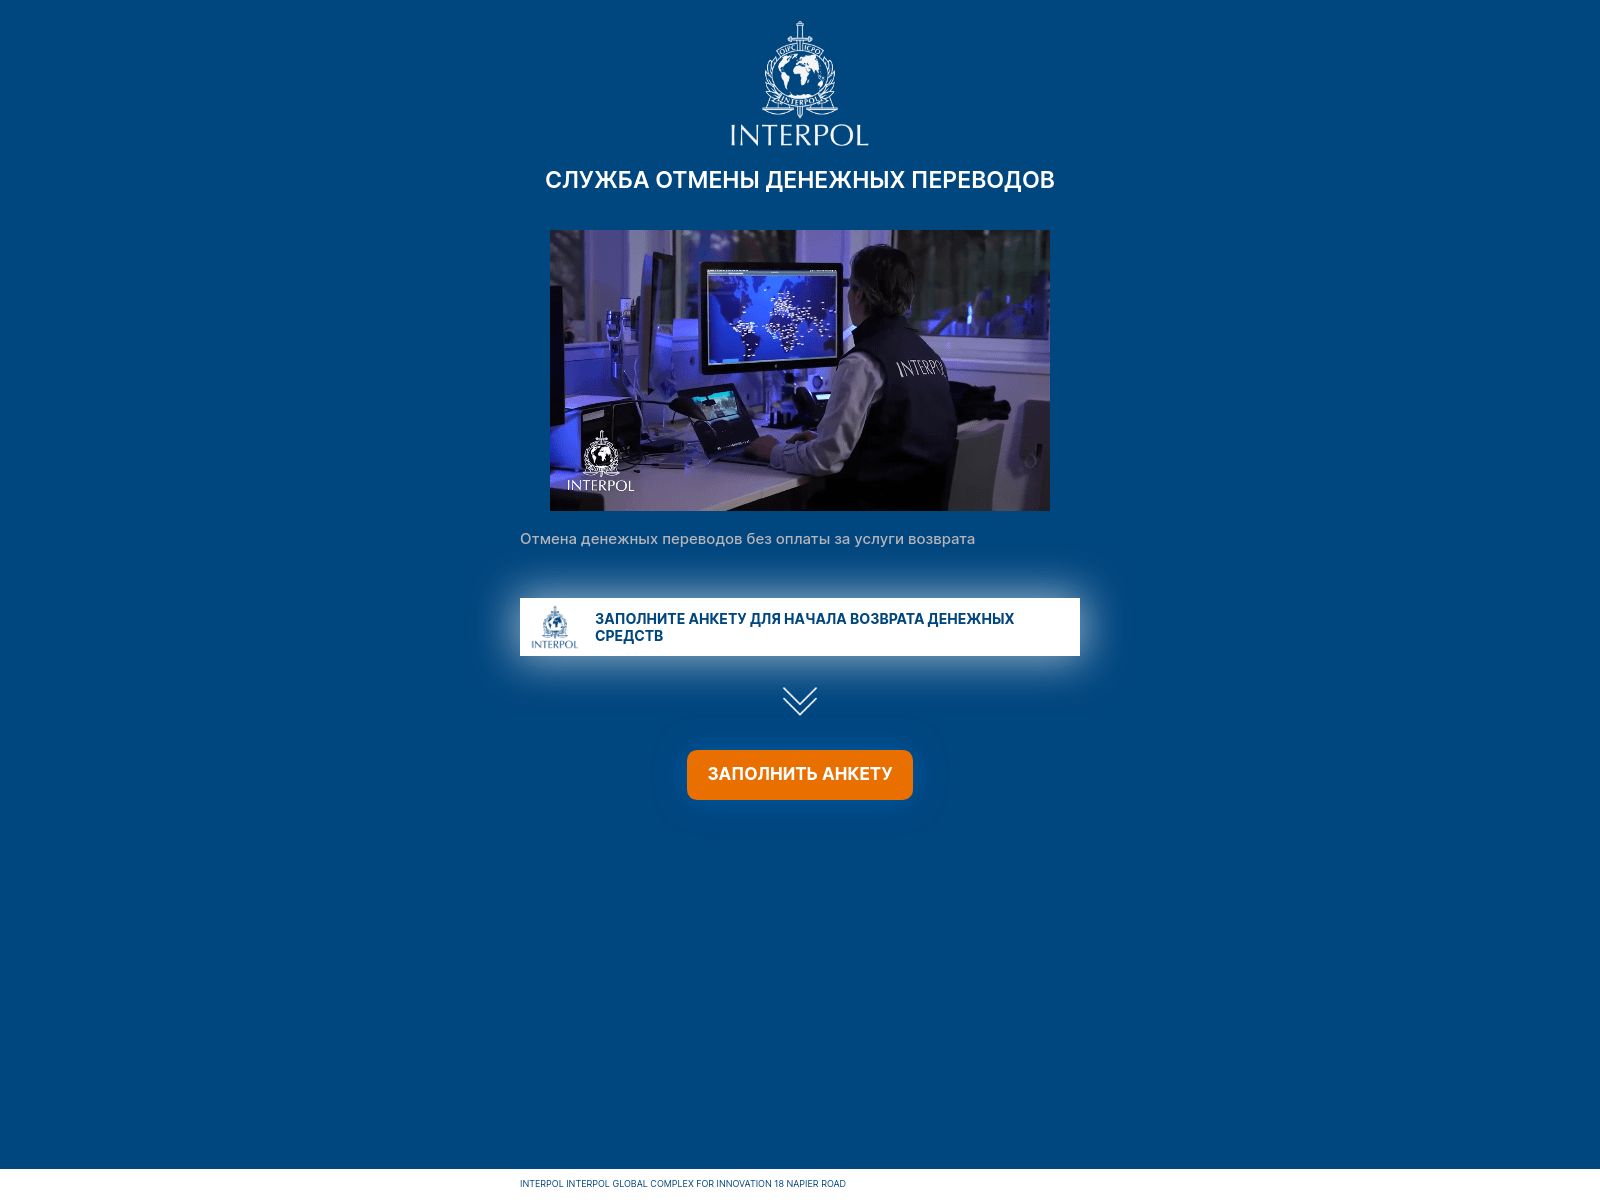
🕵Spamhaus researchers have observed a phishing scam imitating @Interpol - the International Criminal Police Organization.
Scammers are using @instagram, @facebook, @Messenger and @Meta Audience Network to carry out their malicious activity, luring people with slick videos and directing them to a domain, "int-returnback[.]com."
One telltale sign of this suspicious activity is the presence of a more "official" logo. And there's more....🔽


teapaw.org/NDA0E/status/180131007…
Same stealer, different Alias.
Distribution site: rblxshaders[.]com
C2 endpoints:
https://bettershaders[.]xyz/autofill
https://bettershaders[.]xyz/passwords
https://bettershaders[.]xyz/creditcards
https://bettershaders[.]xyz/webhooks
#PhxiStealer #IOC


Crunexy Stealer
C2: shaderify[.]xyz
Distribution site: shaderify[.]com
Web download > Shaderify_Beta.rar > ShaderifyBeta 1.4.0.exe
Shaderify_Beta.rar
03751e8ea2f5db0fe27e1f2bcba62762
ShaderifyBeta 1.4.0.exe
4200f0d5579cdf7a6e27f1fff4b661e0
#Crunexy #Stealer


6
3
404


File hosting C2: api[.]ilovecats[.]life
Uploads: Autofills.txt, Passwords.txt, CreditCards.txt, Exodus.zip, FileZilla.zip and All.zip
Then sends direct download URLs to a discord webhook.
Forwarded via: https://20.199.87.174/dcpost/

1
1
78
Duvet Stealer
C2: malivscute[.]lol
Web download > Farmcoz.rar > Farmcoz.exe
Farmcoz.rar
2913deb536de1ac0f1cfcda8c8b67496
Farmcoz.exe
620cac4efbda12399c6b88a308f4225e
#IOC #DuvetStealer

2
2
211

teapaw.org/banthisguy9349/status/…
IP back up now hosting "conf.txt"
http://91.92.242.200/conf.txt
Reversed base64 and hex encoded exe > decoded: virustotal.com/gui/file/5001…


Here are some #PowerShellEmpire IOCs: pastebin.com/raw/6PTTM4MD
ThreatFox: threatfox.abuse.ch/browse/ta…


#opendir #DBatLoader #XWorm #RemcosRAT
144.126.134.25:5000
144.126.134.25:8080 #AS40021 @ContaboCom
climb-items-macedonia-hometown.trycloudflare[.]com
climb-items-macedonia-hometown.trycloudflare[.]com:8080
Full list: paste.ee/r/wD2MX/0


2
255

Found origin IP used to host #WaveStealer #C2 wavebysudryez[.]fr:
45[.]145[.]166[.]210 #AS207992 @FeelB_SARL @hexanode
Any abuse reports sent to abuse@feelb.]fr would be appreciated.

1
7
178