

Pentesting | Red Teaming Game Hacking | Anti Cheat
Deutschland
Joined July 2019
- Tweets178
- Following418
- Followers262
- Likes315





Pinned Tweet
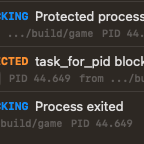
My macOS anti-cheat is coming together. With the APIs of a Security Extension, I have a stable way (no kernel extension) to monitor cheating TTPs and report them securely to a backend. I built it game-agnostic, so it works everywhere. Finally a solid anti-cheat for macOS :D


Patchi/fyi retweeted

Make your payload "sleep" to look like any real Windows activity.
BusyWork is a Rust library that swaps each pause for randomized real work - hashing, file enumeration, registry queries, DNS lookups - drawn from 76 tasks across seven categories with ±30% jitter on every parameter.
No two "pauses" produce the same API sequence, and no timing primitives survive in the compiled binary.
A post by Daniel (@PatchRequest)
Source: patchi.fyi/blog/busywork-sle…
#redteam #blueteam

Just a horse game or malware? A friend got invited to a private Star Stable Online server, via a Tor onion site serving an exe and a .hors file. Down the rabbit hole: NSIS installers, AES-256-GCM encrypted packages, DLL proxying, ECDSA-signed profiles:
patchi.fyi/blog/horse-empire…

EDR has the attention span of a toddler. If it doesn't see the exact pattern it was trained on (sleep, allocate, inject, sleep), it just moves on. Anything else between your calls and it forgets you exist. So I built a library that does exactly that
patchi.fyi/blog/busywork-sle…
New Rust lib drop🦀 Got tired of rewriting userland unhooking and direct/indirect syscalls from scratch for every project. So I built a lib that makes it dead simple: unhook a single syscall, rehook afterwards, or go fully indirect/direct with Halo’s Gate
patchi.fyi/blog/callghost-di…

Updated my DLL proxy framework. It now clones the metadata and signature from the original onto the proxy. Properties show the same company, description, and signer, so sideloading is harder to spot. Looks just like the real thing, just a hash mismatch :)
patchi.fyi/blog/dll-proxy-me…

Patchi/fyi retweeted

Whipped up a standalone wrapper for IDA free while waiting on batch analysis.
Thanks to @PatchRequest for the awesome idea!


Love the cat-and-mouse of game hacking. Had most DLL injection covered, but FakeVEH not yet fully. Now caught via a DR0 hardware breakpoint on LdrpVectorHandlerList, guarded by a watchdog that re-arms the DRs. Manual mapping was already detected anyways :D
patchi.fyi/blog/peregrine-fa…

unavailable
Tested it against my WIP macOS anti-cheat. Raw svc syscalls, hand-built MIG messages, zero library calls doesn't matter. Endpoint Security hooks sit in the kernel MACF layer. task_for_pid is caught regardless of how you call it. The tools are there ACs just aren't using them:


Game hacking is always about Windows, so I looked at macOS. Anti-cheats are severely capped there (no kernel drivers on Apple Silicon) while cheats can do wild stuff with raw Mach traps. Built a framework to explore this:
patchi.fyi/blog/carrot-cheat…
Started working on a macOS anti-cheat built on Apple's Endpoint Security framework. System Extension that blocks memory editors, cheat tools, debugger attachment, DYLD injection; all from user-space. No kernel extension needed. Very promising so far.

Game hacking is always about Windows, so I looked at macOS. Anti-cheats are severely capped there (no kernel drivers on Apple Silicon) while cheats can do wild stuff with raw Mach traps. Built a framework to explore this:
patchi.fyi/blog/carrot-cheat…
new passive blog entry:
patchi.fyi/blog/dll-proxy-fr…
took a technique i used in some cheats and turned it into a framework. point it at any DLL, it generates a full proxy project with assembly trampolines for every export. swap targets in seconds.
I tried starting a security blog like 5 times the past years.
never got past the first post.
So i built a passive blog. i throw my projects in, an LLM writes the posts. every code snippet from real repos, every claim sourced.
patchi.fyi
Continued working on my proof-of-concept anticheat.
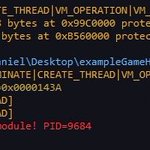
These are the events visible to an anticheat when you use default DLL injection; pretty obvious, I'd say :)
github.com/PatchRequest/Pere…

Just added self-clone to my Mythic agent: spawn new proc + spoofed PPID while original stays alive and running as backup
github.com/PatchRequest/Kass…

Just implemented self-deletion in my Mythic agent while the process keeps running smoothly.
Big thanks to @MalDevAcademy for the inspiration 🔥
github.com/PatchRequest/Kass…


Basic, but I guess effective enough to catch some script kiddies. I added a blacklist of words that should not appear in any running process. I think some cheaters actually get caught in the wild by this lol
github.com/PatchRequest/Pere…

I wanted to consume some ETW providers, but it turned out I needed to be a PPL. So thats a side quest I worked on for now. Not sure how useful this is for protecting the game, but the protection for my own usermode part should be useful for the anti-cheat
github.com/PatchRequest/Pere…

This is how the default settings of the @GuidedHacking injector currently appear in my anti-cheat.
You can clearly see the sequence:
WriteProcessMemory → DLL image load → new thread inside the newly loaded DLL.
github.com/PatchRequest/Pere…

