

Swarming adversarial AI agents delivering AGI-grade security for Web3 & AI systems || Building the trust layer for the open agentic web.
Joined July 2024
- Tweets2.4K
- Following76
- Followers5.8K
- Likes2.8K




People use ChatGPT to spot scams ~3x more than scammers use it.
Worth a skim if you care about AI x security:
cdn.openai.com/threat-intell…
A few bits that stood out:
-> Russian / Korean / Chinese-speaking crews using AI for debugging, translations, phishing copy, basic C2 tweaks.
-> Scam farms in Cambodia / Myanmar / Nigeria using it to churn cold DMs + fake “investment guru” personas.
Just went through OpenAI’s Oct 2025 report on “malicious use of AI”
Some takeways from that is bad actors aren’t inventing crazy new AI hacks. They’re mostly bolting models onto old playbooks (malware, scams, info ops) to move faster & make fewer mistakes.

{QuillAI Network} retweeted

Our Mandates SDK is finally out in typescript.
You can now now create mandates, sign them using EIP-191 signatures through client and server agents, and get them verified by our verification layer.
Gitbook, task primitives and integrations coming soon!
github.com/quillai-network/m…
Ship a fix → rerun the adversarial sim:
-> Did the path die?
-> Did the fix open something else?
-> Is your risk score trending down?
Now you’re doing continuous red-teaming, not one-time “security theater.”
This is why we call QuillShield “The Red Team Co-pilot of Web3”
If your own AI can’t break you after thousands of attacks,
good luck to everyone else.
Instead of generic “High severity bug” messages, QuillShield gives you:
-> Exact attack path (sequence of calls + parameters)
-> What the attacker gains (fund drain, stuck funds, privilege escalation)
-> Why it works (state condition or missing guard they exploit)
This makes it much easier for devs to understand, reproduce, and fix the issue.
This is where it gets fun.
You kick off an RL-based adversarial agent that behaves like a tireless attacker:
-> Tries thousands of call sequences
-> Chains functions in weird orders
-> Pushes edge cases on limits, balances, or roles
Instead of “does this function revert?”, it asks: “What sequence of actions would let me steal, freeze, or grief this protocol?”
Pick the contracts you want to harden:
-> Upload / link your smart contract repo
-> Select the core contracts (Vault, LendingPool, Router, etc.)
QuillShield maps out the attack surface: entrypoints, state variables, external calls.
Most teams still treat security like a final checkbox before mainnet.
We built QuillShield so security becomes a continuous adversarial game your own AI plays against you.
Here’s how teams use QuillShield as their Red Team Co-pilot of Web3 👇

QuillAI unites adversarial agents into a continuous swarm simulating exploits, scoring risk & deploying guardrails to protect users and smart contracts.
AI agents across the on-chain economy. You agree?
unavailable
Now it's time to Test & ship:
ngrok http 3000 → set NEXT_PUBLIC_URL → cast your frame (Use App).
Generate frame env: npx create-onchain --manifest. Prod: NETWORK=base, set CDP_API_KEY_ID/SECRET, prod wallet, plus rate limits, logs & server-side validation.c
For the full deep dive, hit Coinbase’s x402 Miniapps docs: docs.cdp.coinbase.com/x402/m…

Price per endpoint first, then graduate to unlock tiers.
1) $0.01 “action” routes
• /api/protected → micro-utilities, tipping, basic tools
2) $1.00 content gates
• /api/premium-content → longform, datasets, templates
3) $5.00 feature unlocks
• /api/exclusive-feature → pro tools, generators, bulk ops
Gate several endpoints at once or issue a “session pass” by checking a paid flag server-side for N minutes.
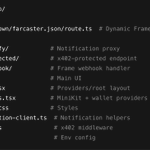
Understand the MiniApp structure & How it works. Like x402 gates server routes.
In middleware.ts price /api/protected (e.g. $0.01 on base-sepolia). Client wraps fetch with wrapFetchWithPayment; server verifies, Frame SDK enables miniapp UX.
Keep secrets in env + enforce the right chain.

Before you start, You’ll need :
• Node 18+ & pnpm 10+
• Wallet to receive funds
• (Mainnet) CDP keys
Do this :-
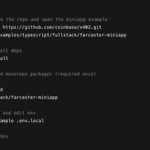
-> Clone & install the repo
-> Build the monorepo once
-> Copy & edit your workspace
-> Set env & run → open http://localhost:3000

Ever heard of Miniapps?
Miniapps are lightweight apps that run inside Farcaster clients (e.g., Warpcast, TBA). Built with MiniKit, they feel native while leveraging Farcaster’s social graph and the user’s connected wallet.
Now let’s ship one with in-flow USDC via x402 in under an hour. From “hello world” to paid features before your coffee cools.
Dive in 🧵

Glad to be the part of the Agent Consortium.
If Agents are where users meet AI, QuillAI is the crash-test + shield, adversarial swarms that harden users, contracts & agents before threats go live.
Let’s make “secure by default” the standard🔥

1/ Agent Consortium
these are the teams building the actual agents AI systems and apps that use sentient’s models and data in the real world
they’re basically the "frontline" of the ecosystem where users interact with AI
full list here↓
– @MessariCrypto
– @FTI_Global
– @KaitoAI
– @myshell_ai
– @thirdweb
– @TheoriqAI
– @qnaweb3
– @JoinPond
– @miranetwork
– @autonolas
– @BiconomyCom
– @Talus_Labs
– @ZettaBlockHQ
– @getaxal
– @MorpheusAIs
– @dFusionAI
– @exponentai
– @Fetch_ai
– @gizatechxyz
– @jus_txAI
– @UnifaiNetwork
– @questflow
– @QuillAI_Network
– @Raiinmakerapp
– @crunchDAO
– @Spectral_Labs
– @UomiNetwork
– @playAInetwork
these partners handle everything from AI-driven financial analytics (messari, franklin templeton) to agent frameworks (fetch AI, myshell)
they bring real-world utility and give sentient’s models a place to act

{QuillAI Network} retweeted

The world if SRs used @QuillAI_Network to find issues during their review.

