

Empowering CISOs to build cyber resilience through AI-native continuous offensive security.
Silicon Valley
Joined January 2020
- Tweets1.3K
- Following126
- Followers1.3K
- Likes46




🚨 When cyberattacks cross from IT into physical infrastructure, seconds and fail-safes make all the difference.
Recently, attackers targeted the refrigeration controls across three facilities of France’s national blood service. Temperature and defrost thresholds for plasma storage units (normally maintained near -30°C) were maliciously altered via remote-monitoring software to extreme setpoints.
Thanks to independent monitoring systems and swift overnight intervention by on-duty technicians, supplies were transferred and zero blood products were lost.
This incident follows a troubling pattern of attacks targeting commercial refrigeration across Europe, but when critical healthcare infrastructure is involved, the risk shifts from spoilage to human safety.
Our very own Darin Fredde, shared an important perspective with Hackread.com on why response posture matters:
“There’s also an important distinction between changing a temperature setpoint and changing the physical temperature. We shouldn’t confuse an attempted manipulation with a confirmed physical consequence. Fortunately, the reported monitoring, alarms, and staff response appear to have prevented damage.”

New research from Censys has identified 1,465 internet-exposed instances of ARTEX, an AI-powered autonomous penetration testing framework previously linked to cyberattacks against South Korean financial institutions and a China-linked campaign targeting ConnectWise customers.
Of those instances, 155 (10.6%) were hosted alongside other detected offensive security tools or threats, including Cobalt Strike, Vshell and additional AI-powered attack frameworks.
Researchers also discovered 32 publicly accessible directories exposing exploitation tools, malware implants and post-exploitation utilities. Censys cautions that not all ARTEX deployments are malicious and that roughly 650 of the observed hosts share nearly identical configurations.
The findings follow October reports from CrowdStrike and Microsoft documenting ARTEX's use in real-world attacks. Microsoft linked the framework to a campaign involving attempted access to more than 2,250 customer tenants, with some victims experiencing privileged cloud access in under three hours.
Darin Fredde, Senior Director and Offensive Security Evangelist, says: "Our response shouldn't be to panic over another AI framework. We need proven countermeasures, strong identity and access controls, and continuous offensive testing that challenges trust boundaries, business logic, and complete attack paths. The real question isn't how quickly an AI agent can find a weakness. It's whether our security controls can stop what happens next."
censys.com/blog/artex-agenti…

1,831 reported cyberattacks in 12 months. 80 classified as nationally significant. And the NCSC now assesses AI-powered ransomware against UK critical national infrastructure as highly likely by 2028.
The NCSC's 2026 Annual Review finds that criminal and state-backed actors are building AI into reconnaissance, social engineering, vulnerability discovery and exploit development. The result is not a new class of attack. It's familiar attacks running at greater speed and scale, with AI-assisted discovery able to turn weaknesses into exploits before patches are deployed.
Root causes unchanged: Unpatched vulnerabilities, stolen credentials, social engineering
The strategic shift is the patch window. If AI shortens the time from disclosure to working exploit, "patched within SLA" stops being a meaningful assurance. For CNI operators, the exposure is not just data loss but disruption to services communities depend on, and boards will want evidence, not status reports.
The better question for leadership: which of our attack paths have been proven closed, and when were they last tested?
As Darin Fredde puts it: "Capability is different from verification. An AI system reporting that a vulnerability has been fixed is not proof that the attack path has been eliminated."
That is the case for continuous, automated penetration testing: using automation to test assumptions, independently validate remediation, and find exploitable paths before adversaries do. "The question isn't whether attackers will get faster. It's whether we can make verified resilience move faster than the threats we're preparing to face."
👉 infosecurity-magazine.com/ne…
#Cybersecurity #CISO #CriticalInfrastructure #OffensiveSecurity

🏥 A leading U.S. precision medicine company releases new apps and APIs constantly, and every release handles sensitive patient data. Its security team had to find exploitable flaws before attackers did, without slowing development down.
They went from quarterly to biweekly testing and cut mean time to remediate by 80%.
→ Download the case study to see how: ridgesecurity.ai/case-study/…

Finding flaws is only half the battle. Here's what CISOs need to know.
Your security tools probably already find more vulnerabilities than your team can handle. Finding flaws isn't the problem anymore. Fixing the right ones before an attacker uses them is.
AI has made that harder. Attackers now move from discovery to exploit at machine speed, while most organizations still pentest once or twice a year. Everything that changes between those tests is a blind spot.
The CISOs pulling ahead are asking a different question: what can an attacker exploit right now, and how fast can we fix it?
In this video, we explain how continuous, AI-driven pentesting answers that question with verified findings, clear remediation, and your data kept inside your own boundary.
▶️ Watch: youtu.be/PuGIkjP6TIM
#CISO #Cybersecurity #Pentesting #AISecurity #RiskManagement

Ridge Security Technology Inc. retweeted

As application security evolves, there’s a critical distinction teams need to make: the difference between AI-powered AppSec and true AI penetration testing. Traditional scanning tools—even when boosted with AI—often flood security teams with disconnected alerts. But finding a flaw isn't the same as proving an adversary can exploit it.
In healthcare and critical infrastructure—where uptime and patient data are non-negotiable—moving from passive detection to validated exposure management isn't a luxury; it's the standard.
Is your security team still sorting static lists, or are you actively validating attack paths?
Read this white paper by @RidgeSecurityAI, a Health-ISAC Community Services Pathfinder. health-isac.org/ai-pentestin…
#PenetrationTesting #ArtificialIntelligence #HealthcareSecurity

Resetting passwords is only the first step after a compromise.
With 2.59M records and 54K email credentials exposed in the Sony So-net breach, attackers now hold static personal data that can never be revoked, fueling targeted impersonation and credential stuffing down the line.
Ridge Security’s Darin Fredde weighed in for eSecurity Planet on why identity exposures outlive basic remediation: esecurityplanet.com/threats/…
#CyberSecurity #DataBreach #RidgeSecurity #InfoSec

Tenable just announced OPEN for AI, connecting exposure intelligence with other security platforms through MCP and APIs. It's a genuinely encouraging step toward a more integrated, mature security architecture.
But connected isn't the same as secure.
In our latest blog, Darin Fredde looks at what happens when AI agents gain access across your security tools, and why every new integration creates authority and trust boundaries that need to be tested, not assumed.
Attackers don't care how good your architecture diagram looks. They're looking for the seams between your products.
👉 Read the full post (2-min read): ridgesecurity.ai/blog/tenabl…
#OffensiveSecurity #AgenticAI #CTEM #CyberSecurity

🏆 Ridge Security has been named one of the Top 25 Most Innovative Cybersecurity Companies in the World for 2026 by @cyberdefensemag!
View the full list here: cyberdefenseawards.com/top-2…
#RidgeSecurity #CyberDefenseMagazine #AgenticAI #Cybersecurity #RidgeGen #RidgeBot #OffensiveSecurity

We are proud to announce that Ridge Security is the only vendor listed across four categories in three separate Gartner research reports:
→ Adversarial Exposure Validation (AEV) — Market Guide for Adversarial Exposure Validation
→ Agentic Red Teaming — Emerging Tech Impact Radar: Preemptive Cybersecurity
→ Unified Exposure Management Platforms — Emerging Tech Impact Radar: Preemptive Cybersecurity
→ Agentic AI for Security — Emerging Tech Impact Radar: AI Cybersecurity Ecosystem
Read the full press release: businesswire.com/news/home/2…
This recognition underscores the broader shift in cybersecurity toward continuous, automated, and evidence-based validation. Through our agentic AI solutions, we are empowering security teams to move beyond static vulnerability lists and see their infrastructure through the eyes of an attacker.
Thank you to our customers, partners, and the entire Ridge Security team for driving this mission forward.
#Cybersecurity #AgenticAI #ExposureManagement #RedTeaming #Pentesting #CTEM #InformationSecurity #RidgeSecurity

The biggest shift in AI isn’t intelligence, it’s authority. We are rapidly moving from AI that suggests actions to autonomous systems granted the authority to execute them: selecting tools, writing code, orchestrating workflows, and interacting with production environments without continuous human direction.
When you delegate authority to machines, the security paradigm fundamentally shifts.
The core question for security leaders isn’t "Can AI do this complex job?"
It’s: "Do we have verifiable proof that the system cannot exceed the boundaries we set for it?"
Read the full perspective: ridgesecurity.ai/blog/the-se…
#CyberSecurity #ArtificialIntelligence #OffensiveSecurity #InfoSec #AIagents #Automation

Your board will ask one question about PHP2Shell: are we exposed? Two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619) let unauthenticated attackers run code on your servers.
Patching is the fix. Finding every server that still needs it is the hard part, especially end-of-life versions that will never get an upstream patch.
And a version number won’t tell you if an attacker can actually reach the flaw. RidgeBot sends a controlled probe and gives your team evidence instead of guesswork.
Full breakdown from our research team 👇
ridgesecurity.ai/blog/php2sh…
#PHP2Shell #CVE #CyberSecurity #RCE #VulnerabilityManagement #CISO

Ridge Security Technology Inc. retweeted

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
Before you trust any AI with offensive testing, you should be able to answer four questions:
🔗 Register: events.teams.microsoft.com/e…
1) Where do my credentials and findings go?
2) Can it act outside the scope I approved?
3) Can I trust what it reports?
4) What does it cost when we test every week instead of every quarter?
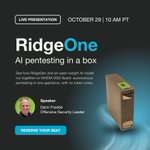
#RidgeOne was built around these questions. Darin Fredde will answer all four with a live presentation.
Can’t join live? Register anyway and we’ll send you the recording.

EV chargers are now critical infrastructure, so we built a realistic EV-charging lab and let RidgeGen loose with no credentials and no human help. In about 4 hours and for roughly $111, it reproduced real Pwn2Own attack chains: it took over the charger’s cloud, stole the cloud credentials, and could start or stop a charging session without logging in.
Every finding was proven by actually exploiting it.
👉 Download the use case: ridgesecurity.ai/use-case/au…
#Cybersecurity #EVCharging #AutomotiveSecurity

Great week at GovWare! ST Engineering, Singapore’s largest system integrator, hosted Ridge Security to present our EV charging infrastructure security solution.
EV chargers are the single most broken category at Pwn2Own Automotive. We showed how RidgeGen autonomously finds, chains, and proves real attack paths across charger cloud consoles and backends, and then retests after every fix. It’s expert-grade validation that scales to an entire charging fleet.
Thank you to the ST Engineering team for having us and to everyone who stopped by!
#RidgeGen #STEngineering #EVCharging #Cybersecurity #AgenticAI #Singapore


AI-driven security testing shouldn’t require sending your data outside your environment.
That’s why we built RidgeOne, a self-contained appliance for autonomous AI pentesting and red teaming. It runs RidgeGen alongside an open-weight model on NVIDIA DGX Spark, entirely on-site, with no external AI calls and no token costs.
RidgeOne is now available, and we’re excited to join the NVIDIA Inception program: businesswire.com/news/home/2…
#AIPentesting #RedTeaming #Cybersecurity

95% of critical infrastructure leaders are worried about AI-powered attacks. Yet 51% still decide what to fix first using CVSS scores or manual review. Here's why that matters:
CVSS grades each vulnerability on its own. Attackers don't think that way. They look for combinations.
Think of a house: an unlocked window, a spare key under the mat, a dog that doesn't bark. None of these looks serious alone. Together, they let someone walk right in.
Your environment works the same way. A few "medium" findings can add up to one critical breach, and a severity score won't show you that.
@PaloAltoNtwks 2026 State of Critical Infrastructure Cybersecurity Report shows the gap:
→ 92% say prioritizing alerts is important or critical
→ 51% still rely on CVSS scores or manual review to do it
→ 91% expect AI-driven security to help defend against AI-powered attacks
If attackers use AI to find your weak spots, you need to find them first. That's what Ridge Security solutions do, test your environment the way a real attacker would.
Source: Palo Alto Networks, 2026 State of Critical Infrastructure Cybersecurity Report www2.paloaltonetworks.com/ne…
We're proud and honored to announce that Ridge Security Technology Inc. has been accepted into @nvidia Inception, NVIDIA's program for startups building breakthrough AI technologies.
This gives the Ridge Security team access to NVIDIA's technical resources, experts, and AI ecosystem as we build #RidgeOne, our AI-powered pentesting solution running on NVIDIA DGX Spark.
Read the announcement: ridgesecurity.ai/blog/ridge-…
#NVIDIAInception #AgenticAI #OffensiveSecurity #Pentesting #RedTeaming #Cybersecurity
