

IT audit and cybersecurity since 2002. Senior-led, never offshore, no products to resell. Plain-English takes on cyber threats to government and enterprise IT.
Tampa, FL
Joined February 2018
- Tweets2.4K
- Following898
- Followers1.1K
- Likes369


Pinned Tweet
Michigan's state agencies had about 370 disaster recovery plans on file. The state auditor found 229 with no recorded test date. A plan can pass every review and still fail the night it's opened, because ransomware goes after the backups and credentials it depends on first.

1
17
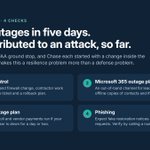
1/ Microsoft 365, the FAA ground stop, Chase. Three outages in five days, and so far none attributed to an attack. Each started with a change inside the organization. What we’re telling clients to check before year end:

1
29
3/ A Microsoft 365 outage plan. An out-of-band channel for leadership and IT, offline copies of contacts and the IR plan, and no urgent alert that depends only on Outlook or Teams.
If a vendor’s script runs on your site, that vendor is part of your attack surface. The Optimizely incident is a good reason to ask whether your third-party risk program covers marketing tags, not just data processors.

Attackers Used Optimizely to A/B Test Malware on Top Websites – Krebs on Security krebsonsecurity.com/2026/11/…
1
13
Charleston County, SC caught unusual network activity Monday night. Services never went down, but the county confirmed data was removed. County IT teams: if your IR tabletop only rehearses a ransomware lockout, add the quiet data-theft scenario. postandcourier.com/moultrie-…

35
NIST’s 2003 password guidance gave us complexity rules and 90-day changes. Its author later said, “Much of what I did I now regret.” Current NIST guidance: 15+ characters if it’s the only factor, screen against compromised lists, change only on evidence of compromise.
1
19
Before you retire the old rules, check PCI DSS, CJIS, cyber insurance and contract terms. Some still require them. Full post: securanceconsulting.com/post…

9
An Ohio district reopens today after a cyber incident closed every school Monday. Phones are back, internet is still limited. Recovery runs in phases. Does your IR plan say what comes back first?
fox8.com/news/questions-rema…

22
A Southeast city that had never run a tabletop exercise was hit by ransomware. A phishing email, a network shared with the county, unclear scope. We ran the war room and sequenced restoration to get core systems back online in about a week.
securanceconsulting.com/case…

1
1
38
Last Tuesday CISA added six exploited flaws to the KEV catalog, including Microsoft Outlook, Google Chromium, and a Barracuda Email Security Gateway auth bypass. Email and browsers are where your users live. Confirm those patches landed first. @CISAgov #PatchManagement
1
37
When yesterday’s Microsoft 365 outage took down email, St. Lucie County’s commission, sheriff and fire district posted phone numbers so residents could still reach them.
Does your incident response plan say how you reach the public when your main platform is down?
#GovTech
1
1
120
Full story via @WPBF25News: wpbf.com/article/microsoft-3…

165
Today’s Microsoft 365 outage is a free tabletop. With Outlook and Teams down, how do you escalate an incident? If the answer lives in SharePoint, that’s your finding. #IncidentResponse
Details via @BleepinComputer: bleepingcomputer.com/news/mi…

946
From our white paper, Tested, Not Just Written: the four assumptions every plan makes until it's tested, and the exercise that exposes each one. securanceconsulting.com/whit…

3
Vanderbilt told its campus to shut down devices and get off Wi-Fi during a cyberattack.Who on your campus can make that call, and have they rehearsed it? #HigherEducation #Ransomware
Latest on Vanderbilt’s recovery: cyberscoop.com/vanderbilt-un…

66
Cyberattacks that disrupted U.S. hospital care kept clinical systems down a median 15 days.
Test your downtime plan against week two, not day two.#HealthcareCybersecurity
Analysis from The Health Management Academy, via @HIPAAJournal: hipaajournal.com/study-insig…

13
A ransomware tabletop is 3–4 hours in one room, not a multi-day outage drill. Where plans stall: a call tree naming someone who left, no one sure which backups are isolated, insurer notice rules missing, legal and comms unsure when to join. securanceconsulting.com/post…

15