

Secured $4B+ | 200+ Audits Done | Top-Ranked in Public Audit | Elite Blockchain Security | Trusted by @Circle , @Fuel_Network ,@soon_svm Redstone & 200 Protocol
Joined January 2022
- Tweets682
- Following219
- Followers816
- Likes3.2K



Pinned Tweet
Really cool development on the @fuel_network the native Fuel token is now bridged via @hyperlane , and the entire integration is secured by @Safe_Edges 🤝

Fuel Expansion.
@Fuel_Network's native token FUEL is now live on Binance Alpha, with the official bridge powered by Hyperlane.
Bridge Here ⏩ usenexus.org/?token=0x3cF30C…
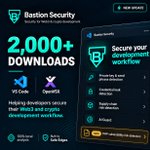
Update ⚡️Bastion Security has crossed 2,000+ downloads on OpenVSX and our latest update adds detection for vulnerable PHP versions.
Activate Bastion Security in your IDE, and it will flag known vulnerable PHP versions in your development environment.
Built by Safe Edges, Bastion Security helps developers identify security risks directly within their development workflow, including:
• Private key and seed phrase exposure
• Credential leaks
• Supply chain risks
• Risky patterns in AI-assisted workflows through AI Guard
• Vulnerable PHP versions
All analysis runs locally on your machine, keeping sensitive code and credentials within your system.
What started as an internal tool to catch security issues earlier continues to grow through community feedback, improved detections, leak free, and performance enhancements.
Thank you to everyone who has installed, tested, reported issues, and supported Bastion Security.
2,000+ downloads and counting. More improvements ahead.
open-vsx.org/extension/safee…

Worst day for cybersecurity.
Multiple zero-days, supply chain compromises, and ongoing active exploitation reported across the industry.
GitLab: CVSS 10.0 remote code execution vulnerability.
Railway: Customer secrets and private keys potentially exposed.
QUIC: Reported zero-day vulnerability.
PHP: Two critical unauthenticated RCE vulnerabilities under active exploitation.
LiteLLM: Backdoored release stealing cloud, SSH, and AI credentials.
eMudhra: Weak certificate authority keys exposed users to certificate forgery risks.
Node.js, Next.js, React: Critical RCE and TLS security vulnerabilities.
TiDB Cloud: Breach involving stolen credentials and customer data exposure.
Plex2Shell: Exploited within hours, deploying cryptominers and backdoors.
BeyondTrust and Ivanti:
Actively exploited zero-days added to CISA's KEV catalog.
Railway Customers are reporting that their private keys and data are circulating
Our internal security agent continues to deliver great results and has proven itself in public audit competitions by finding critical vulnerabilities, securing a 3rd-place position so far.

The @ensdomains Audit Competition is a wrap!
🏆 Top Winners:
🥇 br0nz3p1ck4x3 - $8,013
🥈 @crypt0n1337 - $6,461
🥉 bugtester - $5,557
🏅 @xylz__1 - $3,194
🏅 I_A_J - $3,032
Congrats to all participants & winners! 🎖

Ethereum Glamsterdam upgrade is moving to Sepolia.
The Sepolia testnet activation is scheduled for October 6, 2026, at 13:53:36 UTC.
Glamsterdam brings several protocol-level changes, with two of the more notable ones being:
Enshrined Proposer-Builder Separation (ePBS): Brings proposer-builder separation into the Ethereum protocol itself, changing how block building and proposing are handled.
Block-Level Access Lists: Introduces access lists at the block level, specifying the accounts and storage slots that transactions in a block will access. This is designed to make execution dependencies more explicit and support more parallel processing.
The Sepolia rollout is an important step in testing these changes before the upgrade moves further toward mainnet.
Worth watching closely if you're building or researching around Ethereum execution, MEV, and protocol security.
blog.safeedges.in/the-most-c…

Recently, the U.S. Securities and Exchange Commission (SEC) granted temporary, conditional five-year exemptive relief to certain distributed-ledger trading venues dealing in tokenized NMS stocks, as well as to certain liquidity providers operating on those venues.
This development could open a new phase of institutional adoption, with major financial firms increasingly exploring tokenization, real-world assets (RWAs), and blockchain-based financial infrastructure. This is one reason we are seeing more established institutions and large financial players entering the blockchain space. not simply to experiment with the technology, but to build and operate tokenization and RWA infrastructure.
However, greater institutional adoption also brings greater security risk.
The more capital, financial assets, and market infrastructure move onto blockchain-based systems, the more attractive these platforms become to sophisticated attackers. Security therefore cannot be treated as a secondary consideration.
In this article, we take a deep look at the tokenization landscape from securities and regulatory considerations to the technical and security risks facing institutional tokenization and RWA platforms. We examine how tokenized assets work, where vulnerabilities can emerge
blog.safeedges.in/tokenizati…
The SEC just opened the door.
Today’s Innovation Exemption gives Tokenized Securities Venues five years to trade tokenized NMS stocks using permissioned AMMs and liquidity pools. Smart contracts must be public, auditable, and deployed on permissionless ledgers. Shareholder rights must match the traditional stock. Issuers get notice. Trading must halt in sync with the primary exchange.
This is not a pilot.
This is the first real regulatory path for onchain U.S. equities.
Institutional tokenization and RWA infrastructure just moved from conversation to market reality. The contracts that power these venues will now sit at the center of regulated capital markets.
Safe Edges has been working at this exact layer institutional, RWA, and tokenization-level security for years. Auditable contracts. Real attack-surface analysis. Zero post-audit incidents across $4B+ secured.
The exemption is temporary. The security requirement is not.
This is going to be big.
#Tokenization #RWA #Web3Security #InstitutionalFinance #SafeEdges

August was one of the worst months for DeFi security in Web3, with $185+ million exploited across multiple hacks and incidents. Honestly, the number of attacks we witnessed throughout August is extremely concerning and needs to be addressed properly.
Until we understand the root cause of these incidents, we cannot effectively build better prevention strategies for future attacks. That is exactly why we published this detailed August Web3 Security Incident Report, covering the major incidents, attack vectors
Read the full report, understand the incidents, and learn from them. #safeedges
blog.safeedges.in/august-202…

Now the industry is becoming increasingly dependent on AI, and AI security must become a major concern.
The recent incidents involving Hugging Face and OpenAI show that we need to rethink our perspective: we desperately need security for AI.
This is why we’re investing heavily in AI agent security and working with our partners to secure their AI agents before they can be exploited in production.

We have conducted a thorough investigation into the Hugging Face incident.
We are releasing a technical report and accompanying blog post that reconstruct the agents’ activity, explain why existing safeguards failed, and detail how we’re preventing recurrence.
openai.com/index/hugging-fac…

Let’s meet today everyone

AI agents can think, learn, and act. But to participate in a real economy, they also need identity, permissions, wallets, and secure settlement infrastructure.
Join our upcoming AMA:
AI Agents Need Wallets: Who Will Build Asia’s Machine Economy?
🗓 August 28th, Friday
⏰ 1:00 PM UTC
🎙 Hosted by ENI
Guests:
• Arion, ENI CEO
• Paul Kim, ENI Korea CEO
• Azibi Malawi, AxiomOS @axiomos_
• Saadia, VerityAI @BuildOnVerity
• Vivan Chauhan @wxite, Safe Edges @SafeEdges
• Ahaya, Freedom Asset @FreedomAssett
Discover who will build the wallets, security, coordination, and financial infrastructure powering Asia’s machine economy.

Safe Edges retweeted

AI agents can think, learn, and act. But to participate in a real economy, they also need identity, permissions, wallets, and secure settlement infrastructure.
Join our upcoming AMA:
AI Agents Need Wallets: Who Will Build Asia’s Machine Economy?
🗓 August 28th, Friday
⏰ 1:00 PM UTC
🎙 Hosted by ENI
Guests:
• Arion, ENI CEO
• Paul Kim, ENI Korea CEO
• Azibi Malawi, AxiomOS @axiomos_
• Saadia, VerityAI @BuildOnVerity
• Vivan Chauhan @wxite, Safe Edges @SafeEdges
• Ahaya, Freedom Asset @FreedomAssett
Discover who will build the wallets, security, coordination, and financial infrastructure powering Asia’s machine economy.
Safe Edges is now the Strategic Security Partner for the @X1_EcoChain ecosystem.
X1 is an EVM-compatible L1 running Proof of Nodes, with validators on 4-core, 4GB, low-power hardware rather than datacentre rigs. A validator set shaped like that changes the assumptions around participation, liveness and reward accounting.
Gas from every transaction is redistributed at the protocol level, 90% across validator wallets and 10% to genesis. Custom economic logic like that is where the findings that matter usually sit, not in the parts a generic checklist covers.
For teams building on X1 that means full Solidity coverage on contracts and dApps, plus pen testing across the frontend, API and RPC surfaces, at ecosystem rates and a priority queue.
#SafeEdges is here to secure every team building on X1.

Excited to announce our strategic partnership with @X1_EcoChain
X1 is building an EVM-compatible L1 with up to 90% lower transaction fees.
We’re proud to be part of the X1 ecosystem and look forward to strengthening the security of the teams and protocols building on X1. 🛡️
#safeedges 🤝 #x1ecochain

X1 EcoChain 🤝 @SafeEdges: Fortifying Ecosystem Security
We are thrilled to announce our strategic partnership with Safe Edges — a premier Web3 cybersecurity firm specializing in smart contract audits and protocol verification.
Safe Edges joins us as an official security partner. Moving forward, projects joining the X1 EcoChain ecosystem will get direct access to top-tier security audits under highly exclusive terms.
Key benefits for X1 EcoChain ecosystem projects:
🟢 Special Perks: preferred rates and priority queue for smart contract and dApp audits.
🟢 End-to-End Protection: manual code reviews, invariant testing, and threat monitoring.
🟢 Ecosystem Trust: seamless mainnet onboarding backed by industry-tested security standards
Forward - together with the best 🚀

We're talking about agentic finance for a long time. Coinbase has now launched AI Finance (AIFi), where agents can autonomously decide where to pay, how to pay, and how much to pay.
But the big question is security. We’ve been researching autonomous agentic security closely with our clients to secure the whole flow. We need to give this extra attention. otherwise, it’s going to become a huge challenge.


Autonomous agents are entering Web3 and finance fast. But what happens when a malicious prompt makes an agent sign a transaction or move funds? Could agent security become Web3’s next major security crisis? I wrote the full deep dive.

🚨Harmony was hit by a MASSIVE 4 billion $ONE minting event, worth approximately $3.2 million USD at the time of the incident.
The ~4 billion unauthorized ONE tokens were valued at roughly $3.2 million when ONE was trading near $0.0008, following a ~30–34% price crash.
The exact root cause is not yet clear, but preliminary indications suggest that the attacker may have minted the tokens through empty blocks. Notably, the protocol’s totalSupply failed to immediately reflect the sudden increase in token supply, creating a temporary discrepancy between actual on-chain balances and the reported total supply.
After partnering with leading ecosystems like Fuel, Clique, Hyperlane, and supporting 200+ protocols, we’re now super excited to announce that ENI has chosen Safe Edges as its Official Security Partner.
We’re proud to support ENI and its builders with deep, ecosystem-specific security expertise and help strengthen security across the entire ENI ecosystem.
ENI × Safe Edges — Stronger security for every builder. 🔐
blog.safeedges.in/safe-edges…
#safeedges

Safe Edges is now the Official Security Partner for the @ENI__Official ecosystem.
ENI is building enterprise-grade infrastructure where AppChains and the projects on top of them multiply over time. Every one of those chains carries its own execution environment and its own security surface.
ENI runs Cosmos SDK and Tendermint with an EVM layer that diverges from Ethereum in ways that break standard assumptions.
PREVRANDAO returning a block-time hash. COINBASE mapped to the fee collector. IAVL state instead of MPT.
Auditing here means auditing against those divergences, not against a generic EVM checklist.
#SafeEdges is here to secure every team building on ENI

🚨More than $38 million worth of Bitcoin has reportedly been stolen due to a critical vulnerability affecting Coldcard Mk3 hardware wallets.
Funds from approximately 500 wallets were drained to the attacker's address, totaling 594.48 BTC.
Root Cause
The vulnerability stems from a weak entropy / random number generator (RNG) flaw in Coldcard Mk3 hardware wallets.
Specifically, it affects BIP-39 recovery seeds generated on Coldcard Mk3 devices running firmware 4.0.1 (released in March 2021) through the final Mk3-supported versions (around 5.0.3).
Due to a series of subtle firmware bugs, the device's hardware True Random Number Generator (TRNG) failed to contribute sufficient randomness during seed generation. Instead, the wallet relied heavily on a software-based Pseudo-Random Number Generator (PRNG) seeded primarily from limited and predictable sources, such as device state (e.g., chip identifiers) and timing information.
This significantly reduced the effective entropy of the generated seeds.far below the intended 128 bits. As a result, some recovery phrases became predictable enough that an attacker familiar with the flaw could reconstruct potential seeds offline and steal funds from affected single-signature wallets.
Coinkite, the manufacturer of Coldcard, acknowledged the issue in a security advisory and warned that affected users may be at risk.
Wallets protected with a BIP-39 passphrase (an additional passphrase beyond the recovery seed, not the device PIN) are considered significantly more resistant to this attack. Newer models (Mk4, Q, and Mk5) include different mitigations and are not believed to be affected in the same way.
This weakness is believed to have enabled the coordinated theft of approximately 594.48 BTC from around 500 wallets within a short period.
The fundamental issue was insufficient randomness during master seed generation on the affected Coldcard Mk3 firmware versions.
If this is possible with today's computing power, imagine the impact once practical quantum computing becomes a reality.
Coinkite (the manufacturer) issued a security advisory confirming the issue and warning affected users that their funds may be at risk. Wallets protected by a BIP-39 passphrase
blog.coinkite.com/coldcard-m…
