

🧠 Malware analyst & reverse engineer 🦠 Ransomware, loaders, stealers & RATs 🔬 Reverse engineering • crypto • tooling 📍 Technical research. No buzzwords.
Joined May 2025
- Tweets779
- Following190
- Followers1.2K
- Likes4K



absolutely correct! As specified, in this specific sample the ransomware module is disabled.
I've posted it because, based on my research, the ransomware module was not documented yet. If you have a source, feel free to share :)
🚨ALERT🚨
PhantomStealer4 has a #ransomware module.
AES-256-CBC + HMAC-SHA256, .phantom files, FTP key escrow and file deletion.
Disabled in this build (RansomCheckBox = false)
Bazaar👇
bazaar.abuse.ch/sample/13cee…


🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇


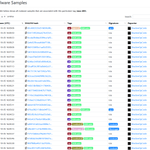
Just uploaded 203 #RGBLoader samples to MalwareBazaar, all discovered through hunting with my custom #YARA rule! 🔬
The samples are now available to the malware research community under the RGBLoader tag.
🔗 bazaar.abuse.ch/browse/tag/R…
#MalwareAnalysis #ThreatHunting


IMPORTANT UPDATE
xitter.cf/ShadowOpCode/status/21…
The loader I’ve been tracking as #RGBLoader is very likely a #GraftLoader variant, documented by @trendaisecurity. Both share the same pixel extraction, crop constants and payload cipher, including implementation quirks.
xitter.cf/ShadowOpCode/status/21…
trendaisecurity.com/en-us/re…
The loader I’ve been tracking as #RGBLoader is very likely a #GraftLoader variant, documented by @trendaisecurity. Both share the same pixel extraction, crop constants and payload cipher, including implementation quirks.
xitter.cf/ShadowOpCode/status/21…
trendaisecurity.com/en-us/re…
🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
This is so fucking true.
It pisses me off that Microsoft Defender for Endpoint doesn't support YARA hunting at scale.
I can write rules that detect entire malware clusters, but how are defenders supposed to operationalize them?
YARAify is useful, but we need better integration.
NEW generalized #YARA rule for #RGBLoader
👇
yaraify.abuse.ch/search/yara…
xitter.cf/ShadowOpCode/status/21…
⚠️NOT tested against FP, consider it a beta⚠️

🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
hxxps://katfiore[.]com (not personally validated as compromised at the moment, just reported)
hxxps://xenseyu[.]com/hex/dr7kggqq4y
hxxps://xenseyu[.]com/p?id=b5b1eb33425d9811d17ff3045684db5a993a9a68&k=0c1507711b004009
cc @shalkie @tobersotski

"french/viet fake program" refers to the language seen in the code, not the threat actor origin or affiliation

🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
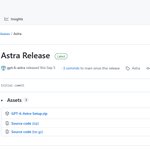
hxxps://github[.]com/gpt-6-astra/gpt-6-astra.github.io/releases/tag/Astra
@malwrhunterteam @vxunderground @skocherhan @tobersotski
