

Intelligence-Driven Blindspot Detection | Uncover Hidden Attacker Infrastructure • Zero-Day Intelligence • Threat Hunting | Turning Intelligence into Action.
Pune, India
Joined December 2025
- Tweets45
- Following27
- Followers75
- Likes66



Pinned Tweet
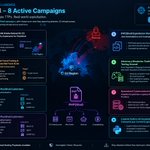
🚨 PHP2Shell isn’t one attacker or one playbook.
Threatactix is tracking 15 campaigns, including K4nha botnet kit C2, Sliver C2, custom Python C2, web shells, cryptojacking & gaming/VPS infrastructure.
🌍 The screenshot below highlights countries represented by the Russian botnet operator in our K4nha / Sliver C2 investigation: Germany, France, UK, Netherlands, Ukraine, and the US.
🔎 Threat-hunting playbooks available.
📩 DM “PHP2SHELL” for a briefing.
🔗 Explore our Intelligence Portal: intelligence.threatactix.com…
#ThreatIntelligence #ThreatHunting #php2shell

🔎 PHP2Shell: Looking Beyond the Initial Compromise
15 campaigns. 8 activity profiles. A deeper investigation into the infrastructure behind PHP2Shell-related activity.
What can campaign-level analysis reveal about attacker operations, C2 infrastructure, and evolving threat patterns?
📖 Read the full technical analysis:
threatactix.com/2026/10/29/p…
#PHP2Shell #ThreatIntelligence #ThreatResearch
@TheHackersNews @BleepinComputer @ch3tanK @Threatactix

🔎 Our PHP2Shell telemetry spans diverse attacker tradecraft, including:
→ C2 infrastructure & botnet activity
→ SMTP authentication & STARTTLS testing
→ Java deserialization & cryptojacking
→ Custom exploitation & command-and-control tooling
🎯 Security teams: Are you hunting the activity after exploitation?
📩 DM “PHP2SHELL” for a threat intelligence briefing and hunting playbooks.
🔗 Log in to our Intelligence Portal:
intelligence.threatactix.com…
#PHP2Shell #ThreatIntelligence #ThreatHunting
🤖 Made with AI

Threatactix Research retweeted

📢 Ransomware Alert 🇦🇺
Race Trakka (racetrakka.com.au), an Australia-based automotive services organization, has reportedly fallen victim to Qilin ransomware.
🛡️ Threat Actor: Qilin
📅 Reported on: 26/10/2026
@ThreatactixLab @Threatactix @ch3tanK

🚨 Threat advisory: we’ve tracked [4] active PHP2Shell C2 servers over the last [48 hours].
They’re tied to [CVE-2026-109618, CVE-2026-109619] and target internet-facing PHP apps for unauthenticated RCE.
#PHP2Shell #ThreatIntel

Sharing Analysis for Threat Actor Activities which are using Cobalt Strike -
Key technical takeaways:
1. Core Tooling & C2: Features mature command-and-control frameworks including Cobalt Strike (cs_loader.dll) and Metasploit/Meterpreter, supported by asynchronous HTTP/HTTPS beaconing.
2. Advanced Tradecraft: Demonstrates active evasion via manual mapping utilities and DLL sideloading (directmanipulation_proxy.dll) designed to bypass security monitoring.
3. Kill Chain & Recon: Initial web-based access vectors transitioning into aggressive Active Directory mapping (SharpHound), credential harvesting (Inveigh), and internal pivoting (KrbRelayup, ncatStarter).
For full analysis-intelligence.threatactix.com…
Threatactix Research retweeted

We are currently tracking live C2 activities

What our telemetry shows around this infrastructure:
→ C2-01: A web app exploitation framework with a post-exploitation operator panel
→ C2-02: Attempted attacks on game server infrastructure
→ C2-03: A Cobalt Strike beacon loader with privilege escalation tooling
→ C2-04: A C2 loader and a lateral movement toolkit
#ThreatHunting #CobaltStrike
What our telemetry shows around this infrastructure:
→ C2-01: A web app exploitation framework with a post-exploitation operator panel
→ C2-02: Attempted attacks on game server infrastructure
→ C2-03: A Cobalt Strike beacon loader with privilege escalation tooling
→ C2-04: A C2 loader and a lateral movement toolkit
#ThreatHunting #CobaltStrike
How Threatactix can help. PHP2Shell data is included in plans:
1. SentryX: SOC/IR teams, with monthly hunting, ATT&CK mapping, and reporting
2. Olympus: MSSPs and large orgs, with weekly hypotheses and detection engineering
Get the full PHP2Shell indicator set in the portal:
🔗 intelligence.threatactix.com…
Want a 20-min walkthrough for your SOC? DM “PHP2SHELL” and we’ll reply within [X hours].
#MSSP #SOC
Threatactix Research retweeted
NEW RANSOMWARE VICTIM DETECTED🚨
Threat Actor: Fulcrumsec
Victim: PingCAP / TiDB Cloud
Sector: Media
Country: United States
Date: 2026-10-19

Threatactix Research retweeted
📢 Ransomware Alert
🔎 Key Details:
🛡️ Threat Actor: Qilin
🏢 Organization: First Brothers Co., Ltd
🌐 Website: firstbrothers[.]com
📅 Reported on: 17 October 2026

Threatactix Research retweeted
🚨 Ransomware Alert 🚨
Qilin ransomware group has added 4 new victims to their dark web portal.
* Mastelli 🇮🇹
* Pergande Group 🇩🇪
* Pengurusan Aset Air Berhad 🇲🇾
* Brutra Logistiek 🇳🇱

Threatactix Research retweeted
📢 Ransomware Alert: 🇺🇸
🔎 Key Details:
🛡️ Threat Actor: Redact
🏢 Organization: Parker-Hannifin Corporation
📅 Reported on: 16 October 2026
@ThreatactixLab

Threatactix Research retweeted
📢 Ransomware Alert: 🇺🇸
🔎 Key Details:
🛡️ Threat Actor: Redact
🏢 Organization: ONEOK, Inc.
📅 Reported on: 16 October 2026
@ThreatactixLab

Threatactix Research retweeted
📢 Ransomware Alert
🔎 Key Details:
🛡️ Threat Actor: Helix
🏢 Organization: Smith Douglas Homes · Records
📅 Reported on: 18 October 2026

Threatactix Research retweeted
📢 Ransomware Alert
🔎 Key Details:
🛡️ Threat Actor: Helix
🏢 Organization: Bay Alarm · Records
📅 Reported on: 18 October 2026

Threatactix Research retweeted
🚨 Ransomware Alert | Green Clinic, USA 🇺🇸
📍 Location: Ruston, Louisiana, USA
🏥 Industry: Healthcare
🌐 Website: green-clinic[.]com
⚠️ Threat Actor: Wallstreet
📂 Reported Data: 2 TB (claimed)
@ThreatactixLab

🚨 CITRIX ATTACK: The CVE is only the beginning.
What happened after exploitation?
We uncovered attacker infrastructure, malware/tooling, network indicators, and behavioral clues - turning the activity into actionable threat-hunting hypotheses.
🔎 Explore the intelligence:
intelligence.threatactix.com…
The real target isn’t the CVE. It’s the infrastructure behind it.
@Threatactix @ch3tanK
#Citrix #ThreatHunting #ThreatIntel #CTI #CyberSecurity
🚨 RANSOMWARE ALERT: Healthcare Sector
We've identified a pre-encryption attack chain targeting hospital networks — 6 correlated artifacts, staged and ready, before the ransomware payload ever runs.
None of them look alarming alone. Together, they're a full operation.
Thread 🧵👇
🤖 Made with AI

The real question isn't:
❌ "Can we detect the ransomware?"
It's:
✅ "Can we detect the operation before ransomware becomes visible?"
That gap = dwell time = the window where defenders actually have leverage.
1
2
20
🚨 Full IOC set, detection logic (Sigma/YARA), and hunting queries for this attack chain — live now:
👉 intelligence.threatactix.com…
If you run a healthcare or pharma-adjacent SOC, this is worth checking against your own coverage today.
#RansomwareAlert #ThreatIntel #HealthcareSecurity #SOC #CISO
1
7