

Soñador.... CriptoInversor.... Haciendo Trading desde El PARAISO, Rep Dominicana ENLACE GRUPO GRATUITO ABAJO https://teapaw.org/t.co/p5kXtMm8rn
Joined September 2009
- Tweets7.1K
- Following483
- Followers1.8K
- Likes2.3K





Pinned Tweet
¡Únete GRATIS a la comunidad cripto más activa!
✅️ Videochats 24/7 con traders pro
✅️Clases y análisis en vivo 24/7
✅️ Señales Gratis
Aprende trading y domina el Bull Run 2025.
👉 Entra ahora: t.me/AccesoAlertas_Bot
#CriptoSeñales #TradingGratis
#BTC #Eth #BullRun – at San Cristóbal, Dominican Republic


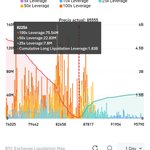
105mil traders liquidados.
+400MM de los LONG murieron
Funding negativo.
Bienvenido al mercado cripto.
A los 105mil liquidados, "No esperen resultados diferentes haciendo lo mismo."

4
284


Esta semana:
PMI de servicios mañana lunes.
Actas de la FOMC el miércoles.
Noticias del mercado, será una semana relativamente dominada por analisis tecnico/onchain.
173
Un buen Tr4der se adelanta a los acontecimientos, proyectar el mercado es vital para lograr resultados positivos.
Confia en tu análisis y respeta tu plan de trading y obtendrás buenos resultados!

4
279
BITGET HACKEADO.
Pocos fondos fueron robados según la CEO @GracyBitget

[SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
At 18:31 UTC on September 24, 2026, Bitget's security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
What we have confirmed:
-Estimated funds affected: approximately $351.6 million
-Cold wallets remain fully secure. Bitget operates a three-tier wallet architecture — the breach contained only a portion of the hot wallet and warm wallet layers.
-User funds are safe. The full amount of this loss falls within the coverage of Bitget's User Protection Fund, which currently holds over $464 million
Actions we have taken:
-Emergency response team activated within minutes of detection
-Abnormal transfer addresses identified, flagged, and reported
-Withdrawals temporarily suspended as a precautionary measure, pending security review
-Law enforcement and on-chain security firms have been formally notified and are engaged
What this means for you:
-Your account balances are accurate and your assets are protected
-Deposits and trading remain fully operational
Withdrawals are temporarily paused and will be restored as soon as the security review is complete
-What comes next: We will provide updates on an hourly basis across this channel and all official platforms. A full incident report — including root cause analysis and corrective actions — will be published within 24 hours. We will not speculate on the attack vector until the investigation is complete.
Bitget has navigated multiple market cycles. We will not run from this. Every dollar and every decision will be accounted for, transparently and in full.
Updates will be posted here and across all official Bitget channels as they become available.
— Gracy Chen, CEO, Bitget
4
327


No. 1 del equipo en la KCGI Global, ojo estoy en un equipo de chinos q me metí ahí.
Equipo en posición 8 a nivel mundial

2
4
346

Tu eres duro si, pero despues q sale la vela....
Los duros son los que antes que llegue la vela ponen el target.


6
310
Proyectado.
Ejecutado
Pero sobre todo en el proceso.
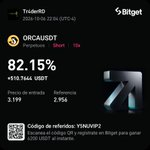
Nosotros lo hacemos juntos y ganamos $$$


1
6
304
Ufff @ClaroRD expliquen esto

🚨🇩🇴 Claro Dominican Republic dataset containing 2.8M+ customer records allegedly leaked
⠀
Claro is a major telecommunications provider in the Dominican Republic, offering mobile, internet, television, and other communications services to consumers and businesses.
⠀
A forum actor using the handle jarol1488 claims to have breached Claro’s systems in the Dominican Republic and obtained a dataset containing information tied to 2,889,256 customers.
⠀
Claimed exposed data includes:
⠀
• Customer identification numbers
• Mobile phone numbers
• Subscription records
• SIM / ICCID identifiers
• Service and account status
• Plan categories and descriptions
• Activation dates
• Billing cycle information
• Release dates
• Mobile validation status
• Internal subscription and plan identifiers
⠀
The actor published sample records showing customer identifiers alongside multiple mobile subscriptions, phone numbers, SIM-related data, account status, and prepaid plan information.
⠀
The breach claim, record count, authenticity of the dataset, and full scope of the exposed customer information have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

369
🇺🇸 IPC Anual
act: 3.4% | est: 3.4% | prev: 3.4%
🇺🇸 IPC Mensual
act: 0.4% | est: 0.4% | prev: 0.1%
🇺🇸 IPC Subyacente Anual
act: 2.4% | est: 2.4% | prev: 2.5%
🇺🇸 IPC Subyacente Mensual
act: 0.3% | est: 0.2% | prev: 0.2%
3
216