

VicOne, headquartered in Tokyo, Japan, is a cybersecurity leader for Physical AI, built on proven automotive cybersecurity expertise.
Joined September 2022
- Tweets471
- Following43
- Followers272
- Likes61
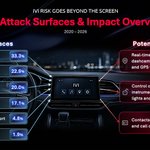


The BYD Shark 6 security research highlights a broader connected-vehicle risk: an IVI security issue can have consequences beyond the infotainment screen. The bigger question is not only where an attacker gets in, but what that access can ultimately affect. #ConnectedVehicles

Why does this matter?
Modern IVI systems connect with cloud services, wireless interfaces, mobile devices and other vehicle systems.
A compromise can potentially extend beyond infotainment to vehicle data, privacy and vehicle functions.
#VehicleCybersecurity
IVI cybersecurity is no longer only about protecting the screen. It is about understanding the connections around it and what those connections can ultimately affect.
#AutomotiveCybersecurity
CVE-2026-86793: SGLang's SafeUnpickler—the patch for CVE-2025-10164—is vulnerable to bypass. A remote attacker can execute arbitrary code through an unauthenticated endpoint. VicOne researcher Reuel Magistrado details the gadget chain. 🧵(1/6)
#ThreatIntelligence #CVE #SGLang
The entry point: /update_weights_from_tensor accepts unauthenticated requests. An attacker sends base64-encoded pickle. SGLang decodes and deserializes. The gadget chain executes. Code runs as the SGLang process. 🧵(5/6)
#ThreatIntelligence #CVE #SGLang
Until SGLang patches, enable authentication immediately. Restrict endpoint access to trusted networks.
Read the full analysis and remediation guidance: vicone.com/blog/cve-2026-867…
🧵(6/6) #ThreatIntelligence #CVE #SGLang

What if one AI prompt could make the server behind it obey an attacker?
VicOne discovered a critical vulnerability, CVE-2026-86793, in SGLang, potentially putting 131,430 servers across 35 countries and regions at risk.
#PhysicalAICybersecurity #VulnerabilityResearch


Learn how Mythos-ready security and always-on VulnOps help CISOs respond faster to AI-accelerated vulnerabilities, exploit chains, and cyber risk at scale.
vicone.com/blog/how-mythos-i…
#AutomotiveCybersecurity #VulnOps #CyberRisk #ThreatIntelligence #Mythos #VulnerabilityManagement

A milestone in robotic cybersecurity, made by @RobotHackComm at @defcon 34.
RoboHack AI CTF findings just became a free NVIDIA Isaac Sim extension.
bit.ly/4qvhNzZ


AI-chained attack vectors are changing vulnerability triage. Learn why automakers and suppliers must move from CVSS scores to attack-path prioritization before July 2026.
vicone.com/blog/what-lies-be…
#AutomotiveCybersecurity #VulnOps #CyberRisk #CISO #VulnerabilityManagement


VicOne retweeted
The robots are asking questions. That's usually a sign something interesting is happening.
Are you ready for the #RoboticHacking #CTF at @defcon CON 34?
→ robotichackingvillage.com
#DEFCON34 #RoboticHackingCommunity
VicOne retweeted
Robotic Hacking Community is launching at @defcon 34 in Las Vegas as the first organized space focused on robotics security research, hands-on workshops, CTFs, and expert talks.
Because robots are not just endpoints.
#DEFCON #Robotics #AISecurity #RobotSecurity

VicOne retweeted
Both dogs.
Both studying each other.
The real one is starring wondering what is in front of him.
The robot dog is logging it and accessing it's AI knowledge.
Both are trained but when triggered badly both can have unpredictable behavior.
#RobotDog #Robotics #PhysicalAISecurity
6/7
The more useful question is which vulnerability can be exploited first, and through which path.
How are your PSIRT, product design, and development teams collaborating when a new CVE is disclosed?
#AutomotiveCybersecurity #VulnerabilityManagement
7/7
Read the full analysis → vicone.com/blog/prerequisite…
#PSIRT #ISOSAE21434 #UNECER155 #SDV #TARA #ConnectedVehicle