

Privacy, AI automation & connectivity insights | Mobile proxies, non-VoIP numbers & global eSIMs. Control your digital identity.
Joined November 2025
- Tweets588
- Following27
- Followers2.7K
- Likes802





Pinned Tweet
Your AI agent can now buy its own phone number, eSIM, and mobile proxy. With a spending cap you set.
We upgraded the VoidMob MCP server. 30 tools, open source, and it now plugs straight into the runtimes everyone's building on: Grok Bot, OpenClaw, Hermes, Pi, and Boat, plus Claude Code, Codex, and Cursor.
Here's the problem it solves:
Every cloud agent, Grok Bot, Meta Muse, OpenAI's dots, runs on a locked machine where the vendor owns the IP and the payment rail. The agent has no way to get a real phone number to verify an account, a clean IP for a geo or AI protected task. So it hands the whole thing back to you.
VoidMob fills that gap. The agent draws on one prepaid balance to buy exactly what it's missing:
- Global non-VoIP numbers, one-time or dedicated, that pass verification where VoIP gets rejected
- Mobile proxies on real carrier IPs, by country and carrier
- eSIM data plans across 180+ destinations
Every purchase runs the same way: the agent quotes the price, waits for your yes, then buys with your approved price as the ceiling. Set a per-order cap and a session budget and nothing goes over it. Give each agent its own key and kill it whenever you want.
No KYC, instant access. Sandbox mode to test every tool on play money first.
One command: npx -y @voidmob/mcp
Setup guides for every runtime:
voidmob.com/mcp
voidmob.com/integrations

You can’t freeze $XMR, $BTC or any other native coin. That’s the fundamental concept of crypto.
And this is only the beginning. More hacks, more breaches, more stolen data.
Keep as little personal data as possible on exchanges, or anywhere you sign up, before your details show up in the next leaked database.

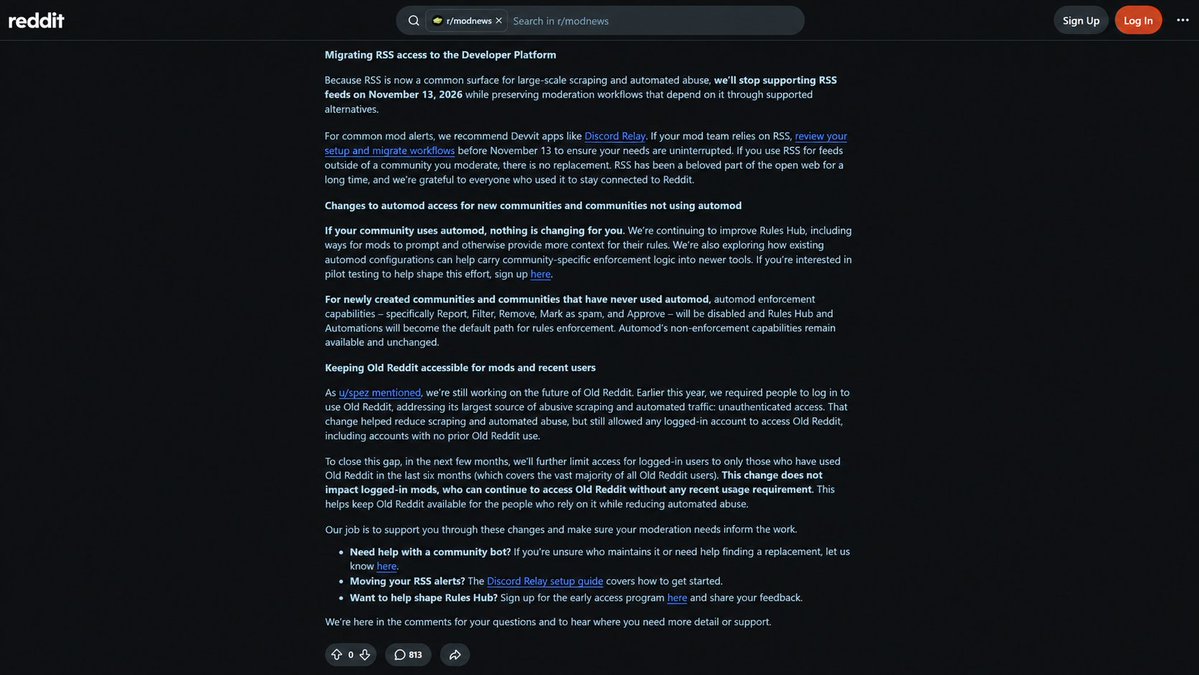
Reddit just killed the public API.
New access requests stop tomorrow, Oct 31. RSS feeds die Nov 13. Everything left shuts by March 2027.
What it means:
- Your Reddit monitoring tool, alert bot or “find leads in subreddits” script stops working unless Reddit approves it
- Every Reddit scraper on GitHub that used the public API or RSS is now dead code
- Parasite SEO on Reddit gets harder, because the logged-out access you used to find threads and track rankings is what Reddit says it’s cutting first
- The data isn’t gone. Reddit sells it to Google and OpenAI. It’s just not free for you anymore
What still works:
1. Use a real account. Logged-in Reddit still serves the same JSON the app uses. Reddit said logged-out traffic was the abuse it’s targeting, so logged-in is the path that survives.
2. One account per IP. Reddit links accounts by IP and device, not by username. Two accounts on one home connection and they both go when one goes.
3. Use a mobile IP, not a datacenter or cheap residential one. Reddit flags hosting ASNs on sight. A carrier IP looks like a phone on 5G because it is one.
4. Warm the account. Post, comment, vote like a person for two weeks before you automate anything. Low Contributor Quality Score gets your posts hidden before anyone sees them.
5. Slow down. A few hundred requests an hour with random gaps, not thousands a minute.
6. Verify with a real carrier number. Reddit rejects VoIP numbers (Google Voice, TextNow) on new accounts.
Reddit made the API a product. Your scraper needs to look like a customer now.
Full guide with working Python: voidmob.com/blog/how-to-scra…
Source: reddit.com/r/modnews
The scary part is you can do everything right and still get burned by a package you trusted.
But most of these leaks spill the same things: your IP, your email, your phone number. That part you control.
- Private eSIM so your real home IP never touches the services you log into.
- Non-VoIP number so your personal line isn’t sitting in the next breach.
- Encrypted mobile proxy so your PC traffic exits on a carrier IP, not your home connection.
Keep your real identity out of the stack, and a breach leaks a shell, not you.

October has been an absolute nightmare for software
> Railway - customer secrets exposure
> LiteLLM - malicious PyPI + Docker releases
> Zeabur - infrastructure breached
> OpenCode - AI API keys exposed
> OVHcloud CLI - official binaries backdoored
> Rank Math PRO - malware in official plugin
> TeamUpdraft - customer data compromised
> ConnectWise - cloud backup identities compromised
> Tensorlake - npm package infected
> SubQuery - backdoored npm package
> GhostAction - GitHub repos with malicious workflows
> PHP - critical RCE vulnerabilities
> Node.js - security vulnerabilities patched
> eMudhra - certificate authority keys compromised
> Tailscale - eMudhra incident
At this point, the biggest security risk might not be the code we write, but the code we trust...
New non-VoIP numbers just dropped. Whether it’s for automation or personal use, you get a real local line that actually works.
Two new countries added:
- Indonesia non-VoIP numbers at $21.99/mo (+62)
- Italy non-VoIP numbers at $29.99/mo (+39)
Monthly, all services supported, real carrier lines not VoIP.
More integrations are on the way.
Get 10% off your first deposit.
voidmob.com/sms

VoidMob (Private Connectivity) retweeted

Hace poco estuve probando un servicio que se llama VoidMob desde Latinoamérica y me sorprendió todo lo que se puede hacer desde una misma app.
Para probarlo en serio contraté una eSIM desde Colombia con salida a internet por Estados Unidos. La activé (es realmente muy fácil hacerlo: escaneás el QR que te dan, aceptás la configuración y listo), revisé la IP y efectivamente estaba saliendo por EE. UU. Algo que me gustó es que antes de comprar podés ver el país de routing y en algunos casos elegirlo.
También probé uno de sus números de teléfono de Estados Unidos. Lo pude configurar con una cuenta de WhatsApp y recibir el código de verificación sin problemas. También me envié SMS desde un teléfono que tengo en USA y llegan perfectamente. Para alguien que está en Latam y necesita tener un número de otro país, esto puede ser sumamente útil.
Además de eso, VoidMob tiene eSIMs para más de 180 países, números de distintos países y proxies móviles 4G/5G. También tienen servicios disponibles en varios países de Latinoamérica (Argentina, Colombia, México, Chile, Brasil, Ecuador, Costa Rica, Uruguay, Paraguay, Perú y otros), así que no es algo pensado únicamente para gente que está viajando por Europa o EE. UU.
Los precios me parecieron bastante razonables. Las eSIM arrancan desde US$2,99, los números dedicados de EE. UU. cuestan US$19,99 al mes y hay proxies móviles compartidos desde US$3,99 por GB. También tienen proxies móviles dedicados con datos ilimitados, aunque ahí el precio depende del país y del tipo de conexión.
Otra cosa que me gustó es que todo funciona con un mismo balance. Cargás saldo y lo vas usando para los distintos servicios. Además, podés pagar con criptomonedas sin KYC.
Incluso tienen un MCP para conectar VoidMob con agentes de IA y que puedan interactuar directamente con el servicio. Todavía no le encontré un uso cotidiano para mí, pero la idea está bastante buena. Será cuestión de probarlo más adelante.
Lo estoy probando ahora desde Colombia y por el momento la experiencia fue muy buena. Sobre todo me parece interesante para quienes estamos en Latinoamérica, ya sea viviendo acá o temporalmente, y necesitamos acceder a servicios, números o conexiones de otros países sin tener que estar físicamente ahí.
Si quieren probarlo, se los recomiendo 100%.
voidmob.com/


The hackiest CAPTCHA setup we've seen in 2026 is a solver + a mobile proxy.
The part nobody posts:
The best way to beat a CAPTCHA is to never trigger it.
This is killing AI agents right now. An agent runs into a Cloudflare block page, doesn't realize it's blocked, and keeps trying to read data that isn't there. The loop burns the whole token budget for nothing.
Scrapers deal with the same thing. Perfect code, then one challenge or rate-limit page and the whole workflow stops.
Here's what people miss. CAPTCHA solvers charge you per solve, $0.60 to $3 per 1000. Most setups pay on nearly every request because their IP looks suspicious before any puzzle even loads.
reCAPTCHA v3 scores every request silently. Turnstile decides the check based on how risky your connection looks. A VPS, VPN IP or your home IP is exactly what those scores flag.
Every CAPTCHA that never appears is a solve you never paid for, and a loop your agent never gets stuck in.
The full setup:
- Mobile proxy (VoidMob), carrier IP for the session so risk checks stay quiet
- A solver (CapSolver, CapMonster, 2Captcha) for the few that still appear
- Route the solver through your proxy, so the challenge gets solved from the same IP you browse from. If the solve and the submit come from different IPs, the site rejects the token.
Solver + mobile proxy is the current captcha bypass meta. One keeps the challenge from showing up, the other solves the few that still do. Most people only buy half.

You can't leak what was never yours to begin with.
You don't need an ISP. You don't need a carrier number. You don't even need your own IP.
That's VoidMob. Privacy with no questions asked.
Your Meta agency accounts didn't get nuked for breaking rules. They got nuked for something you didn't know you were doing.
Everyone blaming the ban wave on "policy violations" is wrong.
Meta openly allows multiple ad accounts, but it tracks patterns and link your accounts.
Meta builds a graph on every advertiser. Your IP, your browser fingerprint, your device, your payment card, your login, each one is a node. The second two "unrelated" accounts share enough nodes, Meta stops seeing an agency with 12 clients and starts seeing one operator running 12 accounts.
The agencies that survived weren't luckier. They were isolated. Nothing shared between accounts, so nothing to link, nothing to cascade.
Here's the exact separation, one per portfolio:
- Dedicated mobile carrier IP. Not office WiFi. Not a datacenter proxy. Not one proxy split across three accounts. One clean IP per portfolio.
- Antidetect browser profile with its own fingerprint. Same browser across two accounts links them. Incognito changes nothing.
- Unique payment card per portfolio. A shared card is one of the strongest links Meta reads.
- Non-VoIP number per account. Meta auto-rejects VoIP. Real carrier lines pass.
- Partner access, never one profile admin-ing everything. Never cross-login.
And before you buy your way out: rented agency accounts don't save you. They come pre-verified with higher trust, then die in the same wave the moment you run them on shared IPs and cards.
The problem was always infrastructure and wrong patterns.
VoidMob covers the two layers that you can actually trust in 2026.

September 2026 has been one long data breach and it's not even over yet.
Revolut handed over passport copies, verification selfies, and full transaction histories to an attacker using a spoofed government email domain.
220 million airline passenger records exposed: names, passport numbers, dates of birth, nationalities. Left open with default credentials.
820 million Alipay users leaked, including phone numbers.
IDScan breached: government ID information, potentially exposed.
Suno: 55 million email addresses and phone numbers.
Notice the pattern. Every breach leaks the same things: your real name, your real number, your real ID, your real email.
The only data that can't leak is the data that was never tied to you.
How to shrink your exposure before the next one:
Register accounts with a VoidMob non-VoIP number, not your personal phone. When that platform gets breached, the leaked number or email tied to it leads nowhere.
Use a fresh email per service, not your main inbox linked to everything.
Route through a VoidMob eSIM and encrypted proxy so your ISP isn't logging and selling your traffic on top of it.
Never hand a platform your passport or biometric selfie unless it's legally unavoidable. IDScan and Revolut just showed where that ends up.
You can't stop companies from getting breached. You can stop your real identity from being in the file when they do.
- VoidMob
VoidMob eSIMs just expanded beyond data.
EU and UK eSIMs now include SMS and calls, not just data. A real number attached to your eSIM for verification and voice, without a carrier account tied to your identity.
Find them under the Network filter, set to "With phone number." Alongside IP Routing, Country, Duration, and Data filters so you configure exactly the profile you need.
Other regions: global eSIMs are on the way. A totally new product. Unlimited global data, calls, and SMS with privacy features no other eSIM offers.
Get yours now. Stay tuned for the updates.
dashboard.voidmob.com/esims

If your SaaS or AI agency doesn't have an automated B2B lead pipeline, you are leaving revenue on the table.
Cold emailing dead lists doesn't work anymore. Local businesses are a goldmine for custom tech, and they sit right in front of your eyes on Google Maps.
The standard lead-gen playbook is broken and outdated. You need high-quality infrastructure that connects directly to your AI agents.
Here is how to build an automated, unblockable scraping pipeline:
Target your niche: Pick your desired location and target business category (e.g., HVAC in Austin or dentist clinics in Miami).
Connect your AI agent via MCP: Hook Cursor, Claude, or your custom agent directly into the VoidMob MCP server.
Bypass scraping limits: Your agent pulls real-time local business data through high-trust 4G/5G mobile carrier IPs - eliminating rate limits, CAPTCHAs, and anti-bot blocks.
Don't waste your time manually compiling business data or fixing broken proxy setups. Your AI agent can handle the entire pipeline end-to-end.
Start VoidMob MCP
github.com/voidmobcom/voidmo…

monero:native is one the most bullish assets of the decade.
Cash is dying. Governments are pushing digital IDs and CBDCs that log every transaction you make.
BTC and ETH won't save you, every transaction sits publicly forever. AI algos now scan transparent chains in milliseconds. Pseudonymous is not private.
Monero is the only one left that's totally anonymous.
And it just got stronger. The FCMP++ upgrade replaced ring signatures with full-chain membership proofs, expanding the anonymity set to 150M+ outputs. Correlation attacks are now mathematically impractical.
XMR is up 120% over 12 months on pure privacy demand.
Think about it.
How VoidMob compares to other mobile proxy providers in 2026.
Bright Data, Oxylabs, Decodo, IPRoyal, NetNut, Proxidize all sell mobile proxies. We looked at what they offer and built the same thing cleaner, more private, and with more protocols.
We have what they have:
- Real 4G/5G carrier IPs like Bright Data and Oxylabs
- Rotating shared pool like Decodo and IPRoyal (11M+ IPs)
- Global geo-targeting by country and carrier
- HTTP, HTTPS, SOCKS5 support
What we do better:
Cleaner sourcing
- Our SDK pool is ISO 27001 + ISO 27701 certified with explicit opt-in consent.
- Our dedicated tier runs on our own in-house SIM hardware. No SDK, no consent chain at all.
NetNut got seized in July for skipping exactly this. We built the opposite.
More privacy
- No KYC.
- Crypto payments (BTC, ETH, SOL, USDT, XMR)
- Minimal logging.
Oxylabs, Bright Data, and Decodo all require identity verification. We don't.
More protocols
- VLESS over Xray REALITY (reads as normal HTTPS, passes DPI)
- OpenVPN and real UDP relay
Nobody in this list offers this on mobile. We do.
More control
- Configurable p0f TCP/IP fingerprinting per port
- Carrier-native DNS, no ASN mismatch
- Dedicated exclusive carrier IPs, not just shared slices
- MCP support so AI agents route through us natively
Pricing: rotating from $3.99/GB, dedicated from $69/month unlimited. Undercuts Bright Data, Oxylabs, and NetNut at every tier.
Same core product as the big providers. Cleaner sourcing, no KYC, and protocols none of them offer.
Full breakdown: voidmob.com/proxies

How to build an online business in a weekend that most people have never heard of?
Bots now make up 57% of all web traffic, and every one of them needs clean IPs to run.
Reselling mobile proxies. Here's the model:
You buy bandwidth wholesale at $2/GB. You set your own retail price. You keep the spread. The supplier runs the hardware, carrier SIMs, and network. You never touch a cell tower.
The math:
- Buy at $2/GB, sell at $6/GB = $4/GB margin
- Move 500GB in a month = $2,000 gross
- No infrastructure, no inventory, no SIM cards
This is a vibecoder's dream business. The entire thing is an API and a dashboard:
- Fund your VoidMob account
- Provision customers programmatically
- White-label so they only ever see your brand
You're building a storefront and a brand on top of infrastructure that already exists. Create a landing page with Cursor or Claude Fable, connect the reseller API, install payments. Ship it in a weekend.
The demand side is only growing. Every scraper, every AI agent, every multi-account operation needs mobile IPs that don't get blocked. Dedicated mobile is the highest-trust product and almost nobody offers it for reselling.
Start today:
dashboard.voidmob.com/develo…

Google's site: operator is going viral for two very different reasons.
Lead-gen guys are scraping "site:facebook.com/groups intitle:looking for a web designer" to find people actively asking to buy.
Others used "site:claude.ai/share" to surface millions of private AI chats that got indexed by accident. Same one-line search trick. Very different targets.
Here's what nobody's saying: the moment you run these at scale, Google blocks you.
Automated systems now generate 57.5% of HTTP requests worldwide, passing human traffic for the first time in June 2026. Google knows.
It defends Search with IP reputation scoring, TLS fingerprinting, behavioral analysis, and CAPTCHA escalation.
Run a site: go across a few hundred queries and you'll get a block:
Datacenter IPs? Flagged at the ASN before you finish.
Python requests? Your JA4 TLS handshake looks nothing like Chrome.
Fixed timing? Bot pattern. Instant flag.
A few hundred queries deep? 429 or reCAPTCHA. IP burned.
The full stack that survives:
- Mobile carrier IP behind CGNAT
- TLS impersonation (curl_cffi with impersonate="chrome") so your JA4 matches a real browser
- Randomized jitter between requests, never fixed intervals
- gl/hl/uule parameters for accurate localized results
- Rotate the second an IP returns a CAPTCHA marker
The site: operator is a goldmine right now. Scraping it without getting blocked is the actual skill.
Full guide with working Python: voidmob.com/blog/how-to-scra…
