

Root out vulns with Sable
Northern Virginia
Joined October 2024
- Tweets112
- Following27
- Followers72
- Likes38




Pinned Tweet
Sable, our AI pentester, found a bug in OneDev that lets any low-privilege user run code as root.
The server's response to the attack is a 403.
The cause: two admin-only endpoints run bean validation before the admin check. That validation compiles Groovy, and Groovys ASTTest annotation executes code at compile time.
Sable spotted it from a single 400 where a 403 should have been.
What runs before your authorization check?
vulnetic.ai/blog/groovygate-…

Not every pentester needs access to every client engagement.
Introducing Project ACLs in Sable. Restrict project access to only the team members who need it.
Keep client engagements isolated and access under control.
vulnetic.ai
4/ What makes this one notable is how long it hid. The flaw was confirmed at runtime on v0.46.0 and in source through v0.47.1. It affects every release before 0.49.0 and is fixed in 0.49.0. The vulnerable Gitea approval path dates back to when the integration was introduced in v0.28.0 (May 2024), so it was most likely present for roughly two and a half years before the patch shipped this month.
1
13
5/ If you run Atlantis with Gitea, upgrade to 0.49.0. vulnetic.ai/blog/rce-in-atla…

12
Edit findings through chat!
Redact confidential information, reword impact statements, tweak remediation, it's all at your fingertips!
Changes are saved to the finding so everything is client ready.
Sable is built to make pentester workflows easy. vulnetic.ai
1/
Sable found a host takeover in Portainer CE 2.45.0.
A standard user could get root on the shared Docker host, even with privileged containers explicitly forbidden.
4/
Same commit through manual redeploy: rejected. Same policy, different code path.
The automatic path reached the deployer without the validation the manual path used.
1
9
5/
Patched in Portainer 2.45.2. Upgrade if you run Portainer with GitOps auto-updates.
Full write-up:
vulnetic.ai/blog/portainer-g…

13
Vulnetic has completed its SOC 2 Type II audit.
Security teams across industry and government trust Sable with access to their environments. This audit independently verifies that the controls protecting that access operate effectively over time, not just on paper.
Learn more about our security posture: vulnetic.ai/security

Vulnetic Inc. retweeted

Read our recent piece on prompt canaries and honeypots and what we found actually works against hacking AIs:
vulnetic.ai/blog/detecting-a…
We tested whether prompt canaries and honeypots could detect AI attackers. Read more below!
vulnetic.ai/blog/detecting-a…

Vulnetic Inc. retweeted
Migrate your own custom skills to Vulnetic! Not only do we have a superior penetration testing harness, but you can also imprint your own custom skills onto Sable.
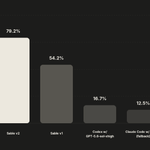
Sable v2 is here!
Scoring 25 percentage points higher than our v1 harness, Sable v2 is a complete rework built around a new assessment harness and improved model orchestration.
The benchmark below reflects multiple assessment passes against our internal custom applications, measuring the ability to identify, exploit, and validate vulnerabilities across web applications and APIs.
View our full changelog here: vulnetic.ai/changelog
